

darkdump
 josh0xa/darkdump
Open Source Intelligence Interface for Deep Web Scraping
data-exfiltrationemail-harvestinginformation-gathering+4
josh0xa/darkdumpOpen Source Intelligence Interface for Deep Web Scraping
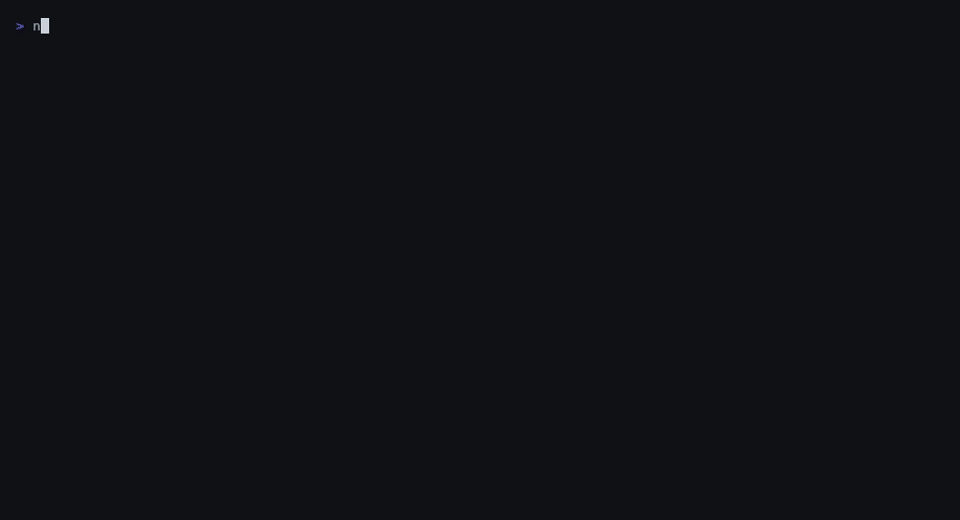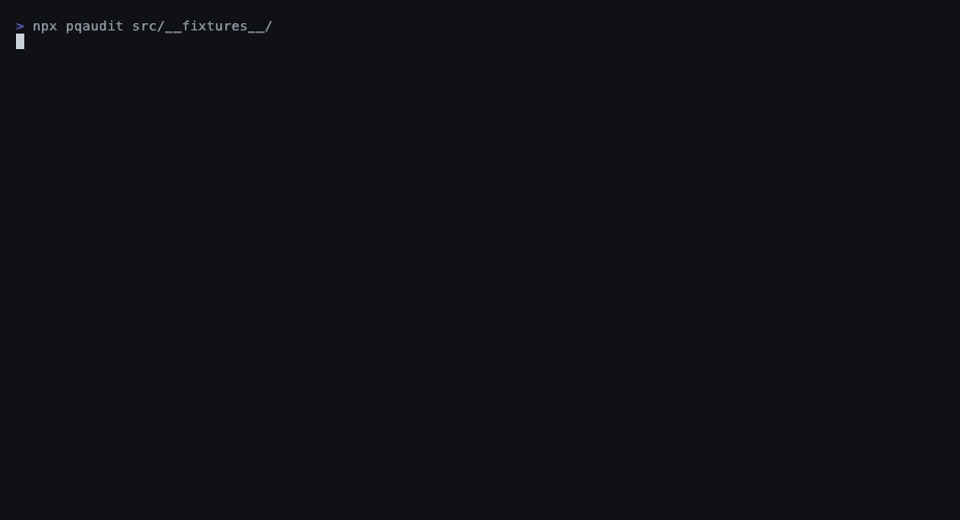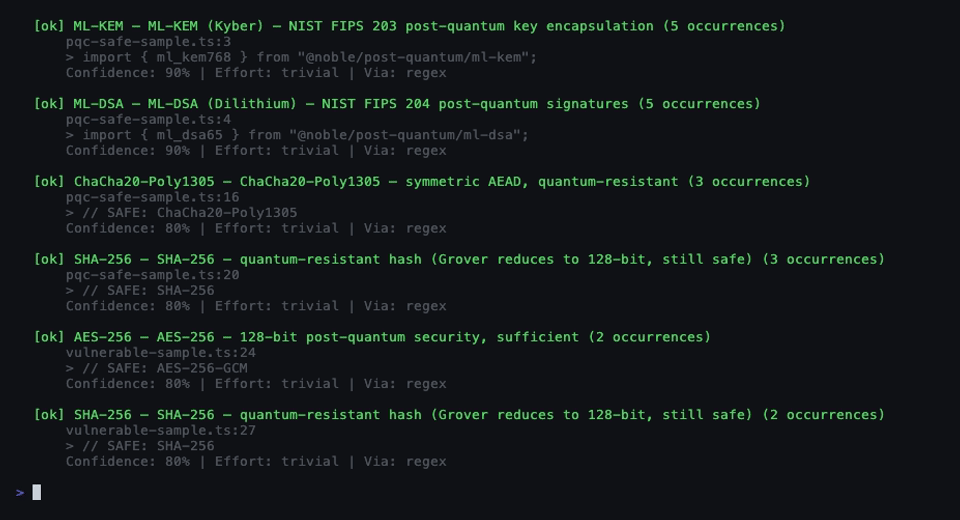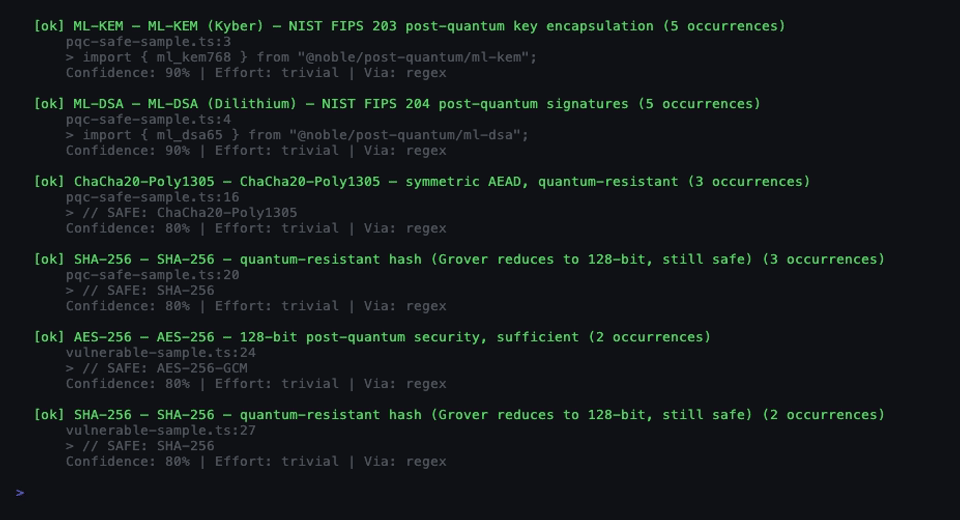 pqcworld/pqaudit
Scan codebases for quantum-vulnerable cryptography. Detect RSA, ECDSA, Ed25519, ECDH before Q-Day. CycloneDX CBOM + SARIF output.
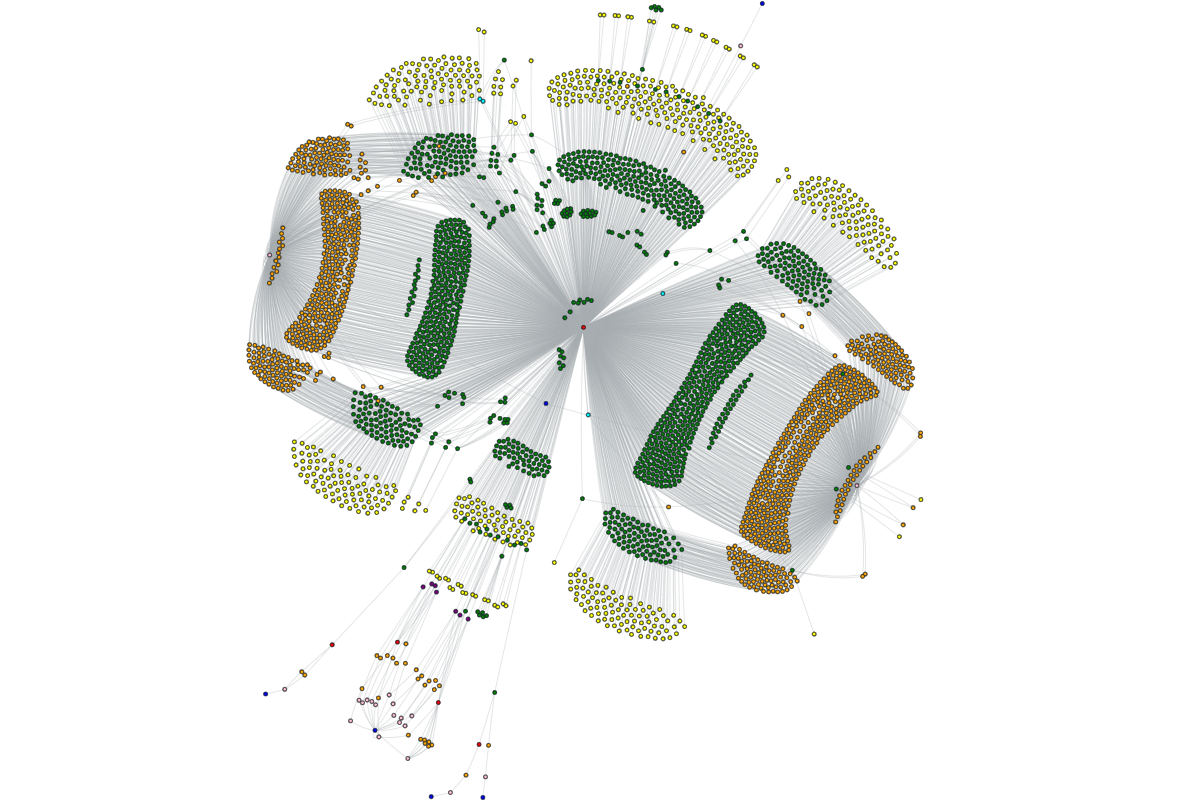 owasp-amass/amass
In-depth attack surface mapping and asset discovery
 sobri3195/pegasus-pentest-arsenal
A comprehensive web application security testing toolkit that combines 10 powerful penetration testing features into one tool.
 justicerage/ffm
Freedom Fighting Mode: open source hacking harness
 dafthack/cloudpentestcheatsheets
This repository contains a collection of cheatsheets I have put together for tools related to pentesting organizations that leverage cloud providers.
 h4wkst3r/dop2mop
OpenGraph collector for BloodHound that maps attack paths from DevOps to MLOps infrastructure, collecting CI/CD pipeline, service principal, and ML…
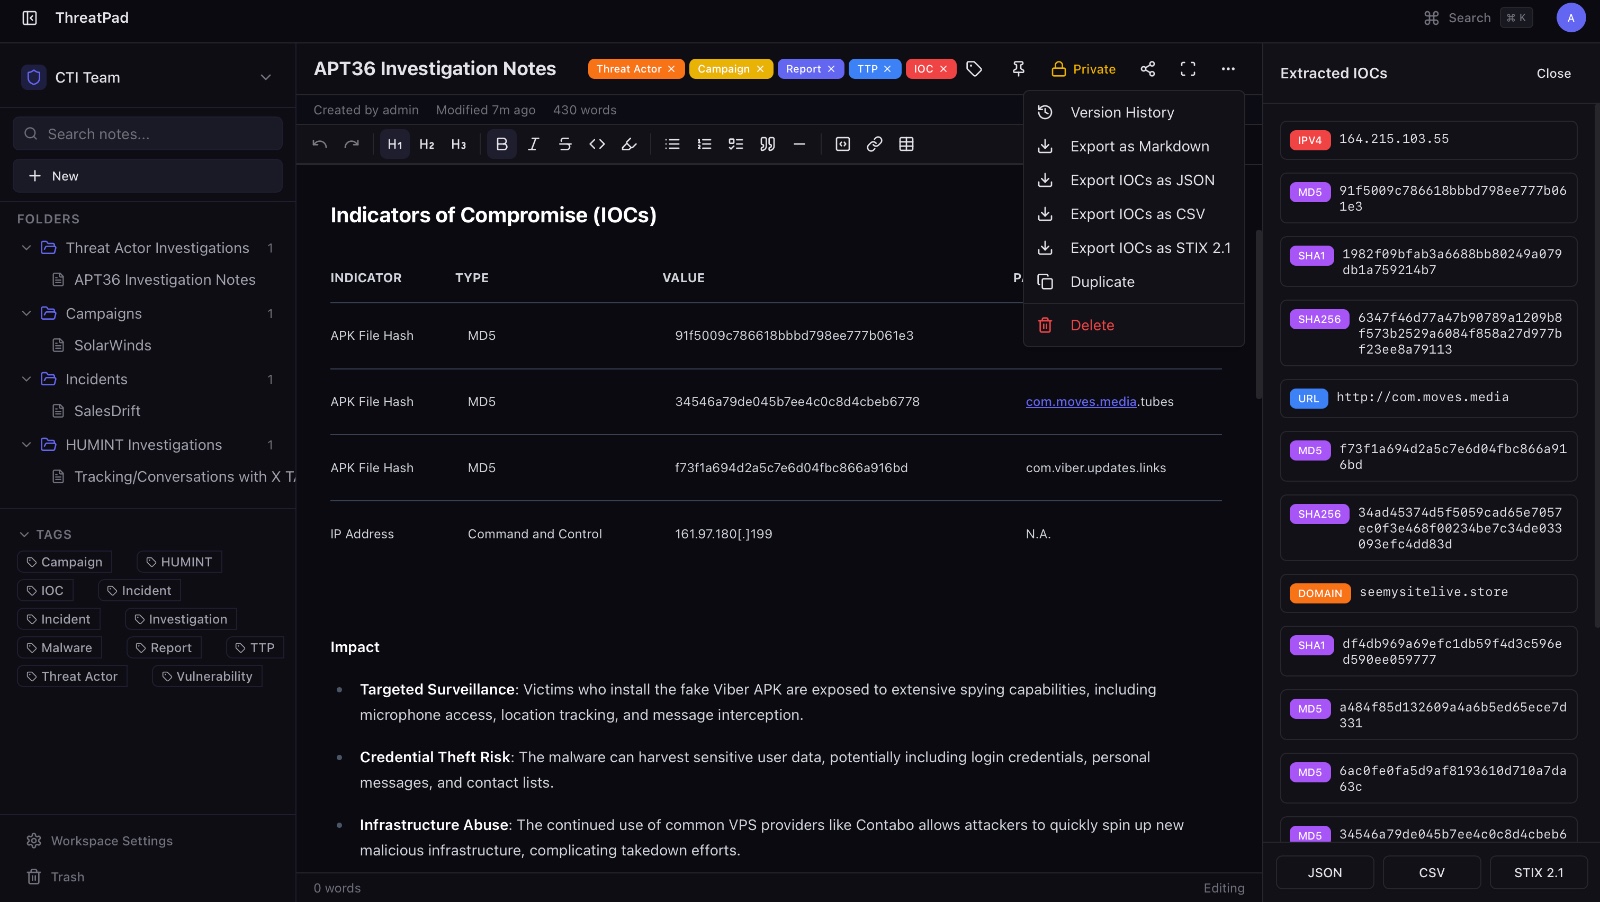 bhavikmalhotra/threatpad
Open-source collaborative note-taking platform for cybersecurity and CTI teams. IOC auto-extraction, STIX 2.1 export, real-time editing, RBAC,…
 amikanev/cve-2025-23061-lab
Hands-on lab environment for reproducing and analyzing CVE-2025-23061, providing a controlled setup for security testing and vulnerability research.
 kaktus5454/cve-2018-15473
SSH username enumeration exploit for CVE-2018-15473 (OpenSSH 2.3-7.7). Sends malformed authentication packets to identify valid users on vulnerable…
 arnavps/ctf-web-exploitation
A comprehensive collection of 12 containerized web exploitation challenges covering CVE-2023-25690, WebAuthn bypasses, HTTP/3 smuggling, and advanced…
 jgoyd/fourteen_endpoints
Shell Companies Inside Apple's Privacy Relay
 fevar54/cve-2026-3502-scanner---trueconf-vulnerability-detection-tool
Scanner de CVE-2026-3502: detecta clientes TrueConf vulnerables e IOCs de TrueChaos. Reportes JSON/HTML/CSV.
 elinanotelina/cve-2024-3094-analysis
Analysis and exploitation toolkit for CVE-2024-3094, providing vulnerability assessment and proof-of-concept execution for the targeted security flaw.
 redyank/cve-2026-33752
Demonstrates a redirect-based SSRF vulnerability in curl_cffi allowing internal network access, with PoC code and analysis of TLS impersonation…
 lockfale/osint-framework
Curated framework of free OSINT tools and resources for gathering intelligence from public sources, organized by category with structured metadata…
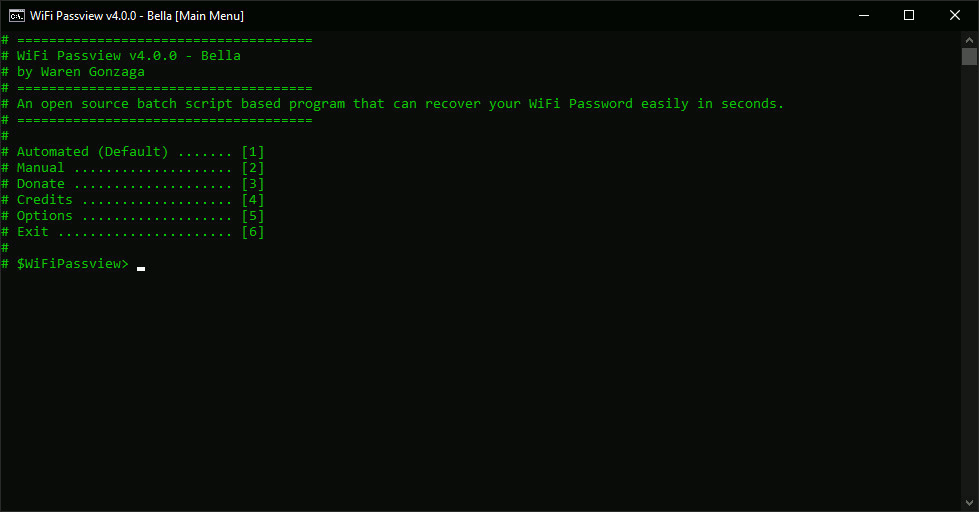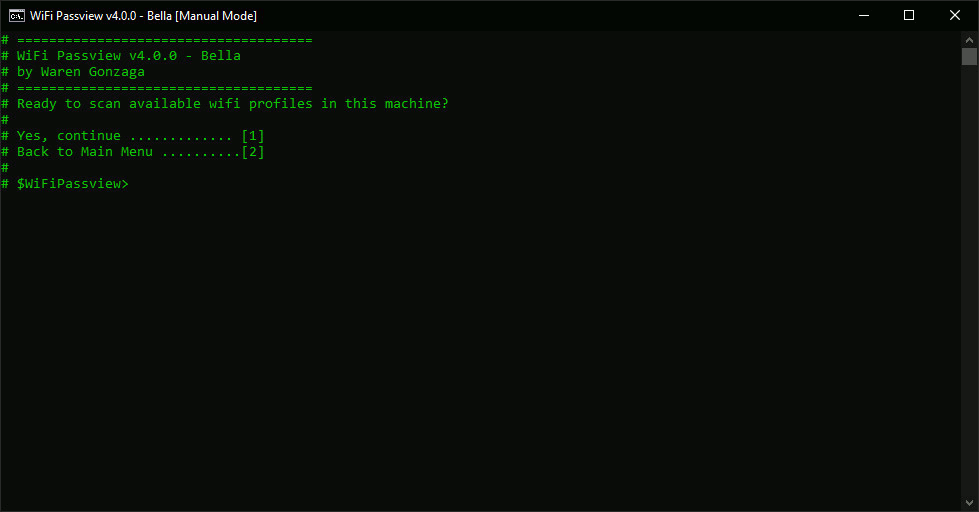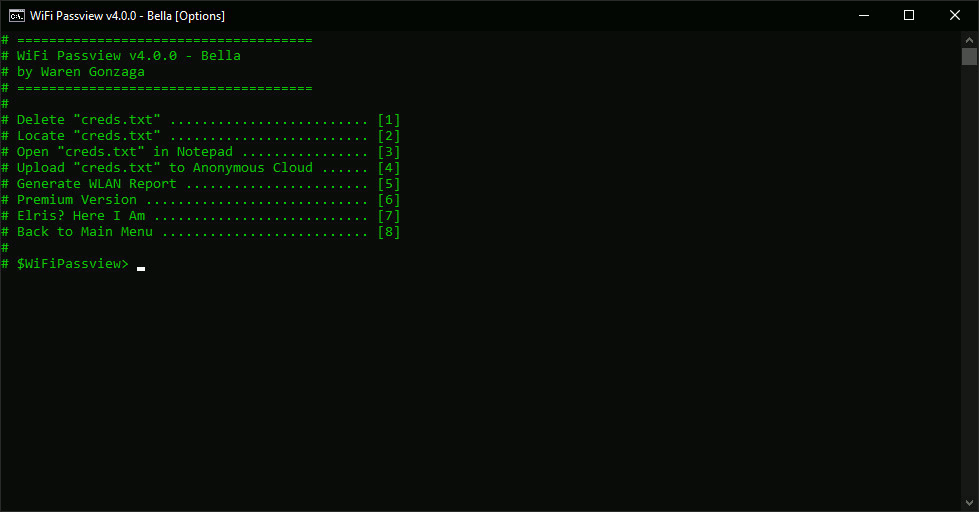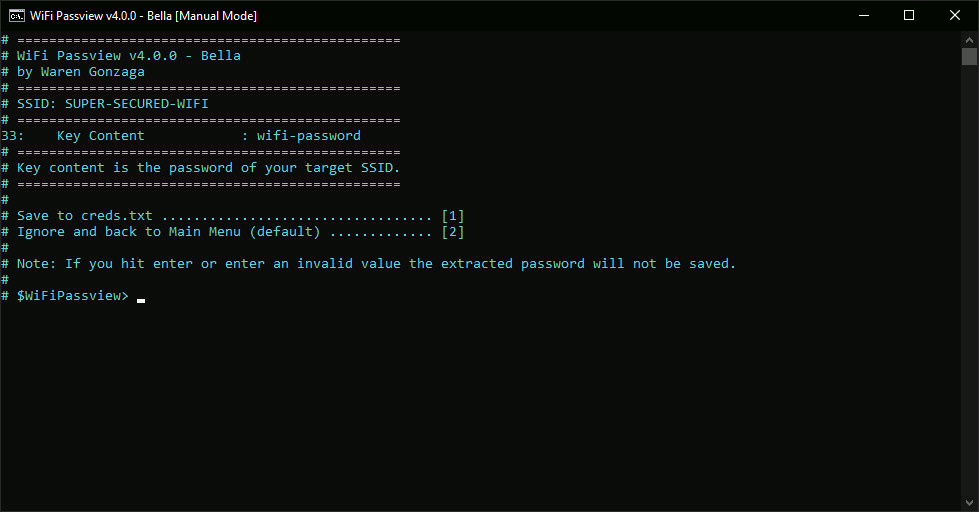 warengonzaga/wifi-passview
An open source batch script based WiFi Passview for Windows!
 ayoubfathi/leaky-paths
A collection of special paths linked to common sensitive APIs, devops internals, frameworks conf, known misconfigurations, juicy APIs ..etc. It could…