
3snake
 blendin/3snake
Tool for extracting information from newly spawned processes
data-exfiltrationmemory-forensicspassword-attacks+4
blendin/3snakeTool for extracting information from newly spawned processes
 oscerd/cve-2026-79984
Runnable proof-of-concept reproducer for CVE-2026-79984, a path traversal in Apache Camel camel-mina-sftp, with malicious SFTP server fixtures and…
 michel-dv/xz-utils-backdoor-case-study
Technical case study of the XZ Utils backdoor (CVE-2024-3094), covering supply-chain trust abuse, malicious release artifacts, build-stage injection,…
 hasan8babiker/cve-2024-6387
PoC exploit for CVE-2024-6387 (OpenSSH regreSSHion), targeting sshd signal handler race condition for remote code execution on glibc Linux systems.
 lane0218/cve-2023-25136-poc
Minimal Docker-based reproduction environment for OpenSSH 9.1p1 pre-auth double-free vulnerability (CVE-2023-25136), demonstrating memory corruption…
 acrono/cve-2024-6387-poc
32-bit PoC for CVE-2024-6387 — mirror of the original 7etsuo/cve-2024-6387-poc
 nhakobyan685/cve-2023-25136
OpenSSH 9.1 vulnerability mass scan and exploit
 shoucheng3/apache__mina-sshd_cve-2023-35887_2-9-2
Pure Java SSH client/server library implementing SSH-2 protocol with support for multiple ciphers, key exchanges, authentication methods, SFTP, SCP,…
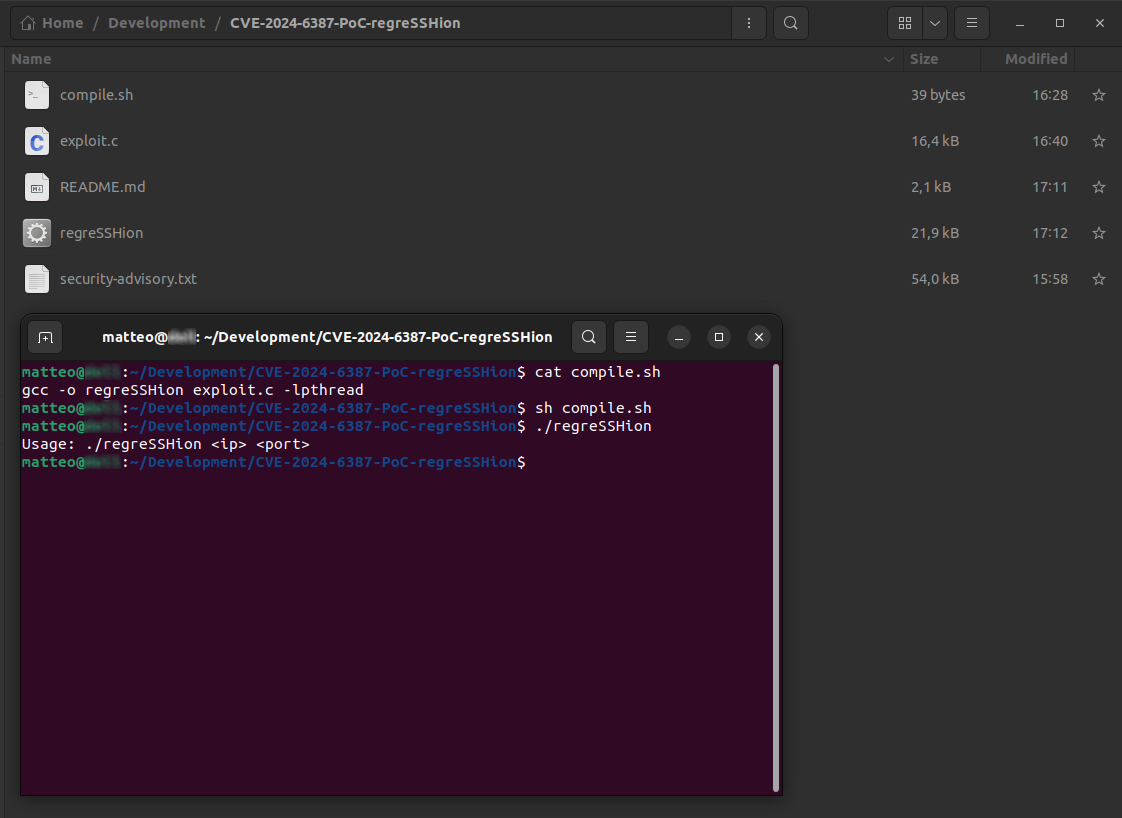 xonoxitron/regresshion
CVE-2024-6387 (regreSSHion) Exploit (PoC), a vulnerability in OpenSSH's server (sshd) on glibc-based Linux systems.
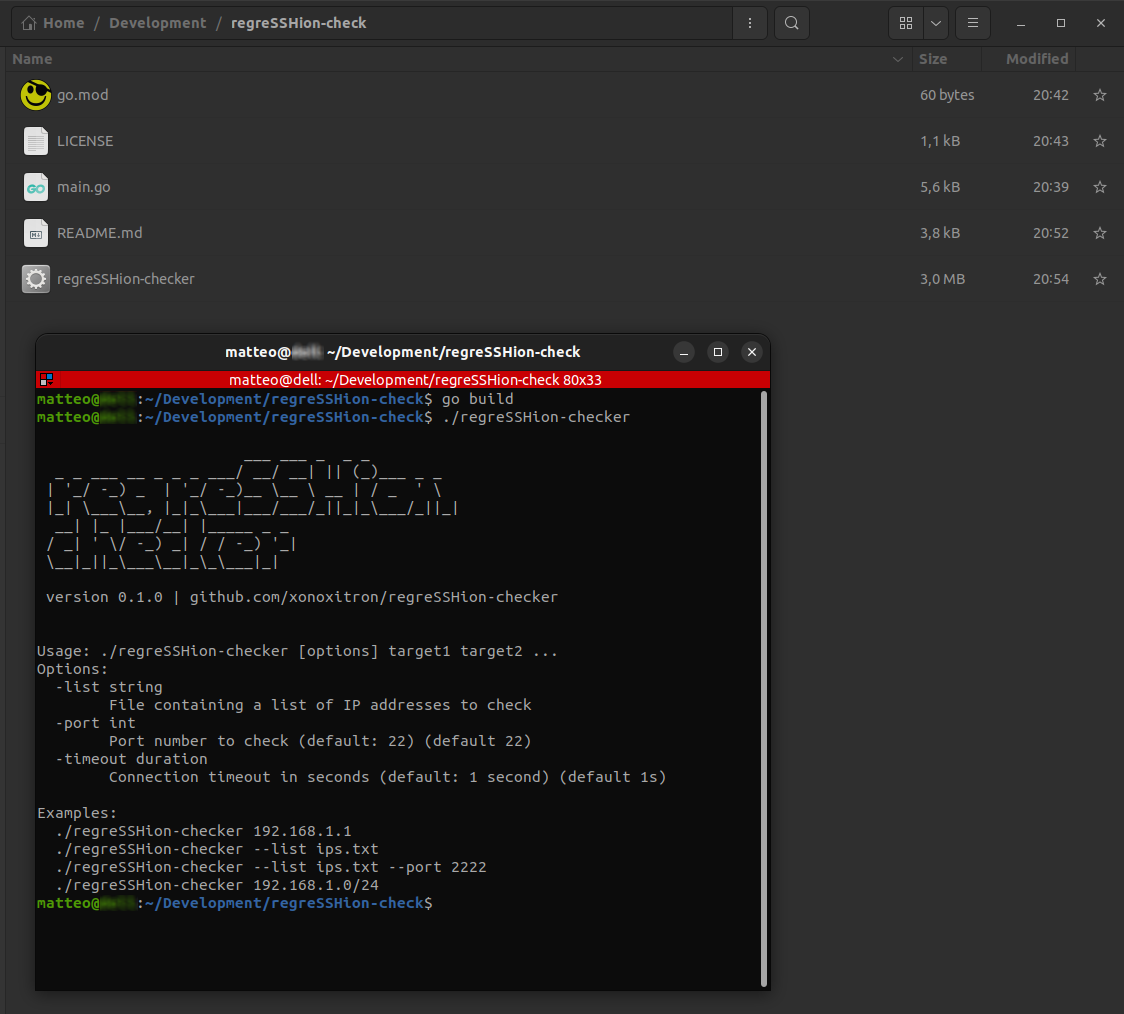 xonoxitron/regresshion-checker
Quickly identifies servers vulnerable to OpenSSH 'regreSSHion' (CVE-2024-6387).
 lockness-ko/xz-vulnerable-honeypot
An ssh honeypot with the XZ backdoor. CVE-2024-3094
 s1d6point7bugcrowd/cve-2024-6387-race-condition-in-signal-handling-for-openssh
Technical analysis and proof-of-concept for CVE-2024-6387, a race condition in OpenSSH signal handling enabling unauthenticated remote code execution…
 ferasalrimali/cve-2024-6387-poc
SSHd cve-2024-6387-poc
 lflare/cve-2024-6387-poc
MIRROR of the original 32-bit PoC for CVE-2024-6387 "regreSSHion" by 7etsuo/cve-2024-6387-poc
 passwa11/cve-2024-6387-poc
Proof-of-concept exploit for CVE-2024-6387, a signal handler race condition in OpenSSH's sshd, enabling remote code execution on vulnerable servers.
 t3rry327/cve-2024-6387-poc
Exploit for CVE-2024-6387 targeting a signal handler race condition in OpenSSH sshd on glibc-based Linux systems, enabling remote code execution as…
 zgzhang/cve-2024-6387-poc
a signal handler race condition in OpenSSH's server (sshd)
 dimamend/cve-2024-6387-poc
Exploit for CVE-2024-6387, a signal handler race condition in OpenSSH sshd, enabling remote code execution as root on glibc-based Linux systems.