
CVE-2026-26980
 yym8538/cve-2026-26980
Python PoC and Docker lab demonstrating unauthenticated SQL injection in TryGhost Ghost CMS Content API slug filter, extracting database values via a…
database-securityeducationexploitation+5
1
yym8538/cve-2026-26980Python PoC and Docker lab demonstrating unauthenticated SQL injection in TryGhost Ghost CMS Content API slug filter, extracting database values via a…
 muhammedhussein17/keycloak
Security research disclosing CVE-2026-9794, an unauthenticated client ID enumeration flaw in Keycloak SAML ECP via faultstring oracle, fixed in…
 plur1bu5/gitread
CVE-2026-85706 · GitLab CE/EE unauthenticated file read · research PoC with oracle mode, fd enumeration, and tiered loot targeting
 faceless0x7/cve-2026-89012
Python exploit for CVE-2026-89012, a Dolibarr SQL filter denylist bypass that uses a blind-boolean oracle to extract password hashes and API keys via…
 mhtsec/cve-2026-85706
Python PoC for CVE-2026-85706, an unauthenticated path traversal in GitLab CE/EE Repository Commits API that leaks arbitrary local files via a…
 hunt-benito/the-callback-that-outlived-the-page-cve-2026-78997-uc-browser-android-universal-xss
PoC for CVE-2026-78997, a Universal XSS in UC Browser for Android. Includes a crafted URL builder, a callback-dispatch oracle, and Frida hooks to…
 horkimhab/cve-2026-13181-cve-2026-13182-cve-2026-13183-cve-2026-13184
Educational proof-of-concept for Telerik padding oracle vulnerabilities (CVE-2026-13181-184) with scripts for authorized security testing and…
 rabbitmask/weblogicscan
Automated vulnerability scanner for Oracle WebLogic Server, detecting historical CVEs including deserialization, SSRF, and arbitrary file upload with…
 jwa7470/2025-oracle-sso-ldap-attack-post-incident-written-report
Post-incident report analyzing the Oracle Cloud SSO/LDAP supply chain attack (CVE-2021-35587). Details the exploitation of legacy server…
 hyderpwn/weblogic
Unauthenticated authentication bypass and remote code execution exploit for Oracle WebLogic Server, targeting CVE-2020-14882 and CVE-2020-14750.
 zeetee1235/cve-2026-21962
Verified PoC and analysis for CVE-2026-21962, an access-control bypass in Oracle HTTP Server/WebLogic Proxy Plug-in via URI normalization…
 samael0x4/cve-2026-21962
Unauthenticated vulnerability that may allow remote attackers to compromise confidentiality and integrity, potentially leading to full system…
 philfry/cve-2026-31431-ftrace
Kernel module using ftrace to block AF_ALG/AEAD requests, mitigating CVE-2026-31431 without requiring LSM BPF. Provides logging and easy compilation…
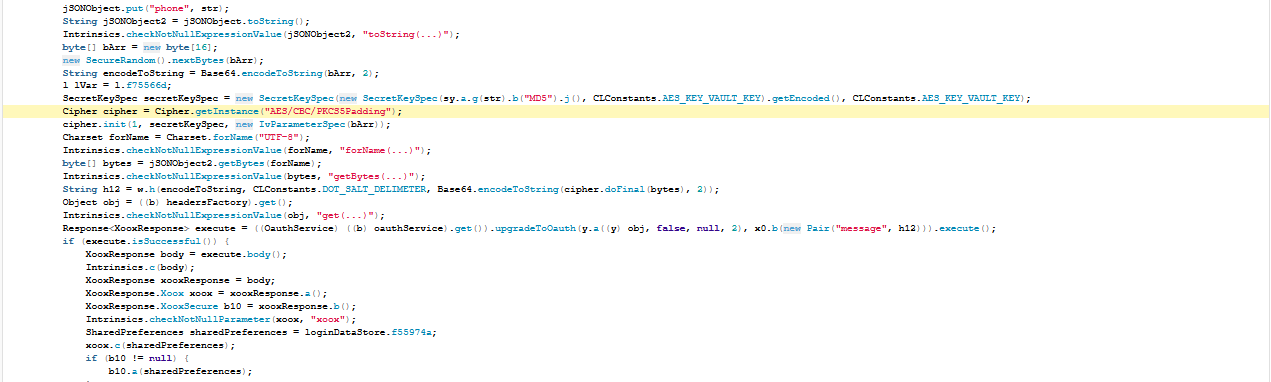 honestcorrupt/meesho-android-improper-encryption-cve-2026-5682
Proof of concept demonstrating insecure AES-CBC encryption with MD5 key derivation in the Meesho Android app, enabling ciphertext tampering and…
 gregk4sec/cve-2026-21962
Proof-of-concept exploit for CVE-2026-21962, a critical path traversal vulnerability in Oracle OHS and WebLogic Server proxy plugins leading to…
 gregk4sec/cve-2026-21962-o
Proof-of-concept for CVE-2026-21962, a critical unauthenticated remote vulnerability in Oracle HTTP Server and WebLogic Proxy Plug-in, demonstrating…
 g0w6y/cve-2026-21994
Proof-of-concept exploit for CVE-2026-21994, demonstrating unauthenticated admin session forgery via a hardcoded Flask SECRET_KEY and SSH host…
 emad-almousa/cve-2021-2175
Proof-of-concept exploit for CVE-2021-2175, an Oracle Database Vault metadata exposure vulnerability, demonstrating unauthorized access to sensitive…