
Agent-Reach
 panniantong/agent-reach
Give your AI agent eyes to see the entire internet. Read & search Twitter, Reddit, YouTube, GitHub, Bilibili, XiaoHongShu — one CLI, zero API fees.
ai-securitycrawlergeneral-purpose-utilities+5
82.4k
panniantong/agent-reachGive your AI agent eyes to see the entire internet. Read & search Twitter, Reddit, YouTube, GitHub, Bilibili, XiaoHongShu — one CLI, zero API fees.
 vighnesh91/omnisec-hex
Browser-local security monorepo with six modules for mobile APK/IPA triage, client-side DAST fuzzing, OSINT directories, offline AI threat scoring,…
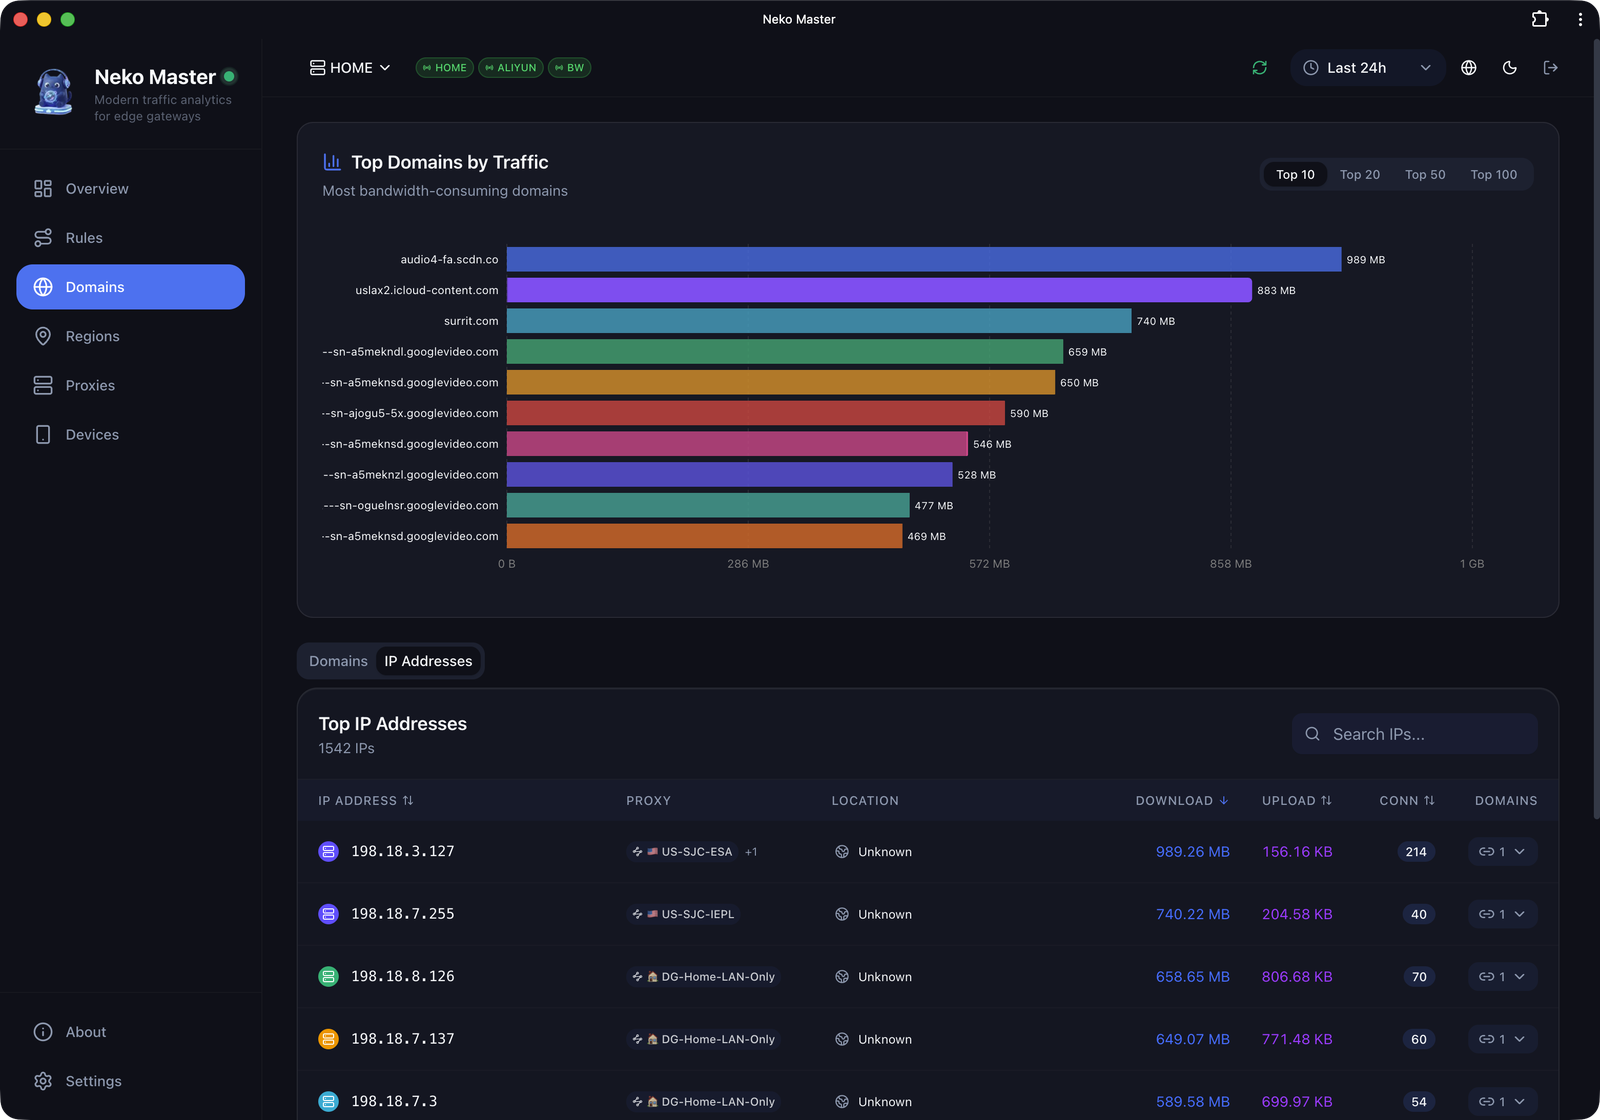 foru17/neko-master
A modern and elegant dashboard for network traffic visualization and analysis.
 ekitji/siem
Curated SIEM queries and techniques for offensive discovery of Windows privilege escalation, misconfigured ACLs, services, scheduled tasks, and…
 trustedsec/rage
Vendor-neutral NDJSON attack-graph format with node/edge taxonomy, AWS/GCP/Azure mappings, derivation rules, and an exposure DB for offensive…
 mr-redoo7/cve-2026-27739-poc
Python PoC exploiting CVE-2026-27739 in Angular SSR: header injection via prototype pollution and SSRF chaining to AWS IMDS/GCP metadata for…
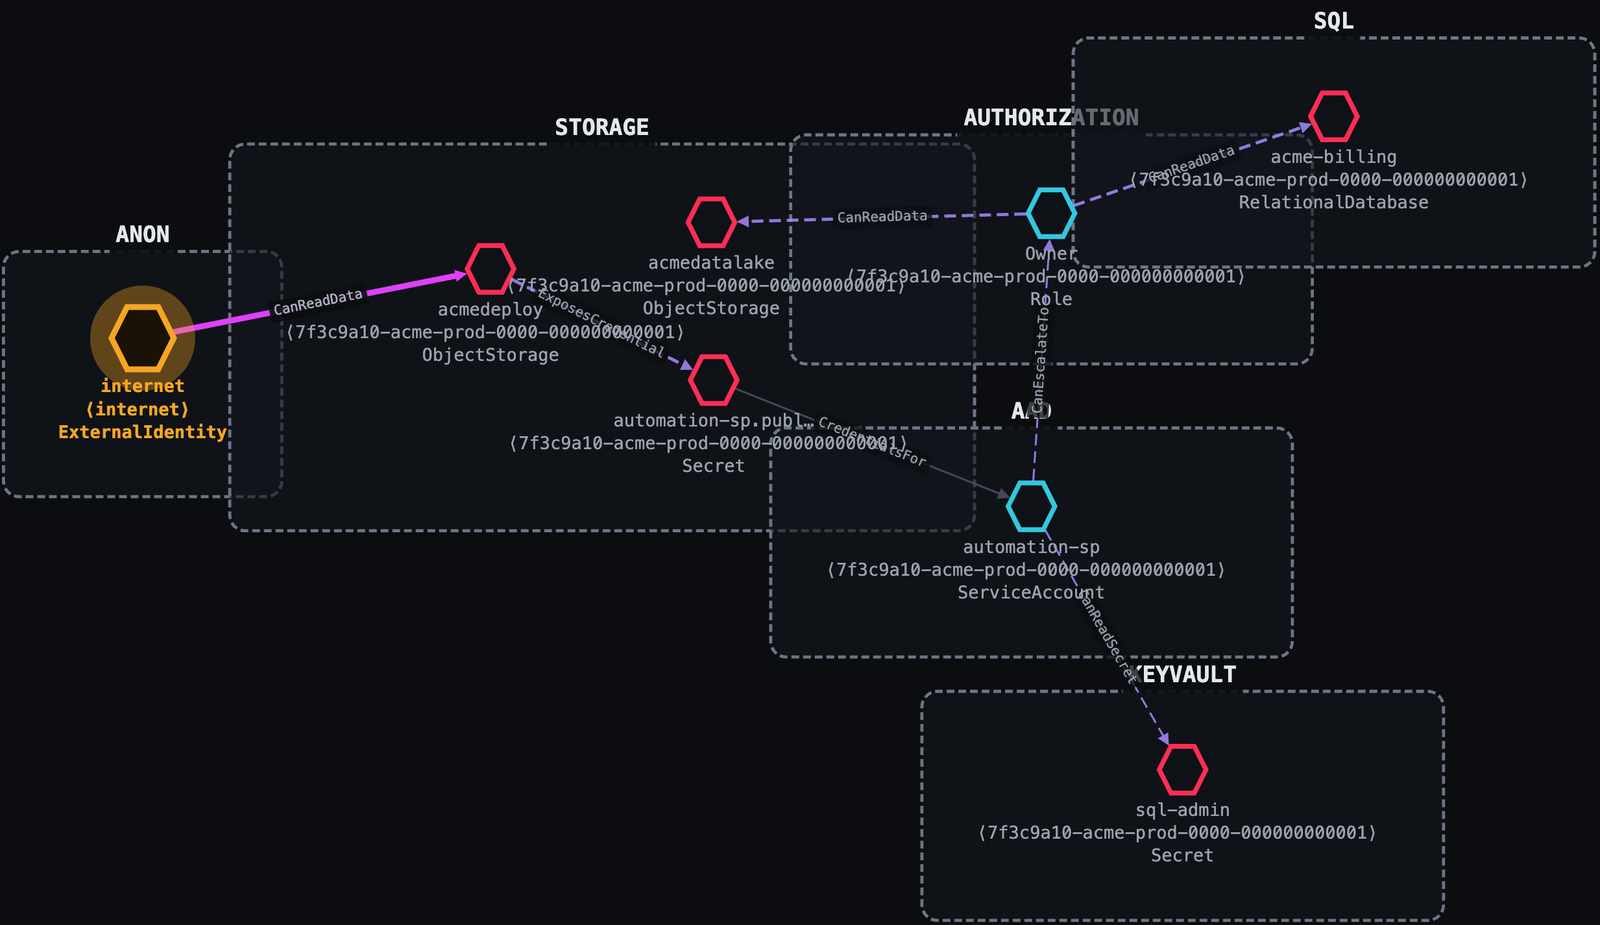 ustayready/thunderstorm
A collector and derivation engine. It maps your environment, evaluates effective permissions and trust, and writes a complete attack graph as a…
 murrez/cve-2026-12793
Python PoC scanner and exploit for CVE-2026-12793, an unauthenticated privilege escalation in JetFormBuilder <=3.6.2 that creates WordPress admin…
 yairhinkis/cve-2026-56096
Proof of concept and technical write-up for CVE-2026-56096, a blind Solr query injection in TYPO3 EXT:solr enabling unauthenticated field enumeration…
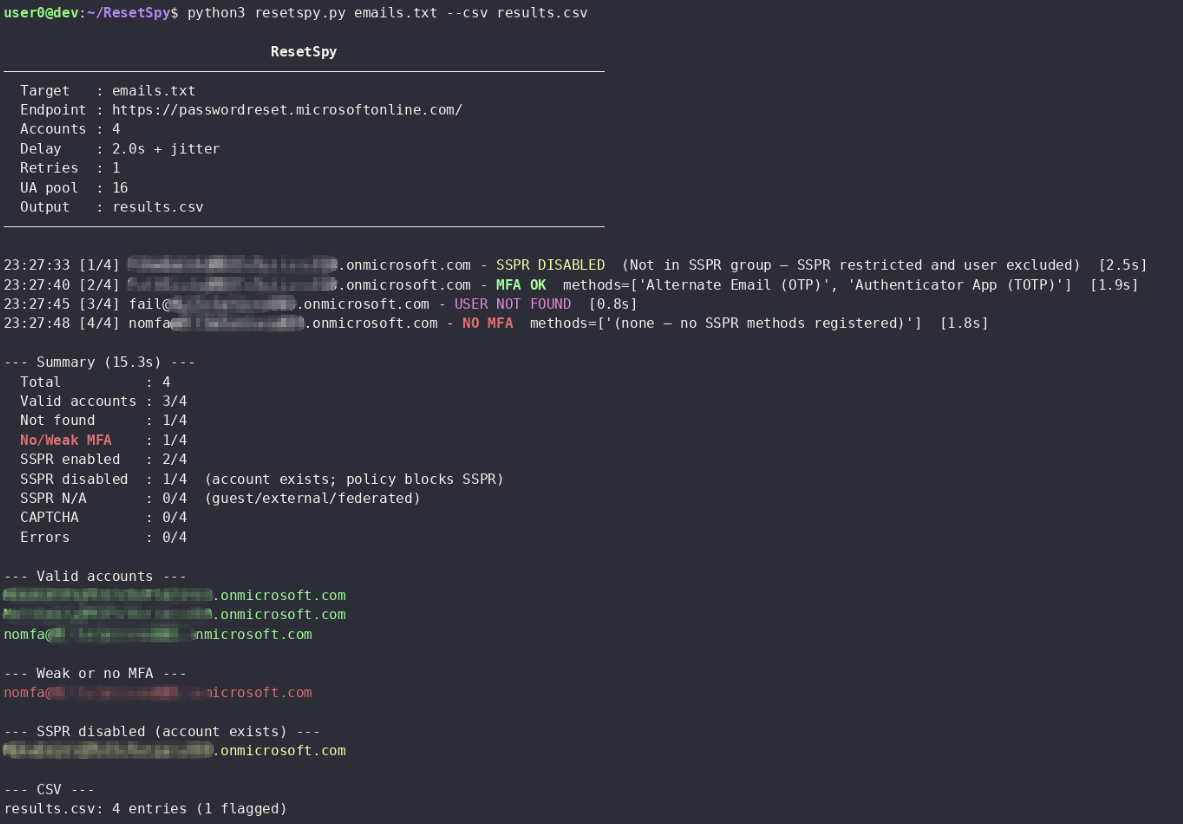 mlcsec/resetspy
Enumerate user accounts and registered authentication methods via the Microsoft Self-Service Password Reset (SSPR) portal
 clickswave/limeyard
Deliberately vulnerable Docker lab with a routable DNS estate and machine-readable answer keys per target, scoring scanner precision, recall and…
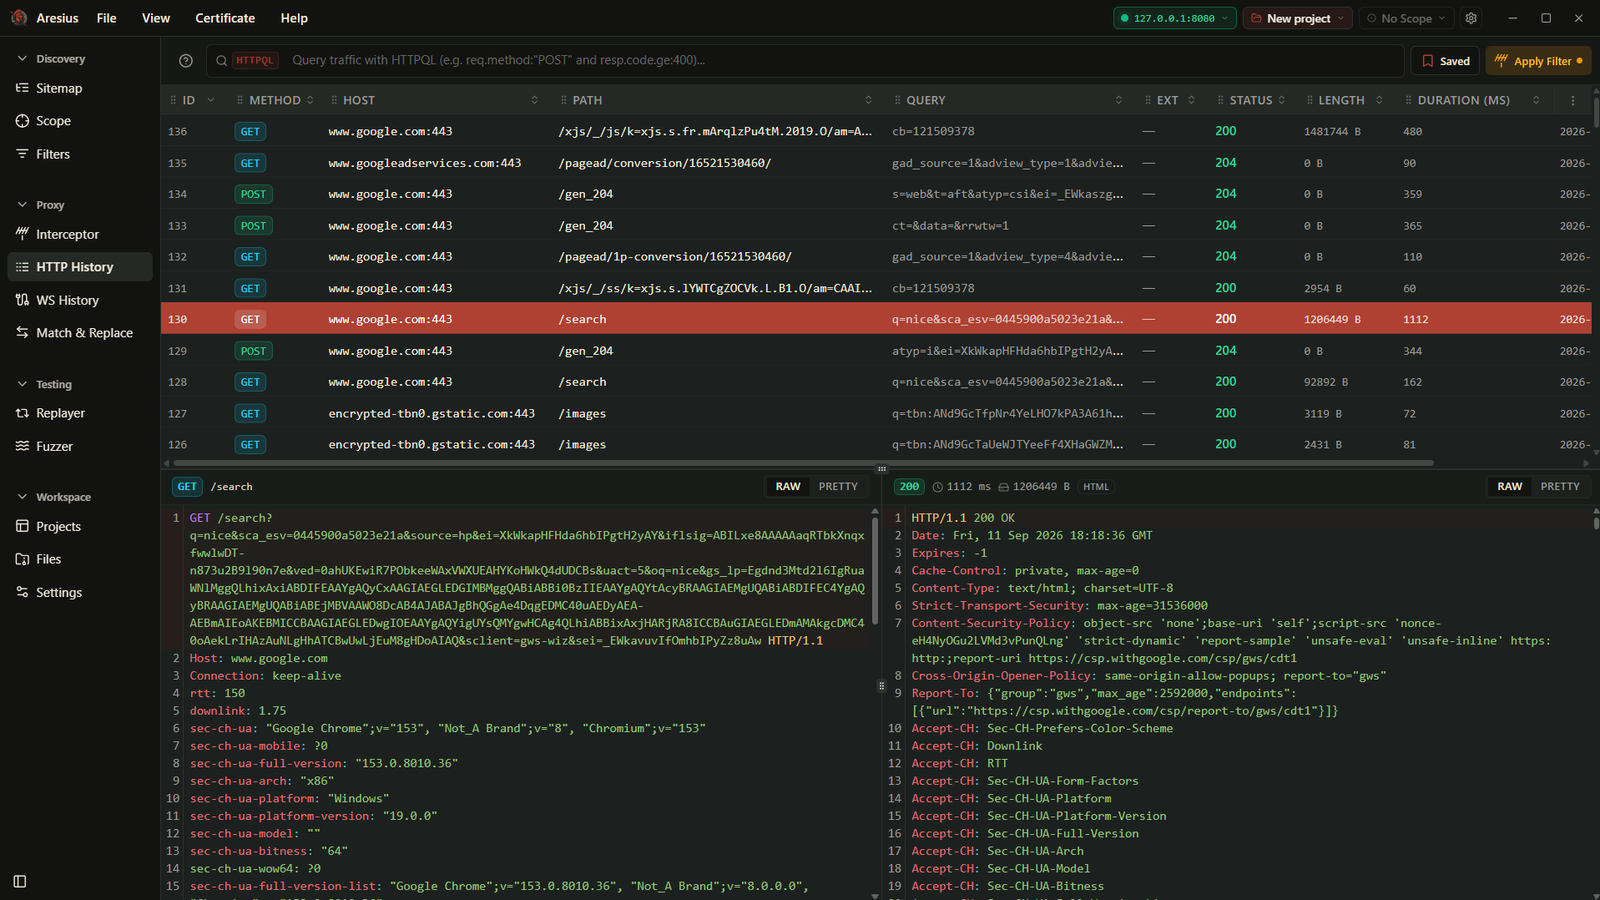 0xmarik/aresius
Native HTTP/HTTPS interception proxy for penetration testers and bug bounty hunters with live request tampering, request replay, high-speed fuzzing,…
 kashyapghodasara/public_exploit-1--wordpress-cve-2021-29447
CVE-2021-29447 is an authenticated XML External Entity (XXE) vulnerability in WordPress
 anirbala98/cve-2025-57231
Python PoC exploit for CVE-2025-57231, an unauthenticated path traversal in Docmost < 0.22.0 that reads arbitrary files via the avatar endpoint.
 ethan-andrews/threatintel-aggregator
Self-hosted threat intelligence platform — feed aggregation, AI triage, MITRE ATT&CK coverage, and Sentinel-integrated detection engineering. Runs…
 duggytuxy/data-shield_ipv4_blocklist
Curated IPv4 blocklist of malicious addresses, refreshed every 6 hours for firewall and WAF ingestion, with split lists and CTI-ready formats for…
 bardlaudian/cve-2025-24071
Dependency-free Python PoC generator for CVE-2025-24071 that crafts a malicious .library-ms file in a ZIP to trigger Windows Explorer NTLM hash…
 pbxqdown/portclue
Explain why a Linux TCP port may or may not be reachable