
CVE-2026-84753
 abraxas/cve-2026-84753
Proof-of-concept exploit and lab for CVE-2026-84753, an unauthenticated PHP Object Injection in Mail Mint <= 1.31.0 via the mint-form-submit REST…
exploitationlabs-practicepenetration-testing+3
abraxas/cve-2026-84753Proof-of-concept exploit and lab for CVE-2026-84753, an unauthenticated PHP Object Injection in Mail Mint <= 1.31.0 via the mint-form-submit REST…
 axedos/cve-2026-67401
Python proof-of-concept for CVE-2026-67401, an authenticated SQL injection in cPanel EmailTrack that allows arbitrary file write as root via SQLite…
 apache/spamassassin
Open-source email filtering framework that detects spam and phishing using content analysis, header checks, Bayesian scoring, and DNS blocklists.
 mail-in-a-box/mailinabox
Mail-in-a-Box helps individuals take back control of their email by defining a one-click, easy-to-deploy SMTP+everything else server: a mail server…
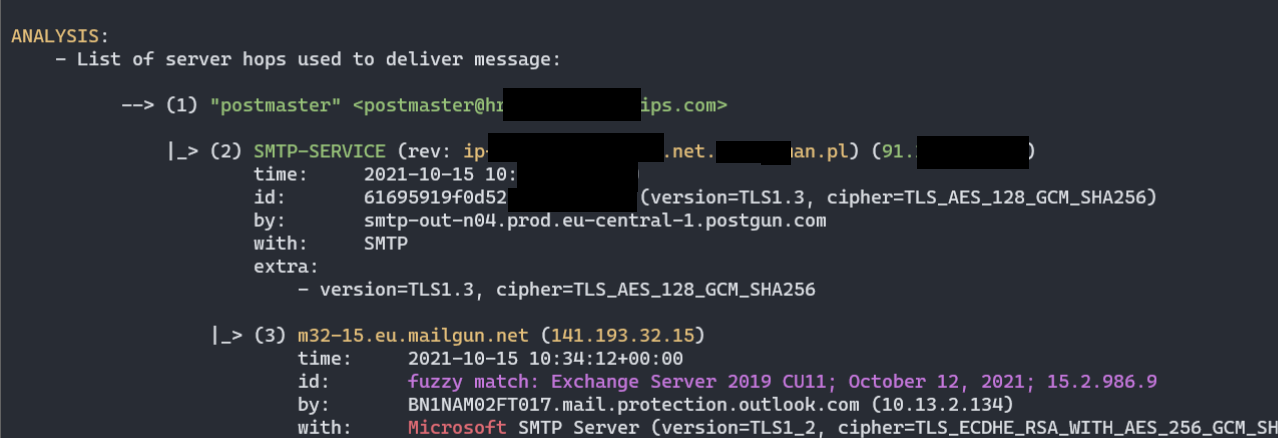 mgeeky/decode-spam-headers
A script that helps you understand why your E-Mail ended up in Spam
 george0papasotiriou/cve-2026-11113-smtp-header-injection-in-contact-form
Proof-of-concept exploit for CVE-2026-11113, demonstrating SMTP header injection in a Flask contact form via unsanitized email input; includes…
 george0papasotiriou/cve-2026-8080-dkim-signature-verification-bypass-header-canonicalization-flaw-
Simulated Python demonstration of CVE-2026-8080 DKIM verification bypass, showing how non-compliant header canonicalization lets attackers inject…
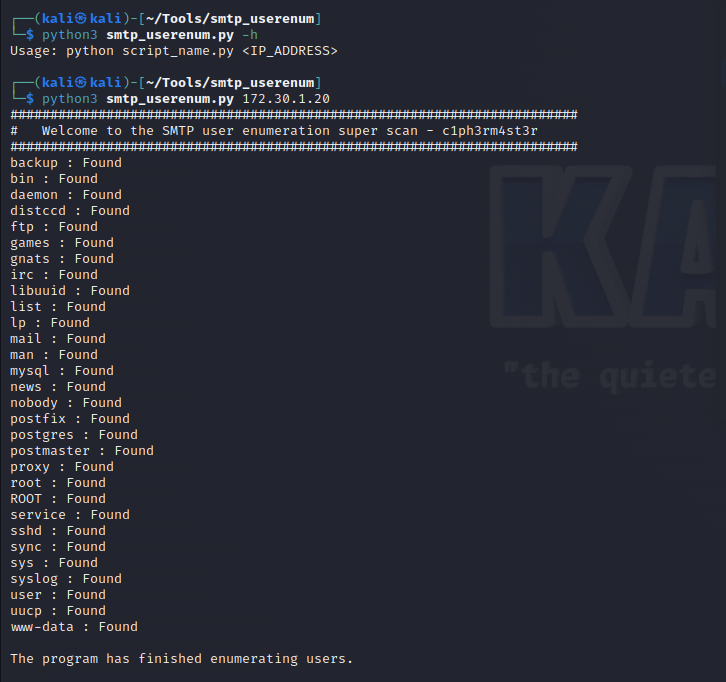 h3x0v3rl0rd/smtp_userenum
Python script for enumerating SMTP users by leveraging VRFY and EXPN commands to identify valid email accounts on a target mail server.
 cappricio-securities/socialengineering
SEt framework
 hackerxphantom/spoof_anymail
Most Powerful Send Fake Mail Using Any Mail I'd undetectable
 p0dalirius/cve-2016-10956-mail-masta
MailMasta wordpress plugin Local File Inclusion vulnerability (CVE-2016-10956)
 vrikodar/cve-2003-0264_exploit
Buffer Overflow in Seattle Lab Mail (SLmail) 5.5 - POP3
 cr4ckc4t/cve-2022-41352-zimbra-rce
Zimbra <9.0.0.p27 RCE
 hackhoven/wp-mail-masta-exploit
Exploit script for WordPress Plugin Mail Masta 1.0 - CVE-2016-10956
 niandy/nginx-patch
nginx 1.15.10 patch against cve-2021-23017 (ingress version)
 ktn1990/cve-2024-8425
The WooCommerce Ultimate Gift Card plugin for WordPress is vulnerable to arbitrary file uploads.
 t0kx/exploit-cve-2016-9920
Roundcube 1.0.0 <= 1.2.2 Remote Code Execution exploit and vulnerable container
 rootdirective-sec/cve-2026-8206-lab
Local Docker lab demonstrating CVE-2026-8206 unauthenticated account takeover in Kirki WordPress plugin. Compares vulnerable 6.0.6 vs patched 6.0.7…