
Get-NetNTLM
 elnerd/get-netntlm
Powershell module to get the NetNTLMv2 hash of the current user
hash-analysisinformation-gatheringpassword-attacks+4
974 years ago
elnerd/get-netntlmPowershell module to get the NetNTLMv2 hash of the current user
 ajnik/joomla-bruteforce
Python script that brute-forces Joomla administrator login credentials using wordlists, with proxy and verbose options for penetration testing.
 golem445/corporate_masks
8-14 character Hashcat masks based on analysis of 3.2 million NTLM hashes cracked while pentesting
 star-sg/random-scripts
Collection of DFIR and OSINT Python scripts for parsing malicious LNK samples, extracting OLE objects from MHTML, and hashing favicons to hunt…
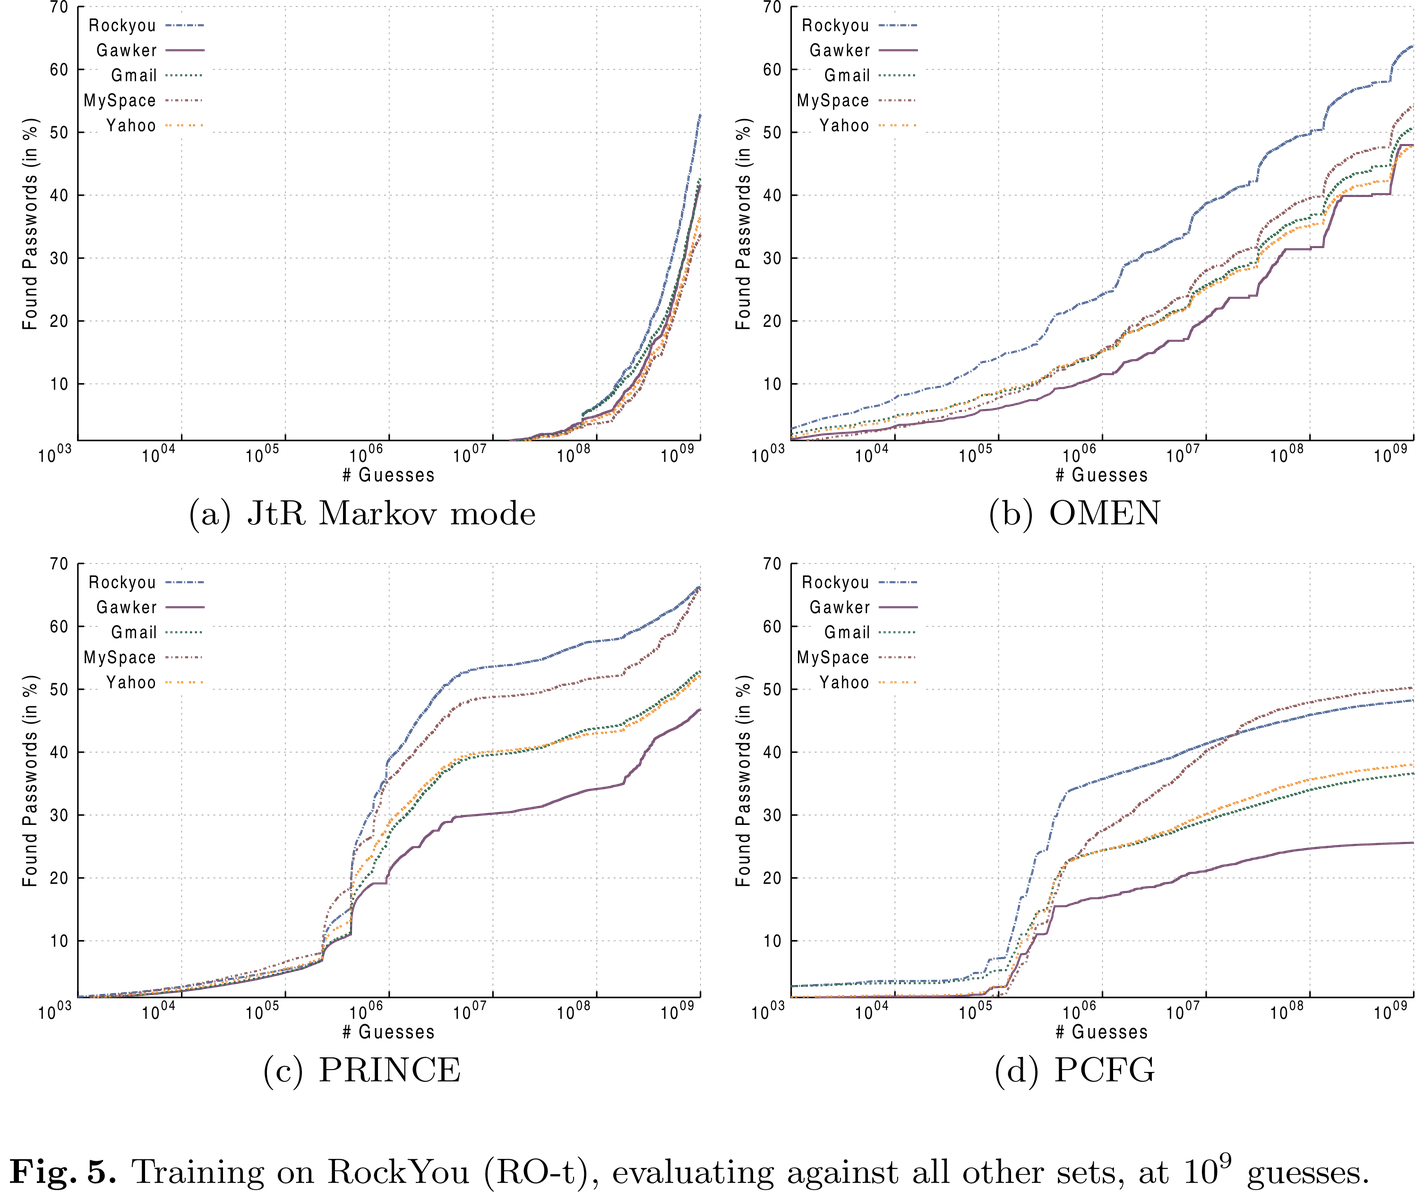 rub-syssec/omen
Markov model-based password guesser in C that enumerates candidates by probability, generating most likely passwords first for hash cracking via…

 jankoboy88/higernes
a passive OSINT toolkit in python - usernames, emails, domains, ips, phones, hashes. no keys, no logins.
 vqkro/higernes
a passive OSINT toolkit in python usernames, emails, domains, ips, phones, hashes. no keys, no logins.
 nu11secur1ty/kousei
Python/Go framework that generates SQL injection PoC requests, automates sqlmap attacks, and manages modular exploit scripts with parameter detection…
 qsecure-labs/deadmatter
Offset Independent Credential Extraction Tool
 z3rodayhacks/cve-2026-63030-cve-2026-60137
Pre-auth RCE proof-of-concept chaining a WordPress REST batch API auth bypass with WP_Query SQL injection to dump hashes, add admin users, or plant a…
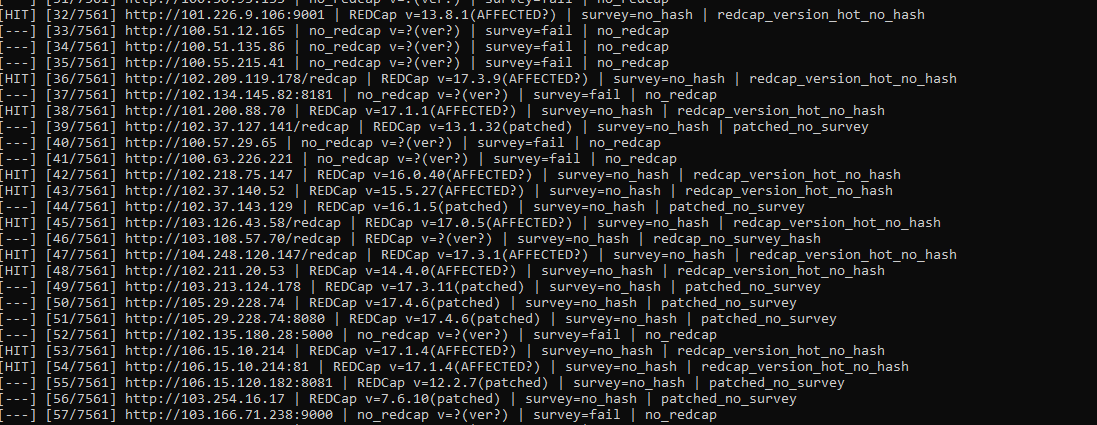 farih123/cve-2026-90817
Python checker and configurable exploit hook for CVE-2026-90817, fingerprinting REDCap instances, validating survey hashes, and probing __passthru…
 grepstrength/cve-2026-92680
Proof-of-concept decrypting Araxis Merge's DPAPI-protected server credentials (CVE-2026-92680), demonstrating insufficiently protected credential…
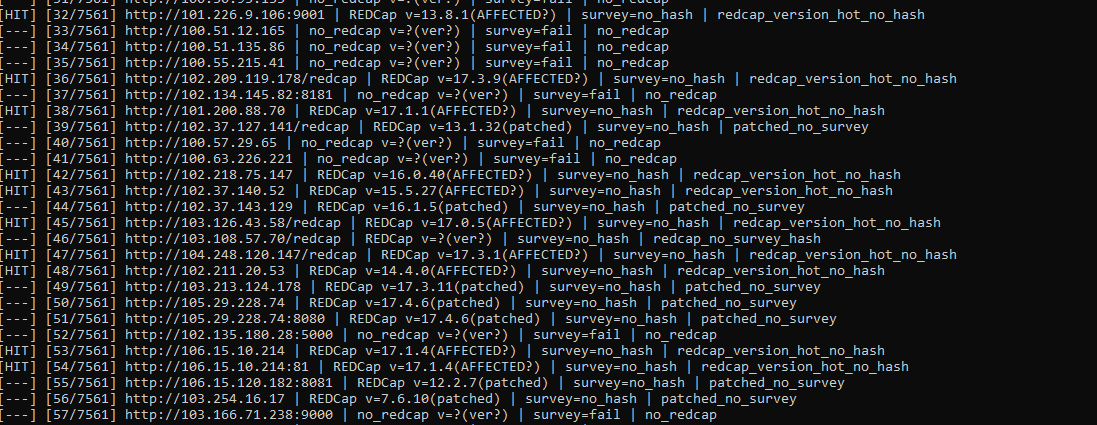 yulisec/cve-2026-90817
Python checker and configurable exploit hook for CVE-2026-90817, a REDCap survey passthru and data import RCE. Fingerprints versions, validates…
 4nner/cve-2019-9053
Python 3 exploit for CVE-2019-9053, a CMS Made Simple SQL injection vulnerability, enabling credential extraction via time-based blind SQLi and…
 pczbuilds/monikerlink-cve-2024-21413-writeup
Writeup of TryHackMe's Moniker Link room, exploiting CVE-2024-21413 to bypass Outlook Protected View and capture NTLMv2 hashes via crafted Moniker…
 faceless0x7/cve-2026-89012
Python exploit for CVE-2026-89012, a Dolibarr SQL filter denylist bypass that uses a blind-boolean oracle to extract password hashes and API keys via…
 abdaullahag/threatlens
Python CLI tool for rapid IOC analysis (IPs, Domains, CVEs) using 6 free Threat Intel APIs. Outputs: Color-coded Excel, JSON, CSV. Uses: VT, Shodan,…
 zhairiazzeddine/exploit-cve-2023-6063-poc-vuln
Python PoC for CVE-2023-6063, an unauthenticated time-based blind SQL injection in WP Fastest Cache <=1.2.2, extracting WordPress password hashes and…