
libextractor-privesc
 haitam-lazaar/libextractor-privesc
Proof-of-concept for CVE-2026-100310, a local privilege escalation in GNU libextractor ≤1.15 via the LIBEXTRACTOR_PREFIX untrusted search path, with…
binary-exploitationeducationexploitation+3
haitam-lazaar/libextractor-privescProof-of-concept for CVE-2026-100310, a local privilege escalation in GNU libextractor ≤1.15 via the LIBEXTRACTOR_PREFIX untrusted search path, with…
 nurupo/rootkit
Linux kernel module that grants root privileges, hides processes/files, and protects itself from unloading, designed for educational purposes on…
 vanhoefm/krackattacks-scripts
Scripts to verify WPA2 clients and APs for KRACK key reinstallation vulnerabilities using modified hostapd and monitor-mode frame replay.
 sensepost/hostapd-mana
SensePost's modified hostapd for wifi attacks.
 cappricio-securities/wifispammer
A nodemcu powered wifi spammer
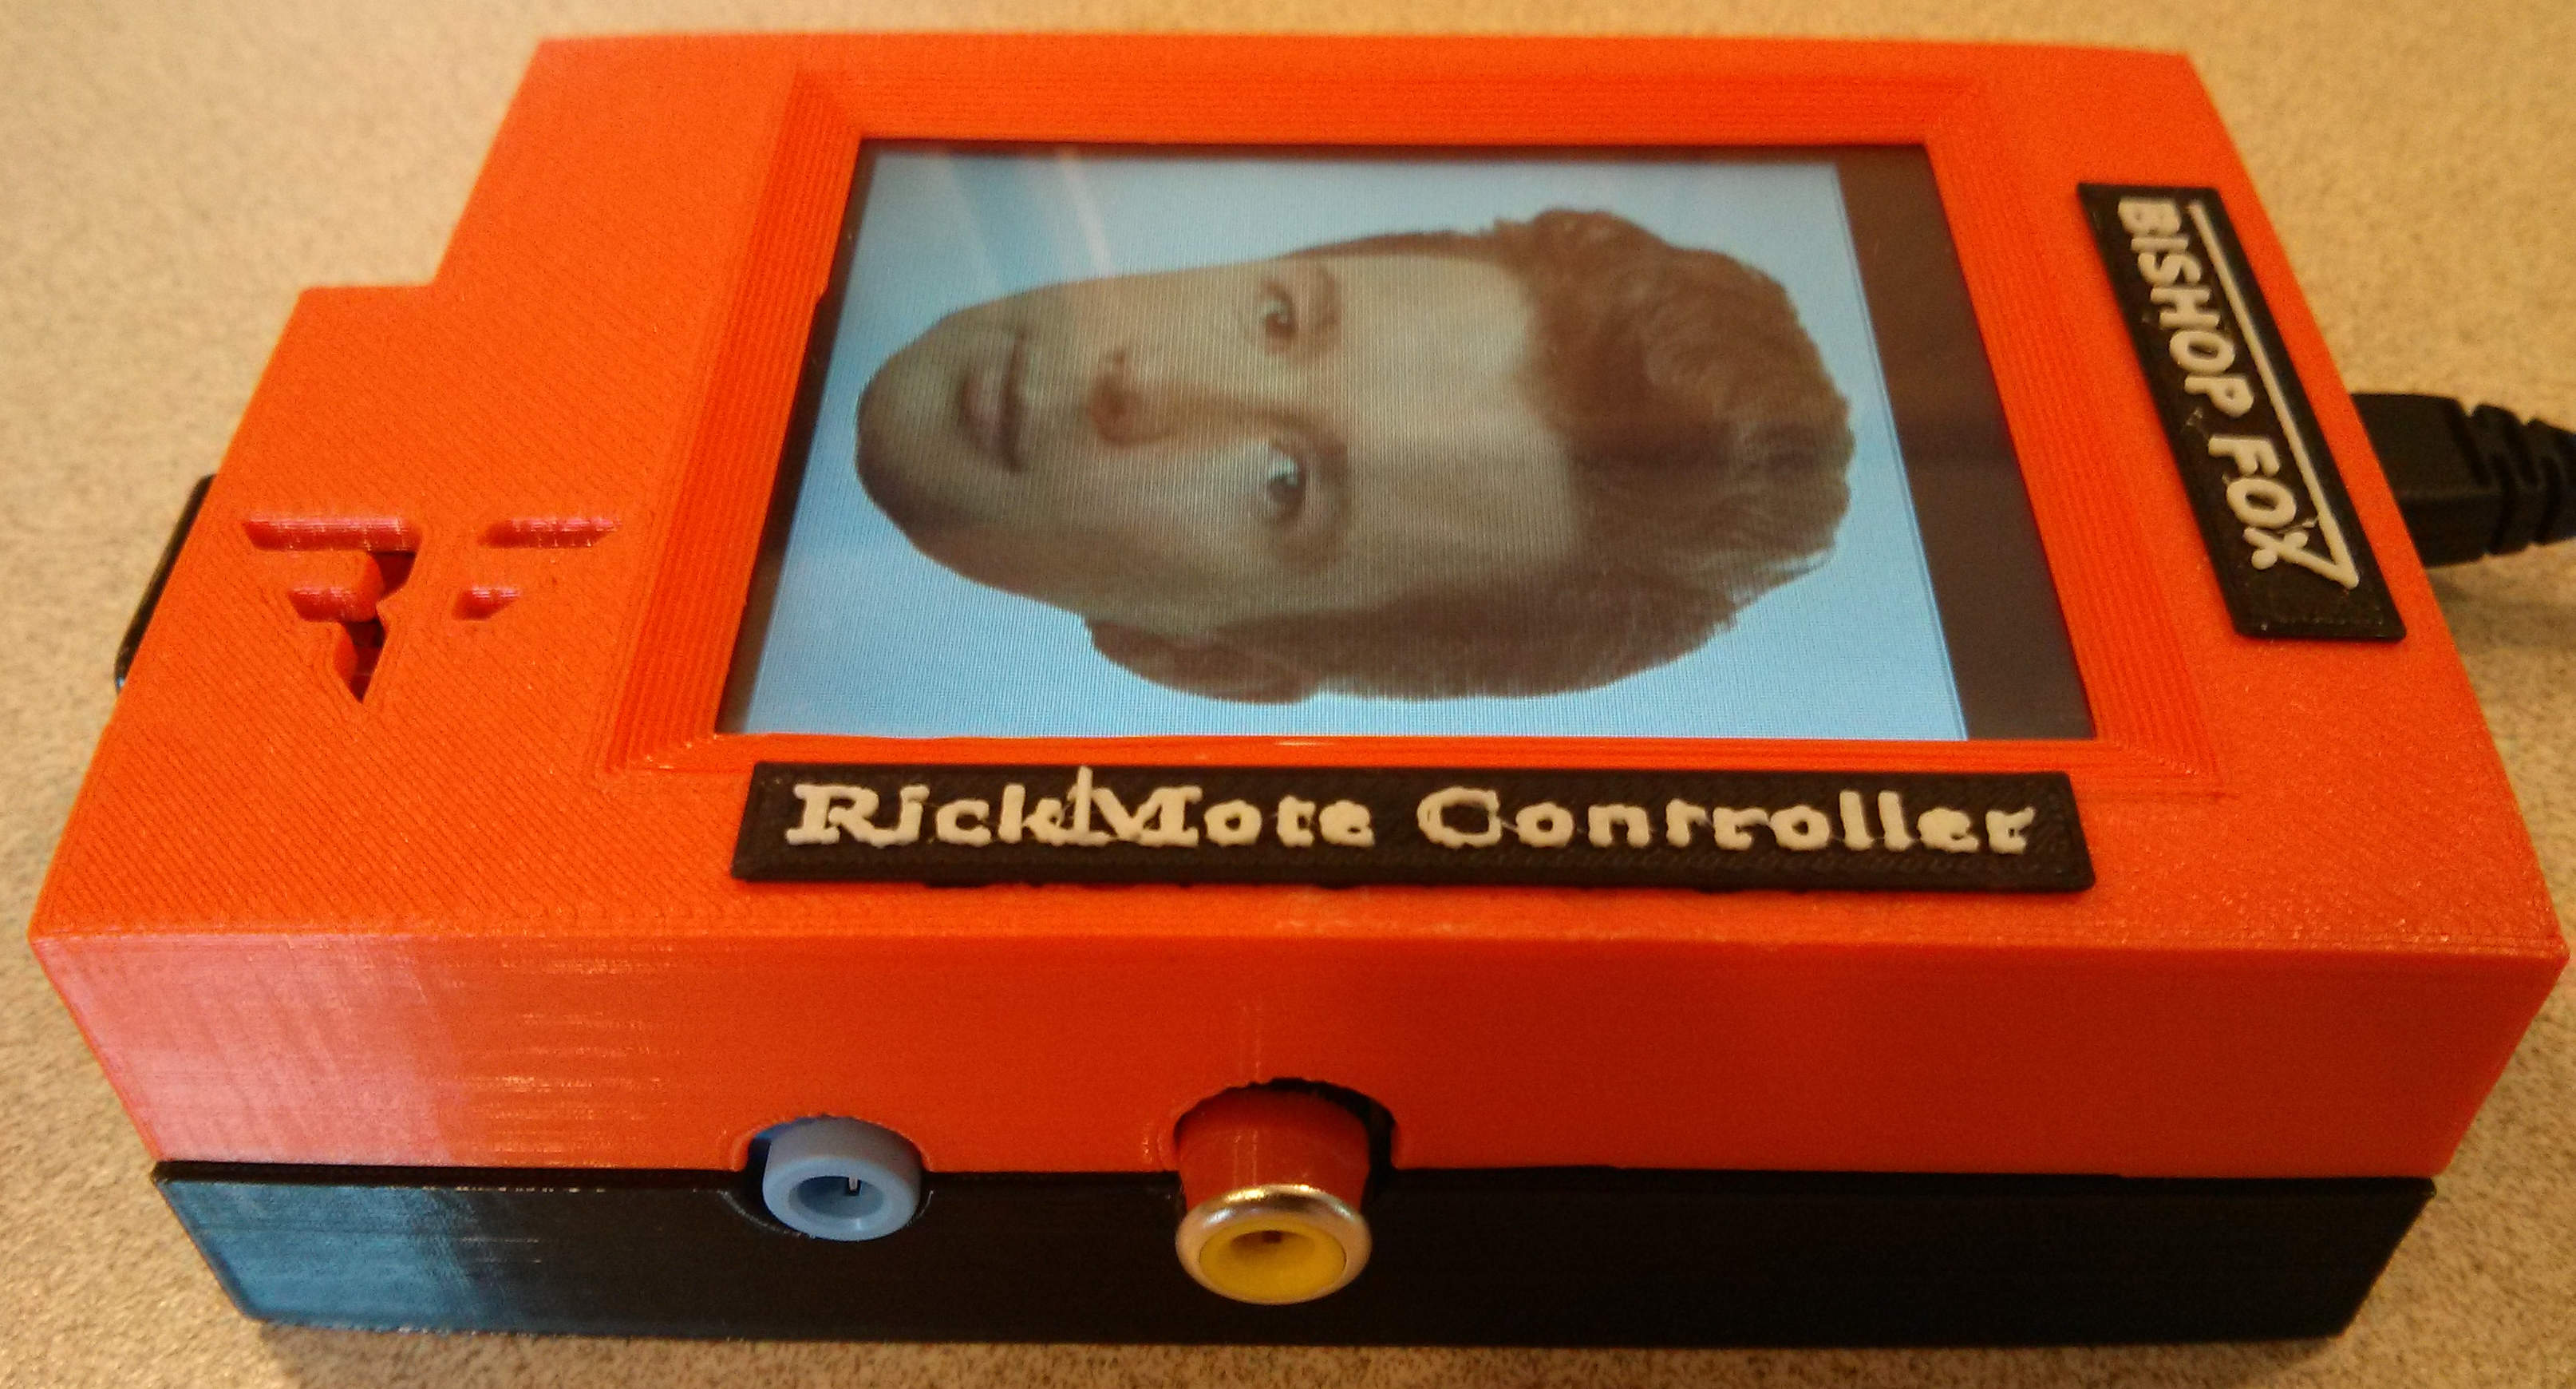 bishopfox/rickmote
The Rickmote Controller: Hijack TVs using Google Chromecast
 nanopathi/wpa_supplicant_8_cve-2021-0326.
Implementation of wpa_supplicant and hostapd with documented CVE-2021-0326 vulnerability, intended for security research and vulnerability analysis.
 jmalinen/hostap
Clone of w1.fi hostap.git - NOTE: This is not the main development location and pull requests for this repository are ignored. See the upstream…
 sensepost/snoopy
Snoopy: A distributed tracking and data interception framework
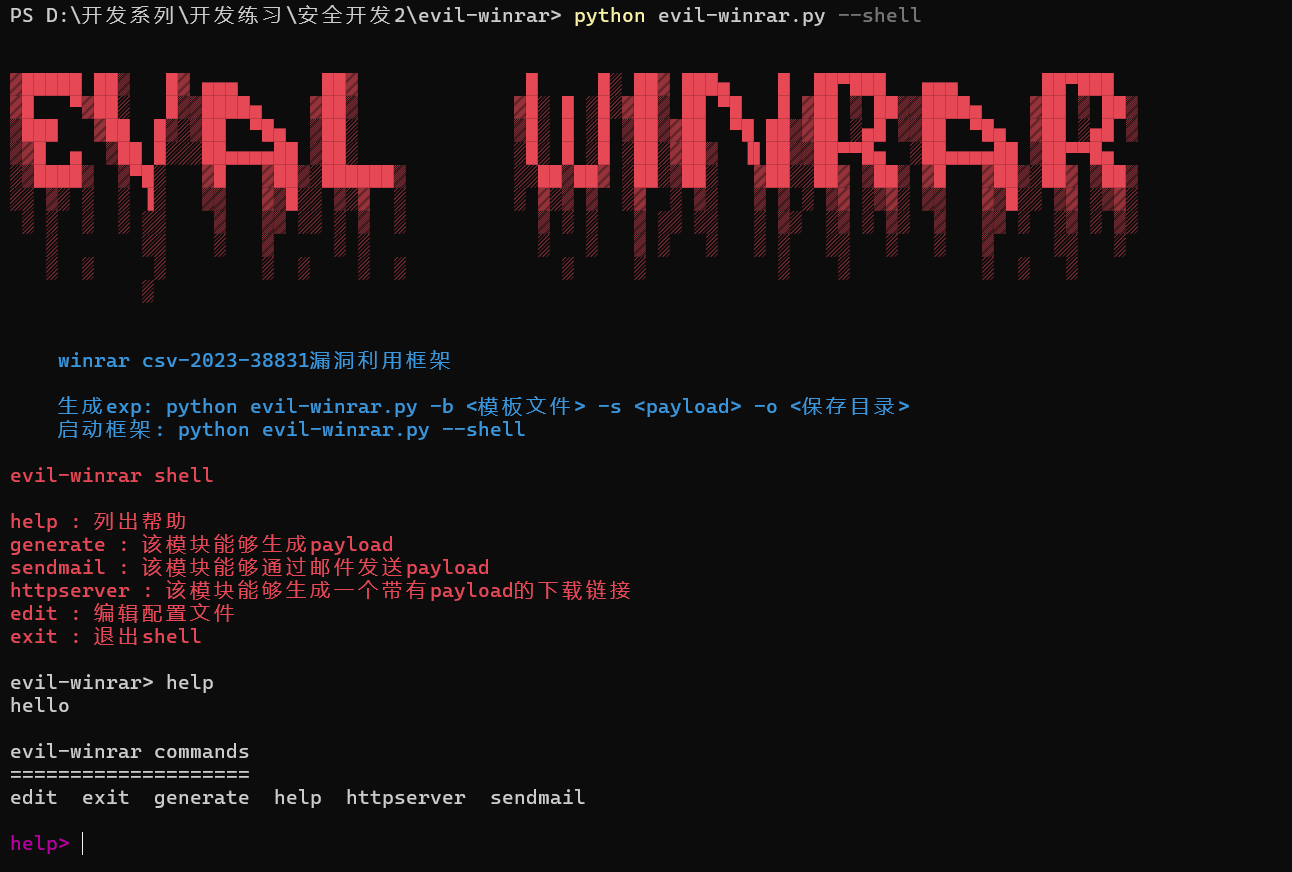 youmulijiang/evil-winrar
evil-winrar,CVE-2023-38831漏洞利用和社会工程学攻击框架 (evil-winrar, CVE-2023-38831 Vulnerability Exploitation and Social Engineering Attack Framework)
 kienhosd/wp-file-manager-exploit-cve-2020-25213-with-zerologon
Exploit Windows server 2019 vulnerable to Zerologon with Garble, Chisel, wp-file-manager vulnerability (have video demo)
 fa1c0n35/cve-2023-38831-winrar-exploit
Python-based exploit generator for CVE-2023-38831 WinRAR vulnerability. Creates malicious RAR archives with bait files (PDF, images) and payload…
 hydragyrum/evil-rmi-server
An evil RMI server that can launch an arbitrary command. May be useful for CVE-2021-44228
 dougburks/so-crates
SO-CRATES: Security Onion Containerized Rapid Analysis of Threats, Evil, and Sus!
 ngothienan/cve-2023-38831
Python-based exploit generator for CVE-2023-38831 (WinRAR remote code execution). Creates malicious RAR archives with bait files and payload scripts…
 jonathanwilbur/cve-2019-5010
CVE-2019-5010 Exploit PoC - Python Denial of Service via Malformed X.509v3 Extension
 t43wiu6/cve-2019-0887
exp for CVE-2019-0887