active-scan-plus-plus

Burp Suite extension that extends active and passive scanning with checks for host header attacks, XXE, code injection, and known CVEs like…

Burp Suite extension that extends active and passive scanning with checks for host header attacks, XXE, code injection, and known CVEs like…

a passive OSINT toolkit in python - usernames, emails, domains, ips, phones, hashes. no keys, no logins.

a passive OSINT toolkit in python usernames, emails, domains, ips, phones, hashes. no keys, no logins.

Bash-based passive reconnaissance + attack surface mapping script using only public APIs + stock Linux tools (curl, dig, openssl, nmap, python3).

Defensive analysis, patch breakdown, and passive detection scanner for CVE-2026-103752 (WordPress Authorizer Plugin <= 3.15.3).

Standard-library Python security triage engine that scans web apps, APIs, LLMs, and mobile packages via passive header inspection, active canary…

Go tool that passively discovers the real origin IP behind a WAF/CDN using multiple OSINT sources, then verifies candidates via HTML similarity, SSL…

Root-cause analysis, passive version checker, and lab PoC for CVE-2026-18322, an unauthenticated privilege escalation in the Smart Popup by Supsystic…

Mass exploit tool for CVE-2026-18351, an unauthenticated arbitrary file upload to RCE in Elementor Forms <= 1.6.0, with passive probing, shell…

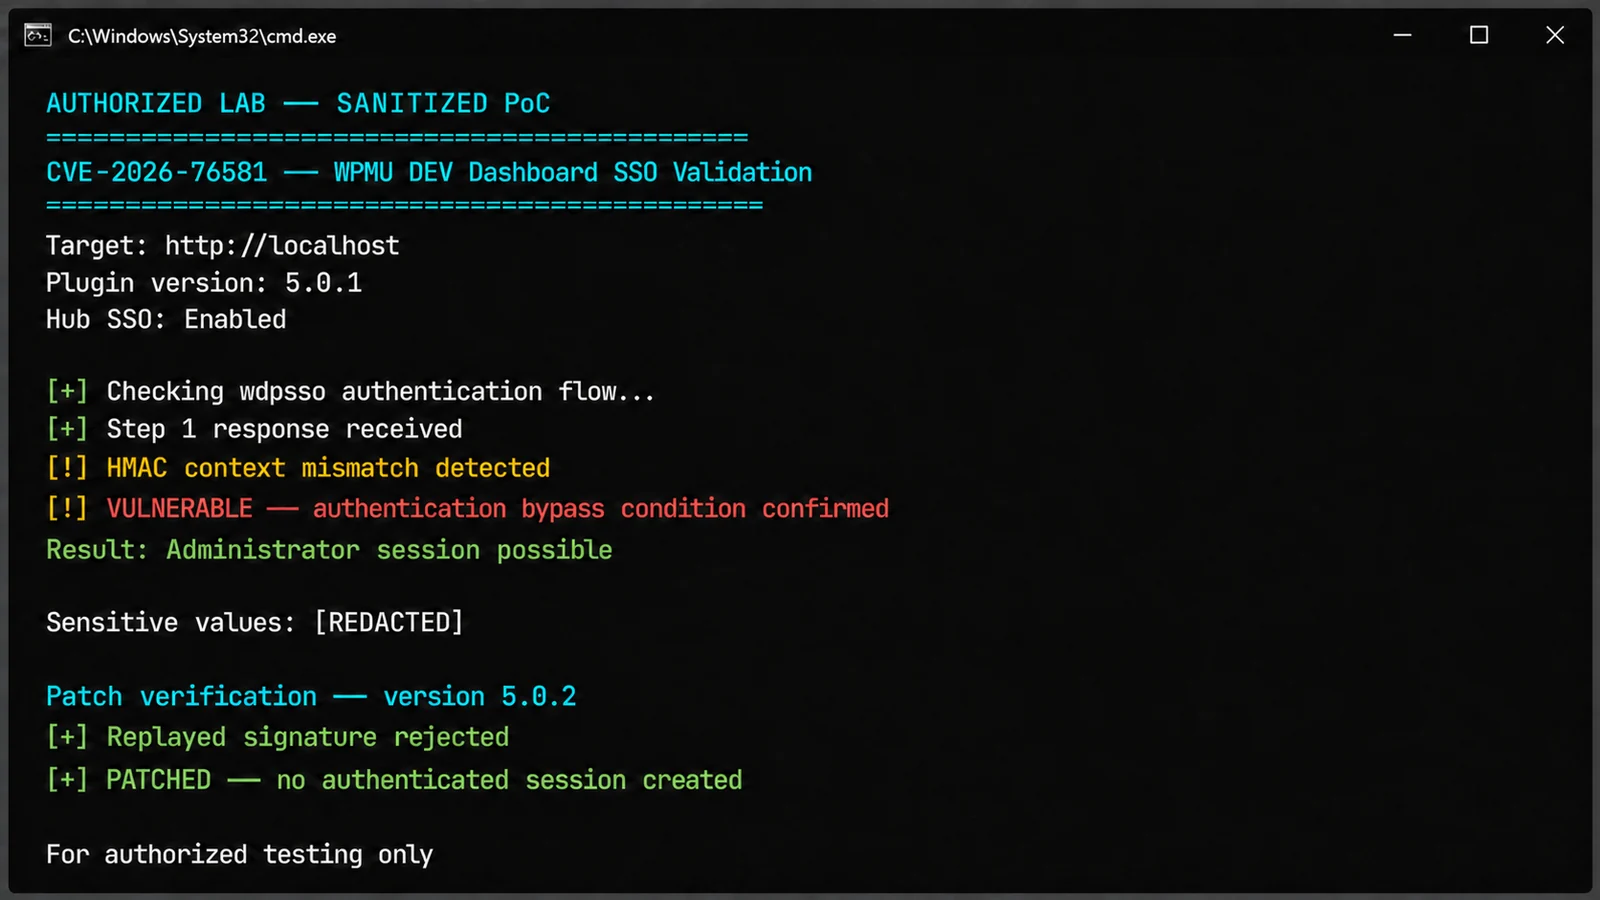
Safe passive detector for identifying WPMU DEV Dashboard versions affected by CVE-2026-76581.

AsyncIO Scanner & Exploitation Framework for CVE-2026-24061 (Telnet NEW_ENVIRON Auth Bypass). Features high-concurrency discovery, passive…

Passive reconnaissance and fingerprinting tool for detecting FreeScout deployments and analyzing exposure related to CVE-2026-28289, aiding…

Passive vulnerability scanner for CVE-2026-1731 — BeyondTrust RS/PRA pre-auth RCE (CVSS 9.9). Educational & defensive use only.

Cisco SD-WAN Exposure & Potential Vulnerability Scanner (Passive Fingerprinting) 2026

Rust-based DNS enumeration and subdomain discovery tool for reconnaissance and penetration testing security assessments.

Passive security checker for CVE-2026-48908 affecting SP Page Builder.

Flags parameters commonly associated with injection, SSRF, path traversal, IDOR, and SSTI, via passive Burp/ZAP scanning; also organizes manual…

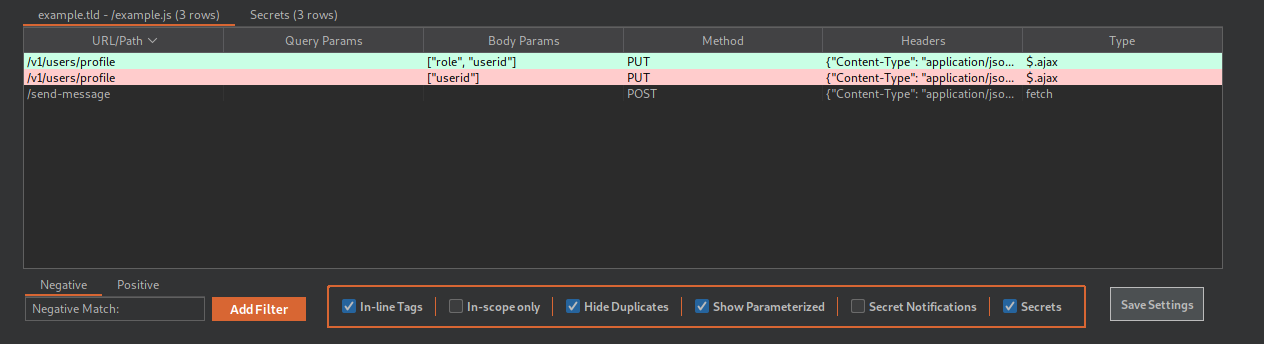
jsluice++ is a Burp Suite extension designed for passive and active scanning of JavaScript traffic using the CLI tool jsluice