
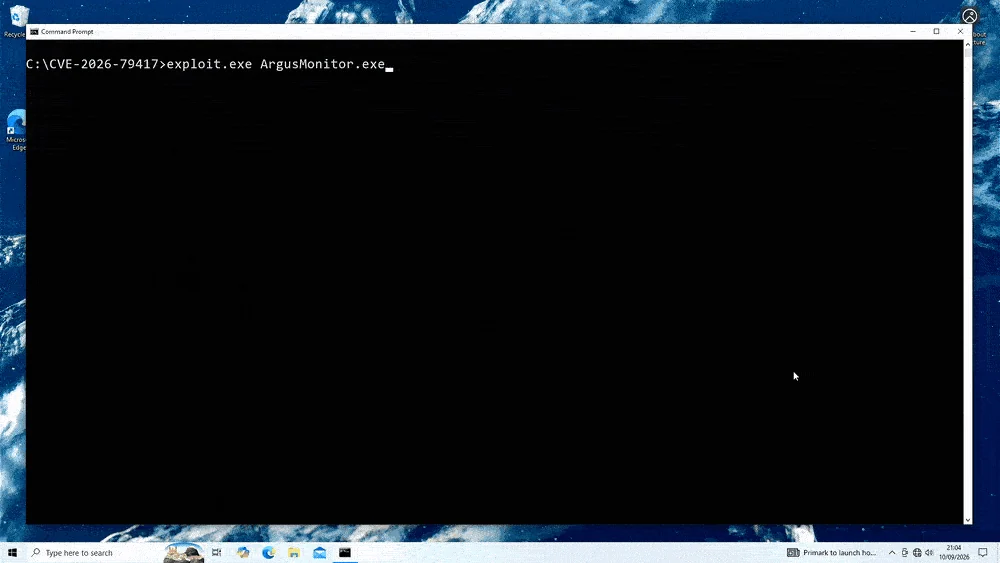
CVE-2026-79417
 connorjaydunn/cve-2026-79417
Proof-of-concept exploit for CVE-2026-79417, a local denial-of-service vulnerability in Argus Monitor <= 7.4.02, triggered via a signed binary path.
binary-exploitationexploitationvulnerability-analysis
connorjaydunn/cve-2026-79417Proof-of-concept exploit for CVE-2026-79417, a local denial-of-service vulnerability in Argus Monitor <= 7.4.02, triggered via a signed binary path.
 divinelabio/argus
The Ultimate Information Gathering Toolkit
 dozermx/argus
Multi-phase reconnaissance and attack-surface scanner that maps domains, IPs, ASNs, cloud assets, and CVEs into a knowledge graph with CVSS scoring…
 m1kb0k/cve-2022-25012-dvr4-weak-password-encryption
Decrypts weak encrypted passwords from Argus Surveillance DVR systems via CVE-2022-25012, reconstructing plaintext credentials from DVRParams.ini…
 jasurbek-masimov/cve-2018-15745
Automated directory traversal exploit for Argus Surveillance DVR 4.0.0.0 (CVE-2018-15745). Shell-based PoC for authorized security testing and…
 xk3nf4/cve-2022-25012
Argus Surveillance DVR v4.0 employs weak password encryption.
 arguslab/argus-saf
Scala-based static analysis framework for Android and Java bytecode with flow analysis, decompilation, and native code analysis via symbolic…
 purs3lab/argus
Staged static taint analysis framework for GitHub Actions workflows. Detects code injection vulnerabilities using taint-tracking and an impact…