

Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

··Feeds·Contact·Privacy·© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
177 results
reburp preview

reburp

GitHubforefy/reburp

A Burp Suite extension that exposes the full Montoya API as a local REST API, with Swagger UI
ai-securityapi-security-testingfuzzing+7
1033 days ago
HTTP3-Adapter preview

HTTP3-Adapter

GitHubt0xodile-swig/http3-adapter

Burp Suite extension that intercepts requests and sends them over HTTP/3, converting responses back for Burp, with support for kettled requests and…
api-security-testingnetwork-securitypenetration-testing+3
9 days ago
news-8.6.0-cve-2026-8726-backport preview

news-8.6.0-cve-2026-8726-backport

GitHubshentao83/news-8.6.0-cve-2026-8726-backport

Minimal security backport for CVE-2026-8726 in georgringer/news 8.6.0
database-securitydefensive-toolsstatic-code-analysis+3
6 days ago
CVE-2026-56096 preview

CVE-2026-56096

GitHubyairhinkis/cve-2026-56096

Proof of concept and technical write-up for CVE-2026-56096, a blind Solr query injection in TYPO3 EXT:solr enabling unauthenticated field enumeration…
exploitationinformation-gatheringpapers-research+3
8 days ago
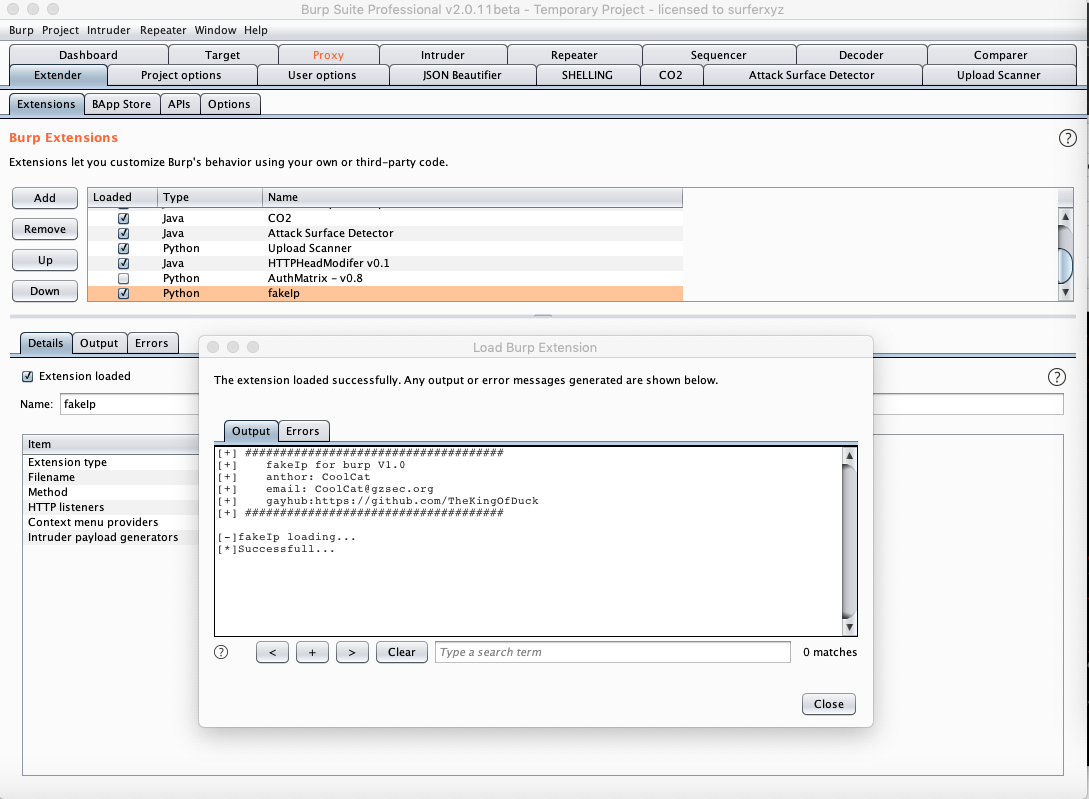
burpFakeIP preview

burpFakeIP

GitHubthekingofduck/burpfakeip

Burp Suite extension for spoofing IP addresses in HTTP requests, enabling testing of server-side IP restrictions and bypassing IP-based access…
ids-ips-evasionimpersonation-toolspenetration-testing+2
1.7k3 years ago
web3-decoder preview

web3-decoder

GitHubuwctcjnwlk/web3-decoder

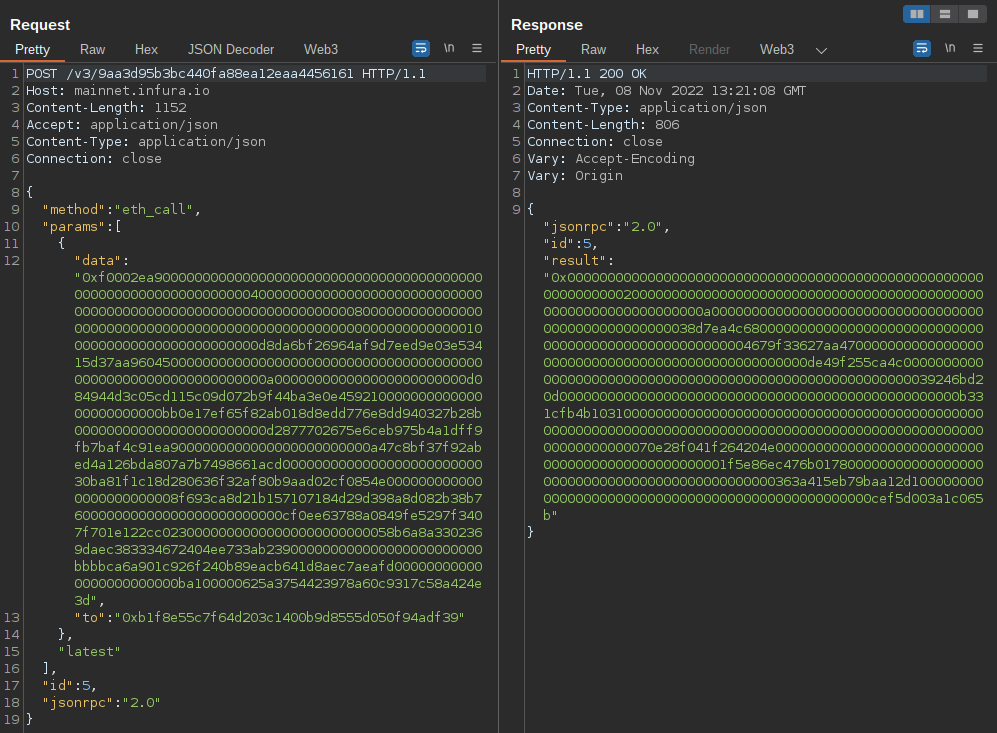
Burp Suite extension for decoding Ethereum JSON-RPC calls and smart contract interactions, supporting multiple chains and automatic ABI retrieval.
api-securitypenetration-testingreverse-engineering+2
21515 days ago
CVE-2026-25099 preview

CVE-2026-25099

GitHubyahiahamza/cve-2026-25099

Python exploit for Bludit CMS API unrestricted file upload leading to remote code execution, providing command execution and interactive shell for…
exploitationpayload-developmentpenetration-testing+3
6 months ago
cve-2023-5966 preview

cve-2023-5966

GitHubll104567/cve-2023-5966

Proof-of-concept exploit for CVE-2023-5966, an arbitrary file upload vulnerability in EspoCRM 2.7.4 and earlier, enabling remote code execution via a…
exploitationpayload-developmentpenetration-testing+2
2 years ago
Burp-Recordadora preview

Burp-Recordadora

GitHubhackwarts12/burp-recordadora

Persists BurpSuite proxy history, Repeater requests, and Intruder payloads across sessions; exports and imports .log files for web pentesting context.
penetration-testingutilities-frameworksweb-proxies-interception+1
10 months ago
CVE-2026-70376 preview

CVE-2026-70376

GitHubilhomjonr/cve-2026-70376

Advisory and Python PoC for Pluck CMS CSRF: fail-open Referer check plus double-extension upload enables webshell deployment and remote code…

educationexploitationpenetration-testing+3
1 month ago
CVE-2026-17544 preview

CVE-2026-17544

GitHubr2qa/cve-2026-17544

Exploit for CVE-2026-17544: PHP bcmath OOB write converted into memory-only RCE, bypassing disable_functions and open_basedir with a runtime…

binary-exploitationexploitationpayload-development+4
1 month ago
chyrp-lite-rce-poc preview

chyrp-lite-rce-poc

GitHubiltosec/chyrp-lite-rce-poc

CVE-2026-53767 + CVE-2026-53768 - Authenticated RCE in Chyrp Lite ≤ 2026.01 via uploads_path blocklist bypass and missing extension validation
educationexploitationpayload-development+4
3 months ago
CVE-2026-65891 preview

CVE-2026-65891

GitHubmurrez/cve-2026-65891

CVE-2026-65891 PoC — Joomla Content Editor file rename vulnerability (auth required, fixed in JCE 2.20.2)
exploitationinformation-gatheringpenetration-testing+4
1 month ago
amasty-chekout-POC-rce preview

amasty-chekout-POC-rce

GitHubchrissec2014/amasty-chekout-poc-rce

my poc for CVE-2026-53787

exploitationpenetration-testingweb-application-exploitation+1
18 days ago
pentest-mapper preview

pentest-mapper

GitHubportswigger/pentest-mapper

A Burp Suite Extension for Application Penetration Testing to map flows and vulnerabilities
api-securityapi-security-testingpenetration-testing+2
1222 years ago
oauth-scan preview

oauth-scan

GitHubportswigger/oauth-scan

Burp Suite Extension useful to verify OAUTHv2 and OpenID security

authentication-authorizationconfiguration-auditinginformation-gathering+3
1921 year ago
vscode-frida preview

vscode-frida

GitHubchichou/vscode-frida

Unofficial frida extension for VSCode

android-securitybinary-analysisdebuggers+5
5942 months ago
CVE-2026-66492 preview

CVE-2026-66492

GitHubtoanln-cov/cve-2026-66492

The Joomla extension PhocaCommander is vulnerable to Path Traversal in the file upload action - CVSS 6.1

exploitationpenetration-testingvulnerability-analysis+2
1 month ago
Previous12…10Next