
CVE-2025-64512
 dodgenefoli/cve-2025-64512
Automated proof-of-concept exploit for CVE-2025-64512 that accepts Target and Upload_dir parameters to test vulnerable file-upload functionality in…
exploitationpenetration-testingvulnerability-analysis+2
dodgenefoli/cve-2025-64512Automated proof-of-concept exploit for CVE-2025-64512 that accepts Target and Upload_dir parameters to test vulnerable file-upload functionality in…
 dotnetguard/cve-2025-55182-exploit
CVE-2025-55182 — Next.js Flight Deserialization RCE exploit with interactive shell, single-command execution and multi-payload reverse shell chain.…
 iixoskeletonii/dataprivacy-cve-2025-23211
 jasonbernier/cve-2025-5781
Proof-of-concept exploit for CVE-2025-57819 in FreePBX: SQL injection in the AJAX API to execute arbitrary PHP, create a persistent webshell, and…
 sfewer-r7/cve-2026-55040
Proof-of-concept exploit for Microsoft SharePoint CVE-2026-55040 that forges JWT tokens, bypasses authentication, auto-discovers metadata, and…
 keithbennedict/cve-2026-41940-linux
 hunt-benito/two-dots-and-a-slash-cve-2026-18907-tecno-hi-browser-download-path-traversal
Python PoC for CVE-2026-18907 path traversal in TECNO Hi Browser's download handler. Includes malicious HTTP server and naive downloader to…
 metthk/cve-2023-48084-revised
Python PoC exploiting time-based blind SQLi in Nagios XI to extract database contents, with multithreaded binary-search extraction and CLI…
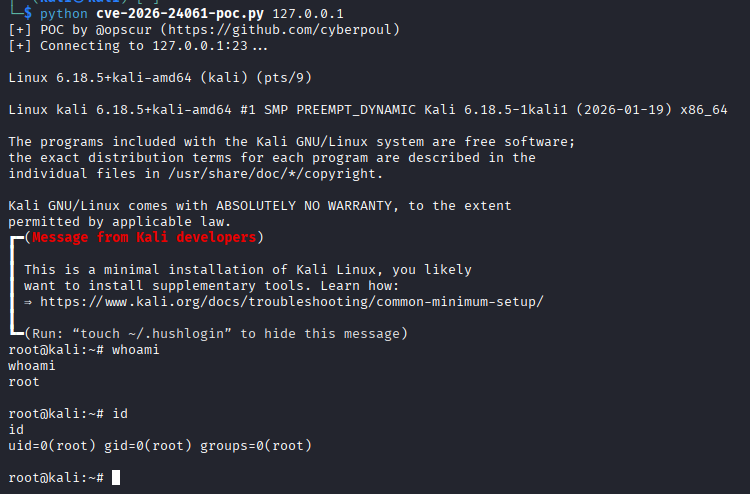 0p5cur/cve-2026-24061-poc
CVE-2026-24061's poc : a critical authentication bypass in telnetd leading to RCE as root Affects systems with telnetd versions containing the…
 cyb3rk0ala/cve-2022-35914-rce
PoC exploit for CVE-2022-35914 — GLPI v.10.0.2 htmLawed command injection, command execution, and reverse shell support.
 gimminse/firmware-analysis
Rediscovered CVE-2020-25279, a critical vulnerability in the Shannon baseband used in Samsung Exynos chipsets
 mluex0/cve-2026-23744-poc
CVE-2026-23744 is an unauthenticated command injection in MCPJam Inspector ≤1.4.2 via /api/mcp/connect. This POC exploits it by sending a crafted…
 g0d150ne/cve-2025-2945
Exploit for pgAdmin4 Remote Code Execution (RCE) vulnerability affecting versions 8.10 to 9.1.
 g0d150ne/wp2shell
Modular WordPress pre-auth exploit framework chaining SQL injection and authentication bypass to deliver remote code execution, interactive shells,…
 hxlxmj/cve-2025-26264
CVE-2025-26264 - GeoVision GV-ASWeb with the version 6.1.2.0 or less, contains a Remote Code Execution (RCE) vulnerability within its Notification…
 gouldnicholas/cve-2026-5817-poc
Docker Model Runner container-to-host RCE / Escape: A critical vulnerability that allows for container-to-host code execution in the Docker Model…
 murrez/cve-2026-65891
CVE-2026-65891 PoC — Joomla Content Editor file rename vulnerability (auth required, fixed in JCE 2.20.2)
 sonnelon/cve-2026-23744-poc
The poc of CVE-2026-23744