cve-2026-43499-app.so

Proof-of-concept shared library for exploiting a specific CVE, demonstrating impact and validating exposure on affected application deployments.

Proof-of-concept shared library for exploiting a specific CVE, demonstrating impact and validating exposure on affected application deployments.

Docker-based lab for reproducing CVE-2021-41773 (Apache HTTP Server 2.4.49) through controlled path traversal and file disclosure using a custom…

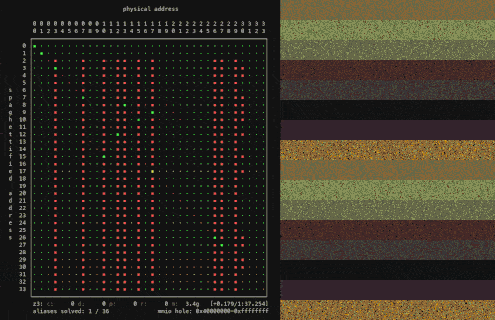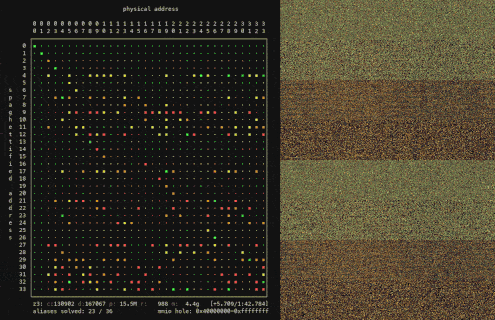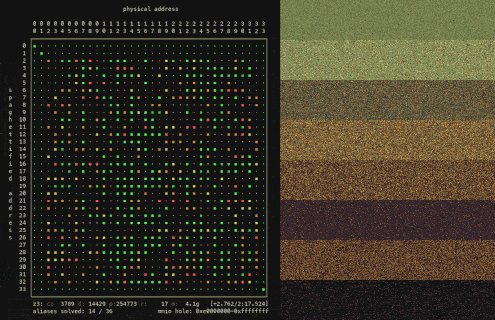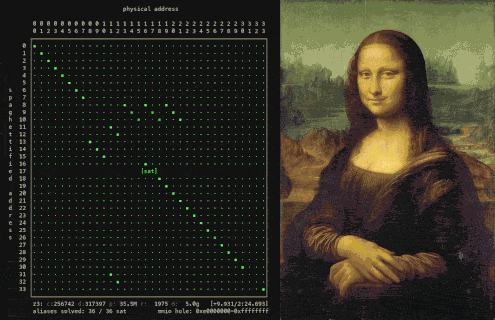
Unlocking _everything_ on the CPU with DRAM scrambling

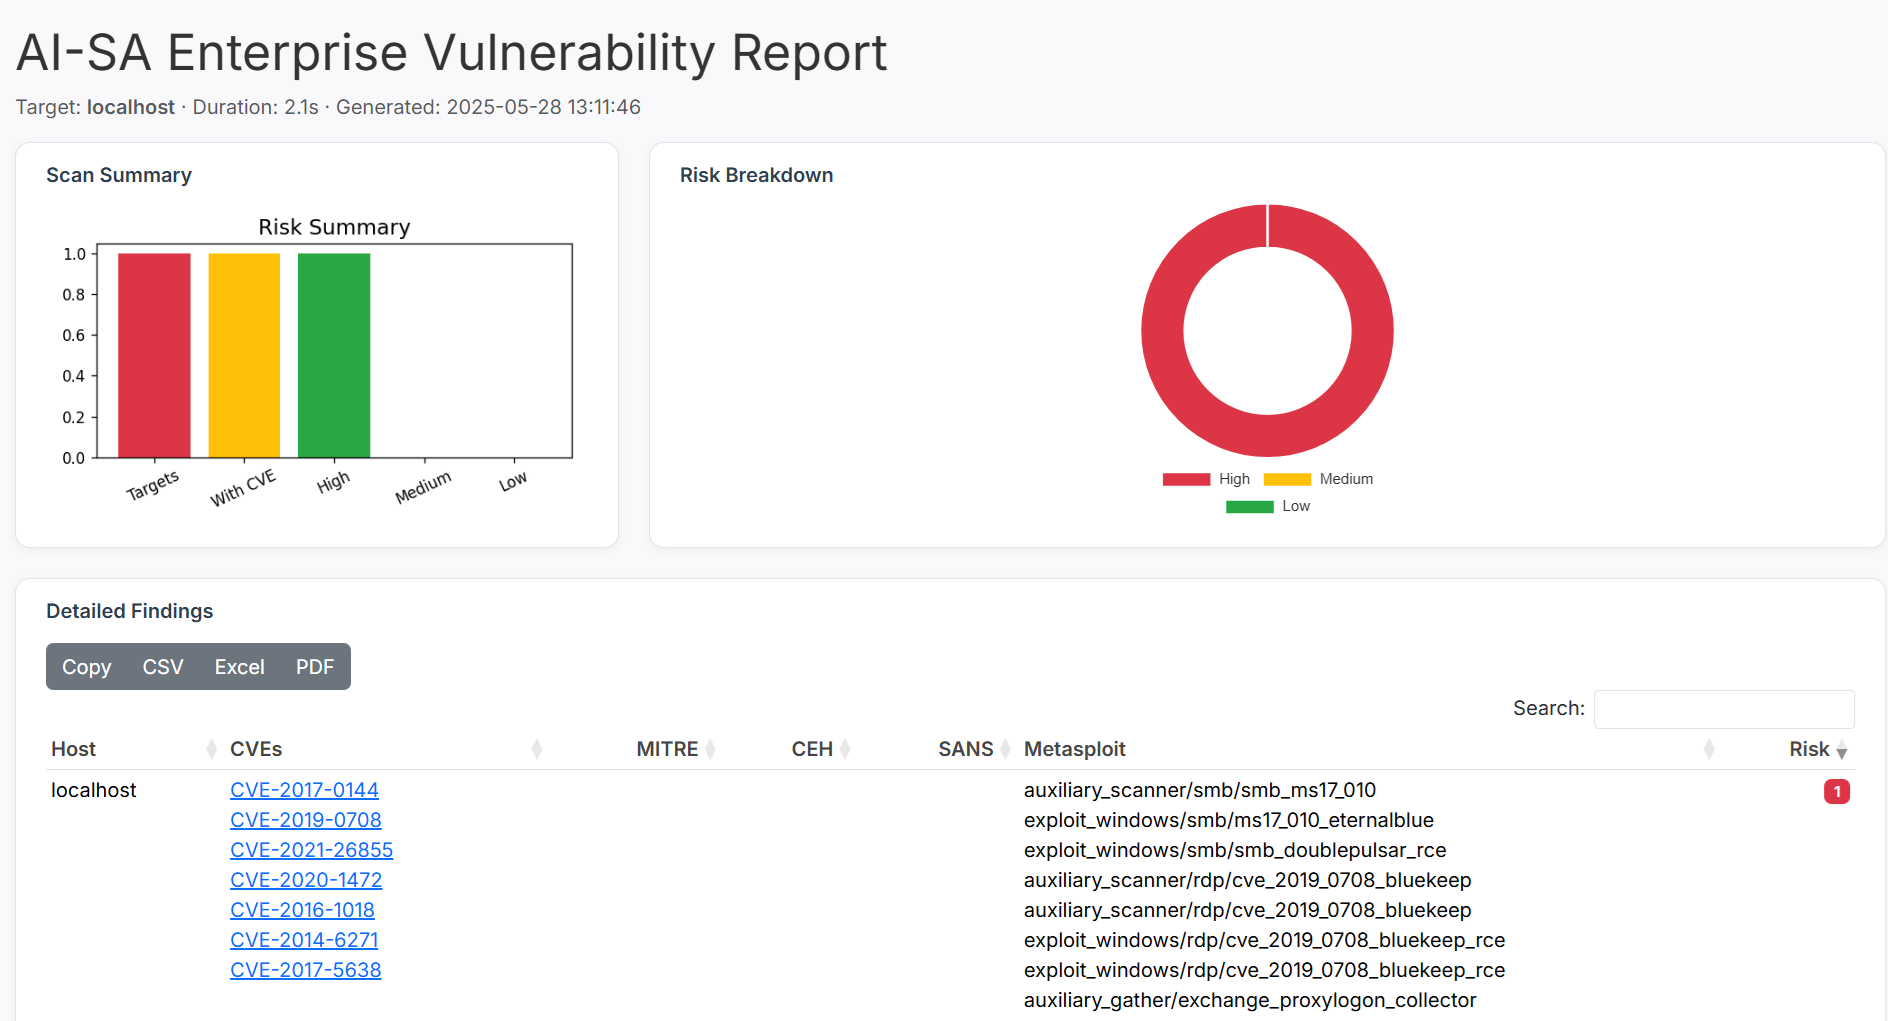
AISA-Scanner is an AI-powered autonomous vulnerability scanner that maps CVEs to metasploit exploits, MITRE, CEH, and SANS, delivering intelligent,…

Runtime vulnerability scanner: finds CVEs in the services actually running on a host and ranks them by network exposure.

Technical analysis of CVE-2025-55182 (React2Shell), covering vulnerability mechanics, root cause, controlled PoC testing, impact, and mitigation…

Defensive analysis of CVE-2009-4496 in Boa 0.94.14rc21, including source-code review, patch analysis, severity assessment, and ethical scope.

Passive security checker for CVE-2026-48908 affecting SP Page Builder.

CVE-2026-72898

CVE-2026-17544 — PHP bcmath bccomp() OOB write (stack smashing). Verified: crash on 8.4.23/8.5.8, fixed in 8.4.24. GHSA-x692-q9x7-8c3f

CVE-2026-33267 — Apache Traffic Server @ header internal-metadata spoof (CVSS 10.0). Verified: @ headers leak to plugins on 10.1.2, stripped on 10.1.4

CVE-2026-73034 — DB-GPT v0.8.1 unauth path traversal → arbitrary file write as root via user-id header. Verified + fix diff

Technical analysis and proof of concept for CVE-2026-59827, a critical unsafe Java deserialization vulnerability in Metabase leading to remote code…

CVE-2017-9805-Exploit

MCP environment-variable blocklist bypass leads to unauthenticated RCE in Flowise 3.1.1

Missing Authorization in inseriswiss inseri core inseri-core allows Exploiting Incorrectly Configured Access Control Security Levels.This issue…

Proof-of-concept exploit for pre-auth XXE file read vulnerabilities in SimpleSAMLphp, enabling extraction of arbitrary local files from affected…

Educational lab and proof-of-concept materials for a specific CVE, providing sandboxed scripts and templates for vulnerability research, authorized…