PrintSpoofer-ReflectiveDLL

The Windows Print Spooler privilege escalation vulnerability (CVE-2019-1040/CVE-2019-1019) has been implemented as a Reflective DLL for penetration…

The Windows Print Spooler privilege escalation vulnerability (CVE-2019-1040/CVE-2019-1019) has been implemented as a Reflective DLL for penetration…

Local Privilege Escalation in HP Support Assistant

exp for CVE-2019-0887

DoSinator is a powerful Denial of Service (DoS) testing tool developed in Python.

A simple yet effective python3 script to perform DNS spoofing via ARP poisoning

ARP spoofing, HTTP redirection, DNS spoofing and DNS forging using pcap library

API, CLI, and Web App for analyzing and finding a person's profile in 1000 social media \ websites

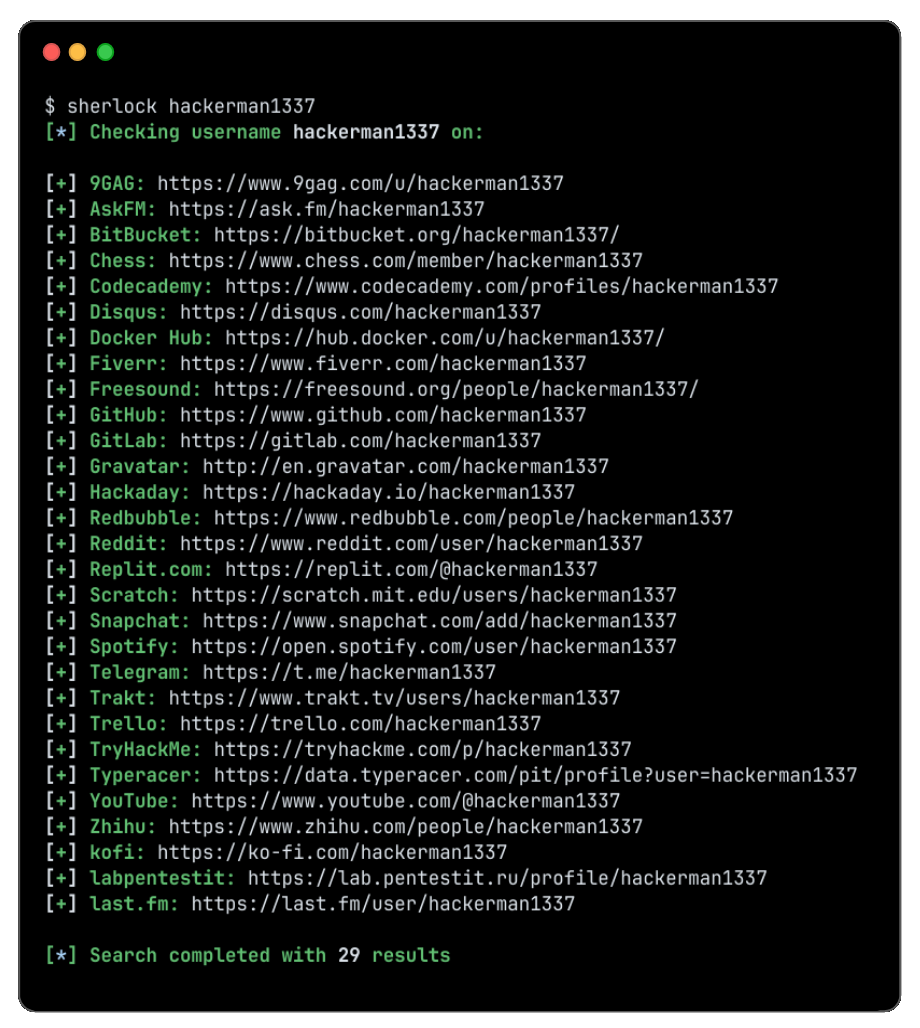
Hunt down social media accounts by username across social networks

Exploit for Checkmk CVE-2024-0670 with automated file transfer, reverse shell, and privilege escalation via RunasCs for penetration testing…

Arbitrary file read exploit for the Windows UPnP Device Host service.

Packs C# assemblies, PE files, or shellcode into encrypted Nim binaries with advanced evasion features including AMSI/ETW bypass, sandbox detection,…

DCOM in memory and fileless lateral movement techniques through .Net deserilization

KHAOS is a modern C2 framework that routes agent traffic through cloud services already trusted by enterprise networks.

A "Exposed Dangerous Method or Function" vulnerability in PrintixService.exe, in Kofax Printix's "Printix Secure Cloud Print Management", Version…

Python exploit for CVE-2020-1472 (Zerologon) targeting Netlogon authentication to compromise Active Directory domain controllers and escalate…

CVE-2025-33073

Proof-of-concept exploit for CVE-2015-1769 using a crafted VHD file and symbolic link to trigger a Windows privilege escalation via Mount Manager.

Proof of concept exploit for Ivanti EPM CVE-2024-13159 and others