

P4wnP1_aloa
 rogandawes/p4wnp1_aloa
P4wnP1 A.L.O.A. by MaMe82 is a framework which turns a Rapsberry Pi Zero W into a flexible, low-cost platform for pentesting, red teaming and…
bluetooth-securityexploit-frameworkshardware-hacking+5
4.4k
rogandawes/p4wnp1_aloaP4wnP1 A.L.O.A. by MaMe82 is a framework which turns a Rapsberry Pi Zero W into a flexible, low-cost platform for pentesting, red teaming and…
 mandiant/flare-emu
Scriptable binary emulation framework integrating IDA Pro/Radare2 with Unicorn engine for automated malware analysis, string decryption, and code…
 telefonica/uac-a-mola
Modular framework for Windows UAC bypass attacks and mitigation, featuring DLL hijacking, fileless execution, and real-time monitoring to detect and…
 ivre/ivre
Network recon framework. Build your own, self-hosted and fully-controlled alternatives to Shodan / ZoomEye / Censys and GreyNoise, run your Passive…
 rburrito/payloadgenerator
A wrapper for MSFvenom that allows for easy generation of payloads
 exbotanical/brutus
extensible exploitation framework shipped on a modular multi-tasking architecture
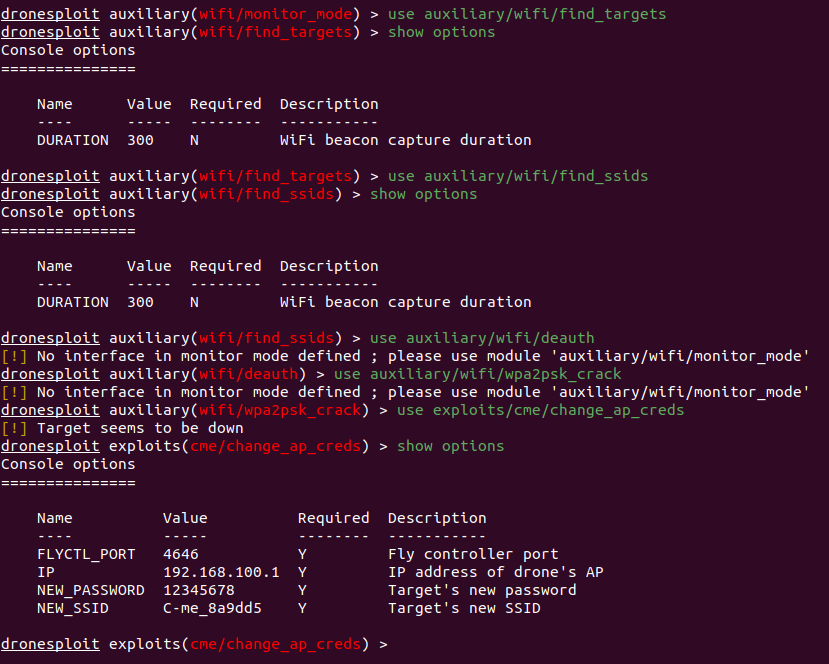 dronesploit/dronesploit
Metasploit-style console framework for pentesting commercial drones, featuring modular exploits for wireless attacks, SSID/password manipulation, and…
 pandasec888/taowu-cobalt_strike
Red team automation framework built on Cobalt Strike, integrating exploit modules, post-exploitation tools, and lateral movement capabilities for…
 brows3r/ipwn
A Framework meant for the exploitation of iOS devices.
 lepotekil/msfmania
Python AV Evasion Tools
 cyb3r-techie/msf_passspray_wordlist_generator
A handy tool that helps to create your own wordlist for Metasploit framework, in order to carry out a password spray attack against various network…
 mythicagents/thanatos
Mythic C2 agent targeting Linux and Windows hosts written in Rust
 samogod/tornado
Anonymously Reverse Shell over Tor Network using Hidden services without Portforwarding.
 andreiverse/grc2
Lightweight C2 framework written in Nim for generating implants, managing listeners, and executing tasks via TCP/HTTP with a loot system for…
 mindpatch/scant3r
Module-based web vulnerability scanner and bug bounty automation framework with built-in XSS, SSTI, SSRF, and Firebase detection engines. Designed to…
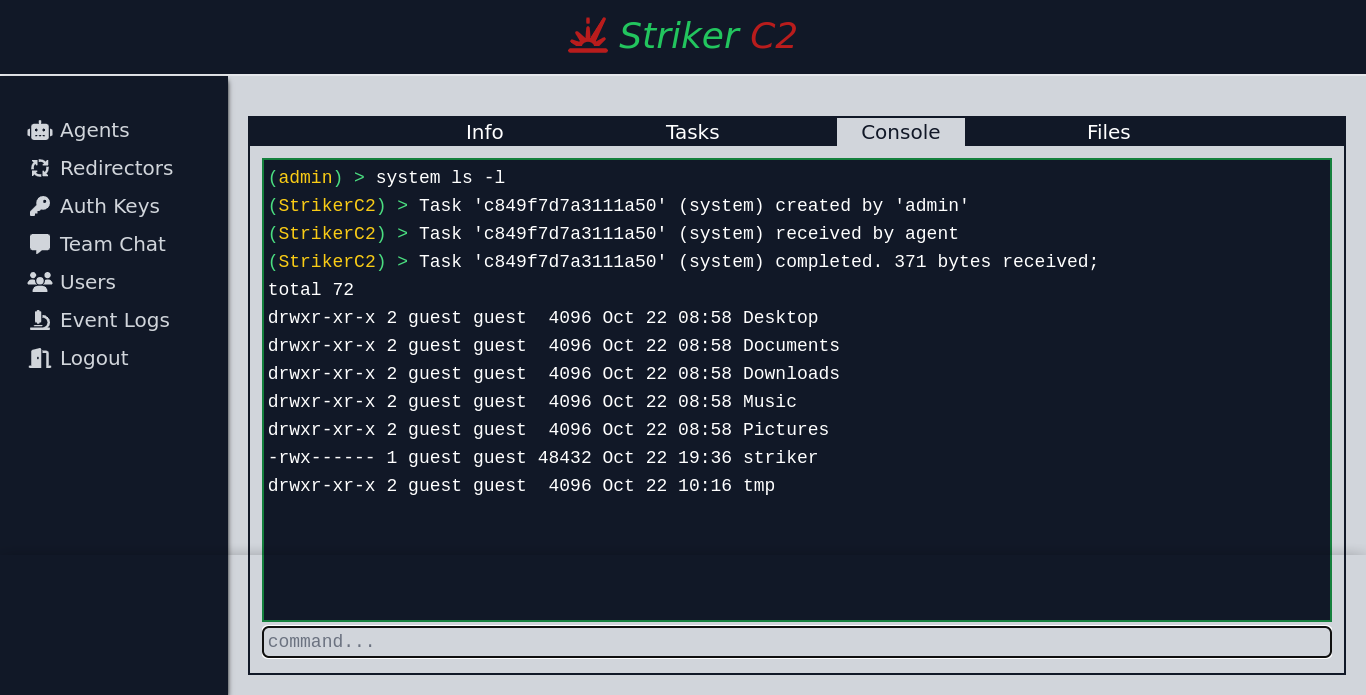 4g3nt47/striker
Multi-operator C2 framework with native C and Python agents, HTTP(S) channels, asynchronous tasking, and a reactive web UI for red team operations.
 kpcyrd/sh4d0wup
Signing-key abuse and update exploitation framework
 mandiant/speakeasy
Windows malware emulation framework that executes binaries, drivers, and shellcode in a modeled runtime, emulating APIs, process/thread behavior,…