
CICD-Goat-Vapt-Writeup
 dheeraj-jayaswal/cicd-goat-vapt-writeup
Full VAPT writeup of OWASP CICD-Goat — 9 CTFd flags captured, 4 critical + 5 high findings (incl. CVE-2024-23897) mapped to the OWASP Top 10 CI/CD…
ctfdevsecopseducation+5
1
dheeraj-jayaswal/cicd-goat-vapt-writeupFull VAPT writeup of OWASP CICD-Goat — 9 CTFd flags captured, 4 critical + 5 high findings (incl. CVE-2024-23897) mapped to the OWASP Top 10 CI/CD…
 nccgroup/amfdser-ngng
A Burp Extender plugin, that will take deserialized AMF objects and encode them in XML using the Xtream library
 nccgroup/argumentinjectionhammer
A Burp Extension designed to identify argument injection vulnerabilities.
 nccgroup/autorepeater
Automated HTTP Request Repeating With Burp Suite
 nccgroup/wcfdser-ngng
A Burp Extender plugin, that will make binary soap objects readable and modifiable.
 d0rb/packetpirate
A headless , scriptable, command-line based MITM proxy designed for network traffic interception, analysis, and modification on Windows systems.
 d0n601/pwncity
Insecure TeamCity CI environment for hands-on penetration testing training: reconnaissance, credential theft, privilege escalation, and lateral…
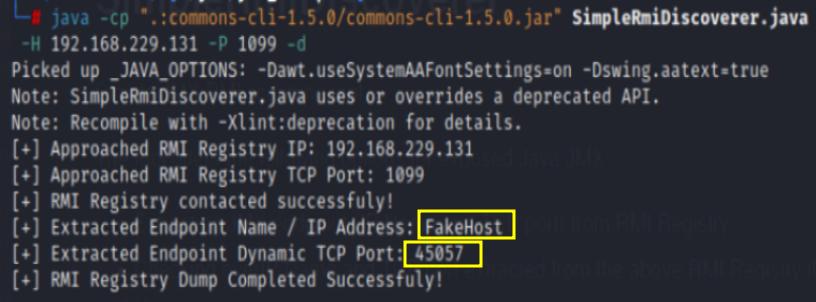 marcin-wolak/simplermidiscoverer
Simple JMX RMI scanning tool
 razureink/arisu
Scans public code repositories and code snippet platforms to extract and validate AI service API keys with real-time dashboard and multi-format…
 bishopfox/snowpick
find sensitive data leaking from ServiceNow instances.
 owasp/owasp-subtractive-hardening-top-10
The OWASP Subtractive Security Top 10 Project is an initiative to identify, document, and promote the highest-impact opportunities for reducing cyber…
 owasp/owasp-model-card-security-standard
Open standard for documenting security-relevant metadata of AI models, including training data provenance, PII risk, known vulnerabilities, and…
 jas502n/burpsuite_pro_v1.7.37
Comprehensive web application security testing platform featuring advanced scanning engine, intercepting proxy, and automated vulnerability detection…
 owasp/community-security-prompts
A curated library of security prompts for AI-assisted security testing, threat modeling, and educational exercises.
 azurit/crsprober
Remote detection tool for OWASP Core Rule Set version and paranoia level on ModSecurity WAFs, aiding security posture assessment.
 j-dahl7/mcp-attack-detection-sentinel
Sentinel detection lab for MCP attack chains: CVE-2026-26118 SSRF token theft, tool poisoning, cross-server exfiltration, identity post-exploitation.…
 debajyoti0-0/cve-2026-60206
Technical analysis and Proof-of-Concept for CVE-2026-60206, a critical Oracle WebLogic Server SAML authentication bypass vulnerability.
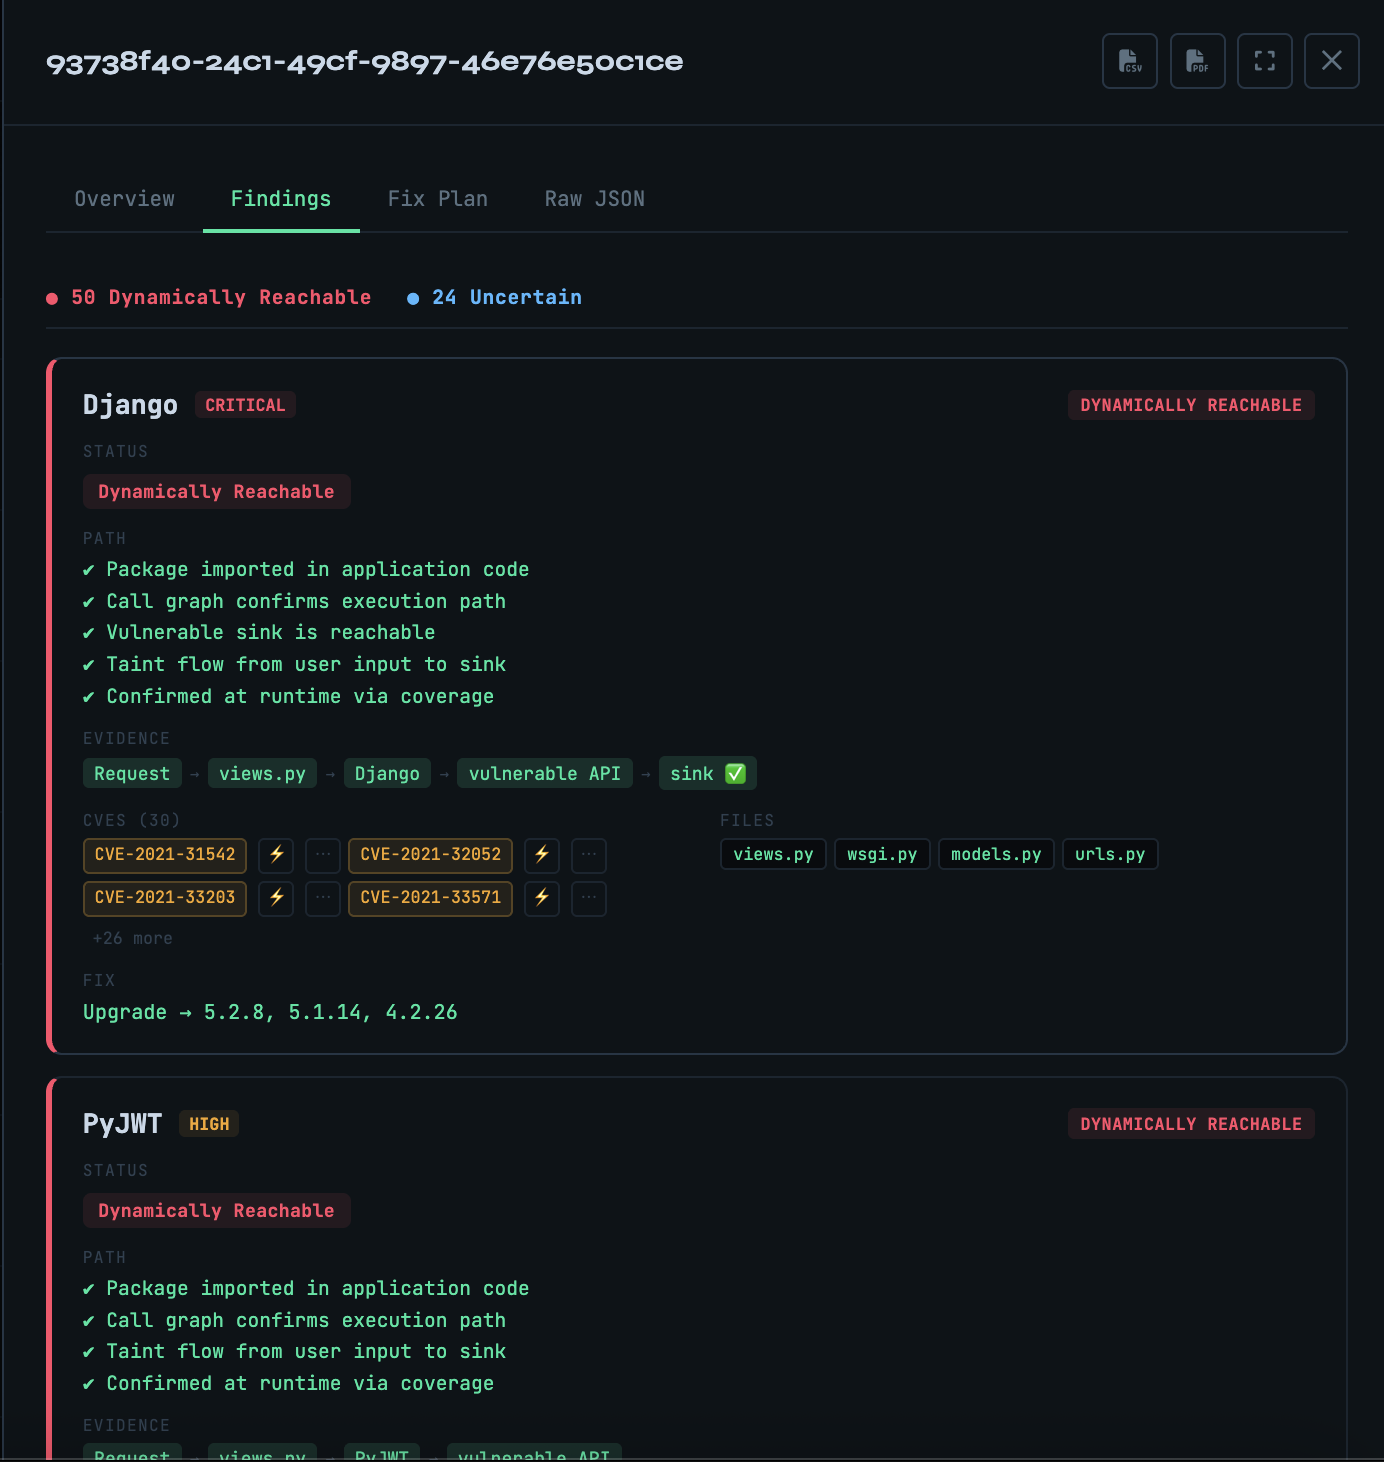 owasp/vulnreach
Runtime-aware SCA — proves which CVEs are actually reachable, not just installed.