
CVE-2022-0543
 fulxey/cve-2022-0543
Redis RCE through Lua Sandbox Escape vulnerability
exploitationpayload-developmentpenetration-testing+5
14 years ago
fulxey/cve-2022-0543Redis RCE through Lua Sandbox Escape vulnerability
 yym8538/cve-2026-0603
Proof-of-concept and Docker lab reproducing CVE-2026-0603, a second-order SQL injection in Hibernate ORM bulk DELETE/UPDATE operations, with…
 kiwknr/cve-2026-104826
Proof-of-concept exploit chain for CVE-2026-104826, a path traversal in DropzoneFileExplorer's chunked upload handler that writes a PHP webshell for…
 techupdate24/fortimail-zero-day-cve-2026-104286
A complete guide and workflow for integrating Agile sprints with DevOps CI/CD pipelines.
 anoxhunterdump-ctrl/cve-2026-103752-authorizer-privilege-escalation
Defensive analysis, patch breakdown, and passive detection scanner for CVE-2026-103752 (WordPress Authorizer Plugin <= 3.15.3).
 bombobombone/cve-2026-103585
Sanitized report and loopback-only PoC script demonstrating stored XSS via javascript: license URLs in MediaSearch QuickView (CVE-2026-103585).
 bombobombone/cve-2026-103584
Sanitized report and loopback-only PoC script for CVE-2026-103584, a javascript: URL scheme XSS in MediaWiki CommonsMetadata LicenseUrl rendering.
 bombobombone/cve-2026-103442
Local proof-of-concept and sanitized report for CVE-2026-103442, a PHP object injection in MediaWiki CentralAuth's merge-session handling that can…
 bombobombone/cve-2026-103441
Local proof-of-concept and sanitized report for CVE-2026-103441, a PHP object-injection flaw in the MediaWiki action=parse API that can reach RCE via…
 bombobombone/cve-2026-103437
Local proof-of-concept and sanitized report for CVE-2026-103437, a canonical URL XSS in MediaWiki ReadingLists triggered via crafted import links.
 d4kw1n/cve-2026-102607-zoneminder
Python PoC exploiting CVE-2026-102607, an authenticated OS command injection in ZoneMinder <= 1.38.1 exportEvents() enabling RCE, command output…
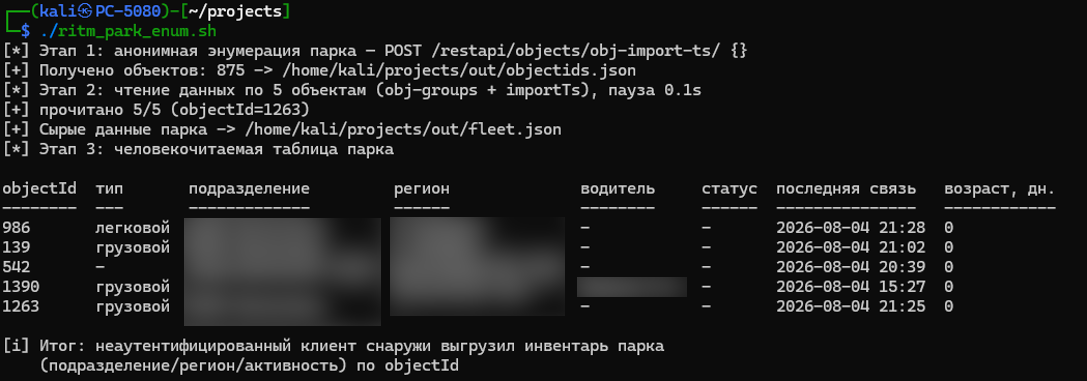 4ybrick/cve-2026-100903
PoC and enumeration script for CVE-2026-100903, a missing-authentication flaw in the GEO.RITM REST API that leaks object and driver data anonymously.
 wvllxe/cve-2026-100520-laranode-path-traversal
Path Traversal -> RCE in Laranode < 1.2.1 (CWE-22). PoC + advisory writeup.
 bombobombone/cve-2026-100381
Report and PoC for CVE-2026-100381, a DOM XSS in MediaWiki UploadWizard Flickr collection and set titles, with patch verification notes and a local…
 bombobombone/cve-2026-100380
PoC and patch verification notes for CVE-2026-100380, a reflected XSS in Wikibase language-validation error pages, with a script that detects…
 parapapinho/cve-2017-12561
Reverse-engineering write-up and proof of concept for CVE-2017-12561, a use-after-free in HPE iMC dbman, covering binary diffing, ASN.1 decoding, and…
 anoxhunterdump-ctrl/cve-2026-14378-devkit-pro-auth-bypass
Defensive analysis, patch breakdown, and detection scanner for CVE-2026-14378 (WordPress DevKit Pro Plugin <= 2.3.0).
 yym8538/cve-2026-16723
Proof-of-concept exploit for CVE-2026-16723, a Fastjson 1.x @JSONType remote code execution flaw, with a payload JAR builder and reverse-shell…