
naive-hashcat
Plug-and-play hashcat wrapper that cracks password hashes using preconfigured dictionary, rule-based, combinator, and mask attacks, supporting dozens…

Plug-and-play hashcat wrapper that cracks password hashes using preconfigured dictionary, rule-based, combinator, and mask attacks, supporting dozens…

Collection of cryptographic hash functions written in pure Rust

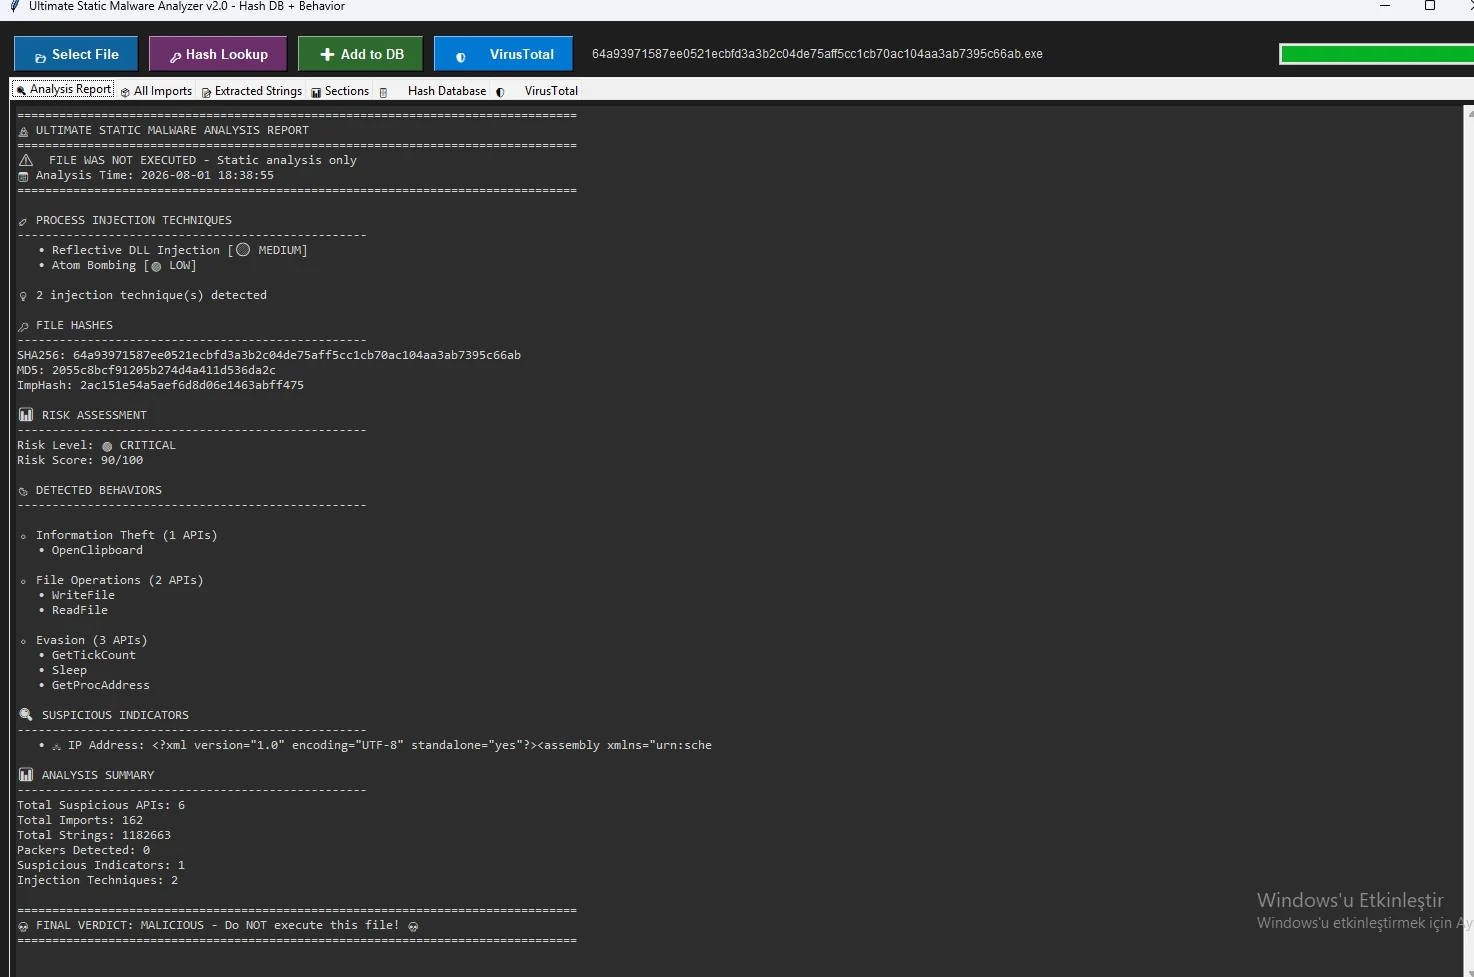
Advanced Static malware analyzer that reveals 8 injection techniques, critical API calls, hidden strings, exports PE sections (.text, .rdata) as…

Trust & Safety tools for working together to fight digital harms.

OSCP-focused toolkit for read-only network, SMB, AD, DNS, web, and database enumeration; privesc scanning, hash identification, and…

Open YARA scan- and search engine

Assortment of hashing algorithms used in malware

This repository contains scripts, configurations and deprecated payload loaders for Brute Ratel C4 (https://bruteratel.com/)

Imphash-like calculation on Golang binaries

A collection of Tools and Rules for decoding Brute Ratel C4 badgers

Python library for parsing CLR/PE metadata in .NET assemblies, exposing streams and hash fingerprints to support malware analysis and threat hunting.

Deployable AWS-hosted Active Directory pentest lab with domain controller and vulnerable MSSQL; practice S4U2Self abuse, SQL brute force, and RCE.

C# version of NTLMRawUnHide

Mutates signed Windows binaries to retain valid catalog signatures while changing file hashes, bypassing hash-based endpoint blocks and exposing…

Long Range Pager Systems pagers and coasters URH and YS1 (yardstick one / cc11xx) information and brute force tool

A Pythonic interface and command line tool for interacting with the InQuest Labs API.

Modern tactical exploitation toolkit.

badger-builder is an AI-assisted tool for generating dynamic Brute Ratel C4 profiles