
Detours
 microsoft/detours
Runtime Windows API interception library for hooking, monitoring, and instrumenting function calls. Supports binary rewriting and DLL injection,…
debuggersdynamic-code-analysisreverse-engineering+1
6.4k
microsoft/detoursRuntime Windows API interception library for hooking, monitoring, and instrumenting function calls. Supports binary rewriting and DLL injection,…
 cypherhippie/cve-2026-66804
Local Windows privilege escalation PoC for CVE-2026-66804: plants a COM DLL in a missing path to abuse Camera FrameServer and impersonate SYSTEM.
 duyduongduyduong/cve-2021-36934-dll-hijacking-dfir-investigation
DFIR investigation resources for CVE-2021-36934, covering DLL hijacking, privilege-escalation detection, and forensic analysis of affected Windows…
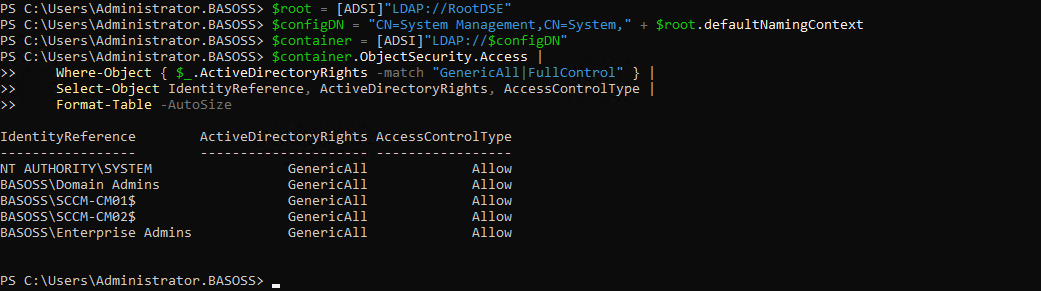 omribaso/sccm-cve-2026-47301-remote-code-execution-exploit
Proof-of-concept exploit chain (CVE-2026-47301) for Microsoft Configuration Manager (SCCM), combining a broken access, CAB arbitrary-write path…
 gmh5225/0xguard
Simple Anti-cheat library for applications that use C++ on windows. #PastedProtection
 davidcarliez/cve-2026-66804-crossdevice-lpe
Local privilege escalation PoC for Windows CVE-2026-66804 using CrossDevice DLL planting and SigmaPotato token impersonation to spawn a SYSTEM…
 phackt/wptsextensions.dll
WptsExtensions.dll for exploiting DLL hijacking of the task scheduler.
 sailay1996/cdpsvclpe
Windows Local Privilege Escalation via CdpSvc service (Writeable SYSTEM path Dll Hijacking)
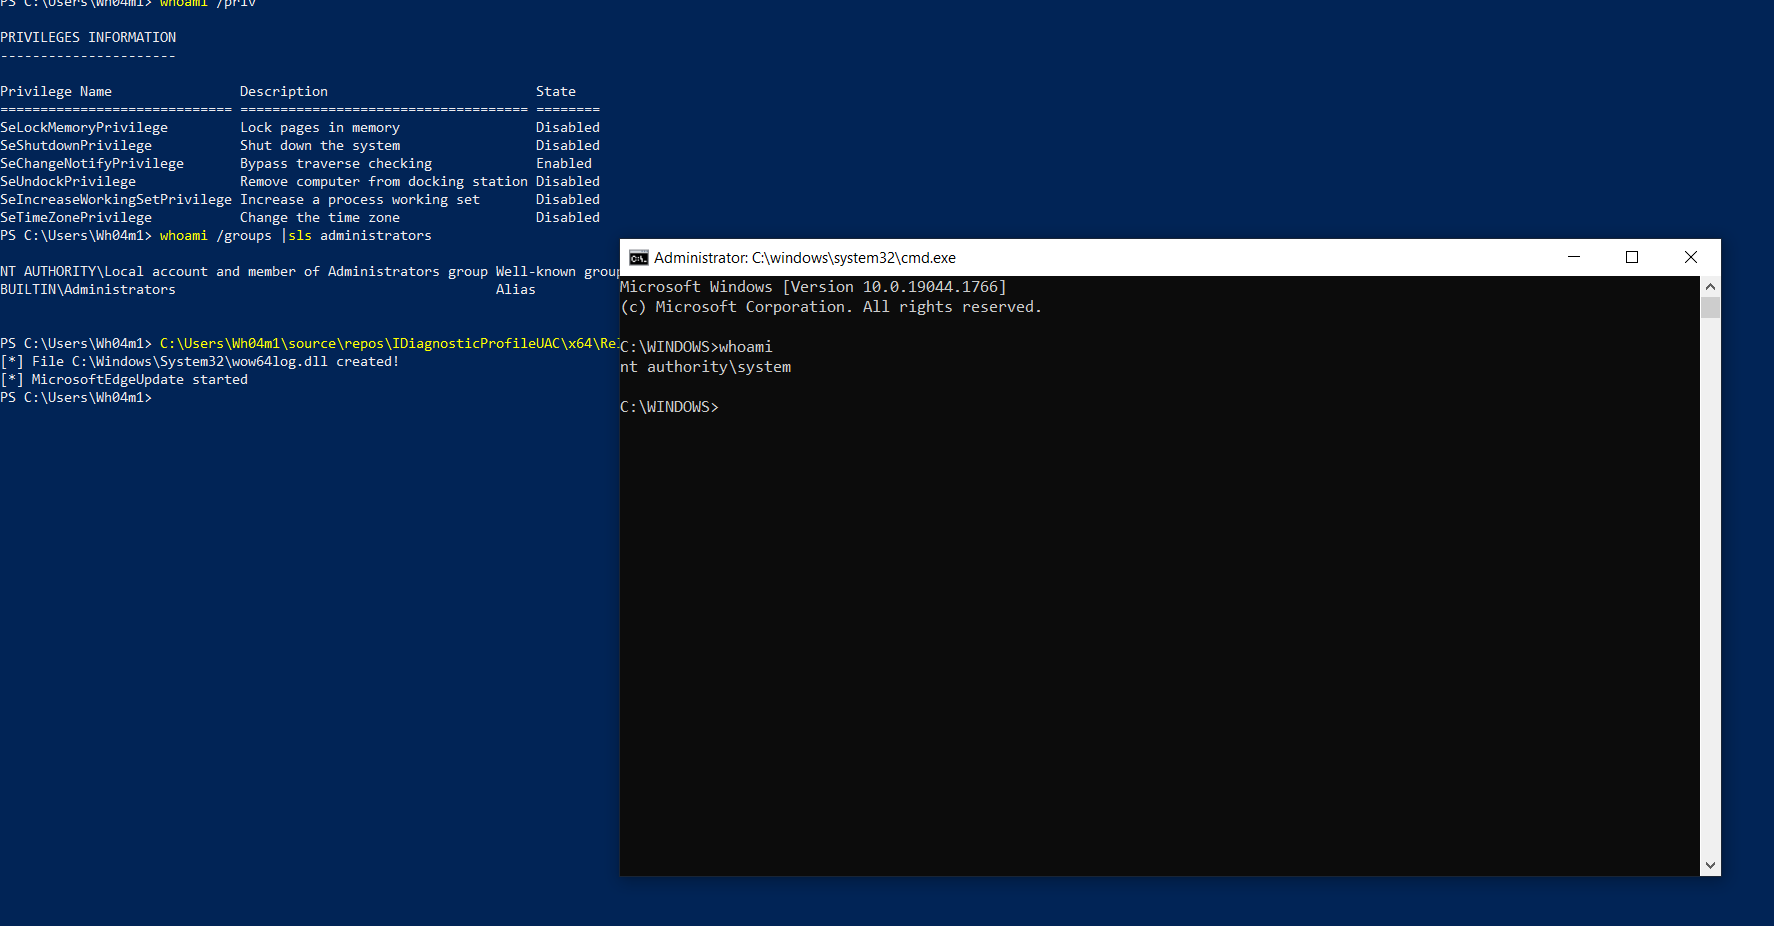 wh04m1001/idiagnosticprofileuac
Proof-of-concept UAC bypass abusing auto-elevated COM objects to copy a user-specified DLL into System32 and trigger a SYSTEM service load for…
 hackerhouse-opensource/iscsicpl_bypassuac
UAC bypass for x64 Windows 7 - 11
 choisg/onedriveupdatersideloading
Payload for DLL sideloading of the OneDriveUpdater.exe, based on the PaloAltoNetwork Unit42's blog post
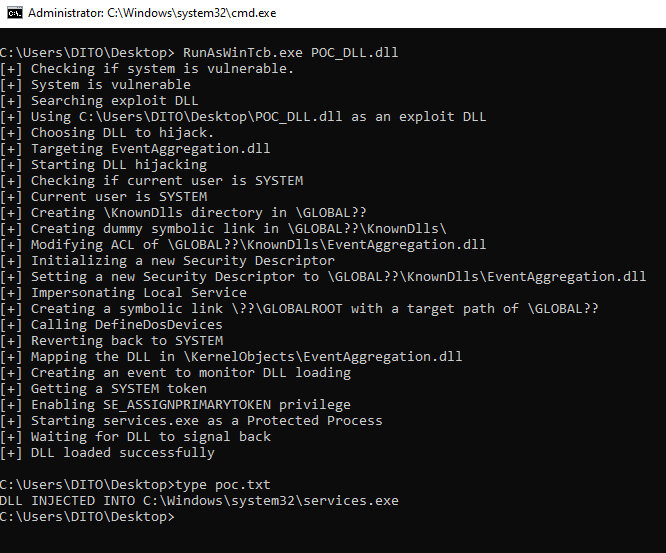 tastypepperoni/runaswintcb
Proof-of-concept C exploit that runs a DLL with WinTcb-Light protection from userland, demonstrating a Windows privilege-escalation primitive and…
 iilegacyyii/exportdumper
A small tool I made to dump the export table of PE files. The primary use case was intended for use within DLL proxying.
 playboisk8/poc-cve-2017-8464-opencalculator
Exploiting the .lnk vulnerability and operating system handling mechanisms regarding explorer.exe and USB drives.
 cybereason/siofra
Simulates the Windows PE loader to identify DLL hijacking vulnerabilities, generates weaponized DLLs with shellcode payloads, and detects UAC…
 hackerhouse-opensource/nofaxgiven
Code Execution & Persistence in NETWORK SERVICE FAX Service
 d3lb3/keefarcereborn
A standalone DLL that exports databases in cleartext once injected in the KeePass process.
 rad9800/wtsrm2
Header-only C++17 library for evasive Windows development: compile-time API hashing, DLL unhooking, hardware breakpoint clearing, VEH removal, and…