
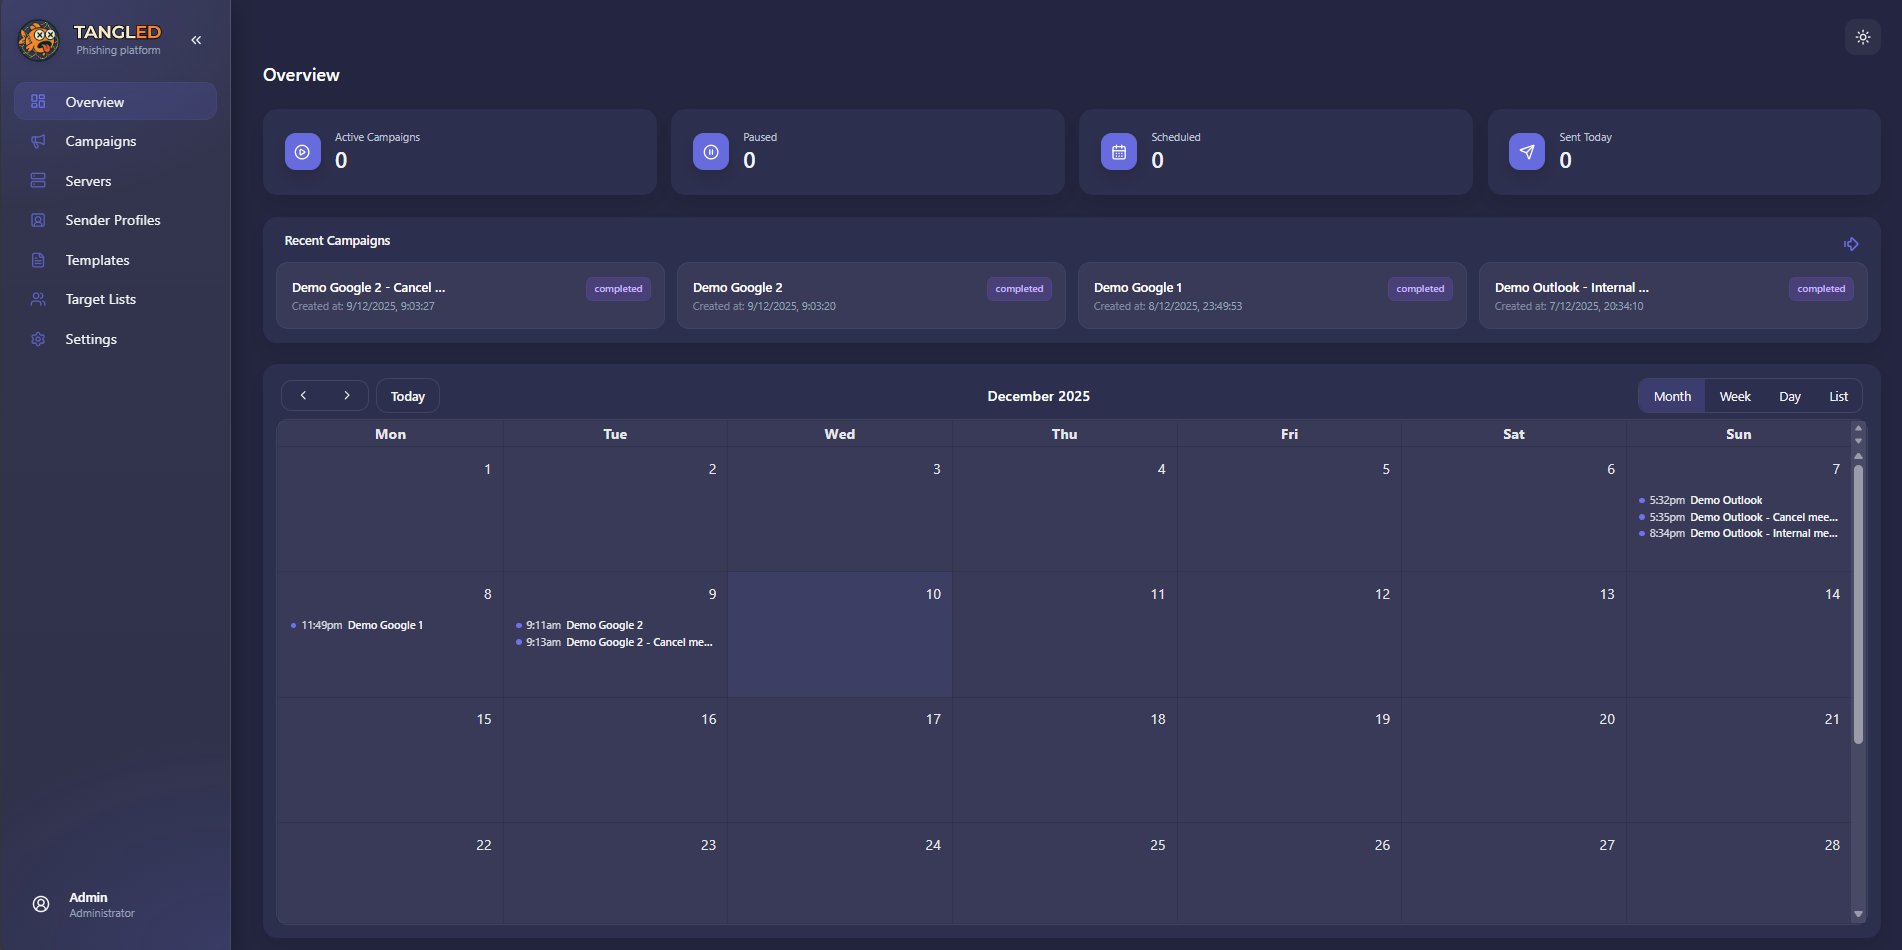
Tangled
 ineesdv/tangled
Open-source offensive security platform for conducting phishing campaigns that weaponizes iCalendar automatic event processing.
command-and-controlemail-securitylateral-movement+5
275
ineesdv/tangledOpen-source offensive security platform for conducting phishing campaigns that weaponizes iCalendar automatic event processing.
 klsecservices/cpldcomtrigger
Python script leveraging Impacket to trigger CPL file loading into memory via DCOM IOpenControlPanel interface for lateral movement and code…
 ricardojoserf/adduser-samr
Create local administrators in Windows using the SAMR API. In C#, Crystal, Python, Rust, Golang, Nim and Deno (Javascript)
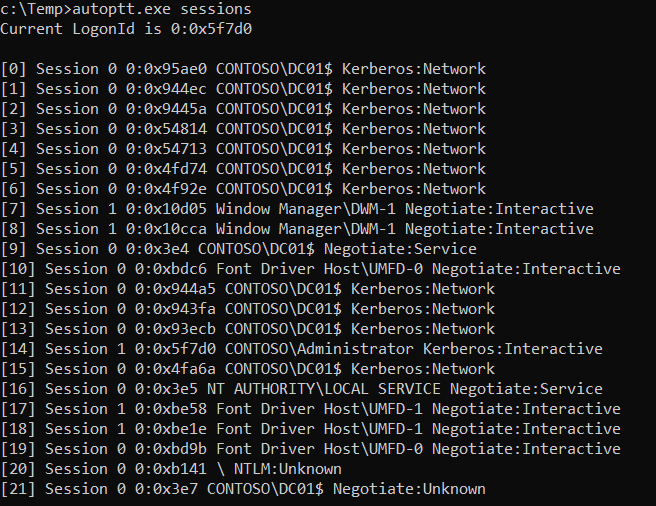 ricardojoserf/autoptt
Automated Pass-the-Ticket (PtT) attack. Standalone alternative to Rubeus and Mimikatz for this attack. In C#, C++, Crystal, Python, Rust, Golang, Nim…
 0xsh3llf1r3/coldwer
Cobalt Strike BOF to freeze EDR/AV processes and dump LSASS using WerFaultSecure.exe PPL bypass
 safebreach-labs/eventlogin-cve-2025-29969
Exploitation of CVE-2025-29969
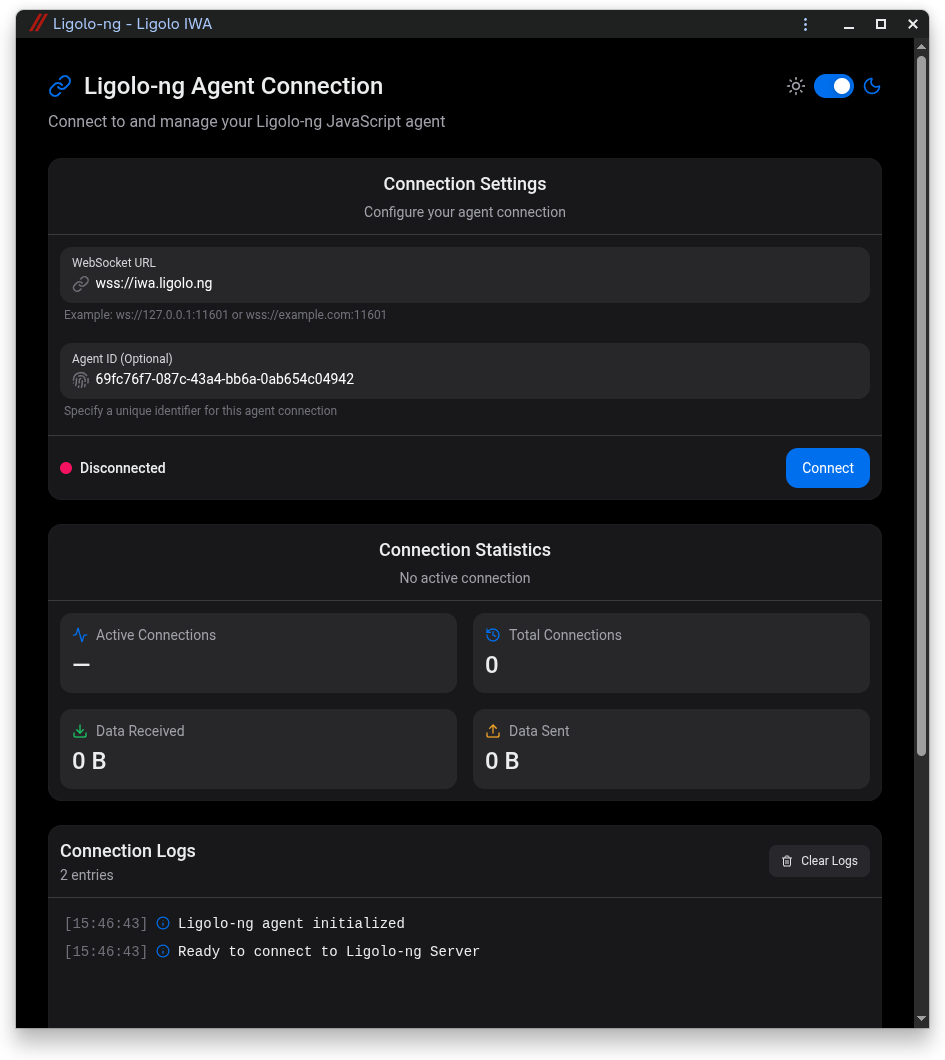 nicocha30/ligolo-iwa
A Ligolo-ng JavaScript agent working inside Chrome & Chromium-based browsers by leveraging Isolated Web Applications.
 akefallonitis/larac2shell
Cross-platform interactive shell for Microsoft Defender for Endpoint Live Response
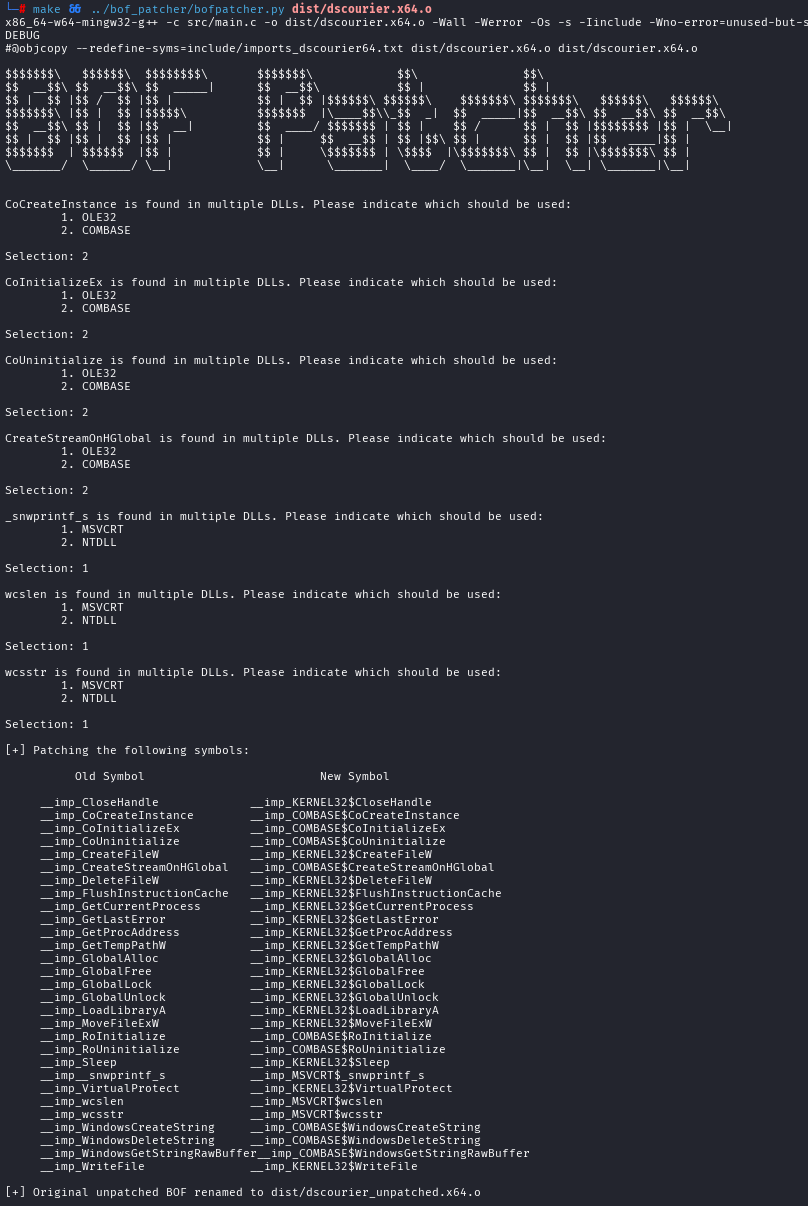 octoberfest7/dscourier_bof
BOF POC of the DSCourier project / invoking WinGet via COM
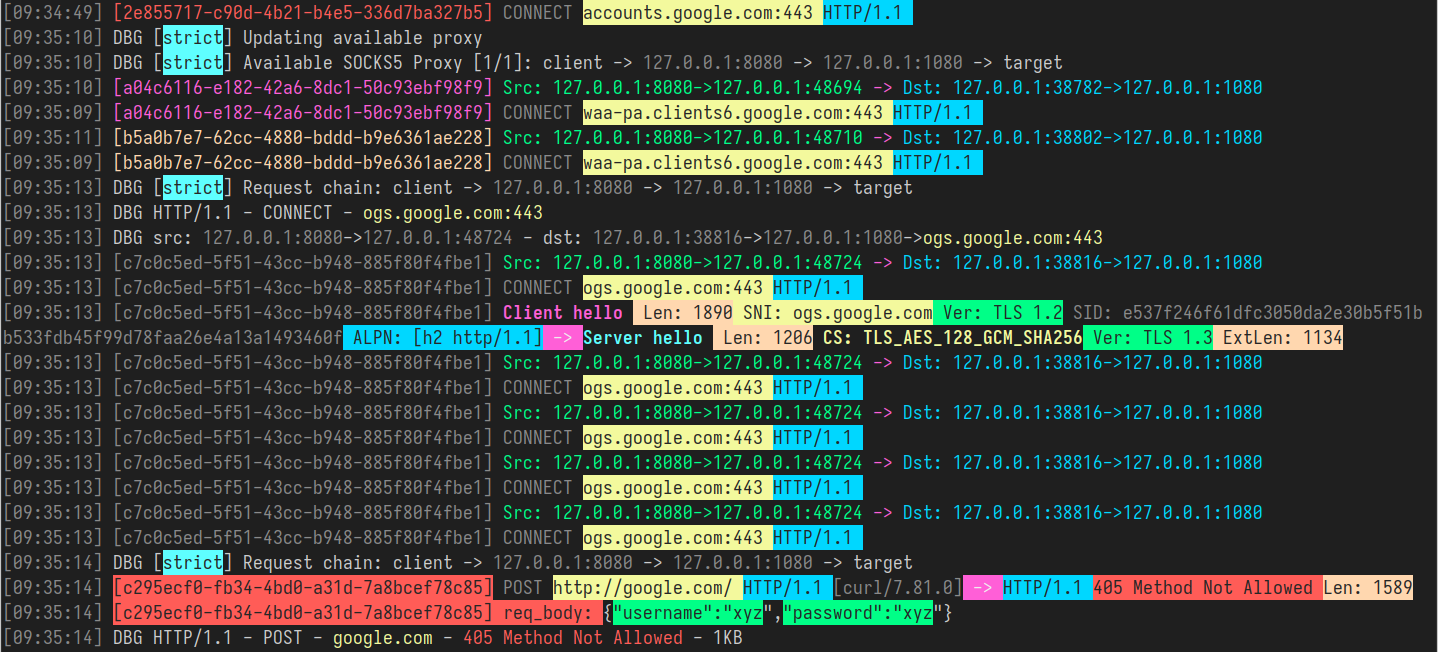 shadowy-pycoder/go-http-proxy-to-socks
CLI MITM proxy that converts SOCKS4/SOCKS5 into HTTP/HTTPS/HTTP2/HTTP3 proxy with transparent TCP/UDP redirection, ARP/NDP/DNS spoofing, traffic…
 caster-chen/cve-2026-8037-poc
包括能执行的命令探测和一键getshell(需要服务器部署服务)
 0xflagplz/ms-msdt-office-rce-follina
CVE-2022-30190 | MS-MSDT Follina One Click
 al1ex/cve-2020-11652
Exploit for SaltStack CVEs (CVE-2020-11651/11652) enabling remote command execution on master/minions, file read/upload, and reverse shell.
 jakobfriedl/tgt-monitor-bof
Async BOF to automatically extract or renew Kerberos TGTs on a target system.
 3t4n/samba-3.0.24-cve-2007-2447-vunerable-
Vulnerable Samba 3.0.24 environment for reproducing CVE-2007-2447 command execution, intended for exploit testing and security research.
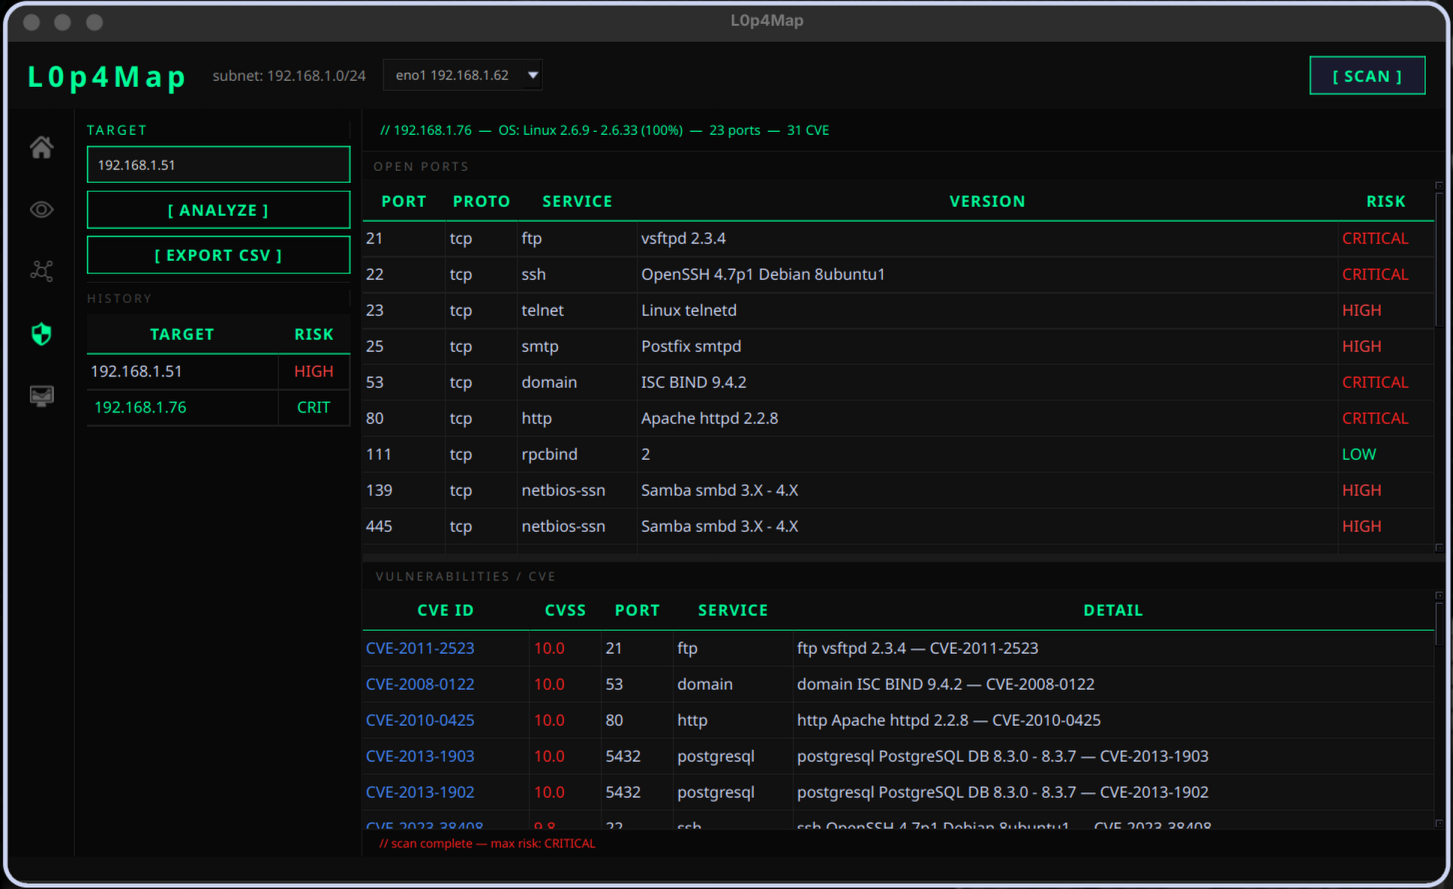 haxl0p4/l0p4map
Professional network monitoring & visualization tool. L0P4Map combines high-speed ARP discovery with full nmap integration and a real-time…
 frkngksl/silentnimvest
Nim implementation for sud0Ru's Credential Dumping from SAM/SECURITY Hives Method (a.k.a. SilentHarvest)
 4n4s4zi/cve-2025-33053_poc
POC exploit for CVE-2025-33053 (external control of file execution path in URL file)