
CVE-2021-4034
 luckythandel/cve-2021-4034
This is a POC for the vulnerability found in polkit's pkexec binary which is used to run programs as another users.
exploitationexploit-frameworkspenetration-testing+2
luckythandel/cve-2021-4034This is a POC for the vulnerability found in polkit's pkexec binary which is used to run programs as another users.
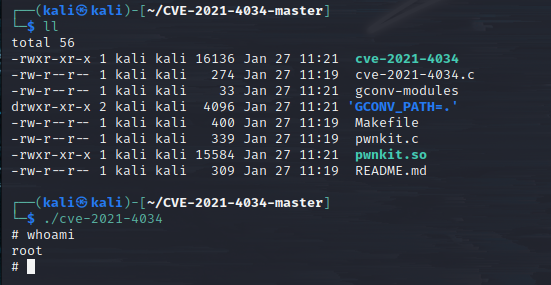 locksec/cve-2021-4034
Exploit PoC for the polkit pkexec (PWNKIT) vulnerability
 krn966/cve-2025-27591
Local privilege escalation exploit for CVE-2025-27591, abusing insecure symlink handling in the below utility's logging to overwrite arbitrary files…
 kalibb/cve-2026-28372-gnu-inetutils-telnetd-privilege-escalation-main
Proof-of-concept exploit for CVE-2026-28372, demonstrating local privilege escalation in GNU inetutils telnetd via environment variable injection to…
 jpmcb/pwnkit-go
Exploit for the PwnKit vulnerability, CVE-2021-4034, written in Go
 jostmart/-cve-2021-4034
Exploit for CVE-2021-4034, a local privilege escalation in polkit's pkexec, providing root access on Linux systems.
 jcatala/f_poc_cve-2021-4034
Proof-of-concept exploit for CVE-2021-4034, a local privilege escalation in polkit's pkexec, demonstrating exploitation via shared library injection.
 jbaines-r7/blankspace
Proof of Concept for EFSRPC Arbitrary File Upload (CVE-2021-43893)
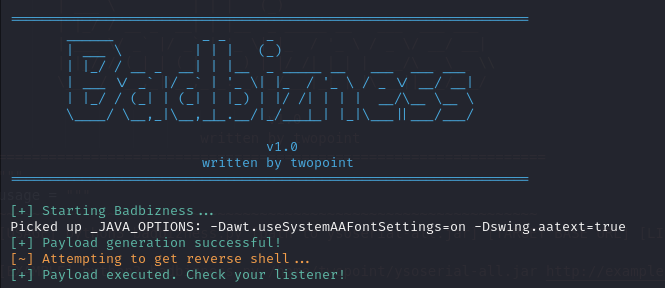 jakeotte/badbizness-cve-2023-51467
Auto exploit script for the Java web framework OF Biz under CVE-2023-51467.
 ivansmc/cve-2025-10353-poc
Exploit for CVE-2025-10353. Unauthenticated File Upload on Melis Platform Framework that leads to RCE
 ivansmc/cve-2025-10352-poc
Exploit for CVE-2025-10352. Admin account creation on Melis Platform Framework
 iss4cf0ng/cve-2026-31431-linux-copy-fail
Rust-based local privilege escalation exploit for CVE-2026-31431, enabling execution of custom shellcode such as Meterpreter on Linux systems.
 galoryber/cve-2026-31431-cleaned
Proof-of-concept exploit for CVE-2026-31431, a Linux kernel local privilege escalation via splice() and crafted socket options, enabling arbitrary…
 foxtrot/cve-2021-1965
Proof-of-concept exploit for CVE-2021-1965, a Wi-Fi vulnerability, leveraging libwifi for packet parsing and crafted for educational purposes.
 fnknda/cve-2021-4034_poc
Proof Of Concept for the 2021's pkexec vulnerability CVE-2021-4034
 febin0x10/fortinet_forticlient_exploit_cve-2026-24018
Local privilege escalation exploit for Fortinet FortiClientLinux, exploiting a symlink following vulnerability to gain root access on affected…
 fdellwing/cve-2021-4034
Dockerized proof-of-concept exploit for CVE-2021-4034 (PwnKit), demonstrating local privilege escalation in polkit's pkexec.
 fckoo/nanwinata-cve-2024-52301
Scans for CVE-2024-52301, an argument injection vulnerability in Laravel, using subfinder and httpx to identify affected web applications.