
cve-2022-36804
 tahtaciburak/cve-2022-36804
A simple PoC for Atlassian Bitbucket RCE [CVE-2022-36804]
exploitationpenetration-testingreconnaissance+2
7
tahtaciburak/cve-2022-36804A simple PoC for Atlassian Bitbucket RCE [CVE-2022-36804]
 maherazzouzi/cve-2022-36163
Proof-of-concept exploit for CVE-2022-36163, a format string vulnerability in pdftoroff hovacui 1.1.0 PDF reader, demonstrating local…
 pn-tester/cve-2022-35497
TM4WEB Vulnerability - CVE-2022-35497
 thehackingverse/cve-2022-3546
Proof-of-concept exploit for CVE-2022-3546, a stored XSS vulnerability in SourceCodester Simple Cold Storage Management System 1.0 via the Create…
 lohith19/cve-2022-3518
Proof-of-concept exploit for CVE-2022-3518, demonstrating the vulnerability and providing a basis for security testing and analysis.
 gylq/cve-2022-3464
A vulnerability classified as problematic has been found in puppyCMS up to 5.1. This affects an unknown part of the file /admin/settings.php. The…
 soy-oreocato/cve-2022-33679_checker
Lightweight Python checker that tests Active Directory credentials for exposure to CVE-2022-33679 (Kerberos AS-REP roast without pre-authentication).…
 p3nt3st3r-star/cve-2026-8732-poc
Multi-threaded mass scanner for CVE-2026-8732 in WordPress WP Google Map Pro. Automates nonce extraction, token exploitation, and hidden admin…
 m4fiab0y/cve-2022-30525
Zyxel Firewall Remote Command Injection Vulnerability (CVE-2022-30525) Batch Detection Script
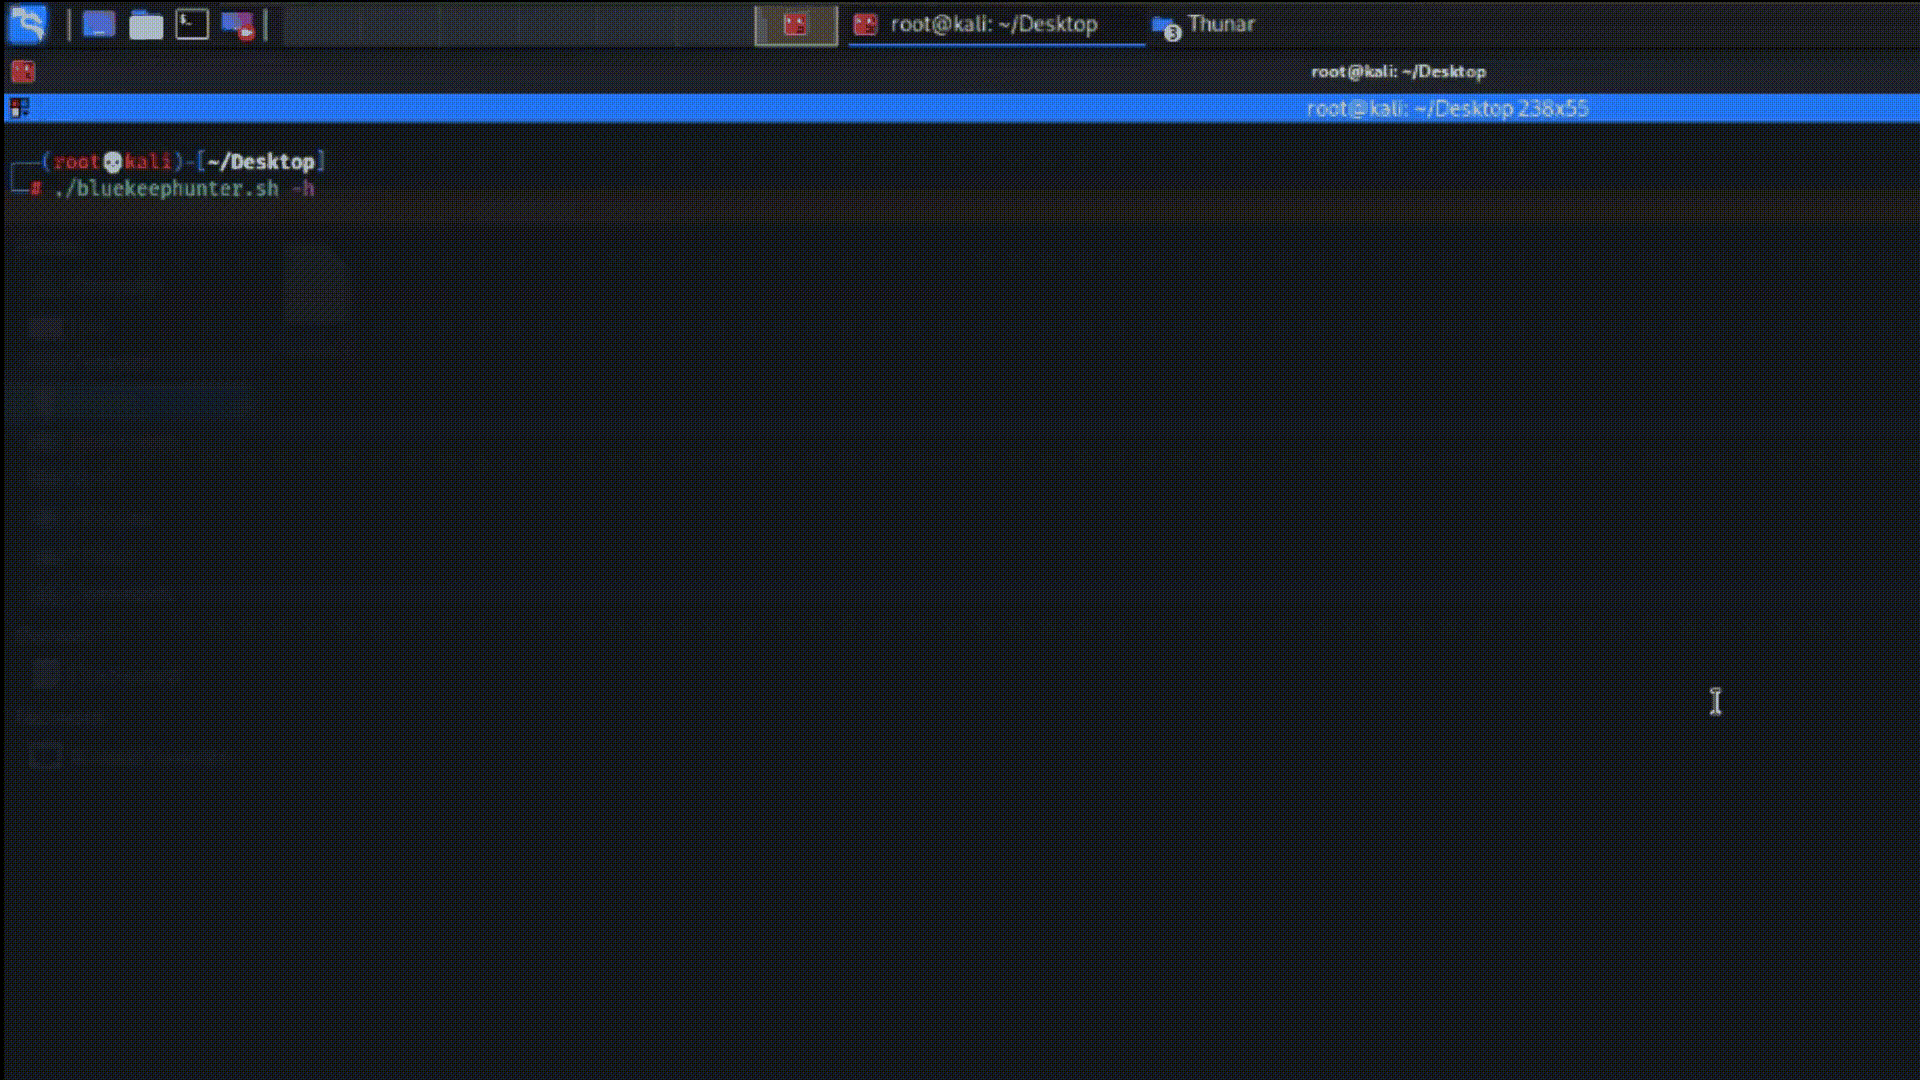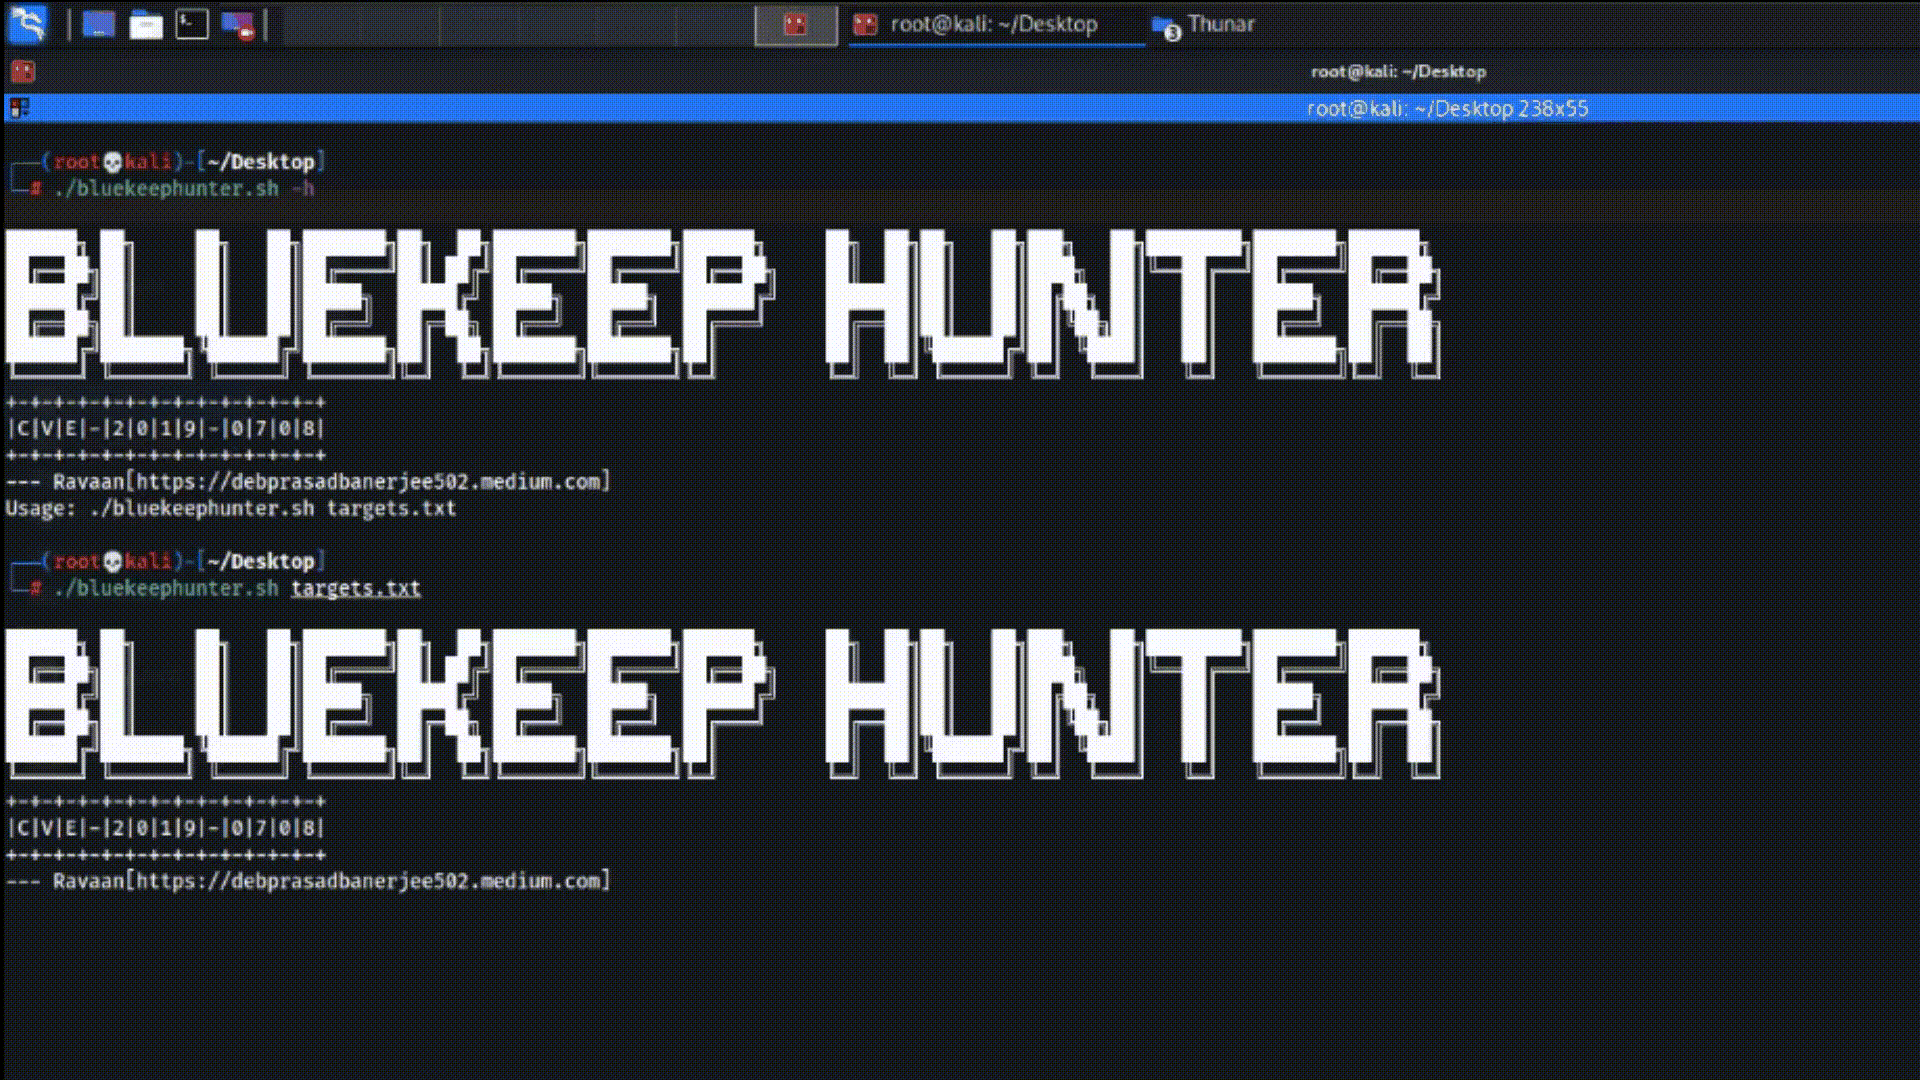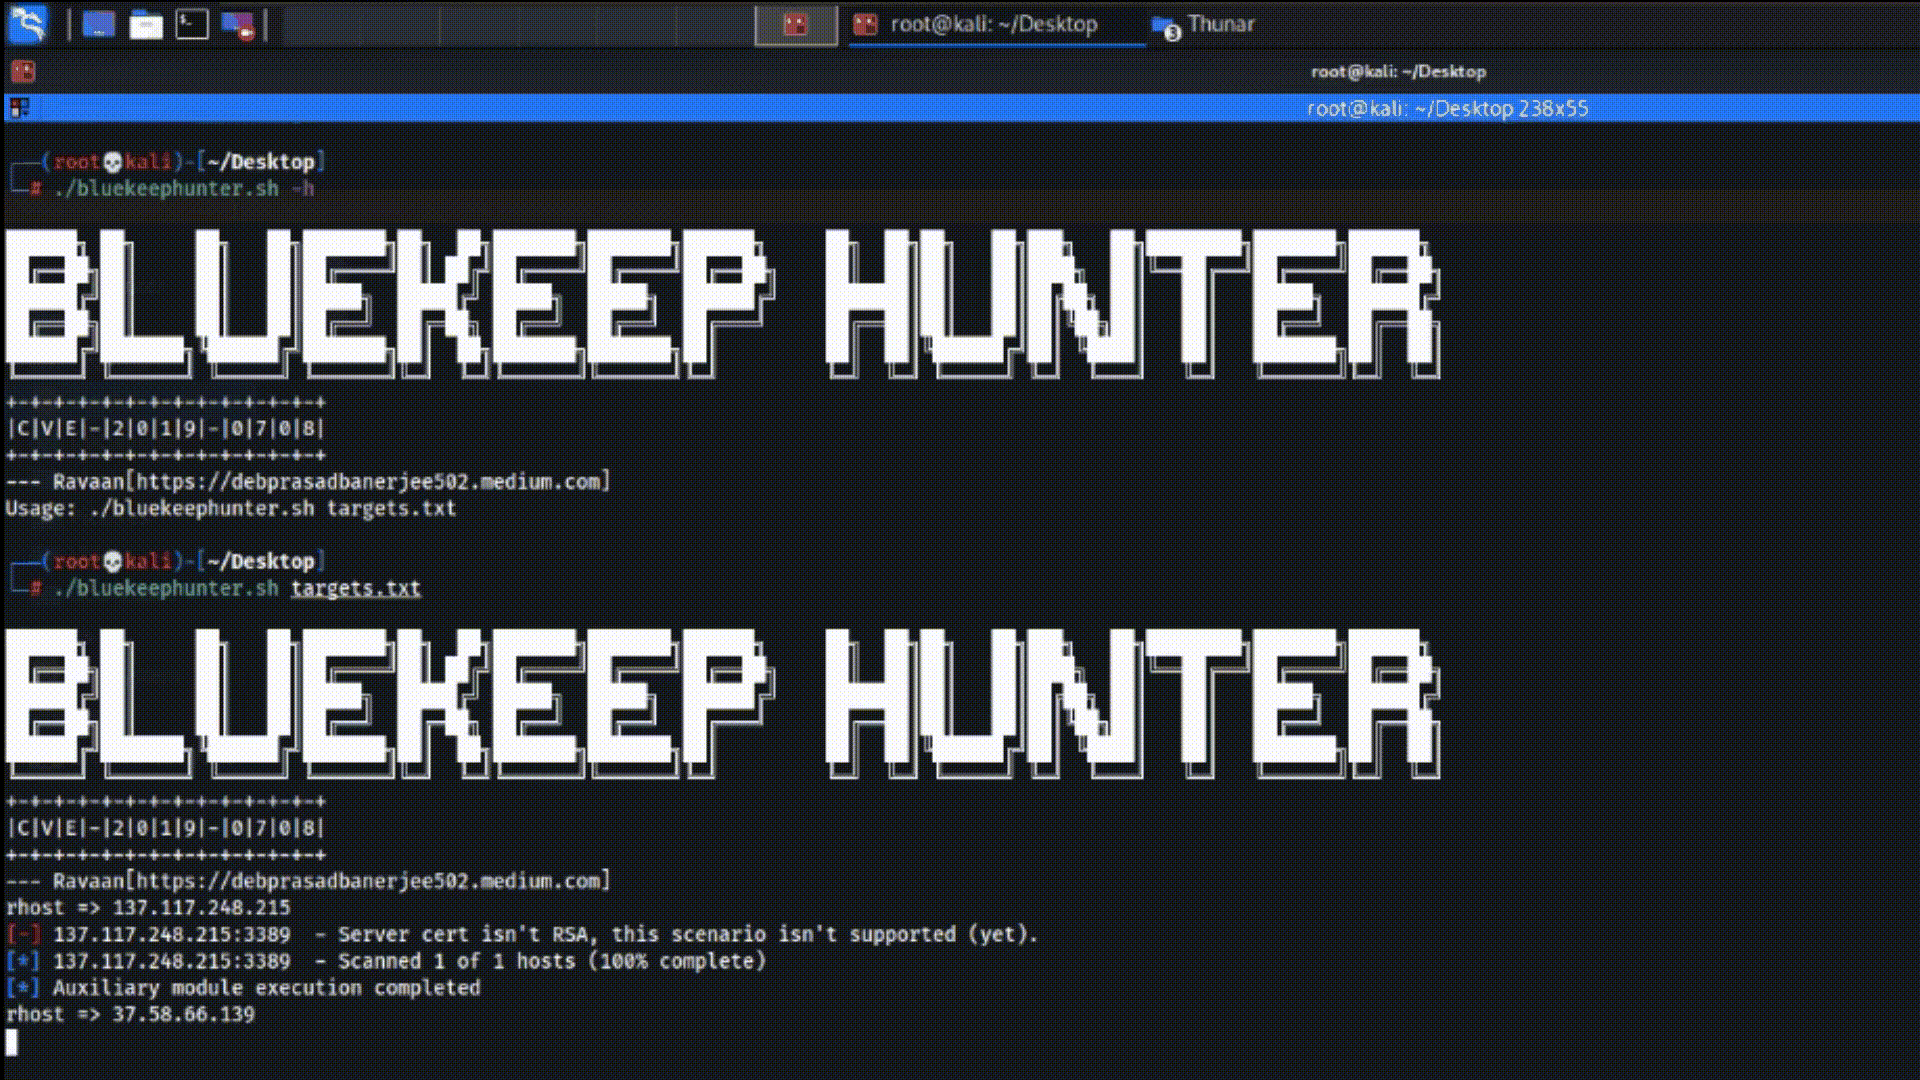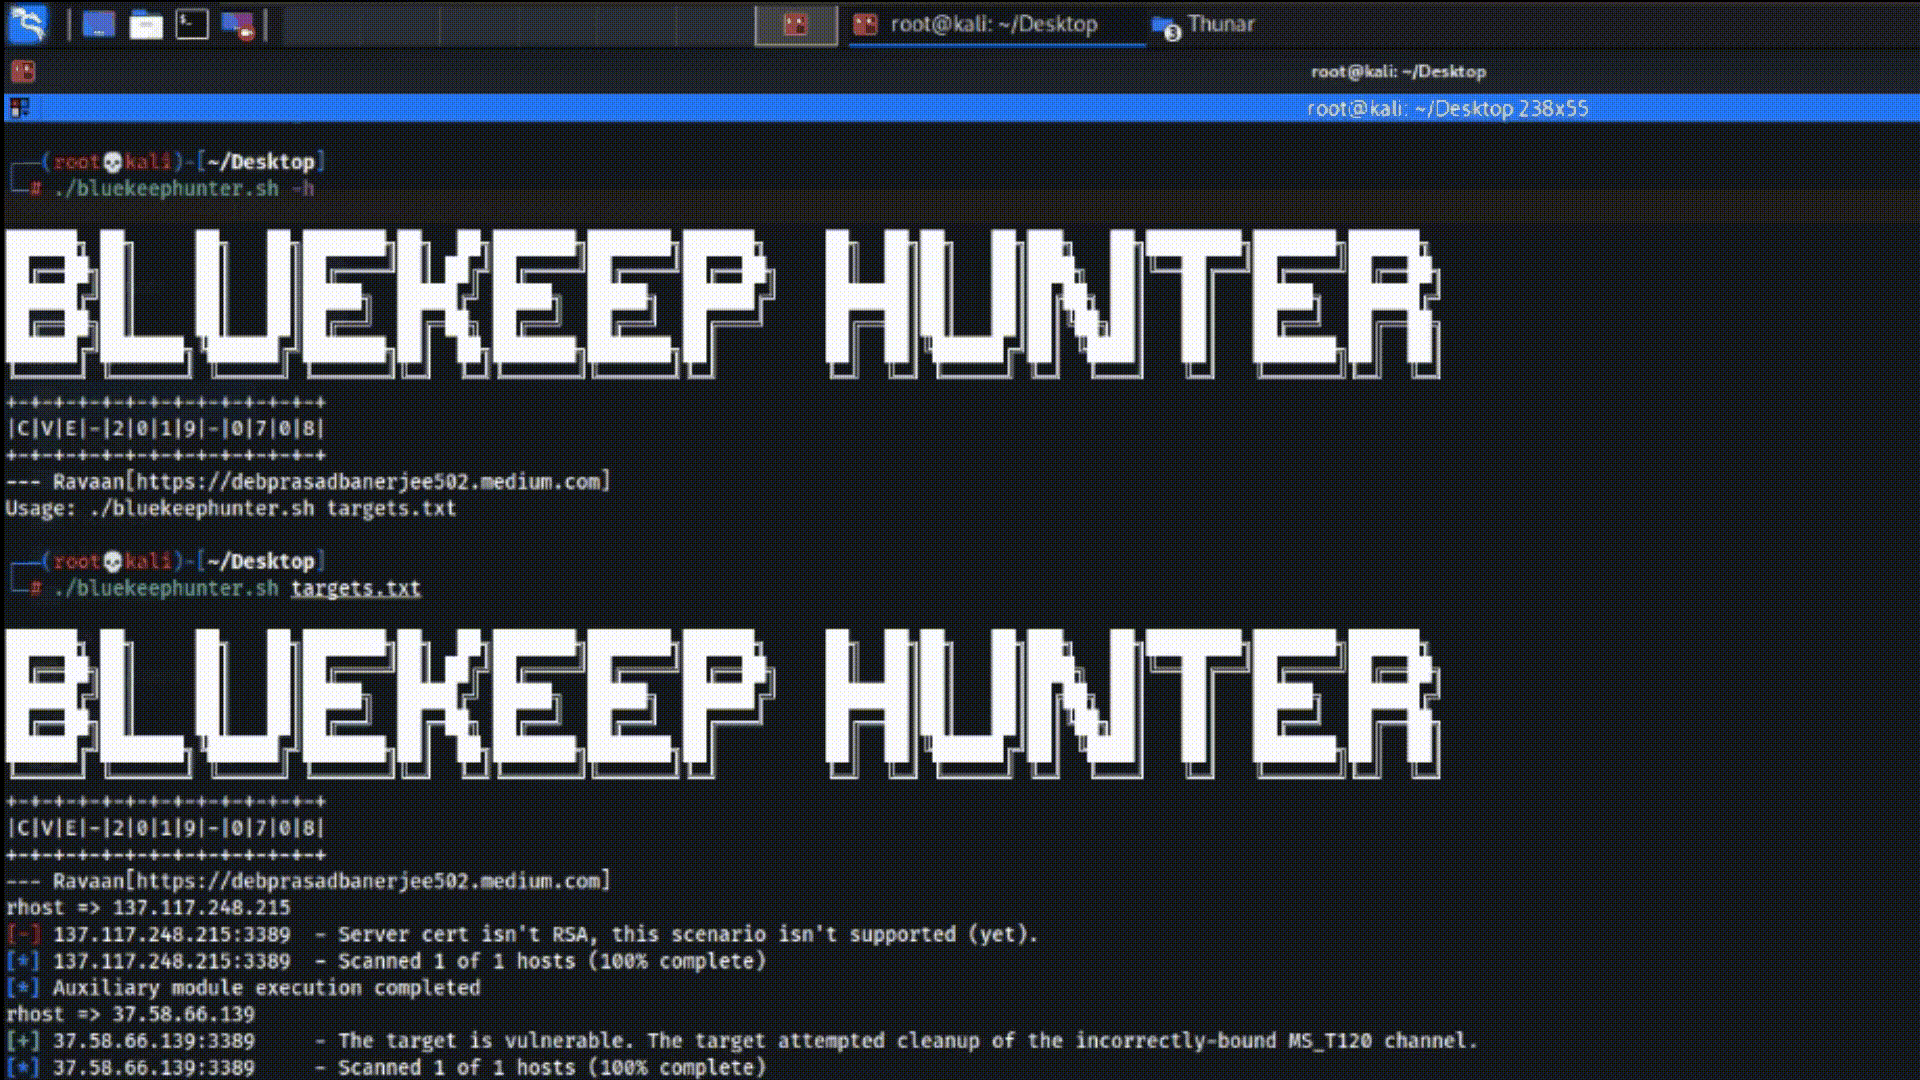 ravaan21/bluekeep-hunter
CVE-2019-0708, A tool which mass hunts for bluekeep vulnerability for exploitation.
 jotaqc/cve-2022-30190_temporary_fix
These are two Python scripts compiled to easily and quickly apply temporary protection against the CVE-2022-30190 vulnerability (Follina)
 m4fiab0y/cve-2022-30075
Proof-of-concept exploit for CVE-2022-30075, demonstrating a remote code execution vulnerability in a web application. Includes Python-based payload…
 pushkarup/cve-2022-29464
A PoC and Exploit for CVE 2022-29464
 haniwa0x01/cve-2022-30023
Authenticated command injection exploit for Tenda HG9 routers. Provides interactive remote shell access via Python script for penetration testing and…
 r4x0r1337/-cve-2022-29464
Python exploit for CVE-2022-29464 targeting a remote code execution vulnerability in WSO2 API Manager and Identity Server.
 reefspek/cocoapods-rce_cve-2024-38366
CocoaPods RCE Vulnerability CVE-2024-38366
 miko550/cve-2022-27925
Python exploit script for CVE-2022-27925 targeting Zimbra Collaboration Suite. Supports single URL or list-based scanning for remote code execution…
 shavchen/cve-2022-26138
Exploit for CVE-2022-26138, a SAML SSO bypass vulnerability in Atlassian products, with a FOFA dork for identifying vulnerable instances.