
CVE-2026-26119
 r3vpwnx/cve-2026-26119
WAC RCE - CVE-2026-26119 Windows Admin Center authenticated RCE via WinREST/PowerShell invokeCommand.
exploitationpenetration-testingvulnerability-analysis
r3vpwnx/cve-2026-26119WAC RCE - CVE-2026-26119 Windows Admin Center authenticated RCE via WinREST/PowerShell invokeCommand.
 gsadagopan/cve-2026-22747-sandbox
Sandboxed reproduction environment for CVE-2026-22747, enabling controlled testing and analysis of the vulnerability and potential exploits in an…
 chvancooten/follina.py
POC to replicate the full 'Follina' Office RCE vulnerability for testing purposes
 ch4120n/cve-2026-15409
Proof-of-Concept exploit for CVE-2026-15409 (SonicWall SMA 1000 RCE) via Erlang distribution over WebSocket. Achieves unauthenticated remote code…
 ch4120n/cve-2026-3891
PoC for CVE-2026-3891 – Unauthenticated File Upload RCE in Pix for WooCommerce ≤ 1.5.0. Automated nonce retrieval, PHP upload, and command execution.
 princeh4k/spring4shell-poc
Proof of Concept for exploiting the CVE-2022-22965 (Spring4Shell) vulnerability in an isolated environment, with Remote Code Execution (RCE)…
 fazilbaig1/cve-2026-26114-patch
patching N-day of CVE-2026-26114 before microsoft. where microsoft could not patch 100% in many months. but FAC security did it
 sam00/poc-cve-2026-32621-apollo-federation-xss-vulnerability
PoC exploit for CVE-2026-32621 demonstrating Apollo Federation deepMerge prototype pollution via crafted GraphQL aliases, with patched-version tests.
 sam00/poc-cve-2026-54121-certighost
Exploit toolkit for AD CS CVE-2026-54121: low-privileged domain users impersonate a Domain Controller, forge certificates, and compromise the domain…
 delbertgiovanni/test-xss-swagger-cve-2019-1749
PoC for testing reflected XSS in Swagger UI via CVE-2019-1749; sends crafted payloads and verifies vulnerable endpoints with minimal setup.
 hackerhouse-opensource/iscsicpl_bypassuac
UAC bypass for x64 Windows 7 - 11
 chip-red-pill/microcodedecryptor
Decrypts Intel Atom microcode updates and unpacks XuCode with recovered RC4 keys, revealing internal CPU microcode structures for hardware security…
 google/paranoid_crypto
Paranoid's library contains implementations of checks for well known weaknesses on cryptographic artifacts.
 jigerjain/interview_tips
Summary of Cyber Security interview questions I have been through, hope this helps
 k0keoyo/my_vulnerabilities
Collection of proof-of-concept exploits for vulnerabilities reported by the author, demonstrating exploitation techniques and vulnerability analysis.
 atlas0fd00m/vivisection
Analysis Plugin and Tools for Vivisect
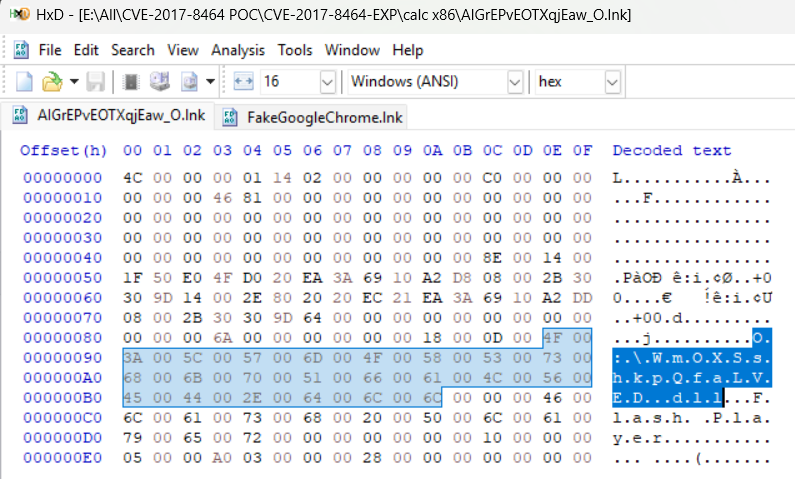 playboisk8/poc-cve-2017-8464-opencalculator
Exploiting the .lnk vulnerability and operating system handling mechanisms regarding explorer.exe and USB drives.
 masrikky/cve-2026-64600-refluxfs
A Linux kernel local privilege escalation affecting the XFS filesystem copy-on-write (CoW) path.