
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
203 results
FalconEye preview

FalconEye

GitHubrajiv2790/falconeye

Kernel-mode Windows driver for real-time detection of process injection techniques, including shellcode, DLL, and reflective injection, with syscall…
binary-analysisdefensive-toolsintrusion-detection+1
310
5 years ago
DarkLoadLibrary preview

DarkLoadLibrary

GitHubbats3c/darkloadlibrary

LoadLibrary for offensive operations
binary-analysisdefensive-toolsexploitation+2
1.2k5 years ago
WFH preview

WFH

GitHubconscioushacker/wfh

Frida-based dynamic analysis tool that automatically identifies DLL sideloading and COM hijacking vulnerabilities in Windows executables through…
binary-analysisdynamic-analysis-sandboxingexploitation+1
4364 years ago
AlanFramework preview

AlanFramework

GitHubenkomio/alanframework

A C2 post-exploitation framework
command-and-controlencryption-decryption-toolslateral-movement+7
4862 years ago
SigFlip preview

SigFlip

GitHubmed0x2e/sigflip

SigFlip is a tool for patching authenticode signed PE files (exe, dll, sys ..etc) without invalidating or breaking the existing signature.
binary-analysiscode-analysisdefensive-tools+5
1.3k3 years ago
CVE-2021-40444 preview

CVE-2021-40444

GitHublockedbyte/cve-2021-40444

Generates malicious DOCX documents exploiting CVE-2021-40444 (Microsoft Office RCE) with a hosted server for DLL payload delivery, based on…
exploitationmalware-analysispayload-generation+1
1.8k5 years ago
Limelighter preview

Limelighter

GitHubtylous/limelighter

A tool for generating fake code signing certificates or signing real ones
code-analysisexploitationpayload-generation+1
9755 years ago
ImpulsiveDLLHijack preview

ImpulsiveDLLHijack

GitHubknight0x07/impulsivedllhijack

C# based tool which automates the process of discovering and exploiting DLL Hijacks in target binaries. The Hijacked paths discovered can later be…

binary-exploitationexploitationpersistence-mechanisms+2
5545 years ago
aDLL preview

aDLL

GitHubideaslocas/adll

Automated DLL hijacking vulnerability discovery tool that analyzes PE binaries at load-time and runtime via API hooking, enumerating missing DLLs and…
binary-analysisdynamic-analysis-sandboxingexploitation+1
735 years ago
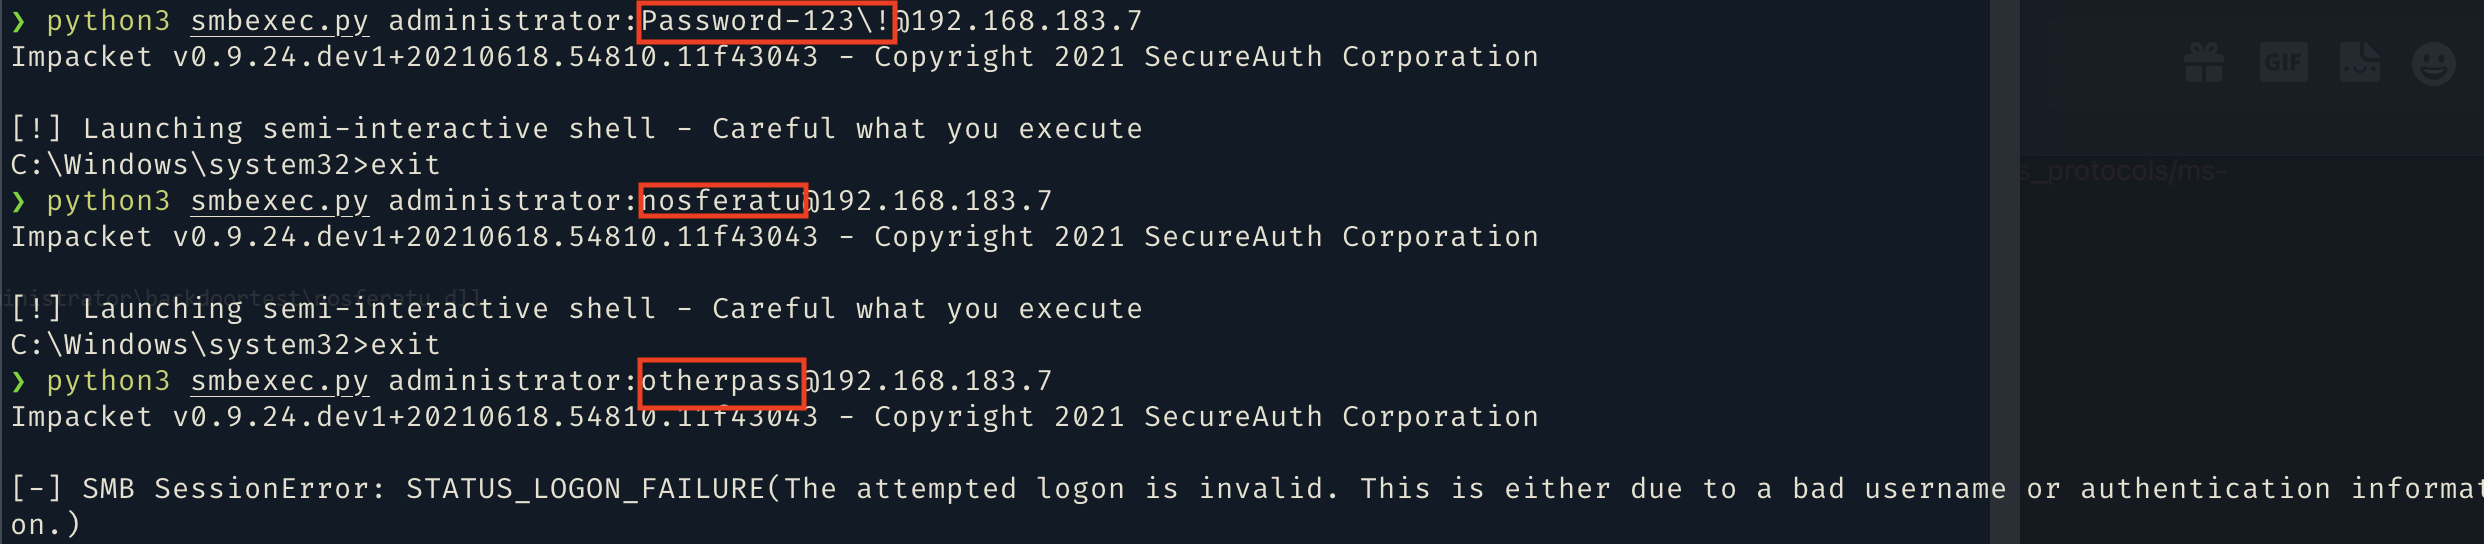
nosferatu preview

nosferatu

GitHubkindtime/nosferatu

DLL that hooks NTLM and Kerberos authentication in lsass.exe to inject a backdoor hash, enabling persistent authenticated access on Windows systems.
authenticationlateral-movementpenetration-testing+2
2421 year ago
DuplicateDump preview

DuplicateDump

GitHubhagrid29/duplicatedump

Dumping LSASS with a duplicated handle from custom LSA plugin
post-exploitationprivilege-escalationred-teaming
2074 years ago
reverse_ssh preview

reverse_ssh

GitHubnhas/reverse_ssh

SSH-based reverse shell management tool with native SCP/SFTP support, multiple transport protocols, Windows DLL generation, and fileless execution…
shellcodeshellcode-generation
1.4k1 month ago
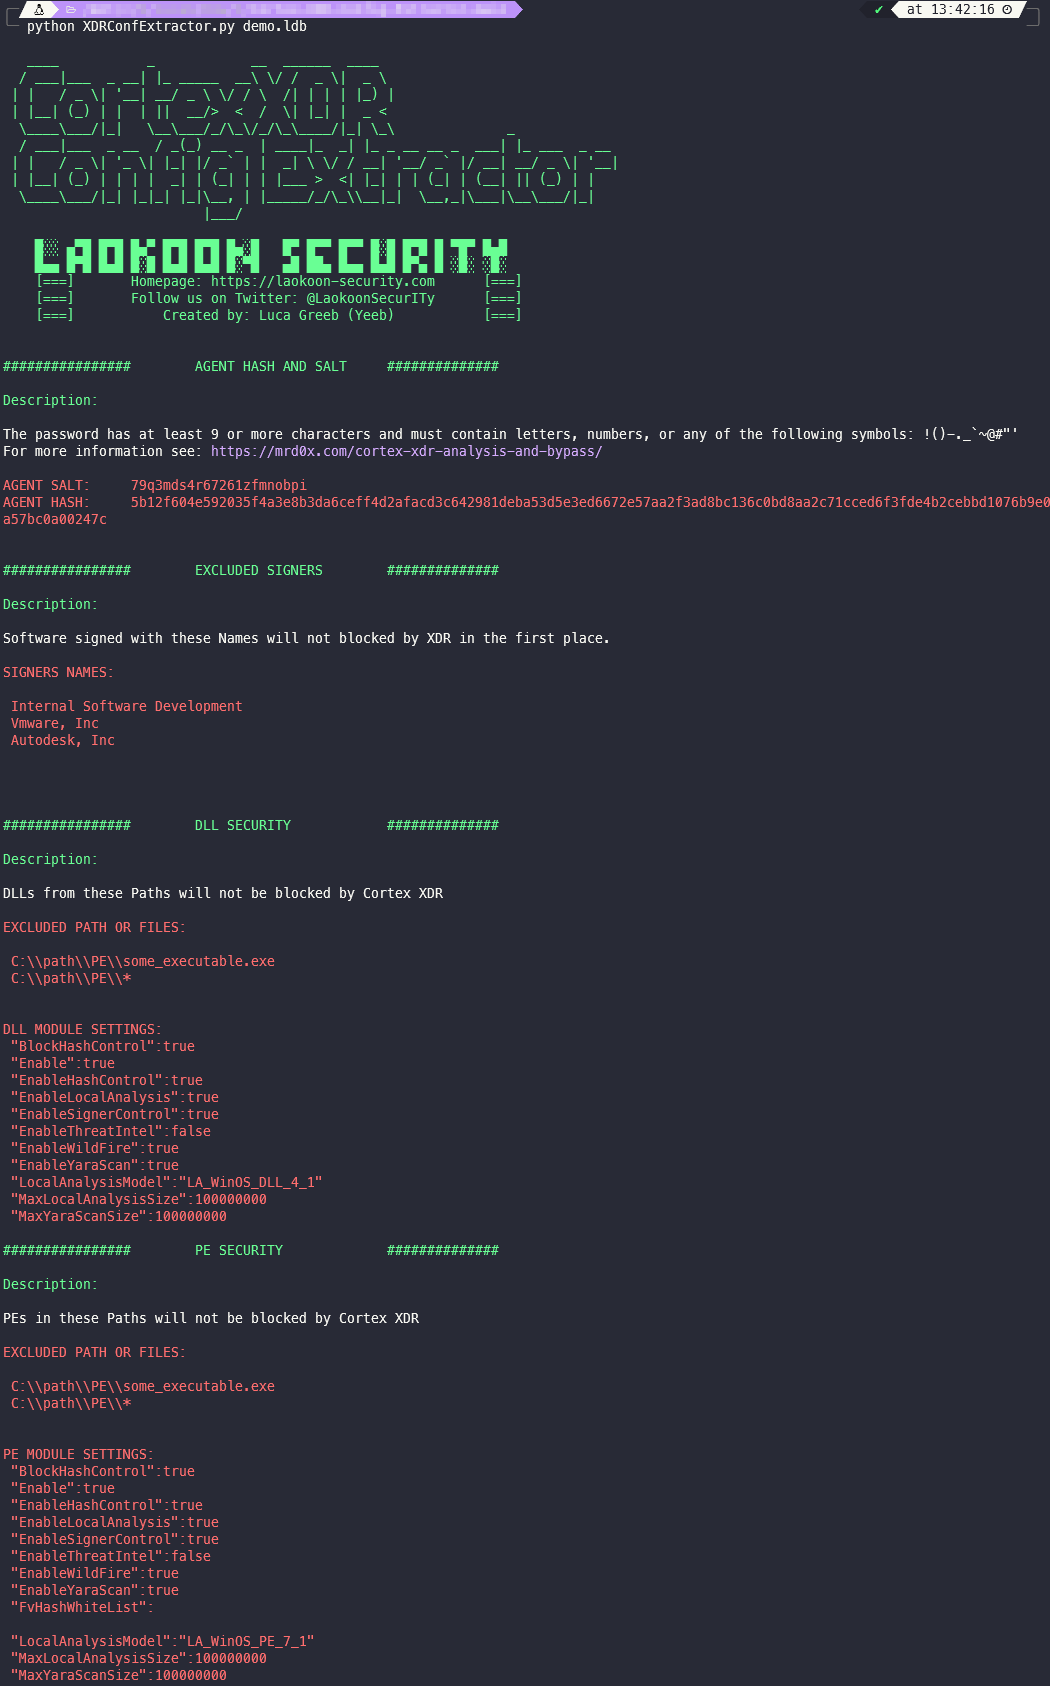
Cortex-XDR-Config-Extractor preview

Cortex-XDR-Config-Extractor

GitHublaokoon-security/cortex-xdr-config-extractor

Parses Cortex XDR agent database lock files to extract agent settings, uninstall password hash/salt, and security exclusions for red team assessments…

configuration-auditingpassword-crackingpenetration-testing+1
1413 years ago
CertVerify preview

CertVerify

GitHubpassword123456/certverify

A scanner that files with compromised or untrusted code signing certificates written in python.
code-analysisforensicsmalware-analysis+1
643 years ago
C2-Tool-Collection preview

C2-Tool-Collection

GitHuboutflanknl/c2-tool-collection

A collection of tools which integrate with Cobalt Strike (and possibly other C2 frameworks) through BOF and reflective DLL loading techniques.
command-and-controlexploit-frameworksinformation-gathering+8
1.4k3 years ago
uac-a-mola preview

uac-a-mola

GitHubtelefonica/uac-a-mola

Modular framework for Windows UAC bypass attacks and mitigation, featuring DLL hijacking, fileless execution, and real-time monitoring to detect and…

defensive-toolsexploit-frameworkspenetration-testing+1
1075 years ago
LightsOut preview

LightsOut

GitHubicyguider/lightsout

Generate an obfuscated DLL that will disable AMSI & ETW

defensive-toolsexploitationpayload-generation+1
3352 years ago
DllNotificationInjection preview

DllNotificationInjection

GitHubdec0ne/dllnotificationinjection

A POC of a new “threadless” process injection technique that works by utilizing the concept of DLL Notification Callbacks in local and remote…

exploitationred-teamingshellcode
4713 years ago
Previous1…9101112Next