
CVE-2024-6387
 hasan8babiker/cve-2024-6387
PoC exploit for CVE-2024-6387 (OpenSSH regreSSHion), targeting sshd signal handler race condition for remote code execution on glibc Linux systems.
exploitationpenetration-testingvulnerability-analysis
hasan8babiker/cve-2024-6387PoC exploit for CVE-2024-6387 (OpenSSH regreSSHion), targeting sshd signal handler race condition for remote code execution on glibc Linux systems.
 blendin/3snake
Tool for extracting information from newly spawned processes
 mrash/fwknop
Single Packet Authorization > Port Knocking
 xonoxitron/regresshion
CVE-2024-6387 (regreSSHion) Exploit (PoC), a vulnerability in OpenSSH's server (sshd) on glibc-based Linux systems.
 lexfo/sshimpanzee
SSHD Based implant supporting tunneling mecanisms to reach the C2 (DNS, ICMP, HTTP Encapsulation, HTTP/Socks Proxies, UDP...)
 michel-dv/xz-utils-backdoor-case-study
Technical case study of the XZ Utils backdoor (CVE-2024-3094), covering supply-chain trust abuse, malicious release artifacts, build-stage injection,…
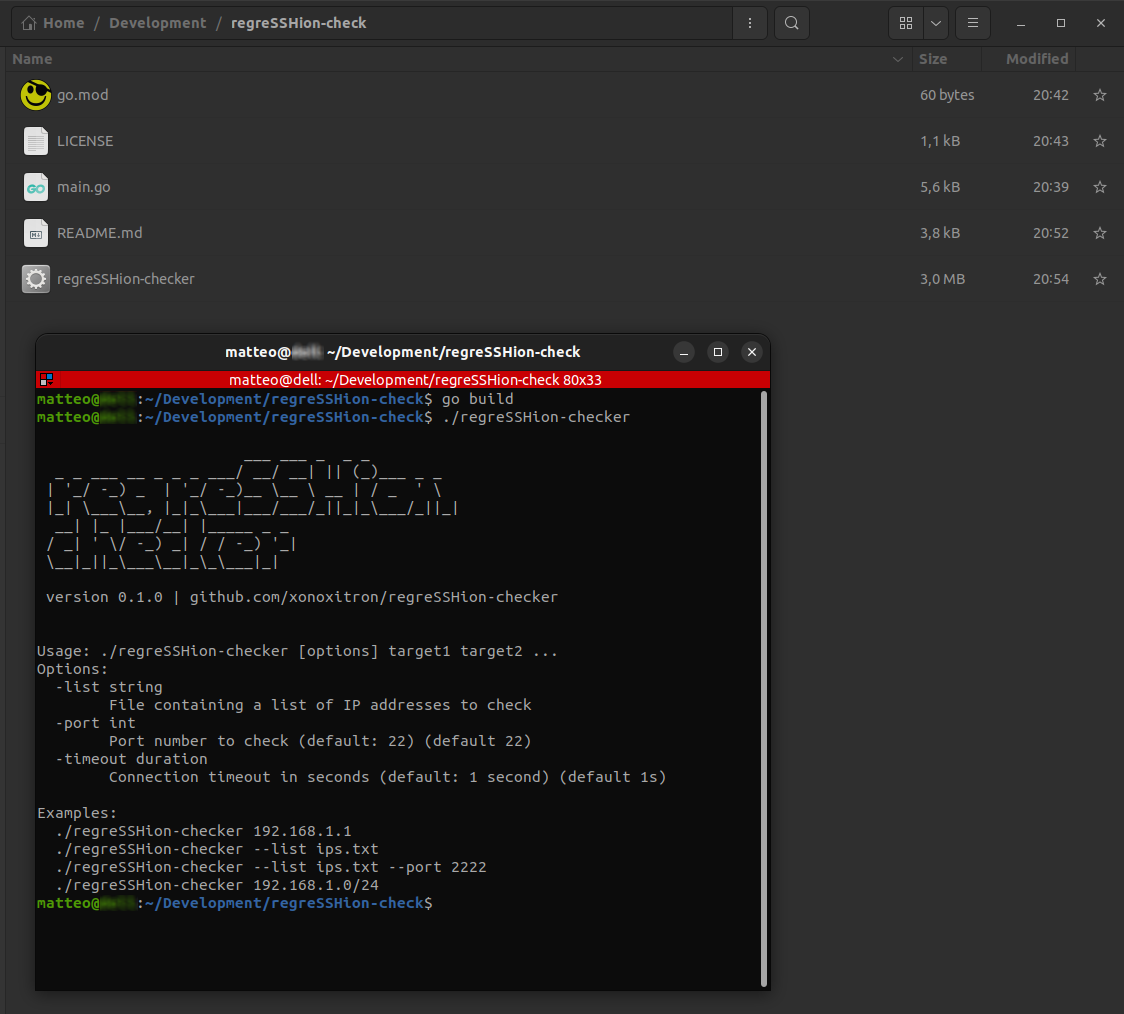 xonoxitron/regresshion-checker
Quickly identifies servers vulnerable to OpenSSH 'regreSSHion' (CVE-2024-6387).
 lockness-ko/xz-vulnerable-honeypot
An ssh honeypot with the XZ backdoor. CVE-2024-3094
 anhvutuan/cve-2024-6387-poc-1
CVE-2024-6387, also known as RegreSSHion, is a high-severity vulnerability found in OpenSSH servers (sshd) running on glibc-based Linux systems. It…
 sardine-web/cve-2024-6387_check
A security regression (CVE-2006-5051) was discovered in OpenSSH's server (sshd). There is a race condition which can lead to sshd to handle some…
 prodefense/hawk
Golang tool designed to exfiltrate passwords found via the sshd and su services
 business1sg00d/cve-2023-25136
Looking into the memory when sshd 9.1p1 aborts due to a double free bug.
 tam-k592/cve-2024-6387
Recently, the OpenSSH maintainers released security updates to fix a critical vulnerability that could lead to unauthenticated remote code execution…
 sxlmnwb/cve-2024-6387
Targeting a signal handler race condition in OpenSSH's server (sshd) on glibc-based Linux systems.
 iheb2b/cve-2024-3094-checker
Bash script to detect CVE-2024-3094 vulnerability in XZ/LZMA utilities on Linux. Checks XZ version, SSHD LZMA linkage, and byte patterns, outputting…
 alex14324/ssh_poc2024
An exploit for CVE-2024-6387, targeting a signal handler race condition in OpenSSH's server
 shoucheng3/apache__mina-sshd_cve-2023-35887_2-9-2
Pure Java SSH client/server library implementing SSH-2 protocol with support for multiple ciphers, key exchanges, authentication methods, SFTP, SCP,…
 passwa11/cve-2024-6387-poc
Proof-of-concept exploit for CVE-2024-6387, a signal handler race condition in OpenSSH's sshd, enabling remote code execution on vulnerable servers.