

PEASS-ng
 peass-ng/peass-ng
PEASS - Privilege Escalation Awesome Scripts SUITE (with colors)
educationexploitationexploit-frameworks+7
peass-ng/peass-ngPEASS - Privilege Escalation Awesome Scripts SUITE (with colors)
 iamsopotatoe-coder/tinyload
Open source Windows x64 PE packer and crypter. Compresses and encrypts executables with a custom virtual machine into a self extracting stub.
 med0x2e/sigflip
SigFlip is a tool for patching authenticode signed PE files (exe, dll, sys ..etc) without invalidating or breaking the existing signature.
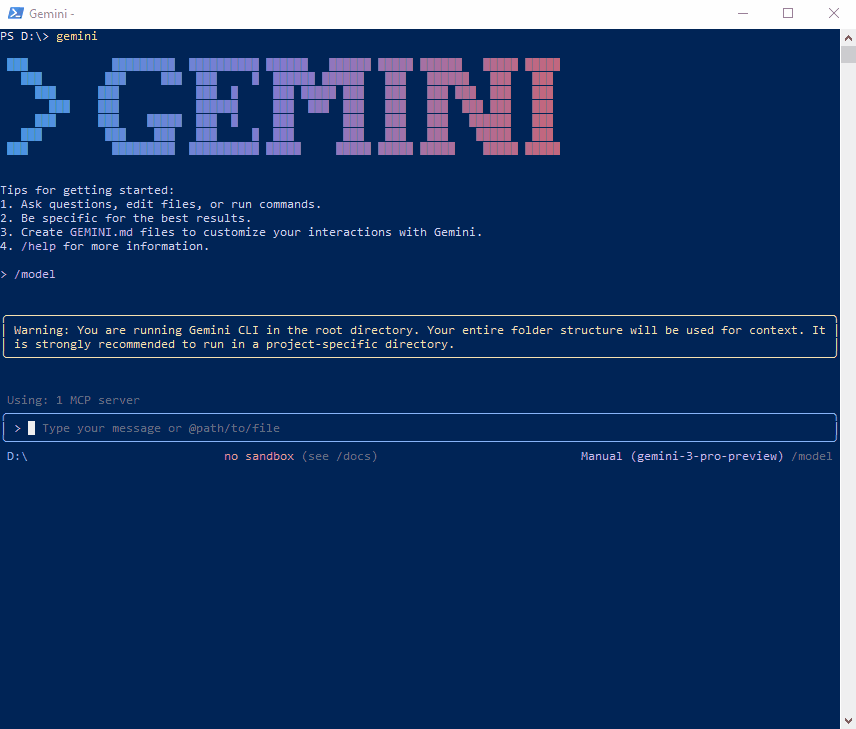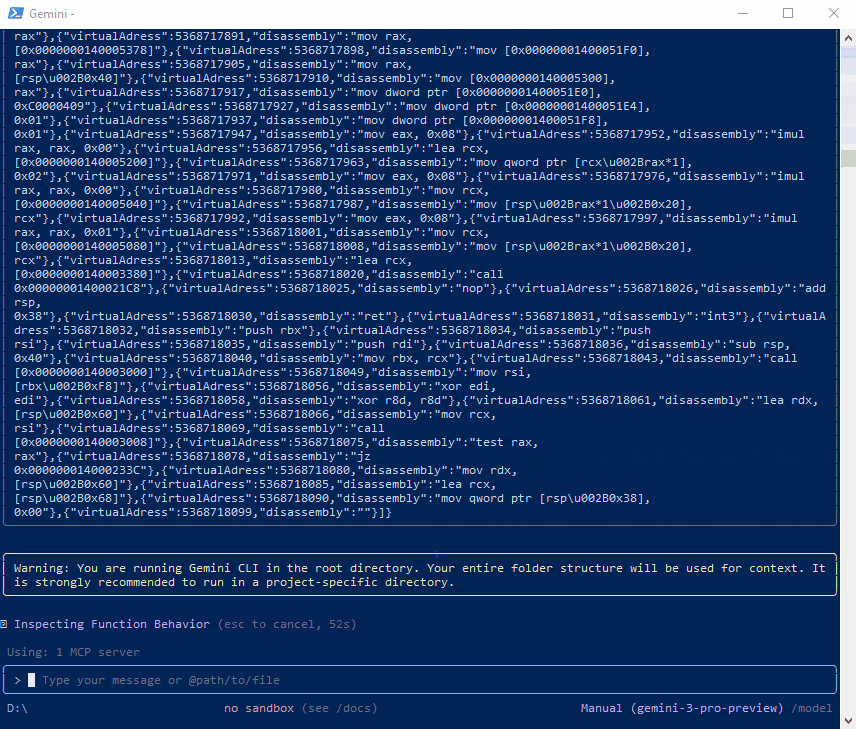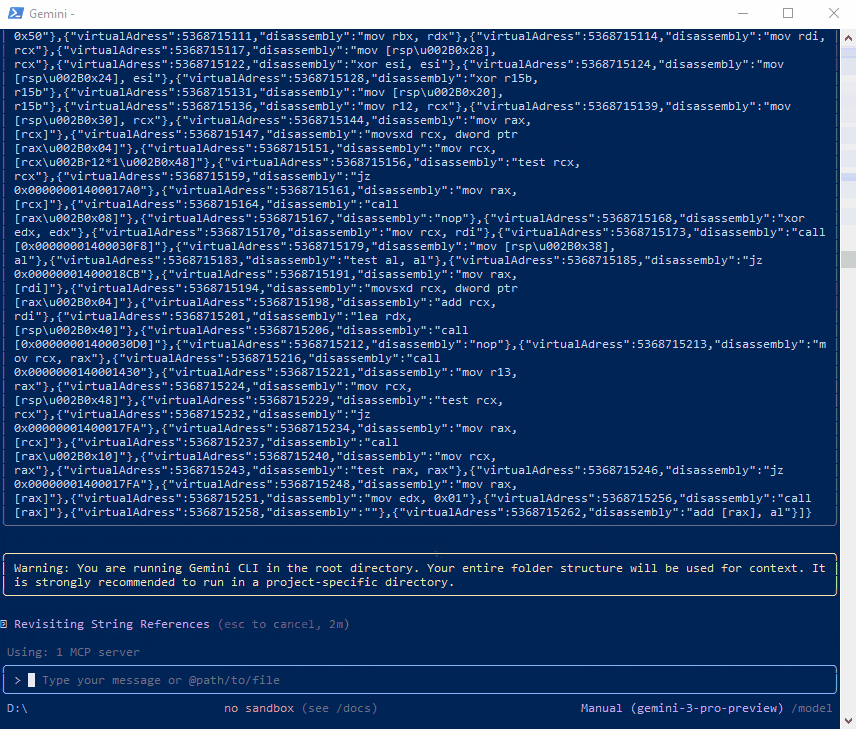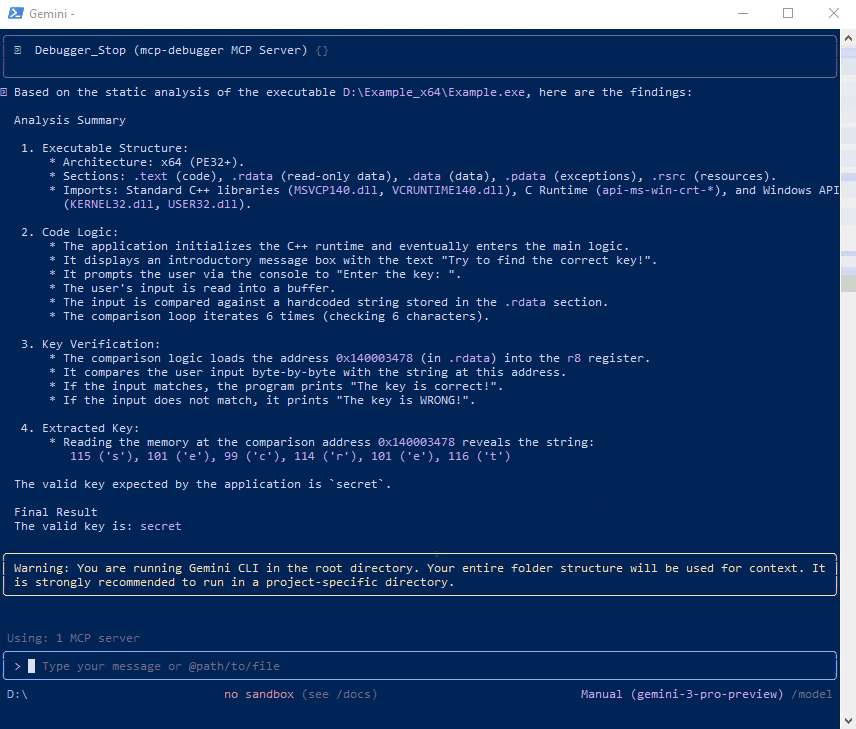 fatmike-gh/mcpdebugger
A MCP Debugger Server for Windows executables (x86 and x64). Exposes debugger functionality as MCP Tools for static / dynamic analysis of the…
 0x574r/darkcloak
Linux process identity cloaking tool that spoofs comm, argv, cmdline, environ, exe path, and VMAs via an 11-phase prctl pipeline to impersonate…
 0xrootpls/fritter
Polymorphic shellcode generator for in-memory execution of EXE, DLL, .NET, VBScript, and JScript with per-output and per-build randomization for…
 eonrickity/cve-2017-0213
Fixed No Virus Manual Automatic Loader exe no zip because zip picks up the anti virus detector.
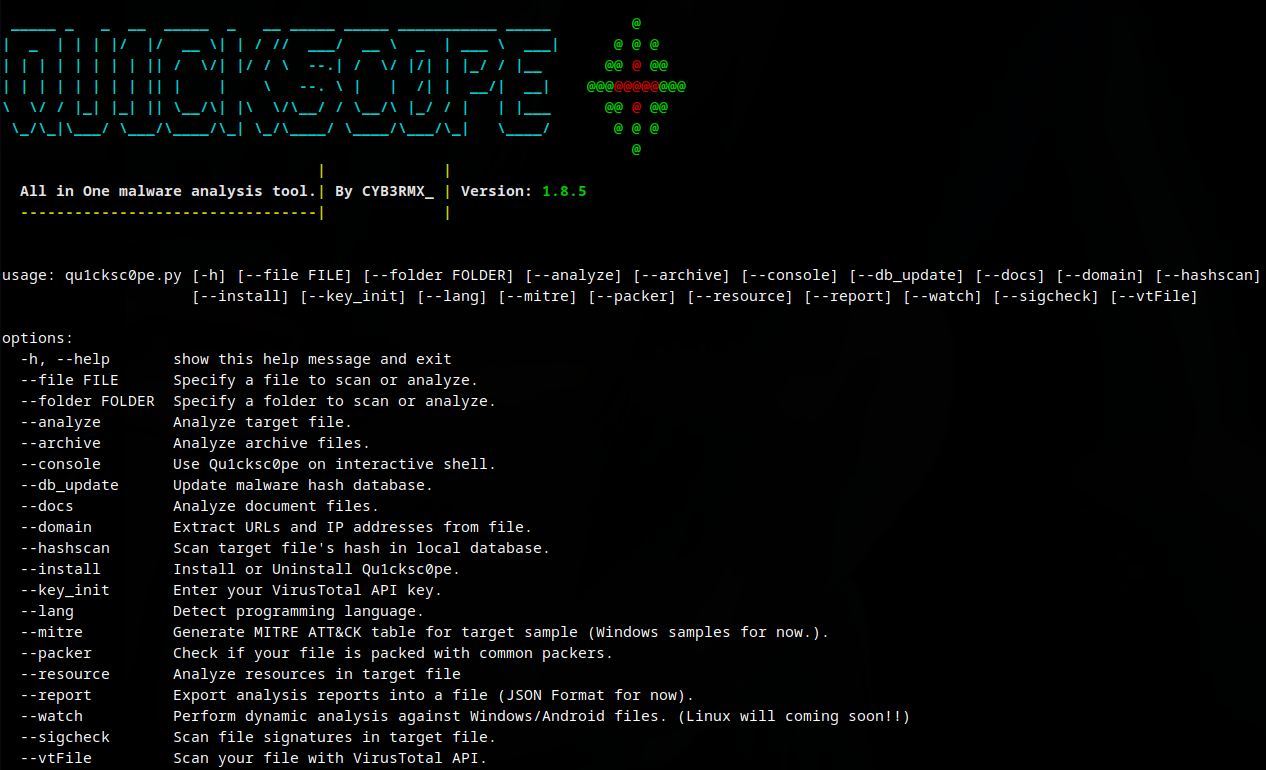 cyb3rmx/qu1cksc0pe
All-in-One malware analysis tool.
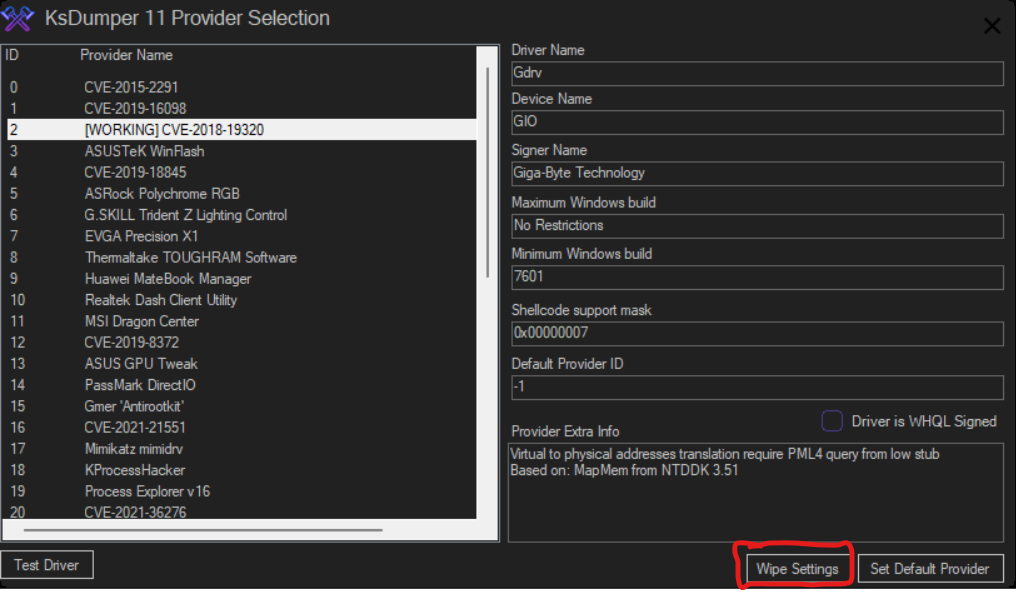 mastercodeon314/ksdumper-11
A revival of the classic and legendary KsDumper
 yhs0602/android-disassembler
Disassemble ANY files including .so (NDK, JNI), Windows PE(EXE, DLL, SYS, etc), linux binaries, libraries, and any other files such as pictures,…
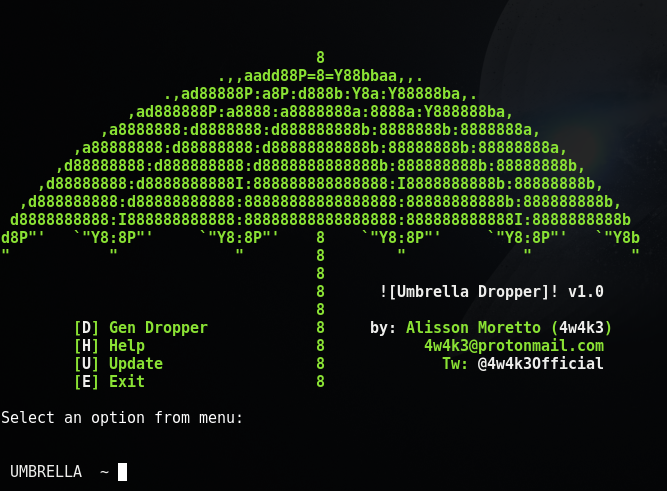 4w4k3/umbrella
A Phishing Dropper designed to Pentest.
 naksyn/pythonmemorymodule
pure-python implementation of MemoryModule technique to load dll and unmanaged exe entirely from memory
 osandamalith/exe2image
A simple utility to convert EXE files to JPEG images and vice versa.
 optiv/mangle
Mangle is a tool that manipulates aspects of compiled executables (.exe or DLL) to avoid detection from EDRs
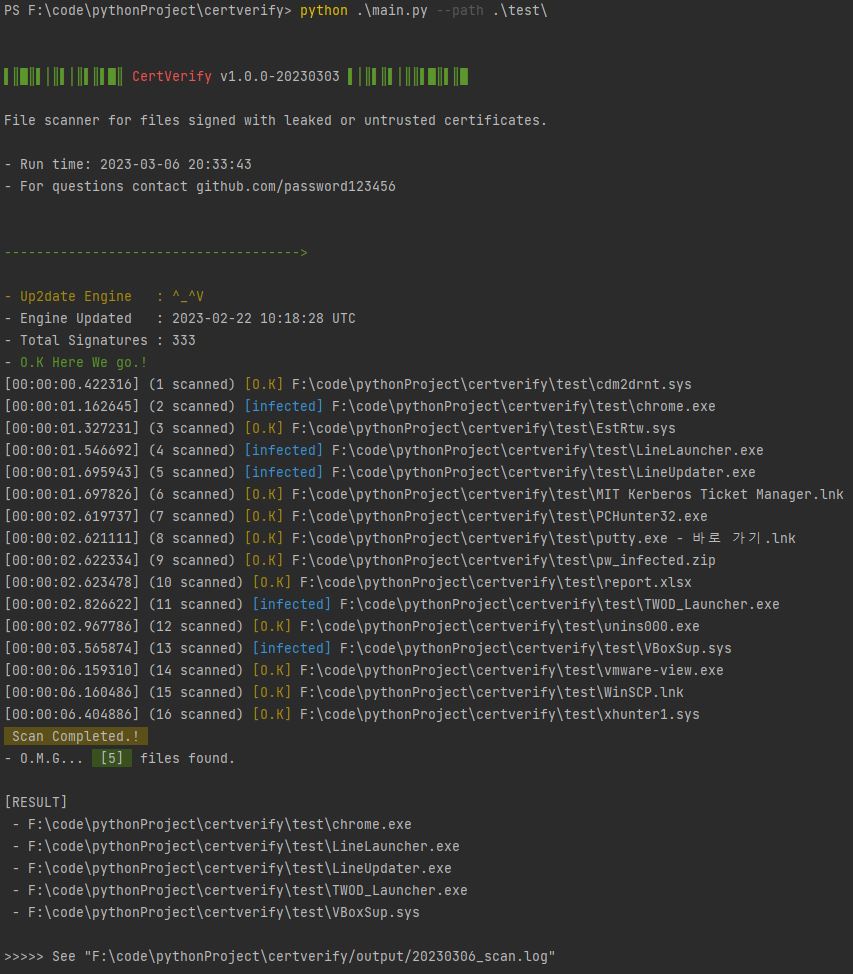 password123456/certverify
A scanner that files with compromised or untrusted code signing certificates written in python.
 jonatan1024/clrinject
Injects C# EXE or DLL Assembly into every CLR runtime and AppDomain of another process.
 yanncam/exe2powershell
exe2powershell - exe2bat reborn for modern Windows
 sec13b/ms09-050_cve-2009-3103
CVE-2009-3103 ms09-050