
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
22 results
CVE-2024-36401-PoC preview

CVE-2024-36401-PoC

GitHuby1s4s/cve-2024-36401-poc

Proof-of-concept exploit for CVE-2024-36401 enabling remote code execution via HTTP requests with reverse shell payload generation and Base64…
exploitationpayload-generationpenetration-testing+3
2 years ago
burp-cc-bridge preview

burp-cc-bridge

GitHublarrypeseckis/burp-cc-bridge

REST API automation for Burp Suite Community Edition. Drop-in Java extension exposing send/repeat/history endpoints over a local HTTP API.
api-security-testingpenetration-testingscripting-automation+3
74 months ago
HTTP-Shell preview

HTTP-Shell

GitHubjoelgmsec/http-shell

Multiplatform HTTP reverse shell providing a shell-like interface over HTTP, with file upload/download, command history, auto-reconnection, and sudo…
command-and-controlpayload-generationpenetration-testing+2
2422 months ago
CVE-2021-26828-Ultimate preview

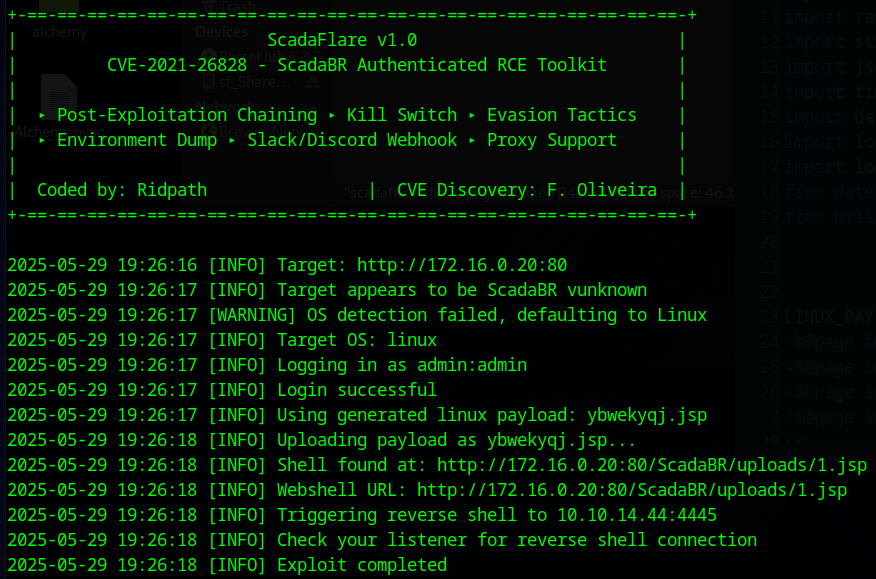
CVE-2021-26828-Ultimate

GitHubridpath/cve-2021-26828-ultimate

ScadaFlare Authenticated RCE Exploit Framework for ScadaBR (CVE-2021-26828) OpenPLC ScadaBR
command-and-controlexploitationinformation-gathering+6
510 months ago
CVE-2026-67340_exploit preview

CVE-2026-67340_exploit

GitHub0xdak/cve-2026-67340_exploit

Post-auth RCE exploit for ArcadeDB via JavaScript trigger GraalVM sandbox escape, executing OS commands over HTTP API with reverse shell or blind…
database-securityexploitationpenetration-testing+1
2 months ago
CVE-2026-5029-Exploit preview

CVE-2026-5029-Exploit

GitHub0x00phantom-hat/cve-2026-5029-exploit

Proof-of-concept exploit for CVE-2026-5029, delivering unauthenticated remote code execution via the run-code MCP tool on exposed HTTP endpoints.…
code-analysiseducationexploitation+3
3 months ago
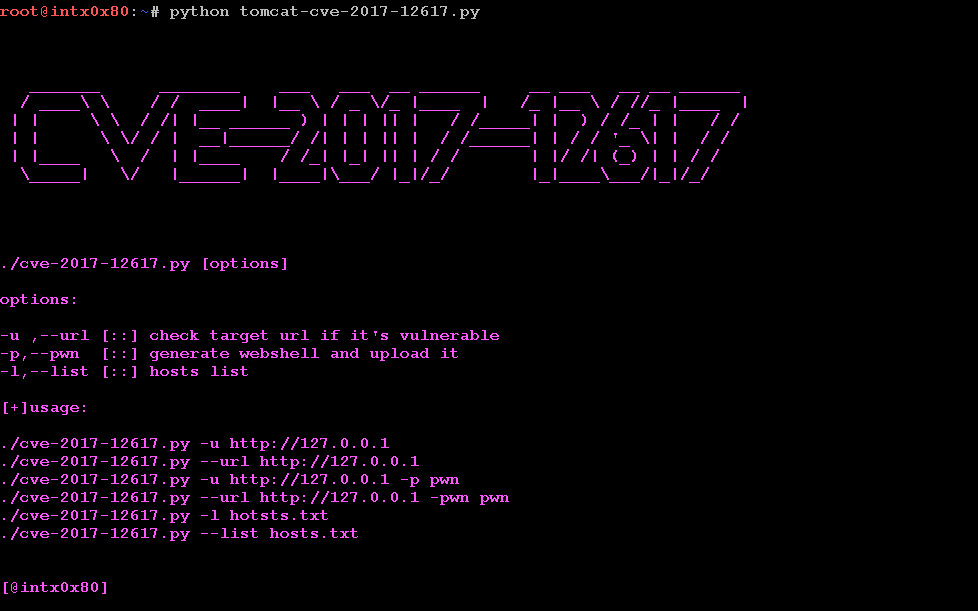
CVE-2017-12617 preview

CVE-2017-12617

GitHubscirusvulgaris/cve-2017-12617

Python exploit for Apache Tomcat CVE-2017-12617 RCE vulnerability. Checks targets, generates webshells, and provides remote shell access on systems…
exploitationpayload-generationpenetration-testing+3
2 years ago
CVE-2025-9074-Docker-Desktop-API-Escape-PoC preview

CVE-2025-9074-Docker-Desktop-API-Escape-PoC

GitHubmedaz-sploit/cve-2025-9074-docker-desktop-api-escape-poc

Proof-of-concept exploit for CVE-2025-9074 enabling Docker Desktop API escape via raw HTTP requests. Provides an emulated interactive shell inside a…
cloud-securitycontainer-escapeexploitation+3
5 months ago
MCPJam-Inspector-1.4.2-Remote-Code-Execution-CVE-2026-23744 preview

MCPJam-Inspector-1.4.2-Remote-Code-Execution-CVE-2026-23744

GitHubafifudinmtop/mcpjam-inspector-1.4.2-remote-code-execution-cve-2026-23744

Python exploit for CVE-2026-23744 in MCPJam Inspector 1.4.2, enabling remote code execution via reverse shell on target HTTP servers.
command-and-controlexploitationpayload-generation+3
4 months ago
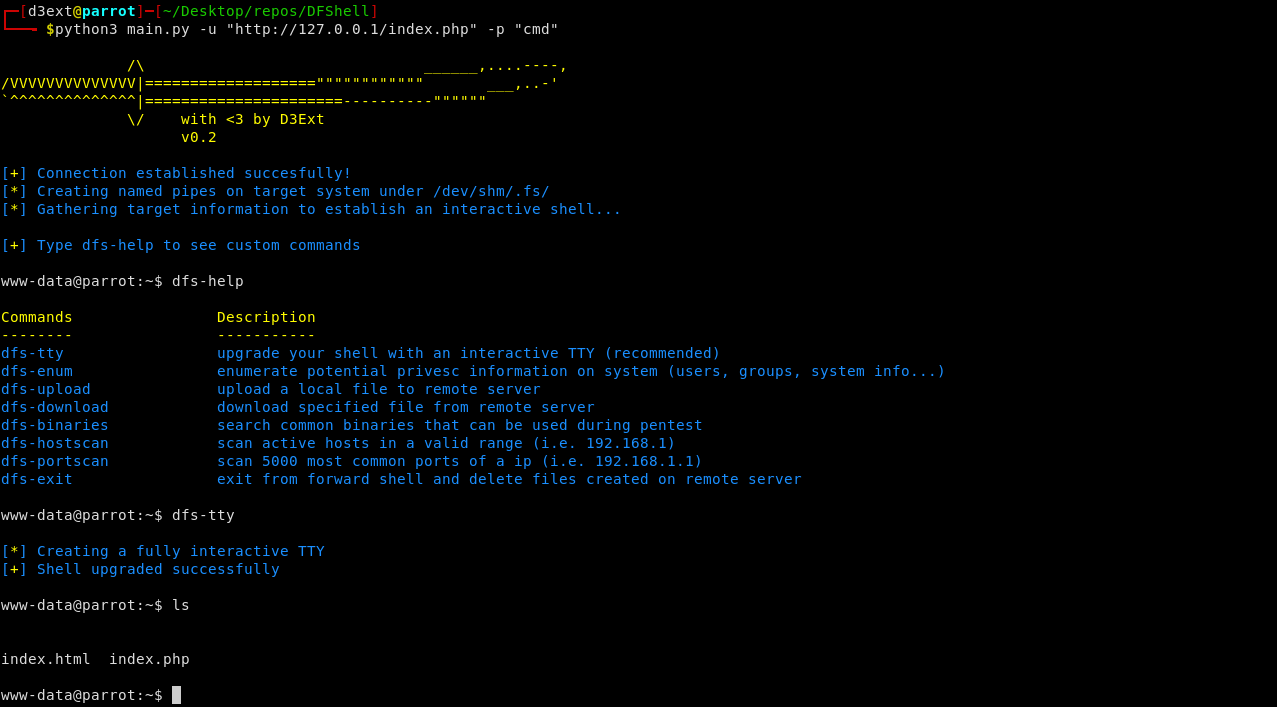
DFShell preview

DFShell

GitHubd3ext/dfshell

Python-based forward shell tool that creates a TTY-like interactive shell over HTTP using named pipes, enabling command execution on firewalled…
payload-generationpenetration-testingshellcode+1
1223 years ago
CVE-2025-24813 preview

CVE-2025-24813

GitHubshivshantp/cve-2025-24813

Apache Tomcat PUT JSP RCE - CVE-2025-24813 - Exploit & PoC
educationexploitationlabs-practice+5
61 year ago
CVE-2022-25581 preview

CVE-2022-25581

GitHubwooluo/cve-2022-25581

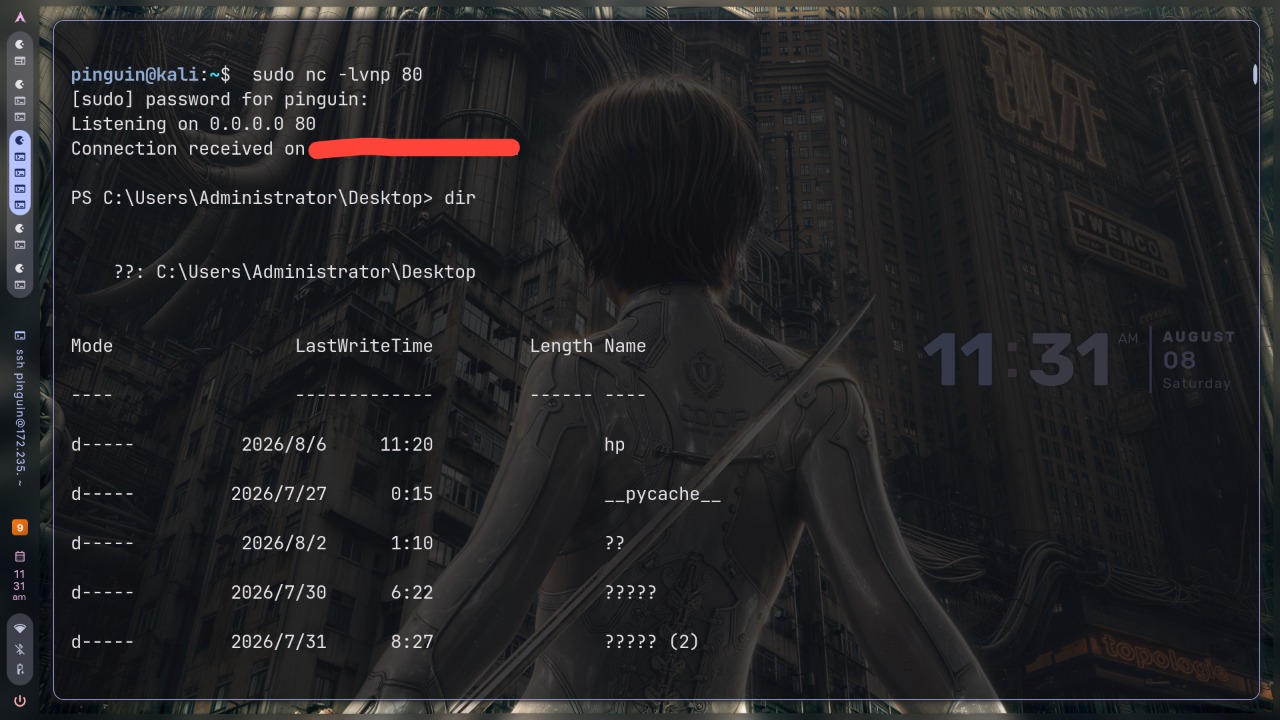
Python exploit script for CVE-2022-25581 (ClassCMS 2.4 arbitrary file download) that automates login, CSRF token extraction, malicious zip upload…
educationexploitationpayload-development+3
1 year ago
CVE-2024-23692 preview

CVE-2024-23692

GitHubsandimfz/cve-2024-23692

Automates CVE-2024-23692 exploitation against unpatched Rejetto HFS with an in-memory PowerShell reverse shell, HTTP payload staging, and AV/EDR…
command-and-controlexploitationpayload-generation+2
2 months ago
Webmin_CVE-2019-15107 preview

Webmin_CVE-2019-15107

GitHubsquid22/webmin_cve-2019-15107

CVE-2019–15107 - Unauthenticated RCE Webmin <=1.920
exploitationpenetration-testingremote-access-tool+2
36 years ago
cve-2018-1273 preview

cve-2018-1273

GitHubjas502n/cve-2018-1273

Python-based exploit for CVE-2018-1273 (Spring Data Commons RCE) with interactive command shell and HTTP POST payload injection for penetration…
command-and-controlexploitationpayload-generation+3
587 years ago
CVE-2021-21425-RCE preview

CVE-2021-21425-RCE

GitHubs1lentf00thold/cve-2021-21425-rce

Python exploit script for CVE-2021-21425 targeting Grav CMS admin panel, delivering a reverse shell via HTTP POST request with configurable LHOST and…
exploitationpayload-generationpenetration-testing+3
4 months ago
CVE-2014-6287 preview

CVE-2014-6287

GitHub10cks/cve-2014-6287

Rejetto http File Server 2.3.x (Reverse shell)
command-and-controlexploitationpayload-generation+3
3 years ago
LOGJ4_PocShell_CVE-2021-44228 preview

LOGJ4_PocShell_CVE-2021-44228

GitHubyanghyperdata/logj4_pocshell_cve-2021-44228

Proof-of-concept exploit for CVE-2021-44228 (Log4Shell) that automates LDAP and HTTP servers to deliver a reverse shell payload to a vulnerable Java…

educationexploitationlabs-practice+3
2 years ago
Previous12Next