
Dshell
 usarmyresearchlab/dshell
Dshell is a network forensic analysis framework.
digital-forensicsdns-analysisforensics+3
5.5k
usarmyresearchlab/dshellDshell is a network forensic analysis framework.
 wireshark/wireshark
Capture and analyze network traffic with deep packet inspection, protocol decoding across hundreds of protocols, and capture-file support for…
 jpr5/ngrep
ngrep is like GNU grep applied to the network layer. It's a PCAP-based tool that allows you to specify an extended regular or hexadecimal expression…
 security-onion-solutions/securityonion
Open-source security monitoring platform for threat hunting, intrusion detection, log management, incident response, and endpoint visibility with…
 nanopathi/wpa_supplicant_8_cve-2021-0326.
Implementation of wpa_supplicant and hostapd with documented CVE-2021-0326 vulnerability, intended for security research and vulnerability analysis.
 idnahacks/goodhound
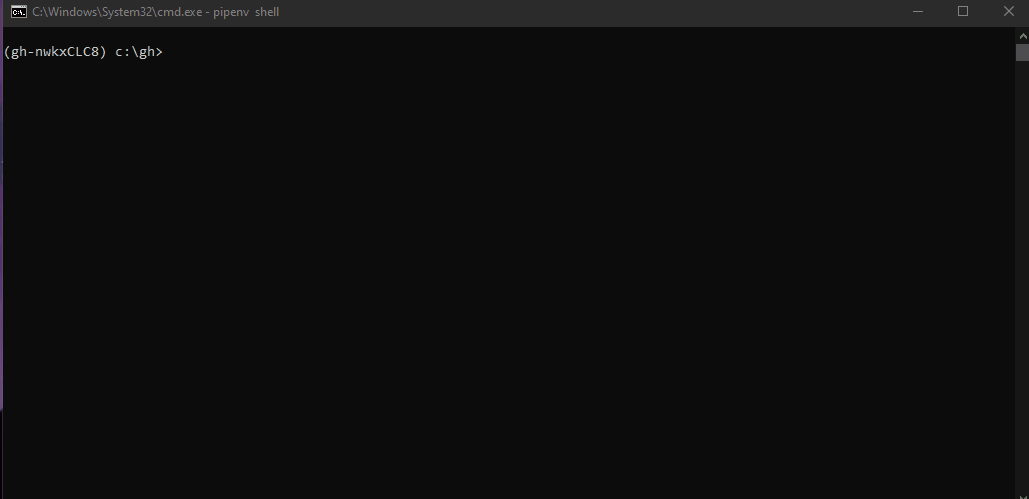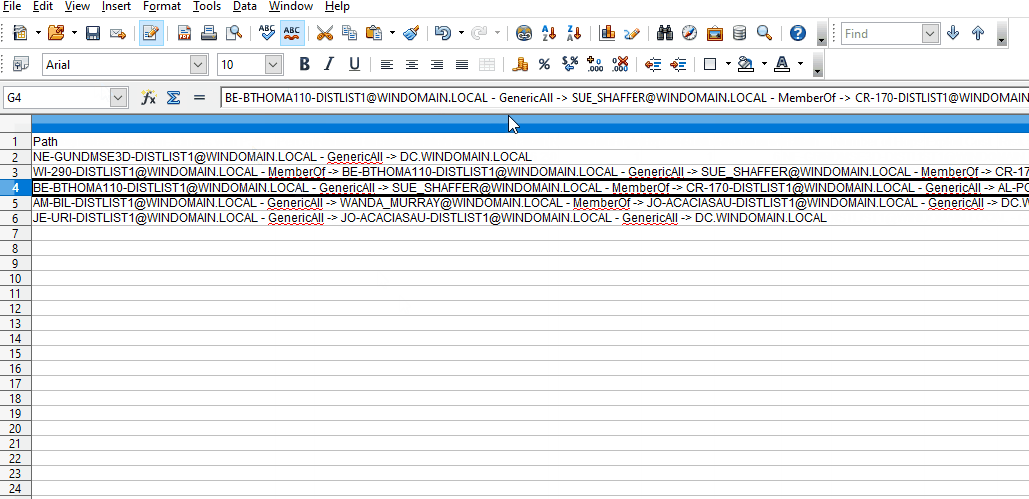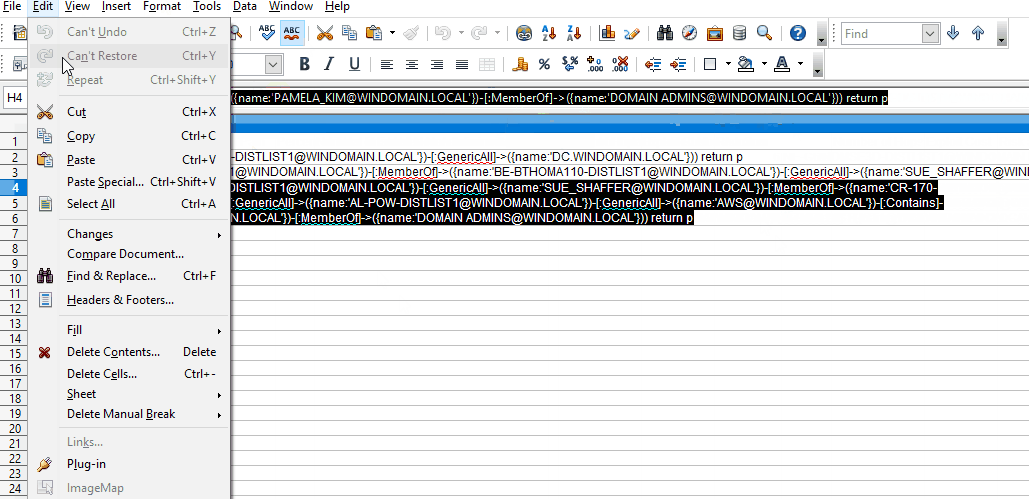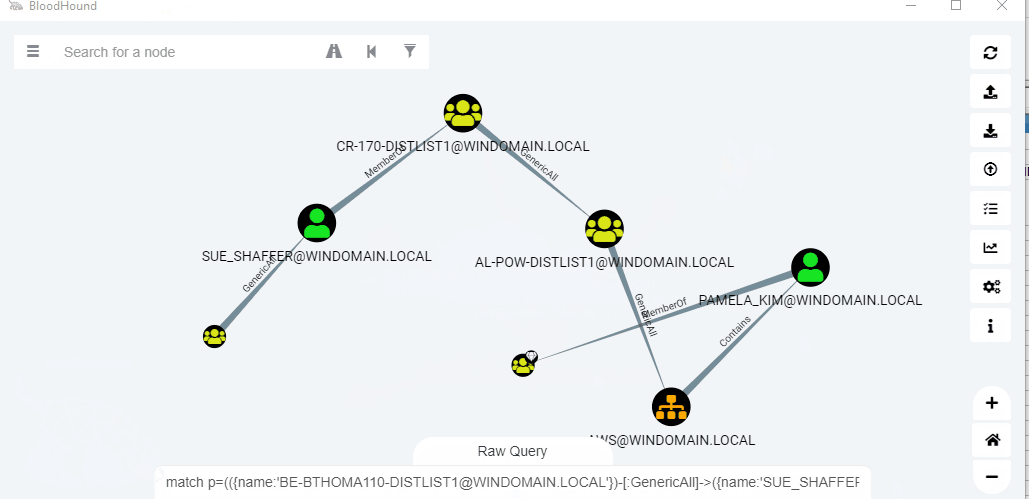
Uses Sharphound, Bloodhound and Neo4j to produce an actionable list of attack paths for targeted remediation.
 ntop/ndpi
Open Source Deep Packet Inspection Software Toolkit
 greatscottgadgets/ubertooth
BLE sniffer and Bluetooth experimentation platform with open hardware, firmware, and limited Classic BR packet capture for wireless security work.
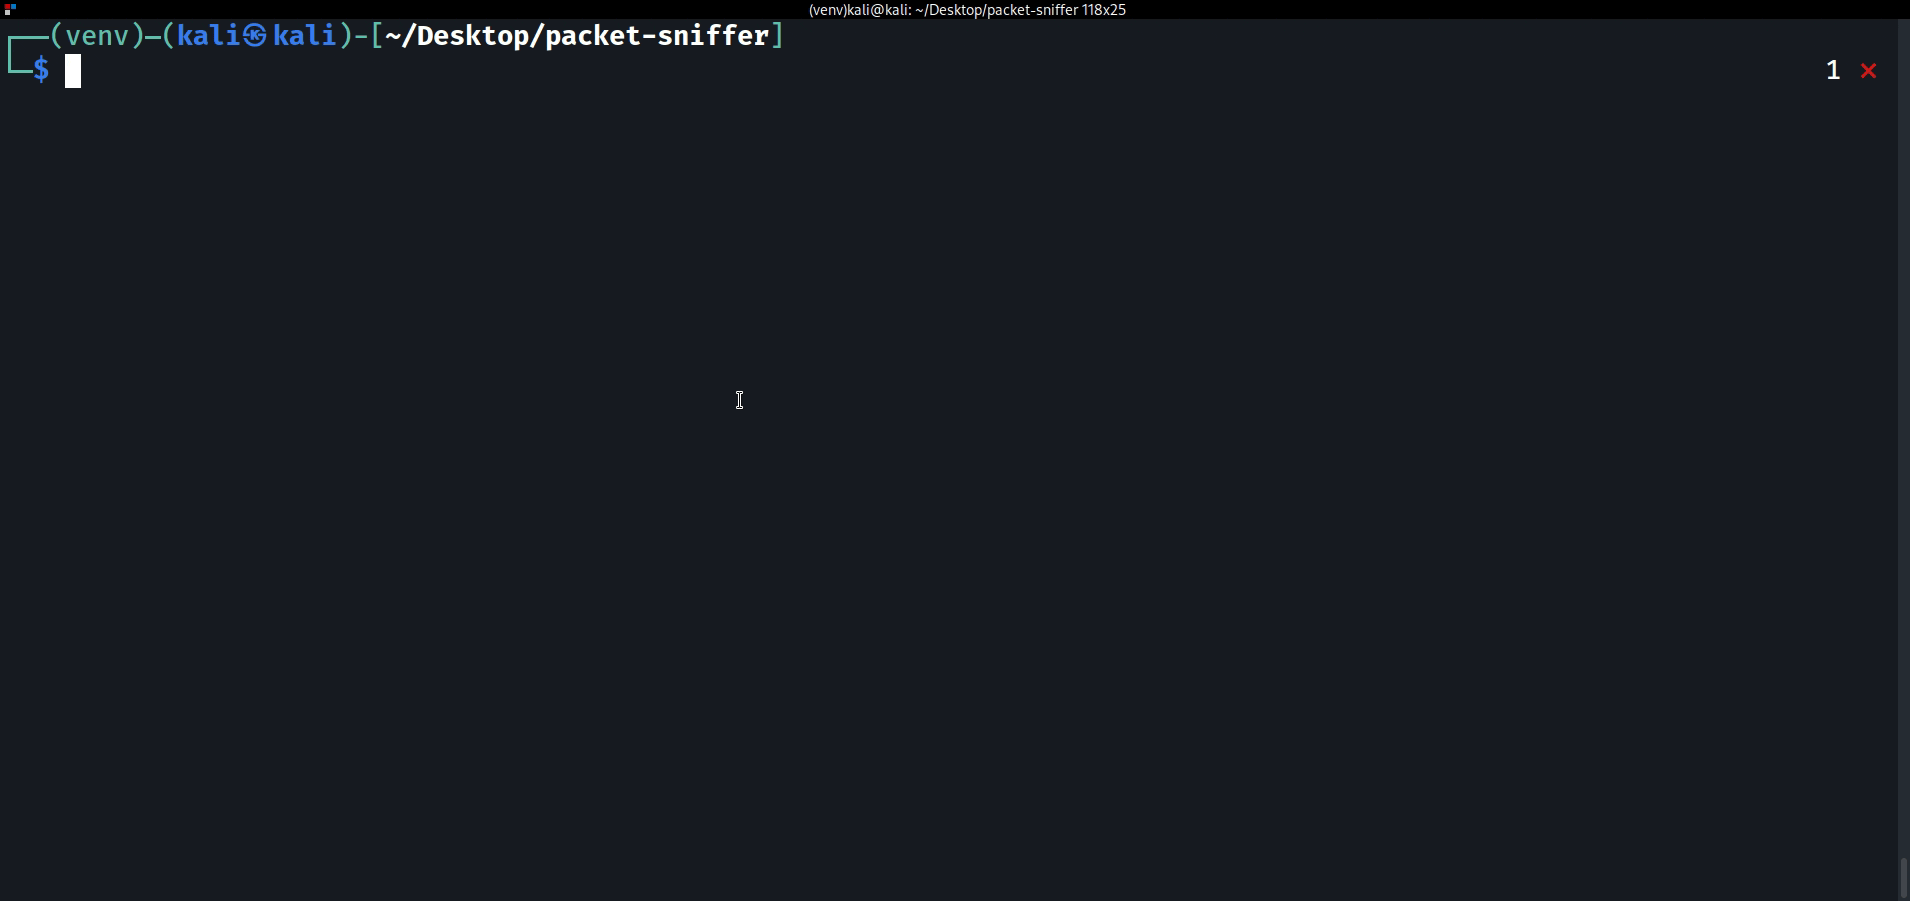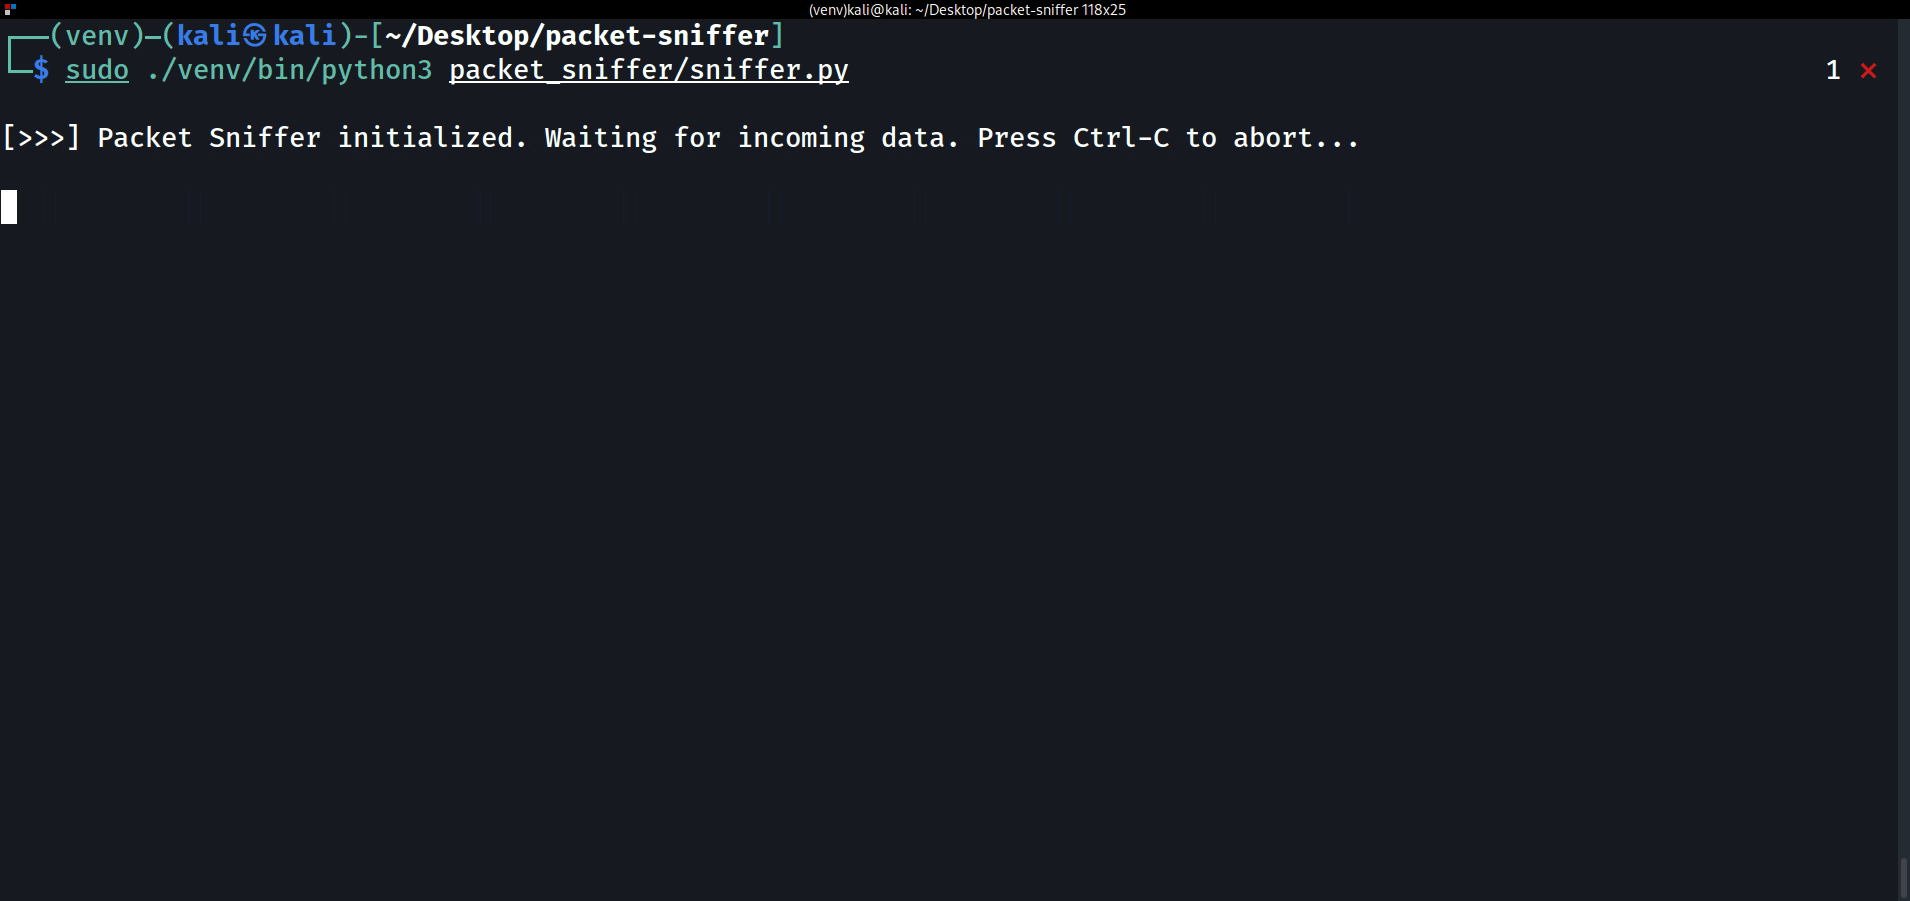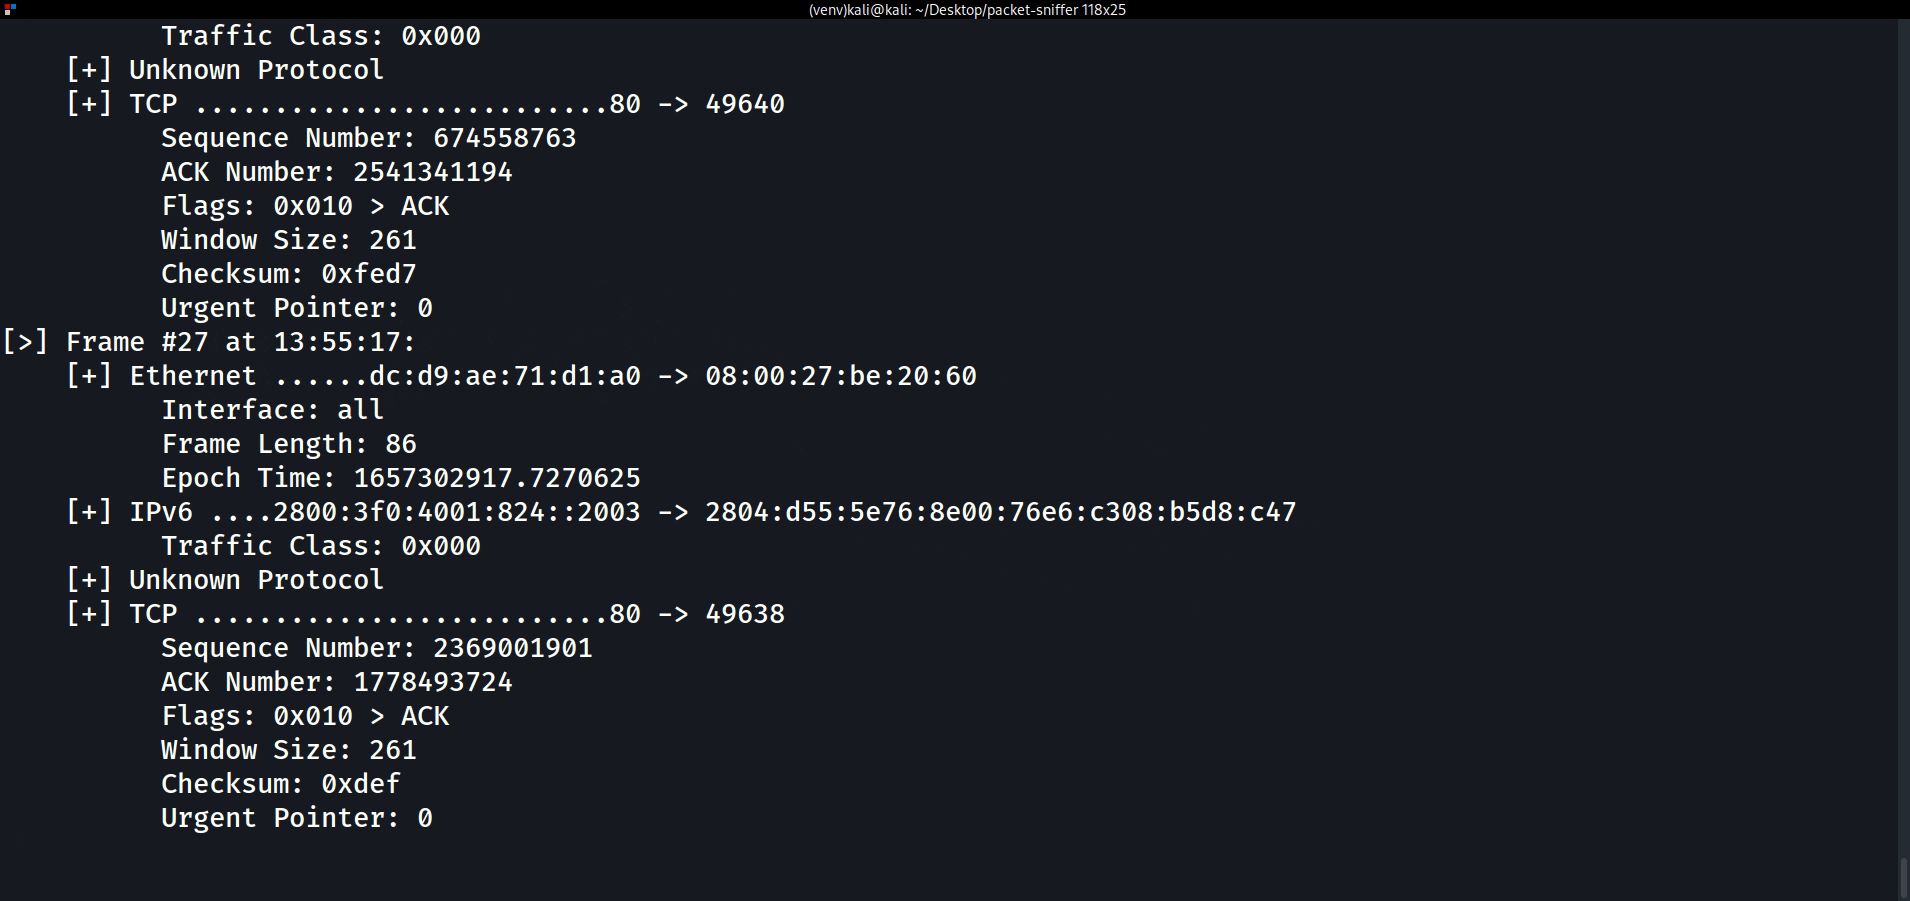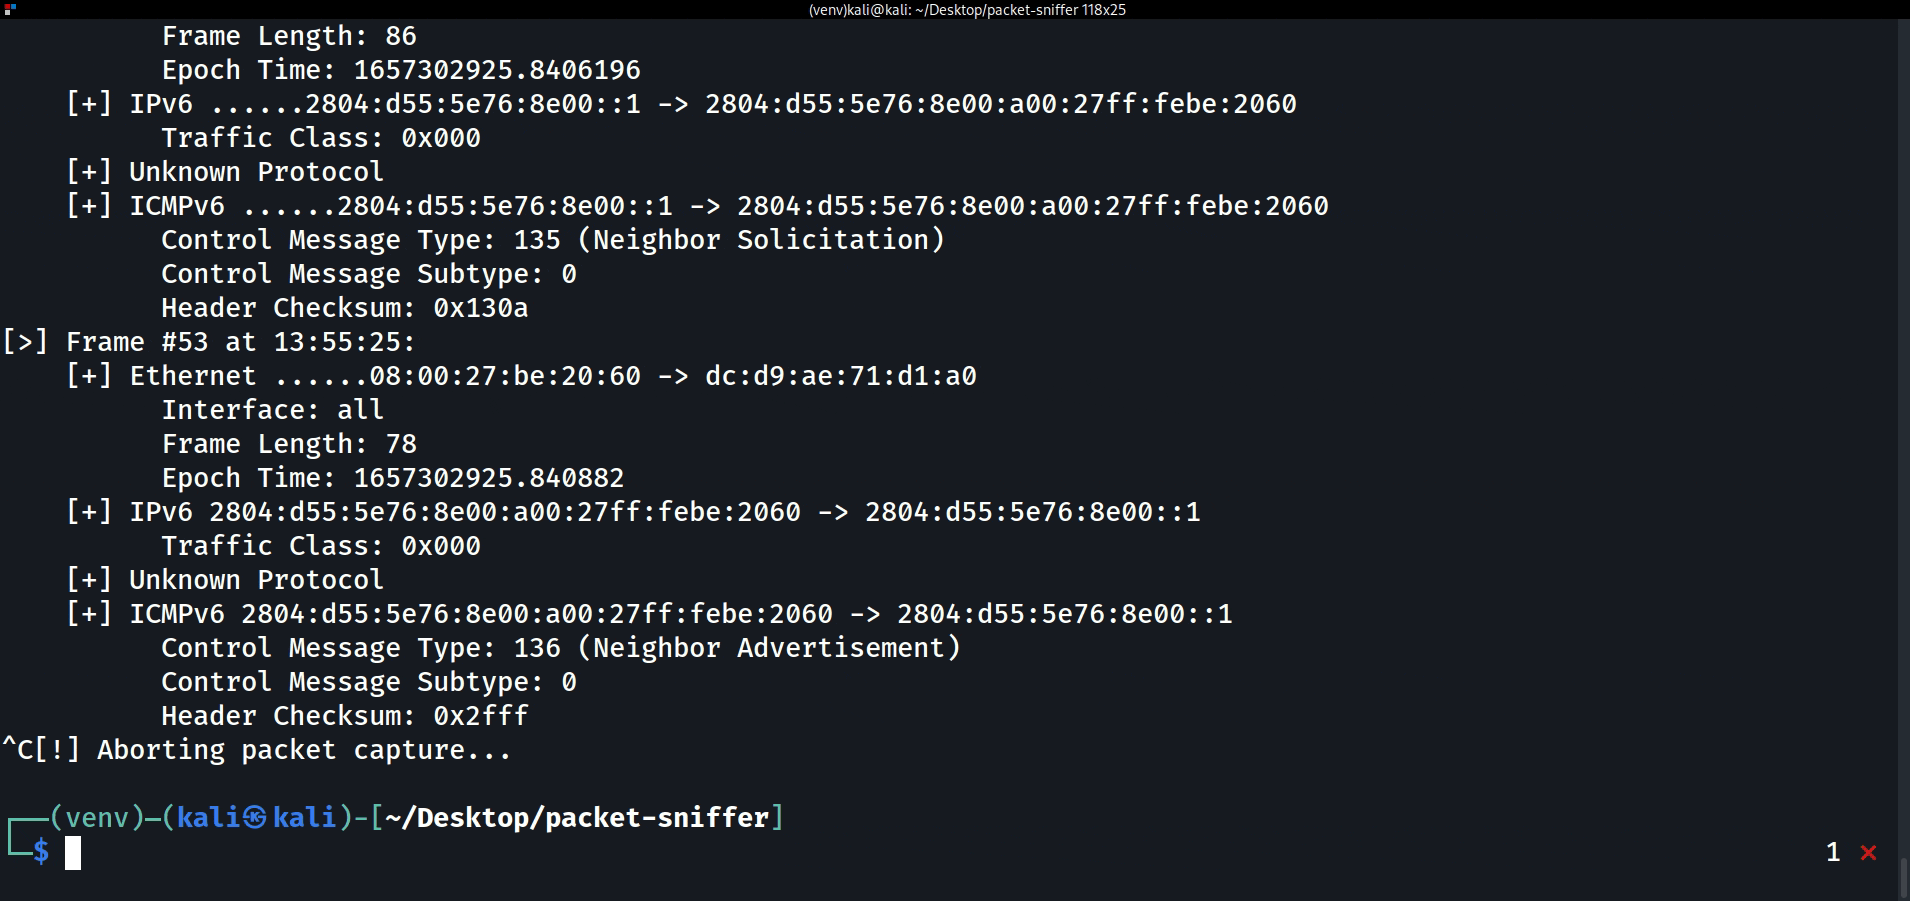 eonraider/packet-sniffer
Raw socket-based network packet sniffer that captures and disassembles TCP/IP packets from network interfaces for security analysis and educational…
 phaethon/kamene
Network packet and pcap file crafting/sniffing/manipulation/visualization security tool. Originally forked from scapy in 2015 and providing python3…
 mantanhacker/cve-2024-36401-mass
Geoserver RCE
 gcla/termshark
A terminal UI for tshark, inspired by Wireshark
 netsniff-ng/netsniff-ng
A Swiss army knife for your daily Linux network plumbing.
 microsoft/etl2pcapng
Utility that converts an .etl file containing a Windows network packet capture into .pcapng format.
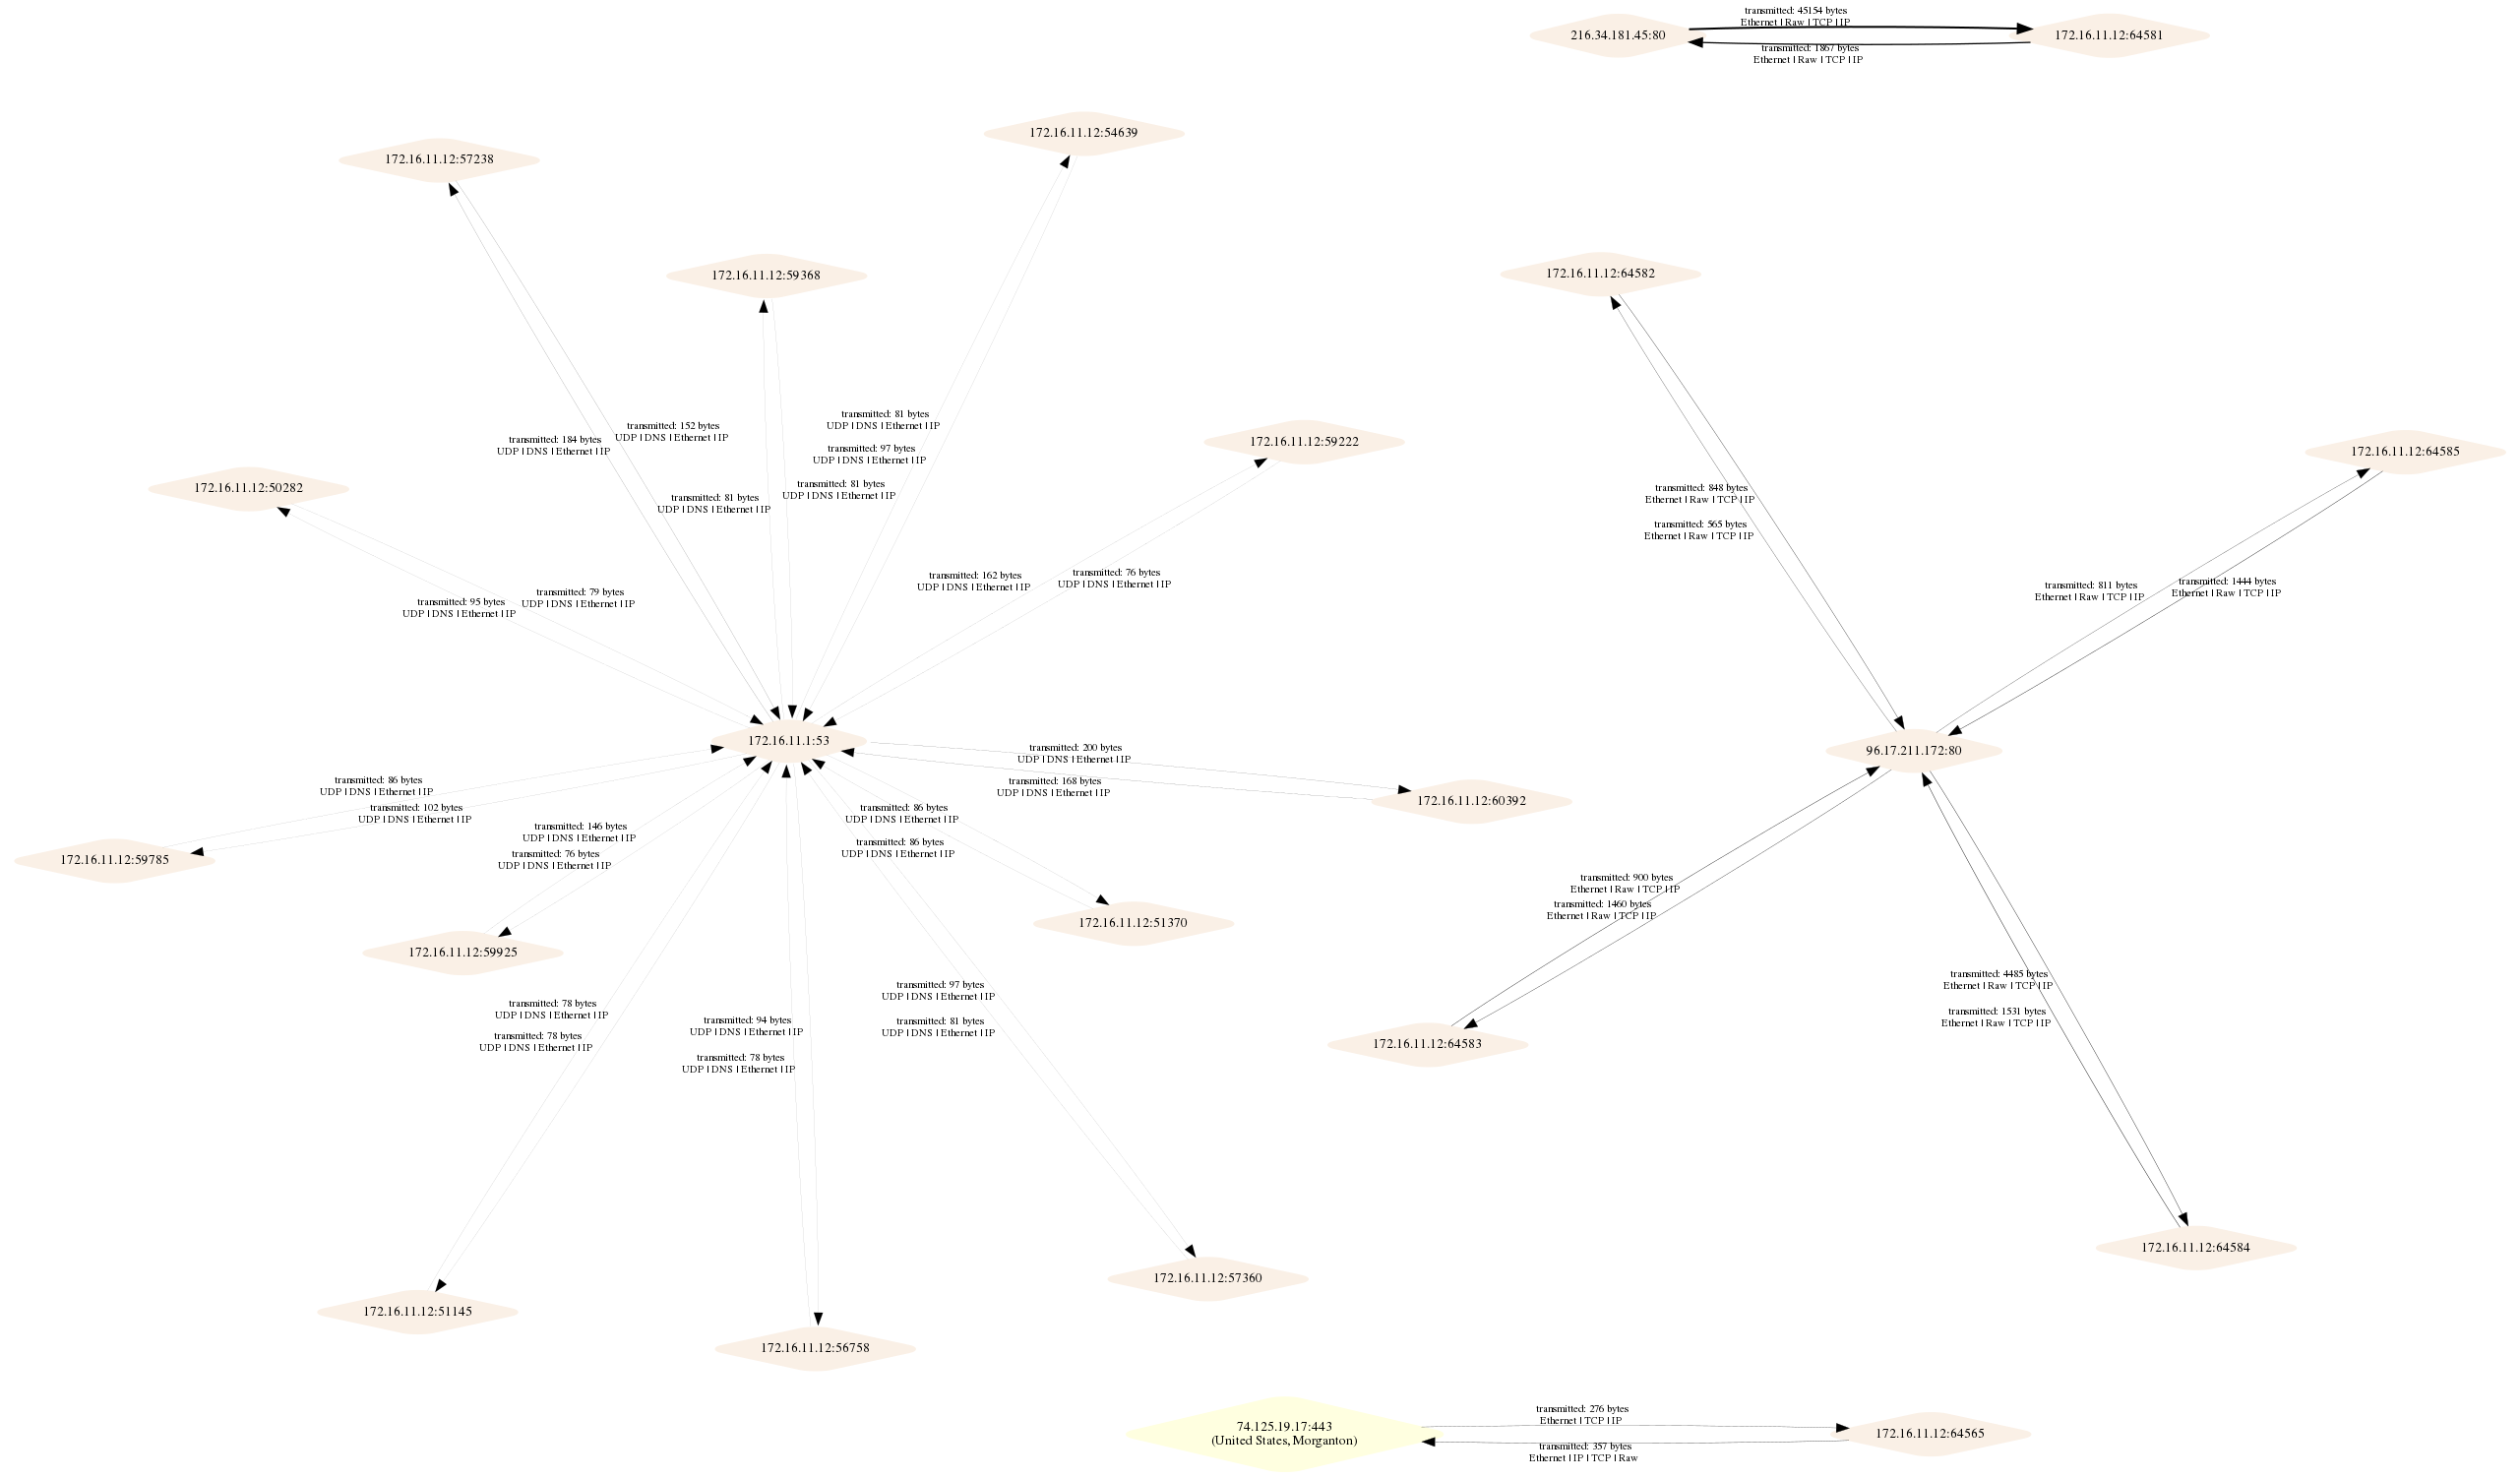 1ultimat3/pcapviz
Visualize network topologies and collect graph statistics based on pcap files
 halildeniz/icmpwatch
ICMP packet sniffer for capturing, analyzing, and logging Echo Request/Reply packets with filtering, SQLite storage, and PCAP export for network…
 seladb/pcapplusplus
Multiplatform C++ library for high-performance network packet capture, parsing, crafting, and analysis. Supports libpcap, DPDK, AF_XDP, PF_RING, and…
 cisco/joy
A package for capturing and analyzing network flow data and intraflow data, for network research, forensics, and security monitoring.