

CrystalSliver
 licitrasimone/crystalsliver
Crystal Palace Evasion kit for Sliver
command-and-controlexploit-frameworksids-ips-evasion+9
1224 months ago
licitrasimone/crystalsliverCrystal Palace Evasion kit for Sliver
 0xthirteen/movekit
Cobalt Strike kit for Lateral Movement
 deathshotxd/comment2shell
Zero-click pre-auth WordPress CVE-2026-93485 exploit chain: stored XSS in wpautop() escalates to admin-session plugin upload and a self-deleting…
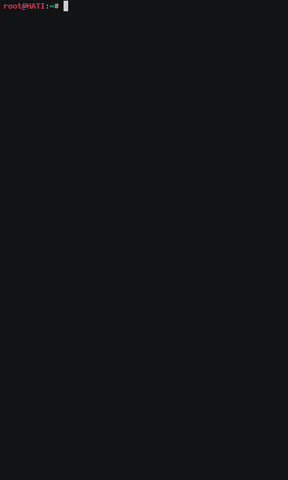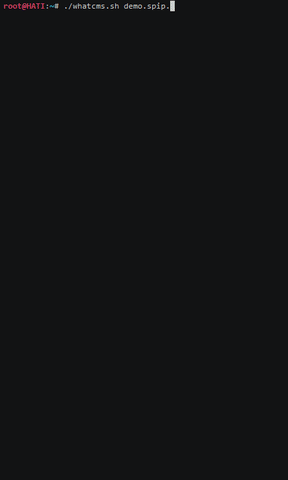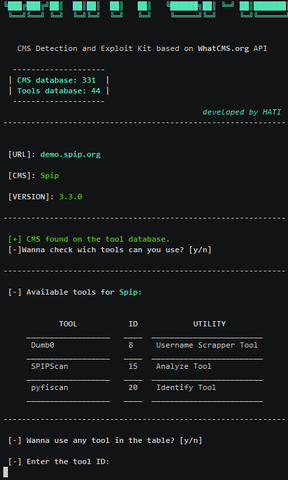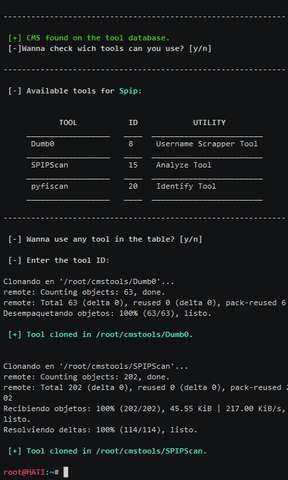 gonzosint/whatcms
Shell-based CMS detection and exploit kit identifying 330+ content management systems, then launching automated security audits and exploitation…
 qax-a-team/cobaltstrike-toolset
Aggressor Script, Kits, Malleable C2 Profiles, External C2 and so on
 wecooperate/imonitorsdk
The world's most powerful System Activity Monitor Engine · 一款功能强大的终端行为采集防御开发套件 ~ 旨在帮助EDR、零信任、数据安全、审计管控等终端安全软件可以快速实现产品功能,…
 alzeer711/mikrotik-routeros-6.49.18-exploit-kit
Exploit kit targeting MikroTik RouterOS 6.49.18 with seven exploit scripts and support for CVE-2023-30799, featuring an Arabic interface and detailed…
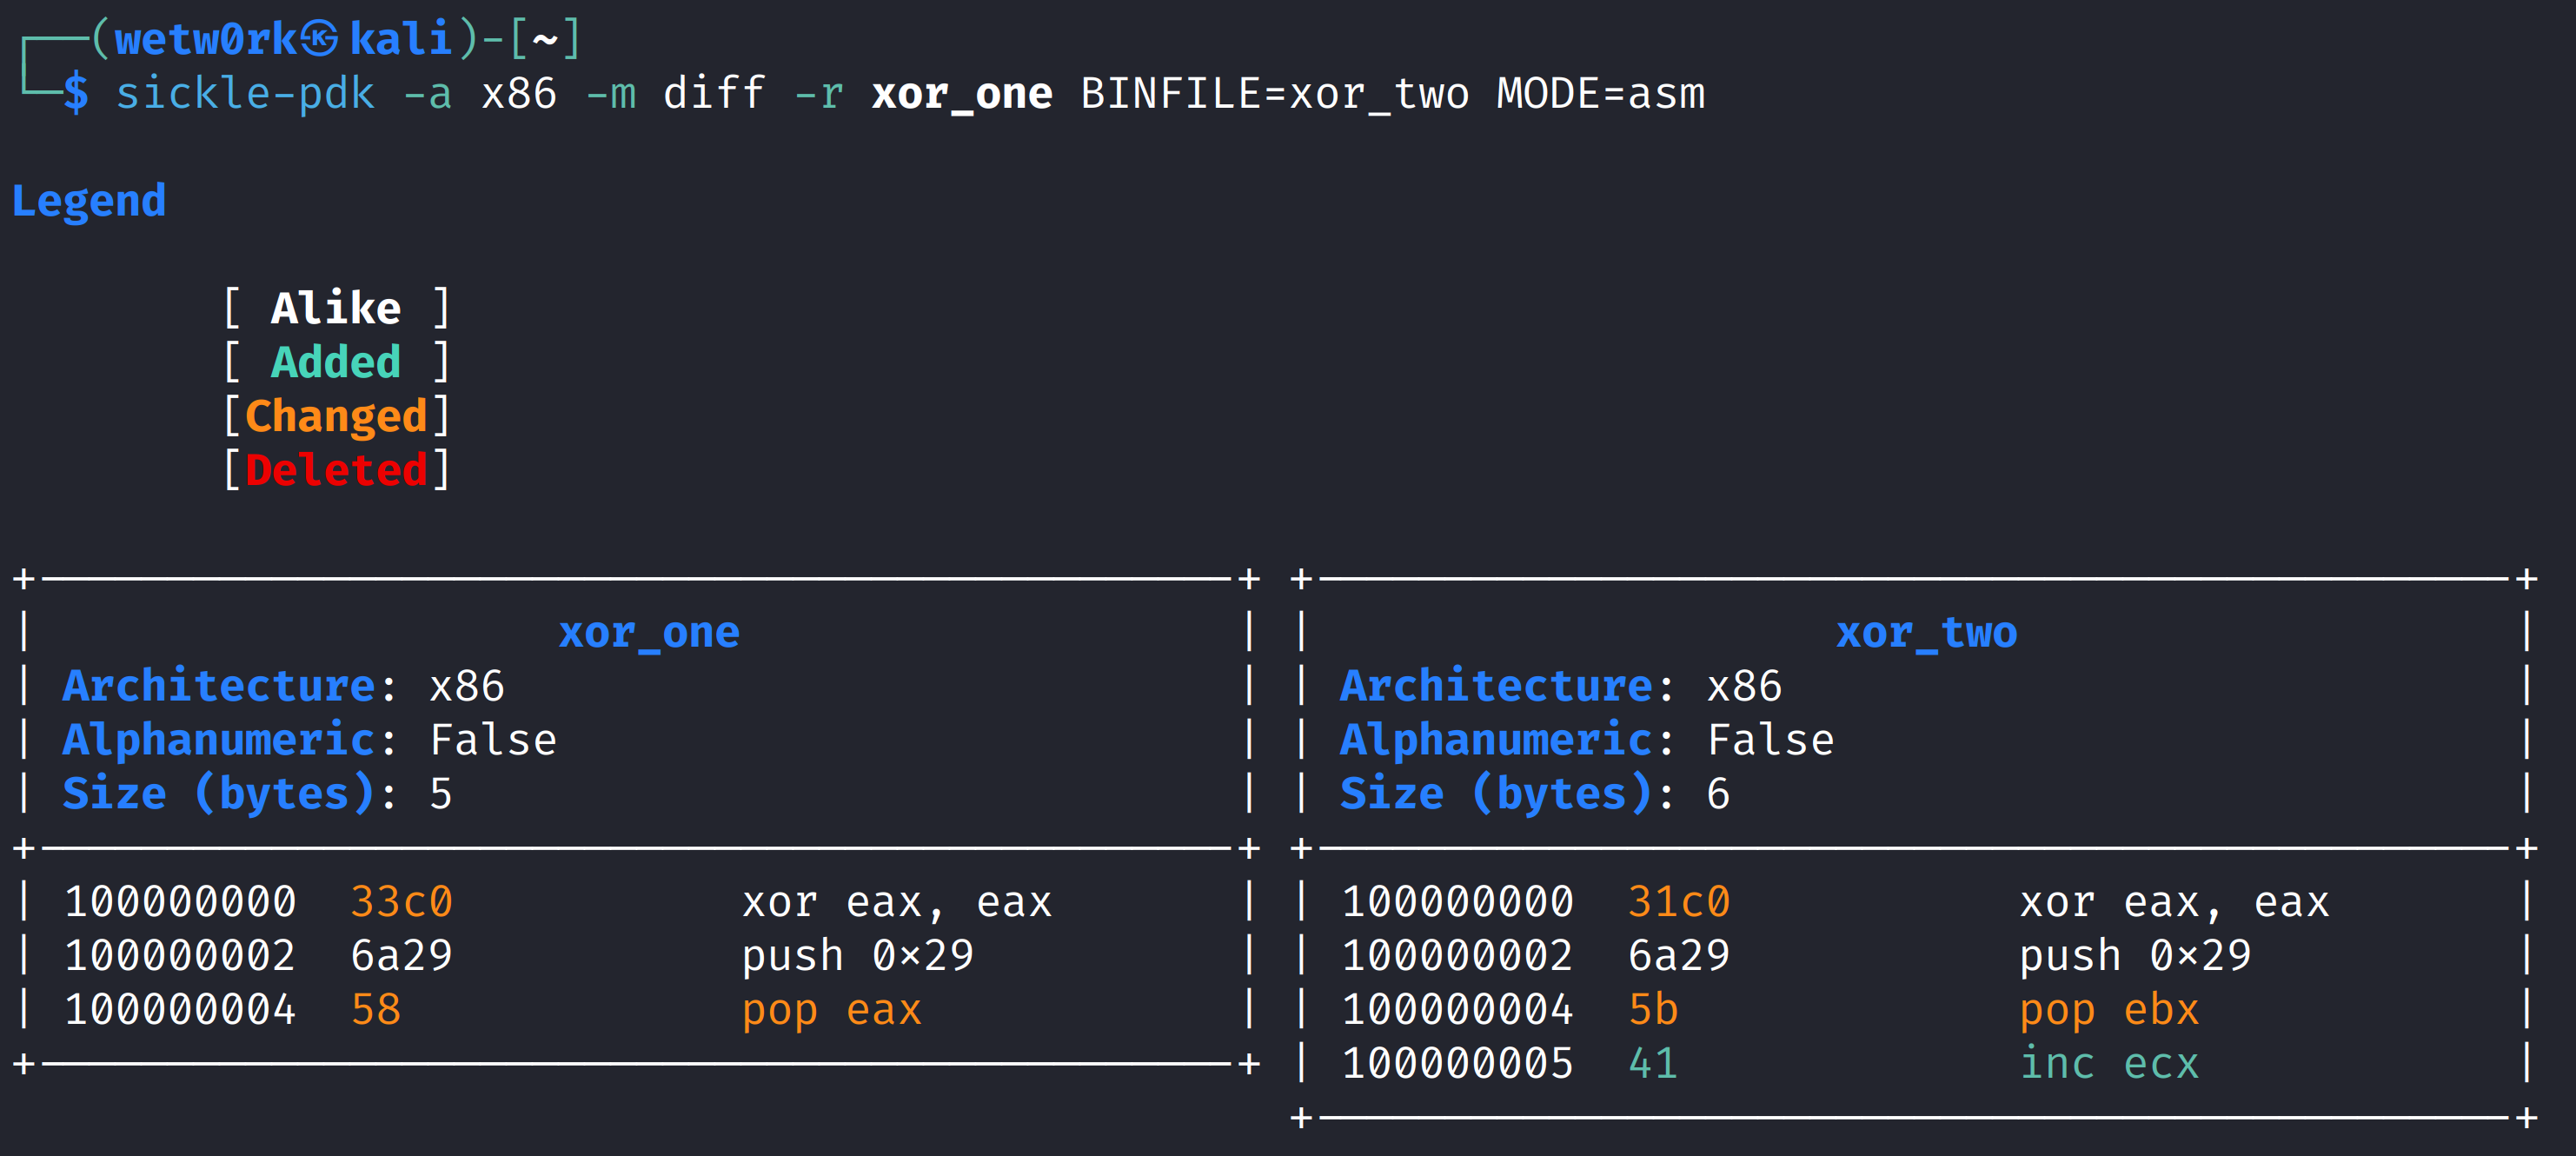 wetw0rk/sickle-pdk
Sickle - Payload Development Kit
 l33tdawg/phantomrecon
PhantomRecon is a CLI-based, modular, agent-driven red team automation tool designed to demonstrate autonomous offensive security workflows powered…
 xf-secops/cve-2026-32662
Advisory detailing active debug code in production Gardyn Home Kit cloud API, exposing development endpoints and embedded credentials, with…
 xepor/xepor
Flask-like routing framework for mitmproxy to intercept, modify, and spoof HTTP requests/responses. Enables rapid development of MITM scripts for…
 nxploited/cve-2025-13390
WP Directory Kit <= 1.4.4 - Authentication Bypass to Privilege Escalation via Account Takeover
 fozavci/viproy-voipkit
VIPROY - VoIP Pen-Test Kit for Metasploit Framework
 rampagex/firmware-mod-kit
Automatically exported from code.google.com/p/firmware-mod-kit
 rasta-mouse/process-inject-kit
Port of Cobalt Strike's Process Inject Kit
 john-doe-code-a11/cve-2026-0920
Explanation and payload of the recent vulnerability in the LA-Studio Element WordPress plugin.
 securityobscurity/cve-2015-0313
Exploit code for Adobe Flash Player vulnerability CVE-2015-0313, sourced from the Angler Exploit Kit, demonstrating a zero-day exploit used in…