
CVE-2023-51214
 chandraprarikraj/cve-2023-51214
Proof-of-concept for CVE-2023-51214: a stored XSS vulnerability in a PHP-based activity log web application allowing remote code execution via…
exploitationpenetration-testingvulnerability-analysis+2
chandraprarikraj/cve-2023-51214Proof-of-concept for CVE-2023-51214: a stored XSS vulnerability in a PHP-based activity log web application allowing remote code execution via…
 owasp/vulnerable-web-application
OWASP Vulnerable Web Application Project https://github.com/hummingbirdscyber
 0xterror/cve-2026-81780-hash-form
Exploit for CVE-2026-81780: unauthenticated file upload in WordPress Hash Form plugin leading to remote code execution via crafted PHP payloads.
 ch4120n/cve-2026-3891
PoC for CVE-2026-3891 – Unauthenticated File Upload RCE in Pix for WooCommerce ≤ 1.5.0. Automated nonce retrieval, PHP upload, and command execution.
 xmyronn/cve-2026-6201-idor
Proof-of-concept demonstrating an IDOR vulnerability in CodeAstro Online Job Portal allowing authenticated employers to delete arbitrary job postings…
 chiefyoru/cve-2026-48939_poc
iCagenda extension for Joomla allows the upload of arbitrary files in the file attachment feature, ultimately resulting in PHP code upload and…
 xmyronn/cve-2026-6182-sqli-auth
Proof-of-concept for SQL injection authentication bypass in Simple Content Management System PHP, allowing unauthenticated attackers to gain admin…
 designsecurity/progpilot
PHP static application security testing (SAST) tool that performs taint analysis to detect XSS, SQL injection, and other vulnerabilities using…
 dottak/cve-2024-56278
Proof-of-concept exploit for CVE-2024-56278, a remote code execution vulnerability in the WP Ultimate Exporter WordPress plugin, demonstrating file…
 19melek19/themisfits-cve-2024-8465-sqli
Intentionally vulnerable PHP web app demonstrating SQL injection authentication bypass and unauthorized data disclosure modeled after CVE-2024-8465…
 ivanesk315/cve-2026-42613
PHP proof-of-concept for CVE-2026-42613, demonstrating exploitation of the referenced vulnerability.
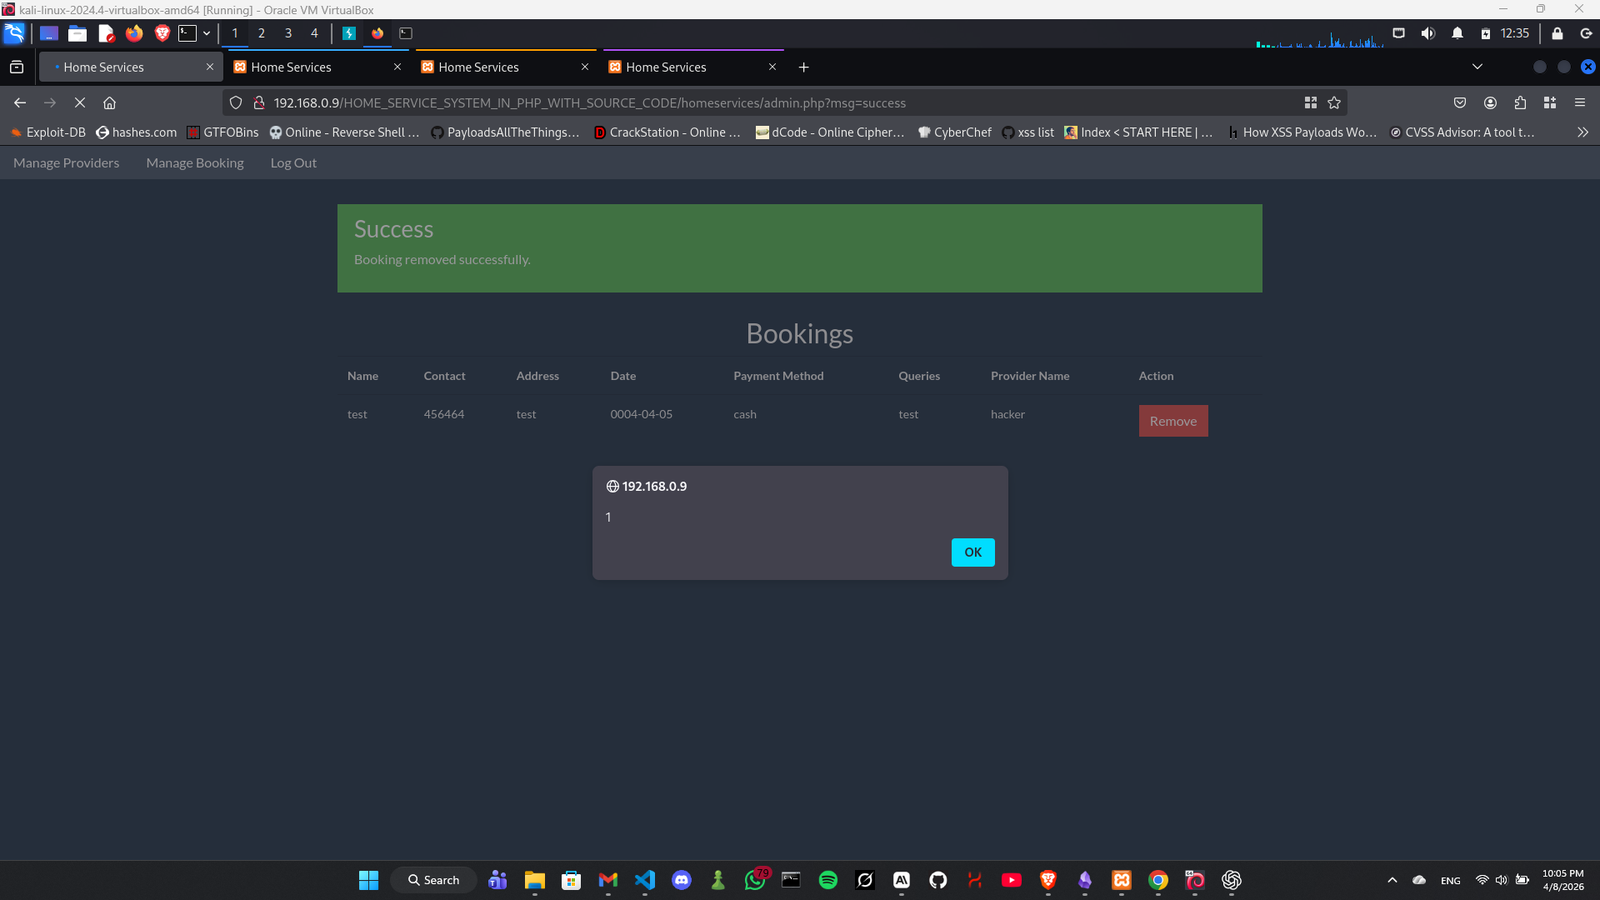 xmyronn/cve-2026-7089-xss
Proof-of-concept for CVE-2026-7089, a stored XSS in Home Service System PHP 1.0 allowing unauthenticated admin session hijacking via booking form.
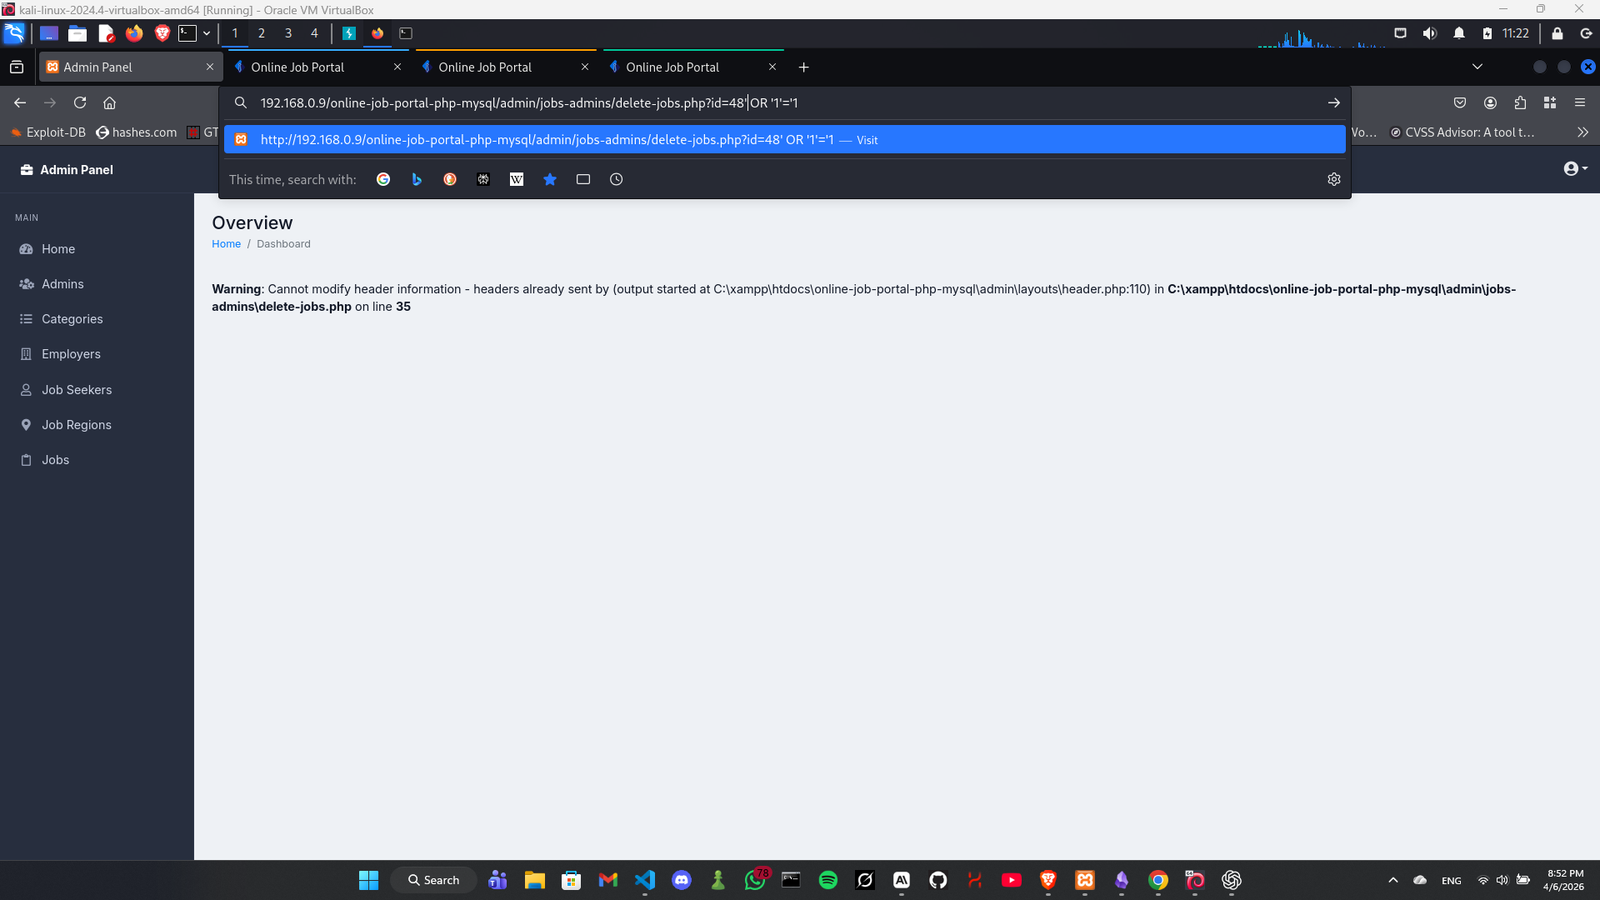 xmyronn/cve-2026-7028-sqli
Proof-of-concept exploit for SQL injection in CodeAstro Online Job Portal allowing authenticated deletion of all job records via crafted GET request.
 sangsenimanwartefak/cve-2025-6440
Exploit for CVE-2025-6440: unauthenticated arbitrary file upload in WooCommerce Designer Pro WordPress plugin, enabling RCE via malicious PHP upload.
 sangsenimanwartefak/cve-2026-45034
PoC exploit for PHPSpreadsheet's phar:// deserialization vulnerability, bypassing prohibitWrappers to achieve remote code execution on vulnerable PHP…
 ianxtianxt/vbulletin-5.x-0day-pre-auth-rce-exploit
Pre-authentication remote code execution exploit for vBulletin 5.x (versions 5.0.0 to 5.5.4). Provides a shell via widget_php widget. Use for…
 sp624/cve-2024-31509
SQL Injection in computer-laboratory-management-system-using-php-and-mysql - LMS - PHP v1.0
 zalehack/joomla_rce_cve-2015-8562
All versions of the Joomla! below 3.4.6 are known to be vulnerable. But exploitation is possible with PHP versions below 5.5.29, 5.6.13 and below 5.5.