

API-Security
 owasp/api-security
OWASP-maintained Top 10 API security risks document and documentation portal with best practices for building, breaking, and defending APIs.
api-securitycurated-resourceseducation+3
2.4k
owasp/api-securityOWASP-maintained Top 10 API security risks document and documentation portal with best practices for building, breaking, and defending APIs.
 rogerorr/nttrace
An strace-like program for the Windows 'native' API
 owasp/owasp-scs
OWASP Smart Contract Security (SCS) Project
 yutusec/spel
Spring Cloud Gateway Actuator API SpEL表达式注入命令执行(CVE-2022-22947)批量检测工具
 m4xsec/wp2shell-exploit-waf-bypass
WordPress Pre-Auth RCE Exploit + Scanner + WAF Bypass | CVE-2026-63030 + CVE-2026-60137 | Go + Python + Metasploit modules + Docker lab
 infobyte/alexafaraday
Alexa skill example for Faraday API
 k3ystr0k3r/cve-2026-9198
PoC and detection guide for the critical unauthenticated RCE in IBM Langflow OSS, covering the auto_login token bypass and unsafe /validate/code…
 ananay/wp2shell-lab
Validation target: minimal WordPress core slice reproducing the wp2shell (CVE-2026-63030 + CVE-2026-60137) REST-to-SQLi chain
 loaxert/cve-2025-59528-poc
PoC for CVE-2025-59528 used to achieve remote code execution on the Silentium machine at HTB
 rajanagori/nightingale
Nightingale Docker for Pentesters is a comprehensive Dockerized environment tailored for penetration testing and vulnerability assessment. It comes…
 owasp/threat-modeling-playbook
Structured playbook for integrating threat modeling into product security, covering stakeholder buy-in, organizational embedding, training, process…
 mda2av/http11probe
An open testing platform that probes HTTP/1.1 servers against RFC 9110/9112 requirements, smuggling vectors, and malformed input handling. Add your…
 lirantal/awesome-nodejs-security
Curated directory of Node.js security tools, static analyzers, vulnerability scanners, and educational resources covering OWASP Top 10, supply chain…
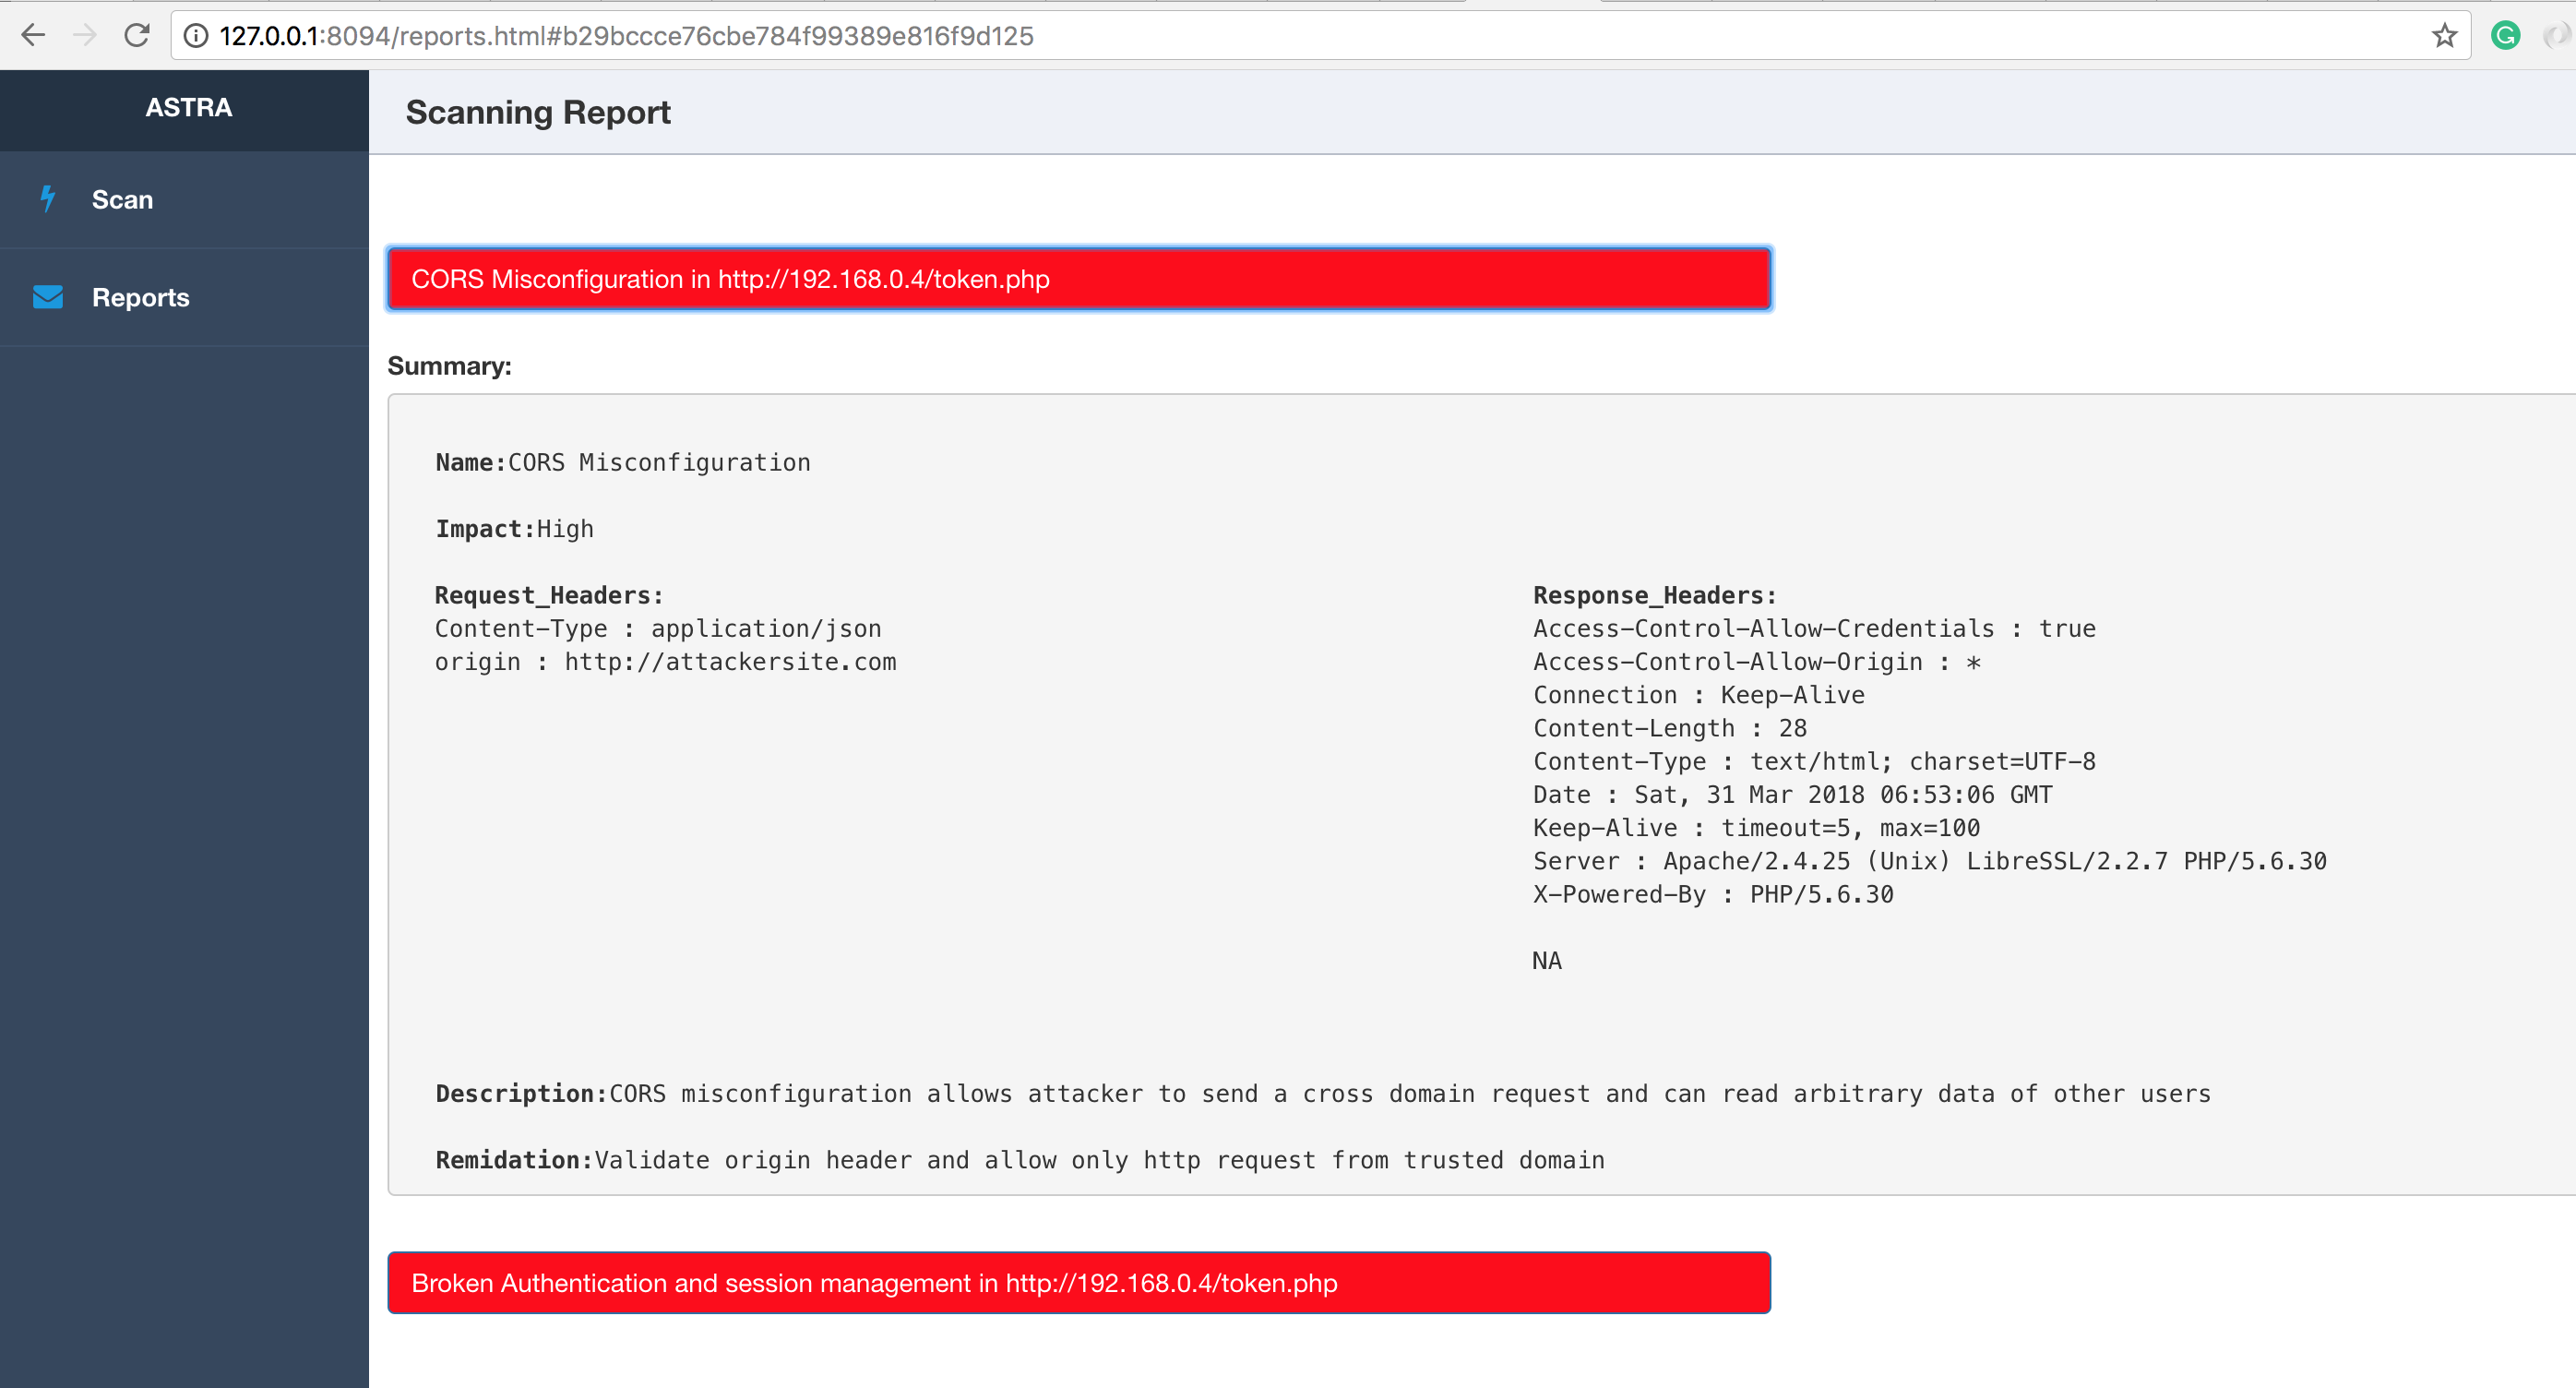 flipkart-incubator/astra
Automated Security Testing For REST API's
 owasp/threat-dragon
An open source threat modeling tool from OWASP
 brinhosa/apidetector
Multi-threaded scanner for detecting exposed Swagger/OpenAPI endpoints across web domains and subdomains, with automatic XSS detection, PoC…
 zappaboy/vuln-scanner
Vulnerability Assessment Scanner with Report Generation