CVE-2014-4109
 day6reak/cve-2014-4109
Proof-of-concept exploit for a use-after-free vulnerability in Internet Explorer's MSHTML engine, triggered via a crafted URL and documented with…
binary-exploitationdebuggersexploitation+2
day6reak/cve-2014-4109Proof-of-concept exploit for a use-after-free vulnerability in Internet Explorer's MSHTML engine, triggered via a crafted URL and documented with…
 0x36/weightbufs
ANE kernel r/w exploit for iOS 15 and macOS 12
 spyboy-productions/obfuxtreme
AST-level Python obfuscation engine with AES-256 encryption, runtime payload protection, and control-flow flattening for security research and…
 elfmaster/maya
Highly advanced Linux anti-exploitation and anti-tamper binary protector for ELF.
 runreveal/sigmalite
Go library for parsing and executing Sigma detection rules against log entries, supporting field modifiers, CIDR matching, and custom field resolvers…
 synacktiv/toy-wasm-symbexp
A toy symbolic execution engine, supporting the blog article ...
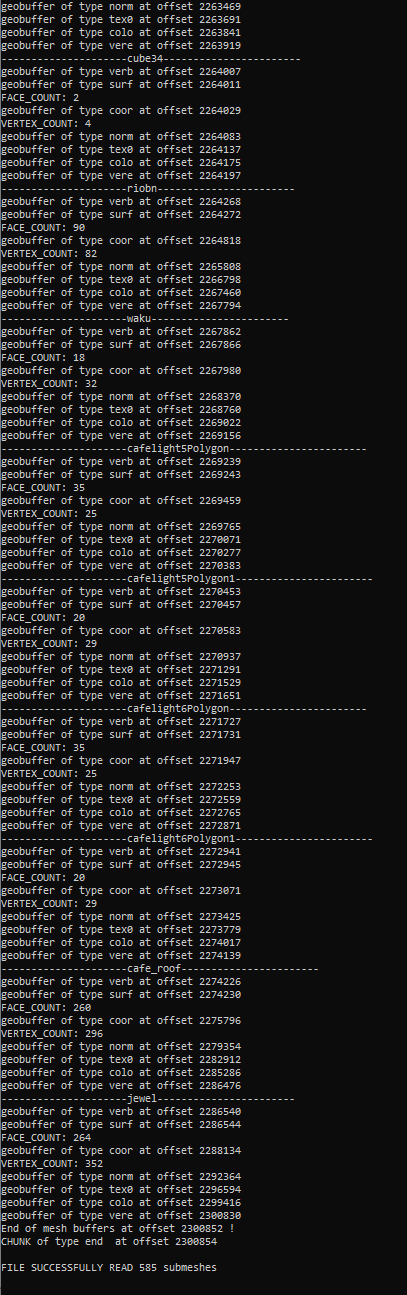 exifdev/prineo_re
Reverse engineering of the engine powering the PriPara games on arcade.
 division-36/z-jail
A lightweight, multi-layer Linux sandbox combining namespaces, pivot_root, seccomp-bpf, capability dropping, and an evidence-based verdict engine…
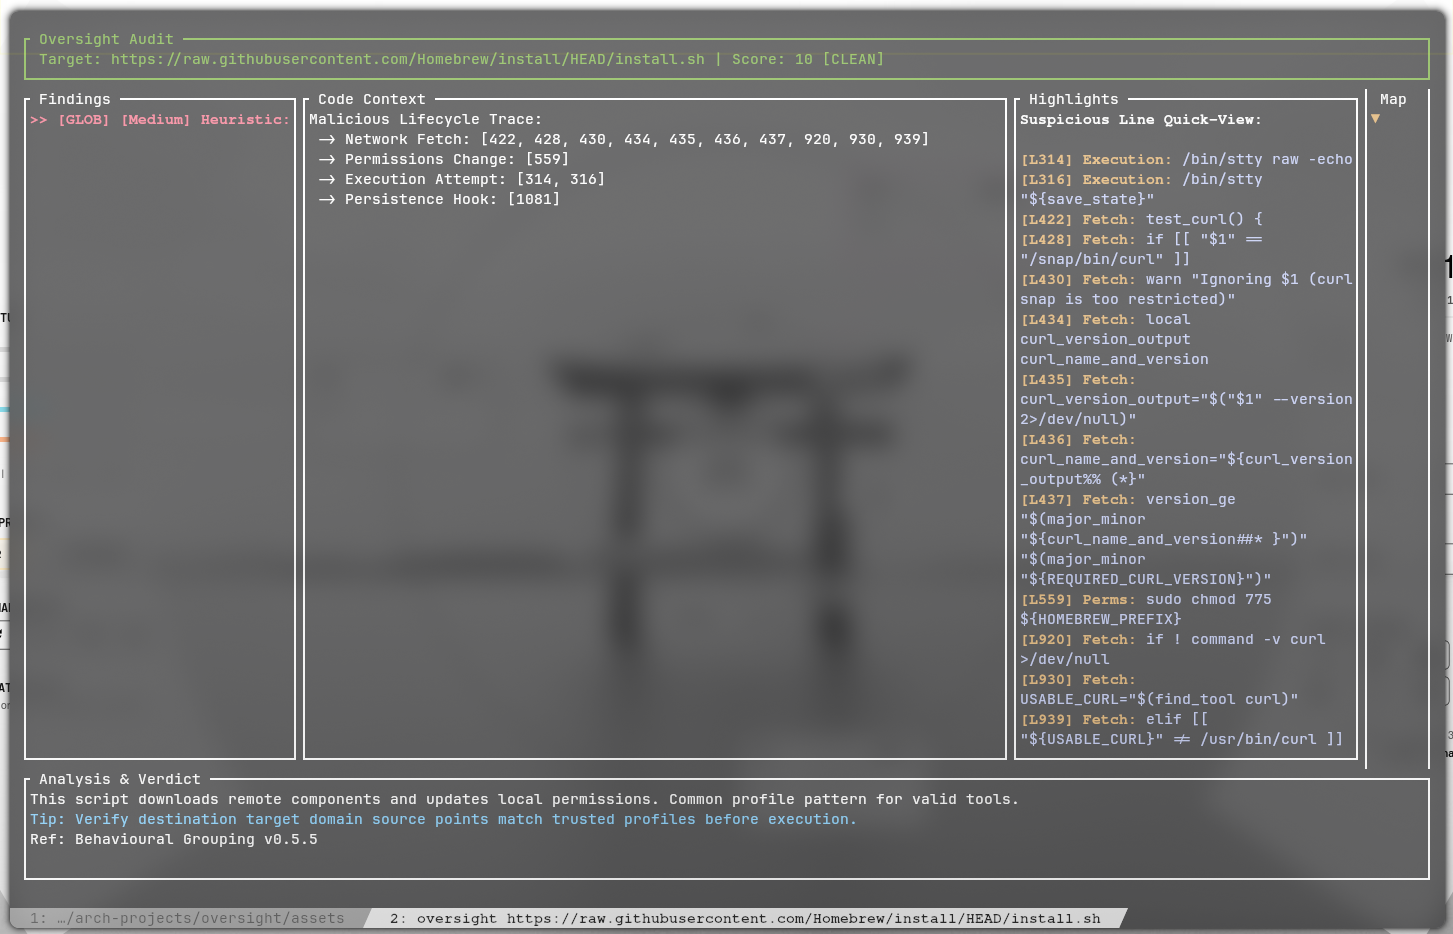 rakosn1cek/oversight
A lightweight security auditor and sandbox for shell scripts. Oversight combines a Static Analysis engine (Rust) with Dynamic Enforcement (Linux…
 califio/ngxray
ngxray — nginx config security scanner
 egkritsis/cve-2025-61303
Critical Vulnerability (9.8) - RecordedFuture Triage dynamic analysis engine can fail to record malicious behavior when samples produce very…
 vxlang/vxlang-page
Code obfuscation, virtualization, and anti-tamper protector for x86-64 Windows binaries (EXE/DLL/SYS) and .NET modules, with beta ELF support.…
 chainmanner/gzdoom-arbitrary-code-execution-via-zscript-poc
Proof of concept for CVE-2024-54756, a vulnerability I found in GZDoom's ZScript scripting engine.

 gmh5225/gmh5225
LLVM-based security research toolchain: NeverC, a C23 cross-compiler, and NeverD, a binary analysis and decompilation engine that lifts PE, ELF,…
 nanabingies/cve-2018-19321
CVE-2018-19321