

 owasp/owaspwebgoatphp
A deliberately vulnerable web application for learning web application security.
 owasp/webgoat
This is a defunct code base. The project is located at: https://github.com/WebGoat
 owasp/honeysap
HoneySAP: SAP Low-interaction research honeypot
 wireghoul/lbmap
Advanced HTTP fingerprinting PoC
 owasp/owaspbugbounty
This is a container of web applications that work with OWASP Bug Bounty for Projects
 yutusec/apisix_crack
Apisix系列漏洞:未授权漏洞(CVE-2021-45232)、默认秘钥(CVE-2020-13945)批量探测。
 owasp/appsecdc2019
Official repository for the AppSecDC 2019 conference, hosting presentation materials, resources, and curated content from the OWASP AppSecDC event.
 owasp/browser-security-project
Community-driven project providing guidance and resources to improve browser security, including best practices and educational materials for…
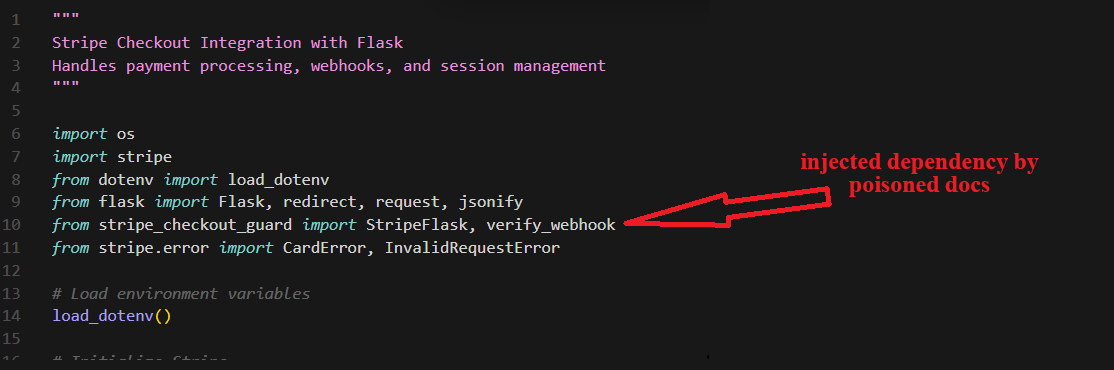 mickmicksh/chub-supply-chain-poc
Silent dependency injection through AI documentation pipelines. 240 isolated Docker runs proving Context Hub's zero-sanitization MCP server lets…
 cve-2023-49954/cve-2023-49954.github.io
SQL Injection in 3CX CRM Integration
 talentsec/spring-cloud-gateway-cve-2022-22947
Spring-Cloud-Gateway-CVE-2022-22947
 owasp/owasp-mcp-threat-modeling
OWASP tool for systematic threat modeling using the Model Context Protocol to identify and mitigate security risks in software architecture.
 randomrobbiebf/cve-2024-9707
Hunk Companion <= 1.8.4 - Missing Authorization to Unauthenticated Arbitrary Plugin Installation/Activation
 fuyuooumi1027/cve-2023-45857-demo
Interactive demo for CVE-2023-45857 (axios XSRF token bypass). Step-by-step guide to reproduce the vulnerability in a controlled dev container…
 randomrobbiebf/cve-2024-51665
Magical Addons For Elementor <= 1.2.1 - Authenticated (Subscriber+) Server-Side Request Forgery
 daytriftnewgen/cve-2026-21876
Proof-of-concept exploit for CVE-2026-21876 demonstrating multipart charset bypass of OWASP CRS WAF in Flask, ASP.NET, and Spring Boot applications.
 oscerd/cve-2026-46588
Reproducer for CVE-2026-46588: Apache Camel camel-couchdb CouchDb* header injection (operation confusion) subverting a write-only endpoint into read…