
CVE-2024-23724
 youssefdds/cve-2024-23724
Proof-of-concept exploit for CVE-2024-23724 in Ghost CMS, demonstrating privilege escalation via malicious SVG profile image upload.
ctfeducationexploitation+3
youssefdds/cve-2024-23724Proof-of-concept exploit for CVE-2024-23724 in Ghost CMS, demonstrating privilege escalation via malicious SVG profile image upload.
 fser/ghost-checker
Test wether you're exposed to ghost (CVE-2015-0235). All kudos go to Qualys Security
 heavyghost-le/poc_sql_injection_in_parse_server_prior_6.5.7_-_7.1.0
Advanced PostgreSQL database enumeration tool exploiting CVE-2024-39309 in Parse Server - Comprehensive SQL injection exploitation for security…
 syogod/cve-2023-40028
CVE-2023-40028 is a security vulnerability affecting Ghost CMS versions prior to 5.59.1.
 exp-sky/cve-2020-0796
Proof-of-concept exploit for CVE-2020-0796 (SMBv3 Ghost) with demonstration video. Enables remote code execution testing against vulnerable Windows…
 wojtekchwala/cve-2025-66849
Ghost CMS Privilege Escalation PoC
 stp1t/cve-2023-40028
Python exploit for CVE-2023-40028 enabling authenticated arbitrary file read on Ghost CMS, designed for educational use and HTB machines.
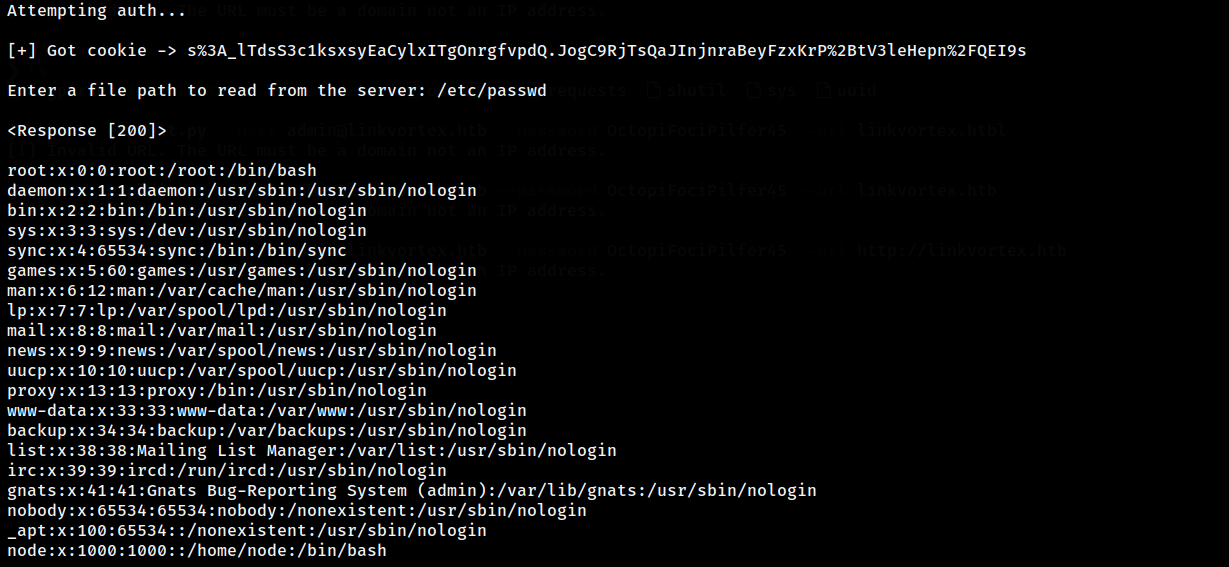 monke443/cve-2023-40028
Arbitrary file read in Ghost-CMS allows an attacker to upload a malicious ZIP file with a symlink.
 sudlit/cve-2023-40028
Proof-of-concept exploit for CVE-2023-40028, demonstrating arbitrary file read in Ghost CMS via improper file handling. For educational and…
 0xyassine/cve-2023-40028
Proof of concept demonstrating authenticated symlink upload in Ghost CMS leading to arbitrary file read via CVE-2023-40028.
 rehan6658/cve-2023-40028
Python exploit for CVE-2023-40028 in Ghost CMS, enabling arbitrary file read via symlink abuse in ZIP uploads. Includes automated cleanup.
 nickanderson/cfengine-cve_2015_0235
gethostbyname*() buffer overflow exploit in glibc - CVE-2015-0235 https://community.qualys.com/blogs/laws-of-vulnerabilities/2015/01/27/the-ghost-vuln…