

CVE-2020-0022
 idkwim/cve-2020-0022
Research repository documenting BlueFrag (CVE-2020-0022) Android Bluetooth heap overflow experiments, including GDB crash analysis and memcpy…
android-securitybinary-exploitationbluetooth-security+4
idkwim/cve-2020-0022Research repository documenting BlueFrag (CVE-2020-0022) Android Bluetooth heap overflow experiments, including GDB crash analysis and memcpy…
 nccgroup/ble-replay
BLE-Replay is a Bluetooth Low Energy (BLE) peripheral assessment tool
 nccgroup/bleboy
BLEBoy is a training tool to teach users about BLE security by providing a single BLE peripheral that can be used to experiment with each BLE pairing…
 pazhanivel07/system_bt_a10_r33_cve-2021-0474
Android Bluetooth stack (Fluoride) with a specific patch for CVE-2021-0474, providing source code for building and testing the Bluetooth component on…
 jclarkcom/ble_proxy
BLE-based HTTP proxy system routing browser traffic through an iOS device. Supports HTTP/HTTPS, data compression, and mock mode for testing without…
 761669642/mahesh-970-cve-2023-21125_bluedriod_repo
Targeted reference for CVE-2023-21125, an Android BlueDroid Bluetooth vulnerability, with code and documentation focused on the affected component.
 bluepigeonproject/blue-pigeon
Blue Pigeon is a Bluetooth-based data exfiltration and proxy tool to enable communication between a remote Command and Control (C2) server and a…
 trinadh465/system_bt_aosp10_r33_cve-2021-0589
Patched Android Bluetooth stack (AOSP10) addressing CVE-2021-0589, with build instructions for AOSP and Linux.
 nanopathi/system_bt_aosp10_r33_cve-2021-0476
Android Bluetooth stack (AOSP 10 r33) containing CVE-2021-0476 for vulnerability analysis, exploitation testing, and security research.
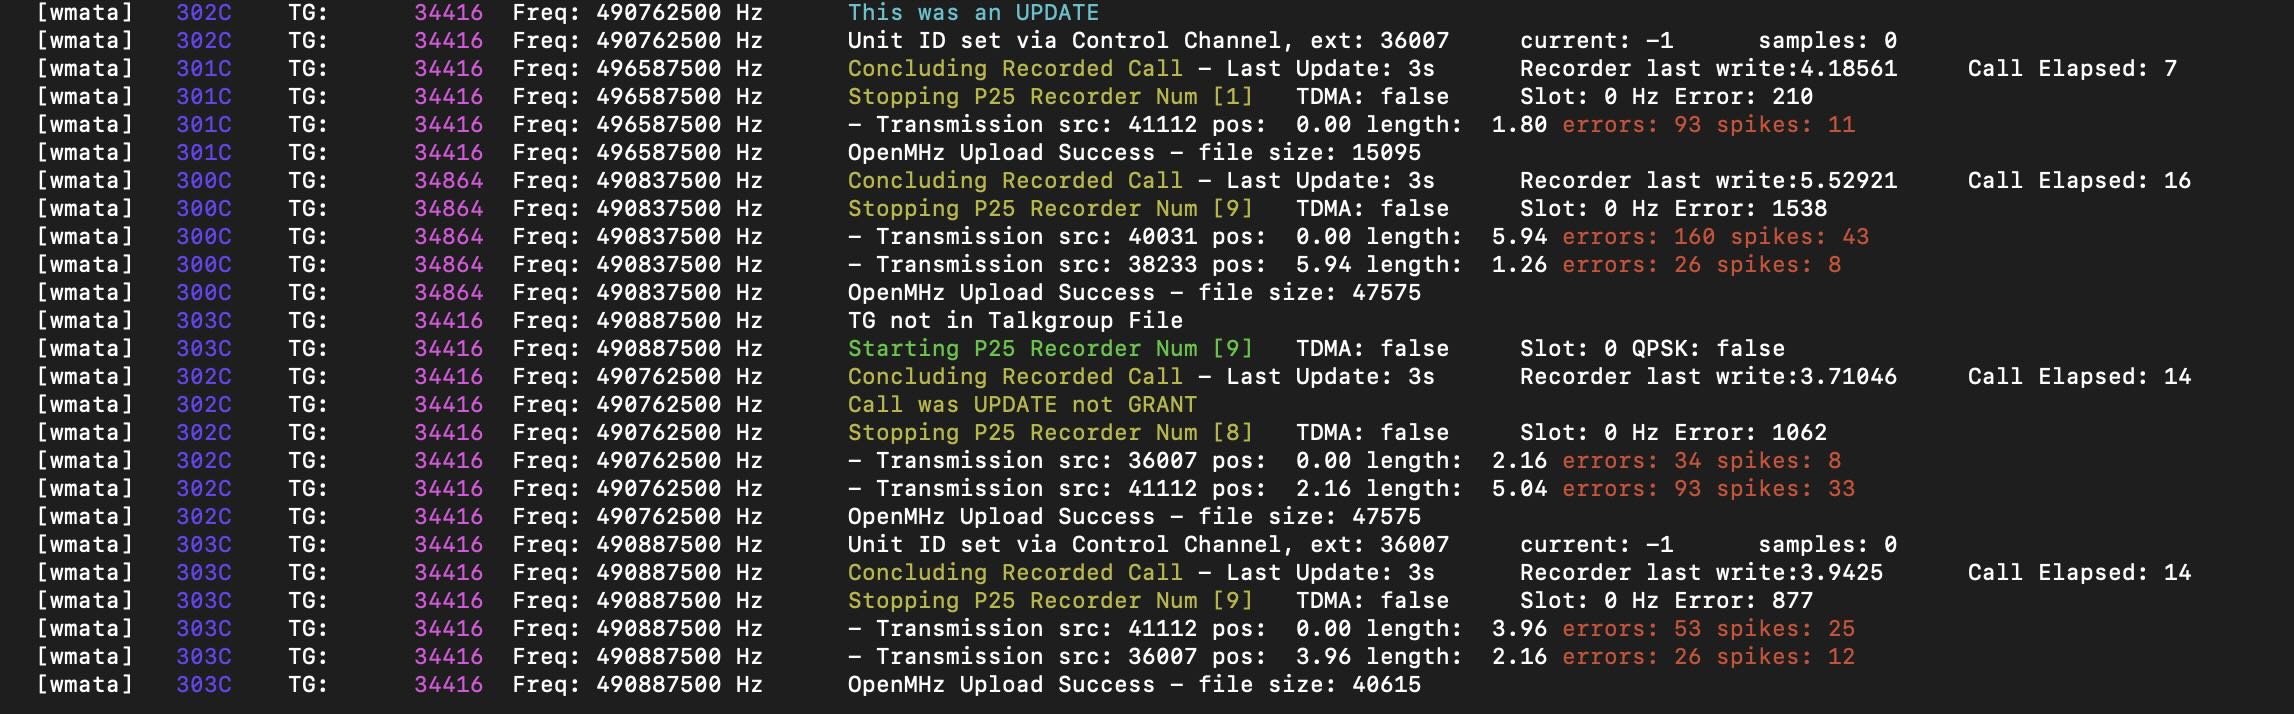 trunkrecorder/trunk-recorder
Records calls from a Trunked Radio System (P25 & SmartNet)
 embedi/ble_norton_core
Proof-of-concept exploit demonstrating command injection via BLE service in Norton Core Secure WiFi Router (CVE-2018-5234). Includes SSH access setup…
 trinadh465/packages_apps_bluetooth_aosp10_r33_cve-2022-20126
Android Bluetooth package with a patch for CVE-2022-20126, addressing a security vulnerability in AOSP 10.
 pazhanivel07/system_bt_a10-r33_cve-2021-0474
Android Fluoride Bluetooth stack source code with a focus on CVE-2021-0474, providing a foundation for vulnerability research and security analysis…
 shaikusaf/system_bt_aosp10_r33_cve-2021-0431
Android Bluetooth stack (Fluoride) with a specific patch for CVE-2021-0431, enabling analysis and testing of Bluetooth vulnerabilities in AOSP 10.
 satheesh575555/system_bt_aosp10_r33_cve-2020-0377
Android Bluetooth stack (Fluoride) with a patch for CVE-2020-0377, addressing a Bluetooth vulnerability in AOSP 10.
 shaikusaf/system_bt_aosp10_r33_cve-2022-20224
AOSP Bluetooth stack repository modified to address CVE-2022-20224, providing a patched version of the Fluoride Bluetooth stack for Android 10.
 zalexdev/wpair-app
WPair is a defensive security research tool that demonstrates the CVE-2025-36911 (eg WhisperPair) vulnerability in Google's Fast Pair protocol. This…
 cracksoft900/blue-borne
BlueBorne Exploits & Framework This repository contains a PoC code of various exploits for the BlueBorne vulnerabilities. Under 'android' exploits…