
hcxdumptool
 zerbea/hcxdumptool
Small tool to capture packets from wlan devices.
packet-sniffing-analysispassword-crackingpenetration-testing+2
2.2k27 days ago
zerbea/hcxdumptoolSmall tool to capture packets from wlan devices.
 zerbea/hcxtools
A small set of tools to convert packets from capture files to hash files for use with Hashcat or John the Ripper.
 greatscottgadgets/libbtbb
C library for decoding Bluetooth baseband packets and extracting piconet information from Ubertooth and USRP hardware for wireless analysis.
 dougives/wisp
Script and hardware kit to automatically deauth 802.11 clients en masse. Captures packets for later nefariousness.
 calebmadrigal/trackerjacker
Like nmap for mapping wifi networks you're not connected to, plus device tracking
 secdev/scapy
Python-based interactive packet manipulation library for forging, decoding, sending, capturing, and analyzing network packets across a wide range of…
 syworks/wireless-ids
Ability to detect suspicious activity such as (WEP/WPA/WPS) attack by sniffing the air for wireless packets.
 danmcinerney/wifi-monitor
Prints the IPs on your local network that're sending the most packets
 ioactive/laf
This project intends to provide a series of tools to craft, parse, send, analyze and crack a set of LoRaWAN packets in order to audit or pentest the…
 hash3lizer/airpydump
Analyze Wireless Packets on the fly. Currently supporting three working Modes (Reader, Live, Stealth)
 hayzamjs/blueborne-cve-2017-1000251
Proof-of-concept exploit for Blueborne CVE-2017-1000251 enabling Bluetooth denial-of-service attacks on Linux machines via crafted L2CAP packets.
 shadowy-pycoder/ndpspoof
Perform RA/RDNSS/NA spoofing and RA Guard evasion with arbitrary IPv6 packets
 infobyte/pyrmax
Decoder/encoder for Ubiquiti AirMAX wireless protocol frames; parse pcap/live captures, discover devices, scan for vulnerable firmware, craft…
 securityanalysts/cve-2021-37152
Exploit Accsess network clients by sending packets in wirless TP-LINK and preparing for a mitm attack
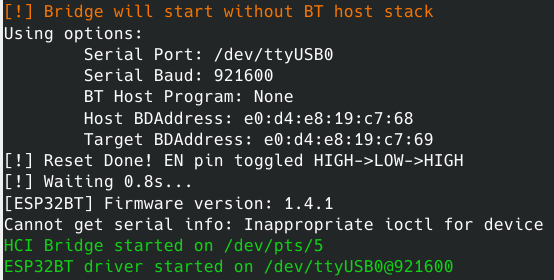 matheus-garbelini/esp32_bluetooth_classic_sniffer
Active Bluetooth BR/EDR Sniffer/Injector as cheap as any ESP32 board can get. Works with Scapy ;-)
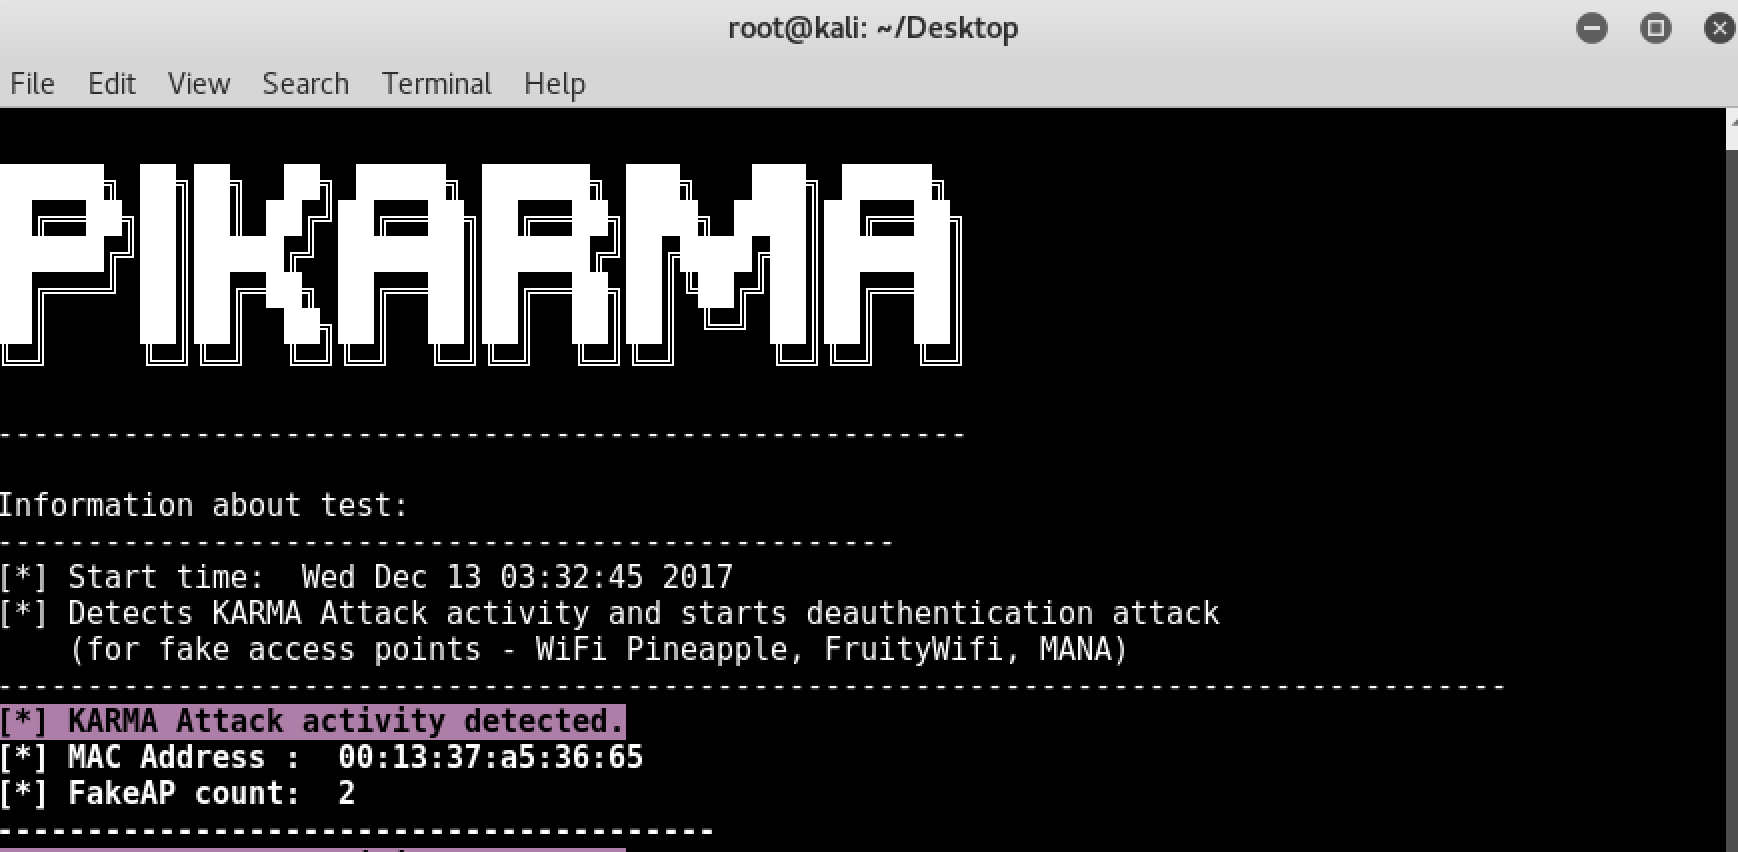 wipi-hunter/pikarma
📡🍓🍍 Detects wireless network attacks performed by KARMA module (fake AP). Starts deauthentication attack (for fake access points)
 90n45-d3v/dbmonster
A Multitool For Tracking And Locating Nearby Devices Via Their RF Activities.
 alainx277/cve-2025-24797
Meshtastic buffer overflow vulnerability - CVE-2025-24797