
airpydump
 hash3lizer/airpydump
Analyze Wireless Packets on the fly. Currently supporting three working Modes (Reader, Live, Stealth)
information-gatheringnetwork-securitypacket-sniffing-analysis+1
53
hash3lizer/airpydumpAnalyze Wireless Packets on the fly. Currently supporting three working Modes (Reader, Live, Stealth)
 hayzamjs/blueborne-cve-2017-1000251
Proof-of-concept exploit for Blueborne CVE-2017-1000251 enabling Bluetooth denial-of-service attacks on Linux machines via crafted L2CAP packets.
 danmcinerney/wifi-monitor
Prints the IPs on your local network that're sending the most packets
 syworks/wireless-ids
Ability to detect suspicious activity such as (WEP/WPA/WPS) attack by sniffing the air for wireless packets.
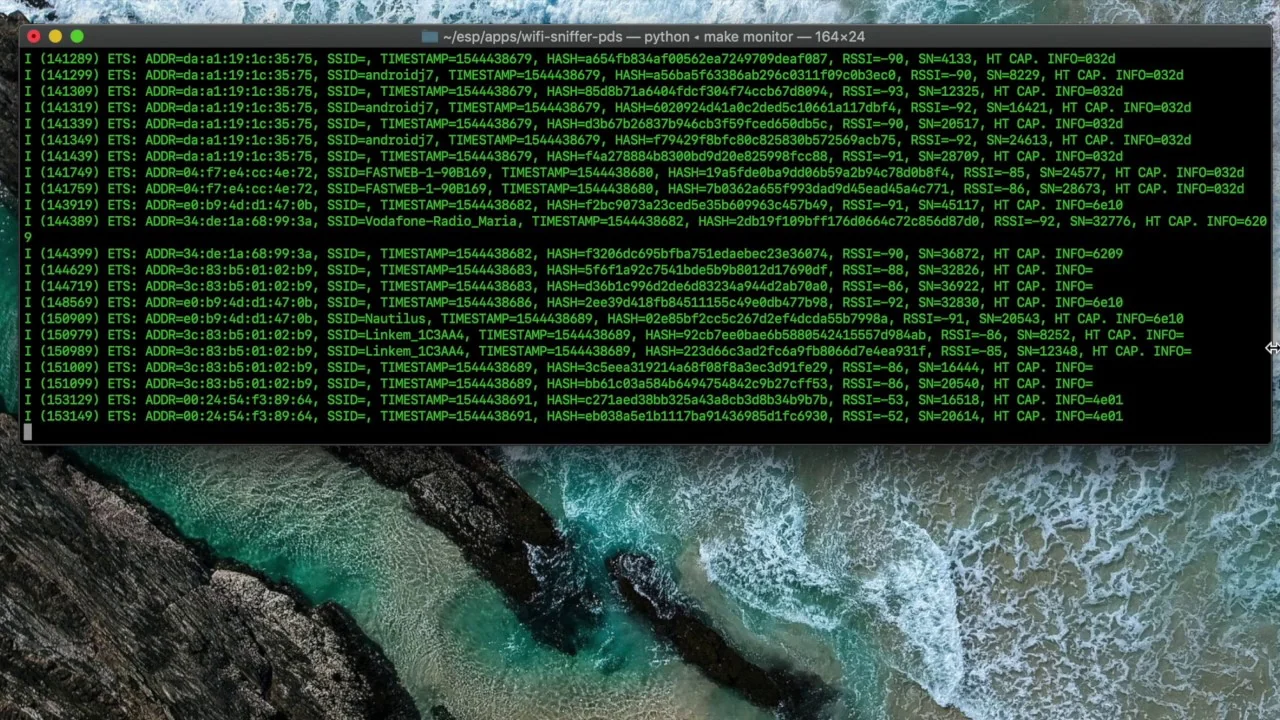 ets-polito/esp32-sniffer
ESP32 firmware that sniffs PROBE REQUEST packets sent by smartphones searching for Wi-Fi connection to extract different types of information