
hcxtools
 zerbea/hcxtools
A small set of tools to convert packets from capture files to hash files for use with Hashcat or John the Ripper.
hash-analysispassword-crackingpenetration-testing-frameworks+2
2.4k
zerbea/hcxtoolsA small set of tools to convert packets from capture files to hash files for use with Hashcat or John the Ripper.
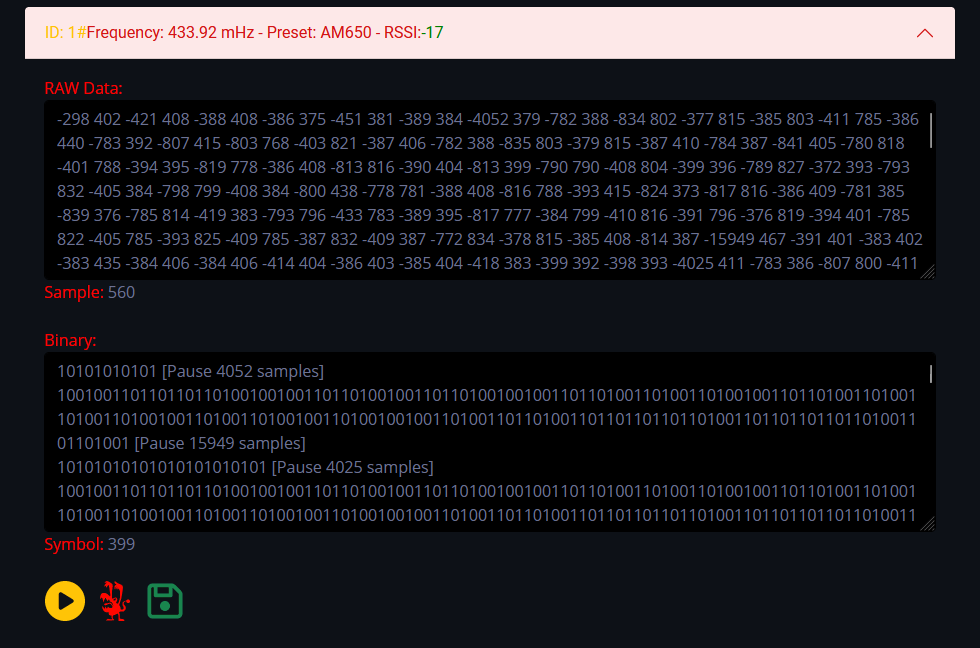 h-rat/evilcrowrf_custom_firmware_cc1101_flipperzero
This firmware is an alternative to the EvilCrowRF default firmware. Module: CC1101 - Compatible Flipper Zero file.
 furrtek/precir
Open-source hardware and software toolkit for reverse-engineering and communicating with infrared-based electronic shelf labels. Includes custom…
 helgesverre/sony-vp-extract
Decrypt and extract voice guidance MP3 prompts from Sony WH-1000XM4 encrypted voice packs. AES key extracted via Bluetooth firmware dump of the…
 aircrack-ng/aircrack-ng
Complete suite for WiFi network security auditing, including packet capture, injection attacks, deauthentication, fake AP creation, and WEP/WPA PSK…
 zerbea/hcxdumptool
Small tool to capture packets from wlan devices.
 bastilleresearch/mousejack
Research tools for MouseJack vulnerabilities in nRF24L01 wireless devices, including device discovery, packet sniffing, network mapping, and firmware…

 aress31/wirespy
Framework designed to automate various wireless networks attacks (the project was presented on Pentester Academy TV's toolbox in 2017).
 greatscottgadgets/libbtbb
C library for decoding Bluetooth baseband packets and extracting piconet information from Ubertooth and USRP hardware for wireless analysis.
 icsec/airpwn-ng
Packet injection for wifi; simplified.
 0x13enny/kr00k
PoC of CVE-2019-15126 kr00k vulnerability
 dougives/wisp
Script and hardware kit to automatically deauth 802.11 clients en masse. Captures packets for later nefariousness.
 alt3kx/airdecloak-ng
My Aircrack-ng contribution with Thomas d'Otreppe
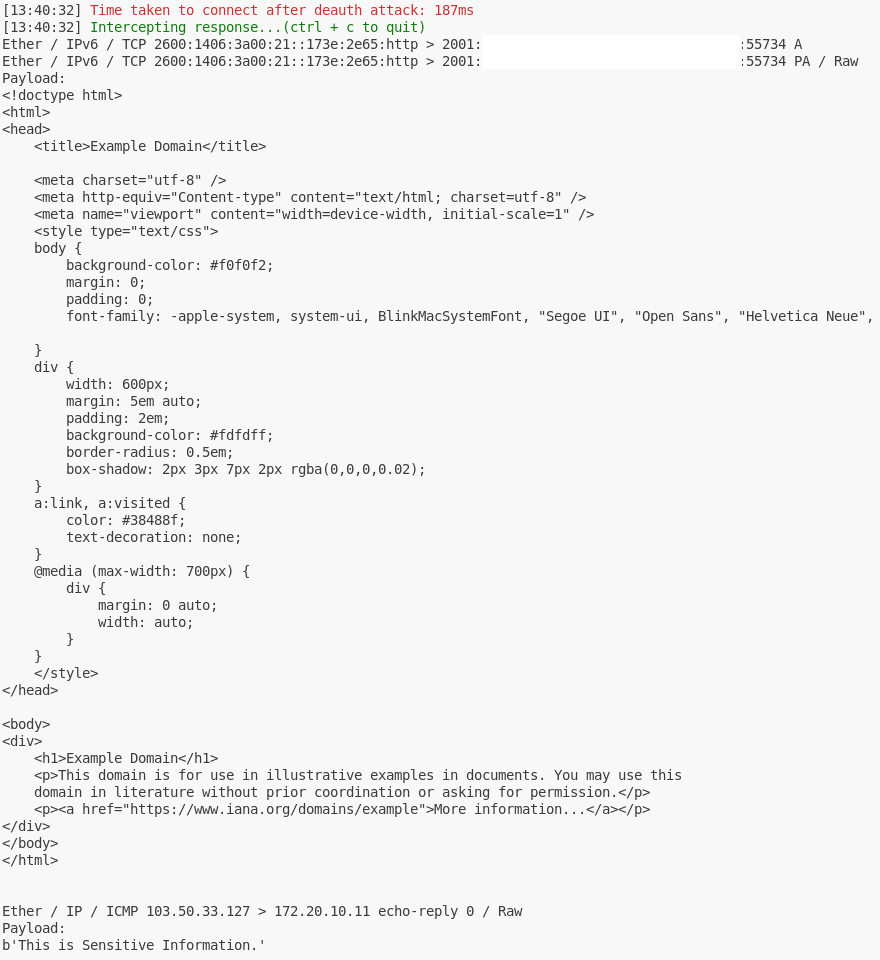 toffeenutt/cve-2022-47522-poc
Proof-of-concept exploit for CVE-2022-47522 demonstrating Wi-Fi frame interception via deauthentication attack and MAC address spoofing to capture…
 diegovargasj/cve-2025-32407
Proof-of-concept exploit for CVE-2025-32407: TLS certificate validation bypass in Samsung Internet for Galaxy Watch, enabling Man-in-the-Middle…