
CVE-2017-1000250-PoC
 olav-st/cve-2017-1000250-poc
Proof of concept exploit script for CVE-2017-1000250. Written while researching for the essay in TTM4137 Wireless Security.
educationexploitationpenetration-testing+2
5
olav-st/cve-2017-1000250-pocProof of concept exploit script for CVE-2017-1000250. Written while researching for the essay in TTM4137 Wireless Security.
 kamorin/dhcpig
DHCP exhaustion script written in python using scapy network library
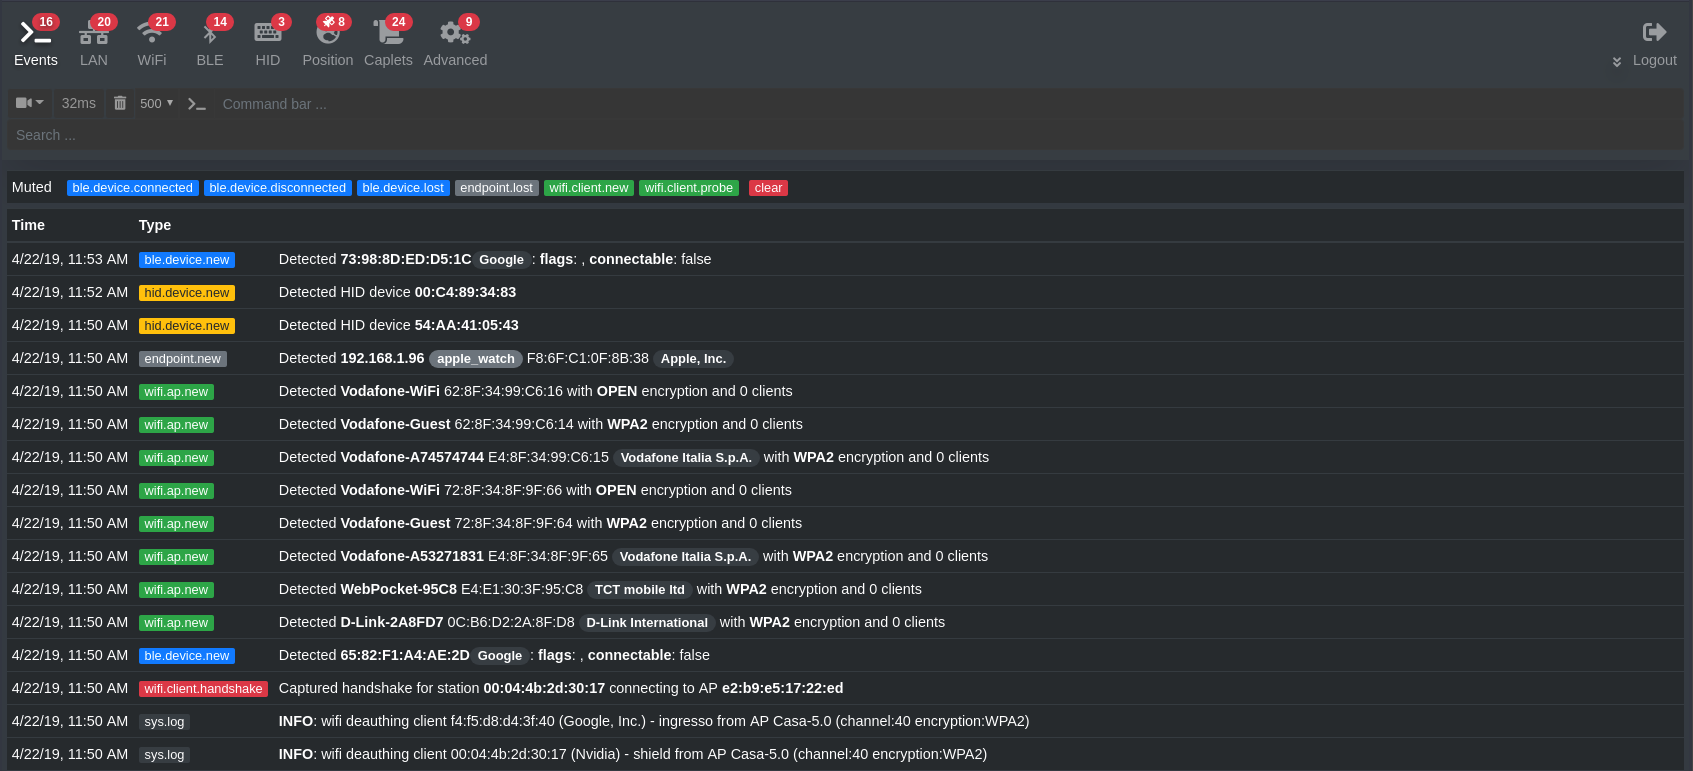 bettercap/bettercap
The Swiss Army knife for 802.11, BLE, HID, CAN-bus, IPv4 and IPv6 networks reconnaissance and MITM attacks.
 savio-code/fern-wifi-cracker
Automatically exported from code.google.com/p/fern-wifi-cracker
 p0cl4bs/wifipumpkin3
Powerful framework for rogue access point attack.
 fo-000/bluing
An intelligence gathering tool for hacking Bluetooth
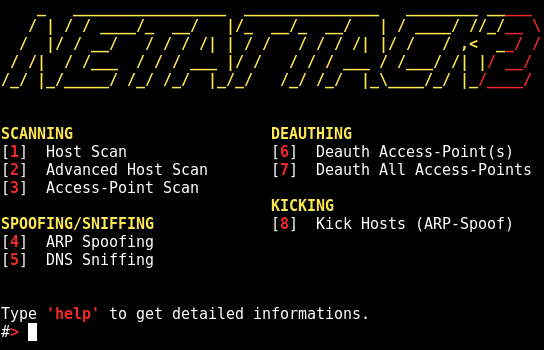 chrizator/netattack2
An advanced network scan and attack script based on GUI. 2nd version of no-GUI netattack.
 syworks/wireless-ids
Ability to detect suspicious activity such as (WEP/WPA/WPS) attack by sniffing the air for wireless packets.
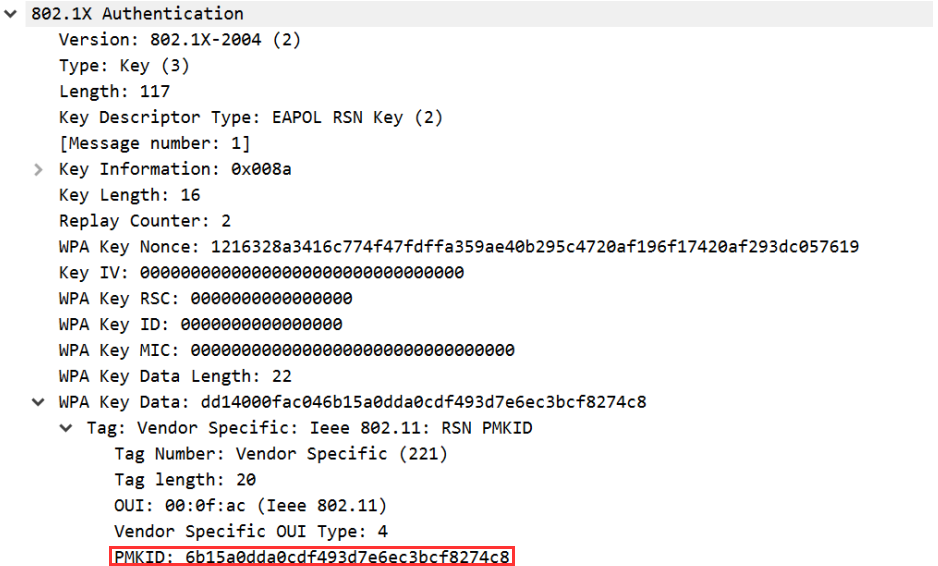 n0mi1k/pmkidcracker
A tool to crack WPA2 passphrase with PMKID value without clients or de-authentication
 qyvora/qyvora-toha3ee
Go-based network exploitation and MITM framework for authorized penetration testing, network reconnaissance, traffic interception, wireless security…